
packetfence
PacketFence is a fully supported, trusted, Free and Open Source network access control (NAC) solution. Boasting an impressive feature set including a…

PacketFence is a fully supported, trusted, Free and Open Source network access control (NAC) solution. Boasting an impressive feature set including a…

Kubesploit is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in Golang, focused on containerized environments.

Control Web Panel (CWP) vulnerability scenario related to CVE-2026-57517

Automated API security testing tool that generates tests from OpenAPI specs, fuzzes inputs, and checks for OWASP API Top 10 vulnerabilities including…

Pentest/BugBounty progress control with scanning modules

Automated authorization security scanner for OpenAPI-based APIs. Tests GET endpoints with multiple credential sets to detect privilege escalation and…

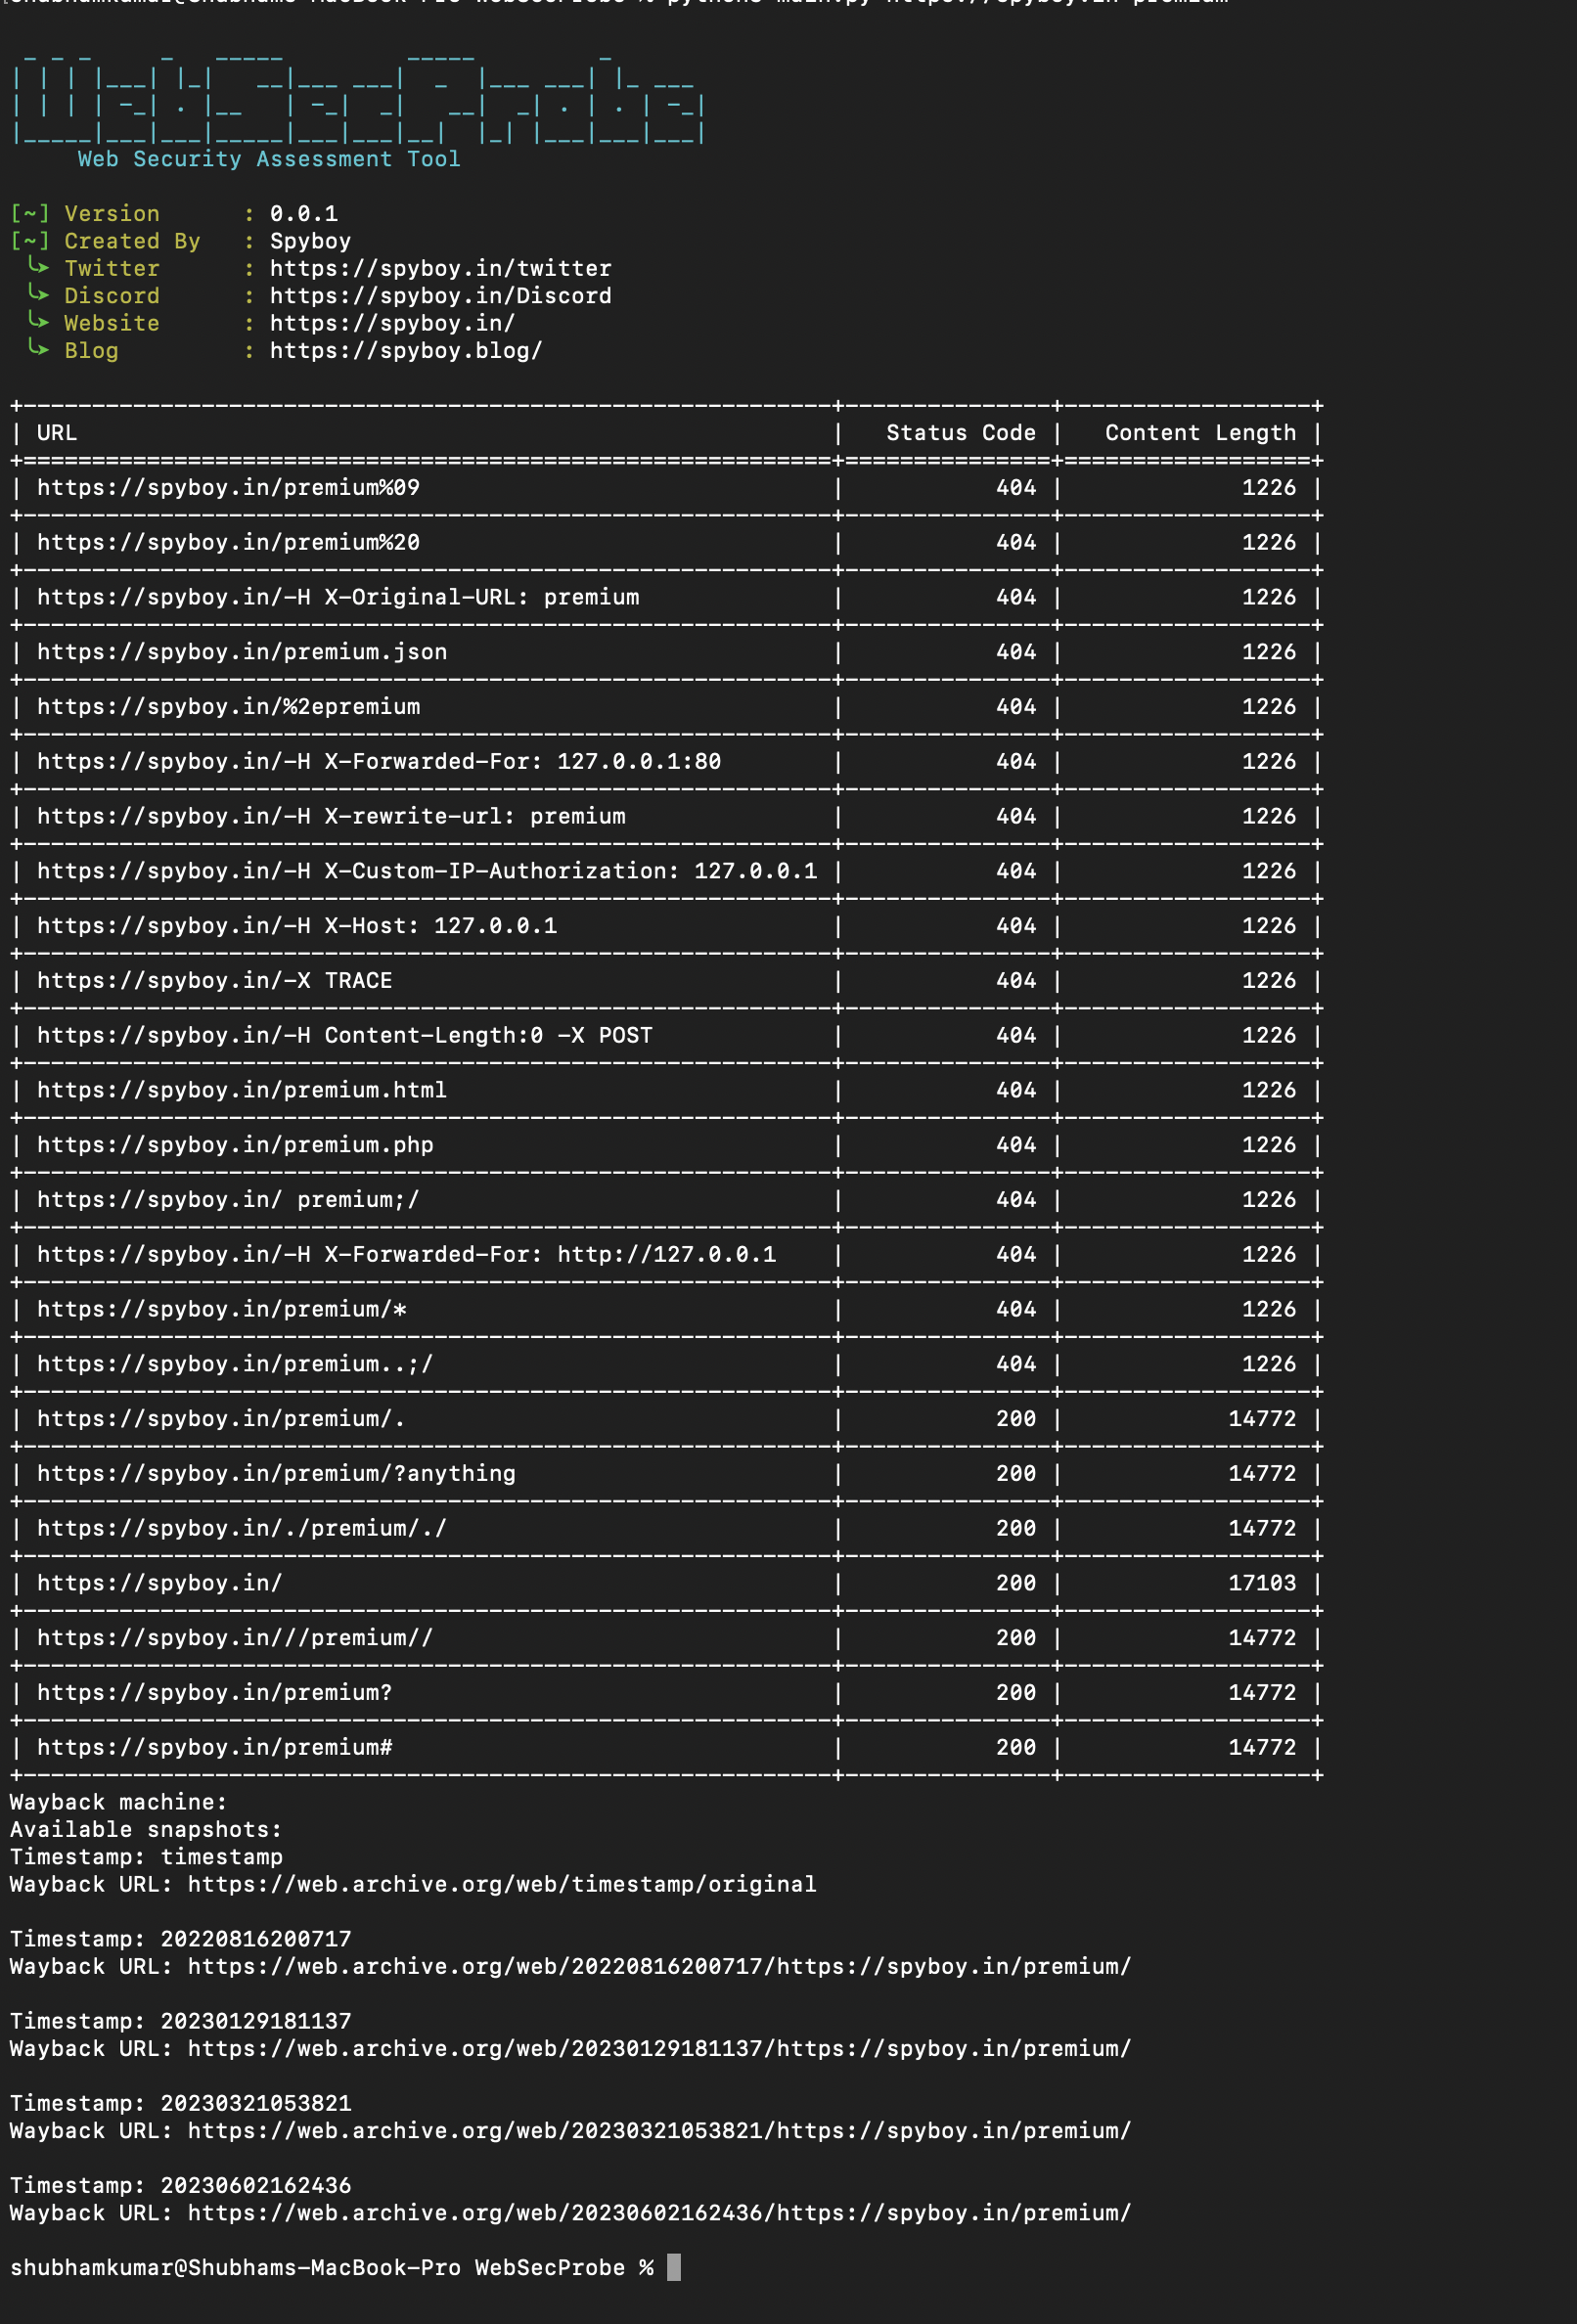
Security testing tool for analyzing HTTP 403 responses and identifying access control misconfigurations in web applications.

Automated penetration testing framework for REST APIs with OpenAPI-driven test generation, 32 OWASP-based security tests, and built-in access control…

Scanner for CVE-2023-22515 - Broken Access Control Vulnerability in Atlassian Confluence

Open security scanner and self-hosted control plane for AI, MCP, and cloud. One evidence model — run scans in your environment, centralize findings,…

This vulnerability may allow an unauthenticated attacker with network access to the BIG-IP system through the management port and/or self IP…

9 MITRE ATT&CK-mapped KQL detections on a live Microsoft Sentinel + Defender XDR environment (control-plane, endpoint, identity), with a PR-gated…

Authorized education-sector recon & triage orchestrator (nmap/dirsearch/sqlmap/hydra + CVE-2024-4577, secret/API-key leak, XSS, wp2shell) with a web…

💉 Blind SQL Injection → RCE exploit for Control Web Panel (CWP) ≤ 0.9.8.1224 — userRes POST → INTO DUMPFILE → cwpsvc shell

Atlassian Confluence Data Center and Server Broken Access Control Vulnerability

PoC de CVE-2026-35616: control de acceso indebido en FortiClient EMS.

Synthetic demo target for CVE-2024-10821 vulnerability detection and automated fix via compensating control. Demonstrates one-click PR-based…

On Thursday (December 9th), a 0-day exploit in the popular Java logging library log4j (version 2) was discovered that results in Remote Code…