

pillager
 brittonhayes/pillager
Pillage filesystems for sensitive information with Go 🔍
data-exfiltrationinformation-gatheringpenetration-testing+4
31710 months ago
brittonhayes/pillagerPillage filesystems for sensitive information with Go 🔍
 jonaslejon/malicious-pdf
Generate malicious PDF test files for penetration testing, bug bounty hunting, and red teaming. Tests SSRF, XSS, XXE, NTLM credential theft, and data…
 solivaquaant/cve-2026-85706
Proof-of-concept and reproduction lab for CVE-2026-85706, an unauthenticated path-traversal file read in GitLab CE/EE repository commits and files…
 b1tsec/cve-1999-0524
A Bash script to check if systems are vulnerable to ICMP Timestamp Request Remote Date Disclosure (CVE-1999-0524).
 ransc0rp1on/icmp-timestamp-poc
A reconnaissance tool to detect CVE-1999-0524 (ICMP Timestamp Disclosure) by automating timestamp extraction via nping or hping3. Converts raw ICMP…
 olivsec/loboguara
Cyber threat intelligence platform for SSL certificate discovery, domain/URL scanning, data leak monitoring, tracking link generation, and threat…
 citcheese/odbparser
OSINT tool to search, parse and dump only the open Elasticsearch and MongoDB directories that have the data you care about exposing
 ridhinva/drupal-jsonapi-sqli-scanner
Scanner: CVE-2026-9082 Drupal PostgreSQL SQLi via JSON:API — Python scanner for unauthenticated SQLi leading to RCE (CISA KEV)
 j0lt-github/mongobleedburp
Burp Suite extension to detect CVE-2025-14847 (MongoBleed) via manual leak tests from a dedicated UI tab.
 becrevex/cve-2024-38063
Performs an IPv6 vulnerability scan and packet flood attack on specified targets. The script simulates a SYN flood and ICMP flood attack and…
 yunuscadirci/callstranger
Vulnerability checker for Callstranger (CVE-2020-12695)
 papermtn/gitlab-watchman
Finding exposed secrets and personal data in GitLab
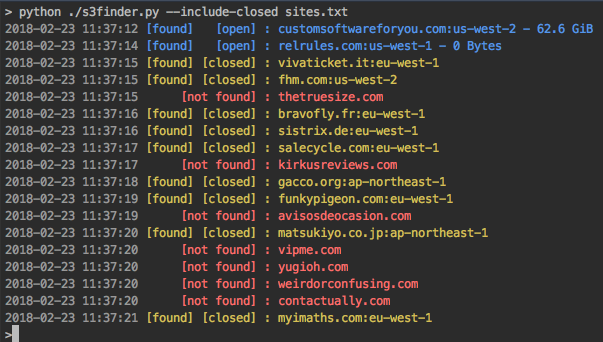 yehgdotnet/s3scanner
Scan for open S3 buckets and dump
 gabrielunknown/cve-2026-85706
Perl PoC exploiting CVE-2026-85706, an unauthenticated GitLab path traversal enabling arbitrary file read, with bulk scanning and credential…
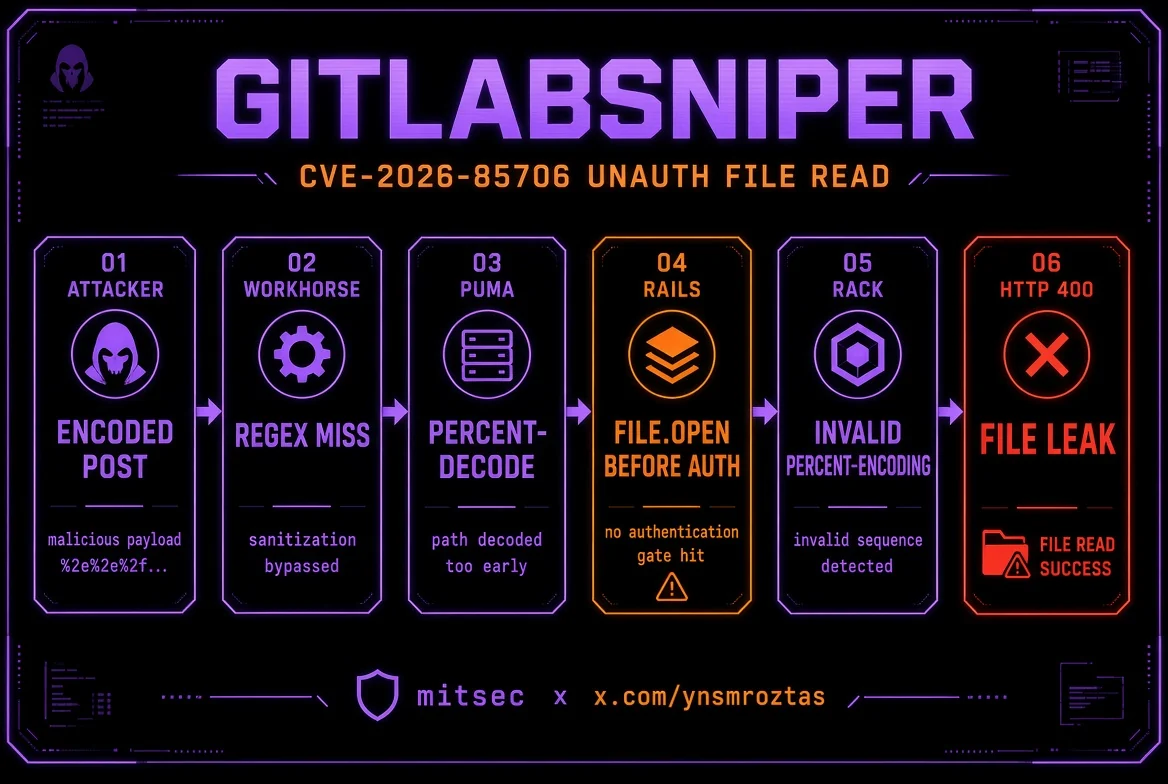 ynsmroztas/gitlabsniper
Single-file Python scanner and exploit for CVE-2026-85706, an unauthenticated arbitrary file read in self-managed GitLab CE/EE, with project…
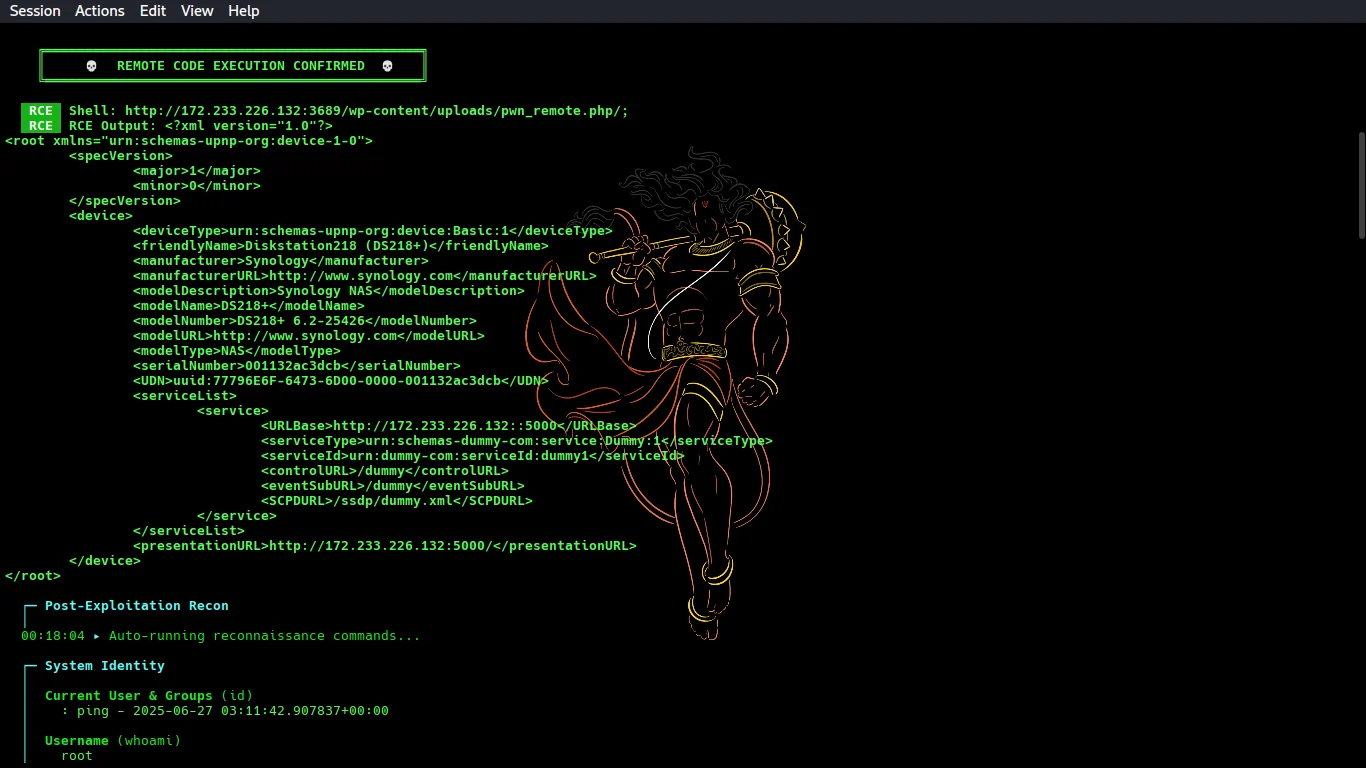 cybertechajju/cve-2026-1357-poc
Automated exploit tool for CVE-2026-1357, an unauthenticated RCE in WPvivid Backup & Migration. Scans WordPress targets, bypasses WAF/403, uploads a…
 shinthink/cve-2026-60004
CVE-2026-60004 — Gitea/Forgejo Diffpatch Git Hook RCE. Bare clone → post-index-change hook injection. CVSS 9.8 | CWE-94 | Gitea < 1.27.1
 1amunvalid/cve-2025-10951
Proof-of-concept checker for CVE-2025-10951, an unauthenticated path traversal in ml-logger, validating arbitrary file read via /glob and /stream…