
cirrusgo
 ph33rr/cirrusgo
A fast tool to scan SAAS,PAAS App written in Go
cloud-securityinformation-gatheringvulnerability-scanners+1
ph33rr/cirrusgoA fast tool to scan SAAS,PAAS App written in Go
 hakaioffsec/navgix
Multi-threaded Go tool to detect nginx alias traversal vulnerabilities using heuristic and brute-force techniques for identifying vulnerable…
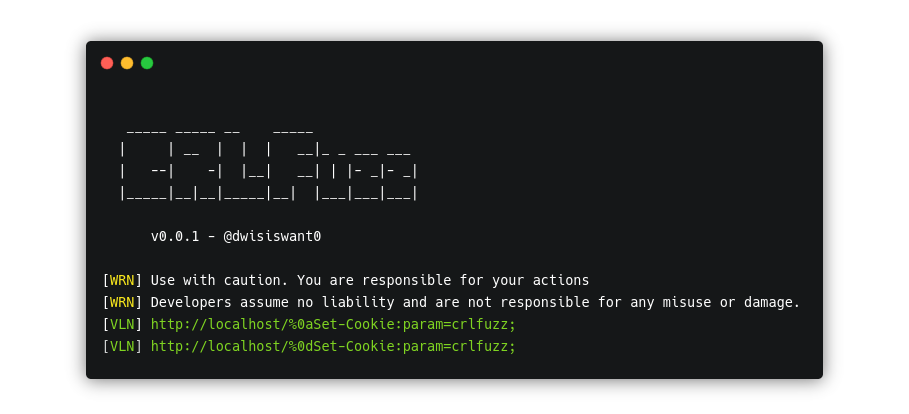 dwisiswant0/crlfuzz
A fast tool to scan CRLF vulnerability written in Go
 jibaru/cve-2025-66478-github-patcher
Go-based automation tool that scans GitHub repositories for vulnerable Next.js versions (CVE-2025-66478) and automatically creates pull requests with…
 kleiton0x00/ppmap
A scanner/exploitation tool written in GO, which leverages client-side Prototype Pollution to XSS by exploiting known gadgets.
 0xteles/jsleak
a Go code to detect leaks in JS files via regex patterns
 brosck/mantra
「🔑」A tool used to hunt down API key leaks in JS files and pages
 iqzer0/vulnknox
A Go-based wrapper for the KNOXSS API to automate XSS vulnerability testing.
 tanmayshahane/kyubisweep
A lightweight, cross-platform CLI tool that scans your filesystem to detect exposed secrets, API keys, and tokens. Built with Go for maximum…
 gagaltotal/cve-2026-57517-cwp
Control Web Panel (CWP) vulnerability scenario related to CVE-2026-57517
 hillu/local-log4j-vuln-scanner
[Moved to Codeberg] Simple local scanner for vulnerable log4j instances
 in3tinct/see-surf
Security tool to find potential vulnerable Server Side Request Forgery (SSRF) parameters.
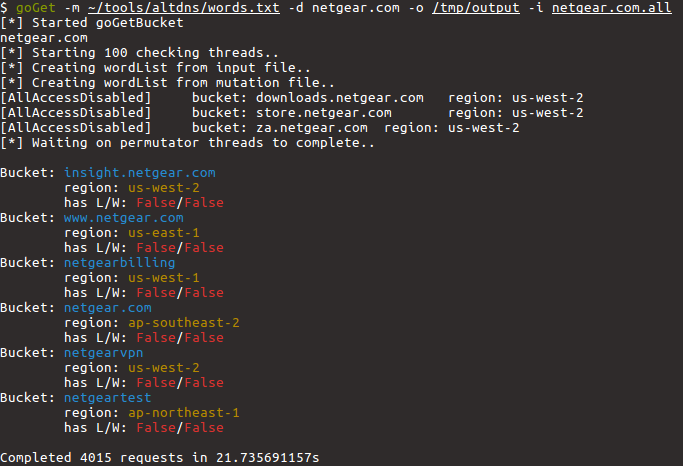 glem0/gogetbucket
A penetration testing tool to enumerate and analyse Amazon S3 Buckets owned by a domain.
 ryandamour/ssrfuzz
SSRFuzz is a tool to find Server Side Request Forgery vulnerabilities, with CRLF chaining capabilities
 dwisiswant0/proxylogscan
A fast tool to mass scan for a vulnerability on Microsoft Exchange Server that allows an attacker bypassing the authentication and impersonating as…
 ryandamour/crlfmap
CRLFMap is a tool to find HTTP Splitting vulnerabilities
 ethicalhackingplayground/crlfmap
CRLFMap is a tool to find HTTP Splitting vulnerabilities
 jpiechowka/at-doom-fortigate
Fortigate CVE-2018-13379 - Tool to search for vulnerable Fortigate hosts in Rapid7 Project Sonar data anonymously through The Tor network.