
faraday-cli
 infobyte/faraday-cli
Faraday's Command Line Interface
command-and-controldevsecopspenetration-testing+1
infobyte/faraday-cliFaraday's Command Line Interface
 promptfoo/promptfoo
Test your prompts, agents, and RAGs. Red teaming/pentesting/vulnerability scanning for AI. Compare performance of GPT, Claude, Gemini, DeepSeek, and…
 appliscale/cloud-security-audit
A command line security audit tool for Amazon Web Services
 valtersit/wordpress-cve-scanner
Scan your WordPress core, themes and plugins for known CVEs from the command line. Open source, auditable, privacy-first — powered by the ValtersIT…
 amirrezamarzban/portscan-cve-2026-41940
IP CIDRs (presumably as input, maybe command line or file) and checks ports 2083 and 2087 for openness
 zack0x01/cve-2025-55182-advanced-scanner-
Command-line scanner for detecting and exploiting CVE-2025-55182 (React Server Components RCE) in Next.js applications. Supports custom command…
 rix4uni/cve-2025-55182
A command-line tool for detecting CVE-2025-55182 and CVE-2025-66478 in Next.js applications using React Server Components.
 exdev994/cve-2026-4631-cockpit-rce
Unauthenticated Remote Code Execution via SSH Command-Line Argument Injection Cockpit versions 327 – 359 | CVSS 9.8 Critical | CWE-78
 iamblacksolo2-bugbounty/poc-cve-2025-55182
Bash-based scanner for detecting and exploiting CVE-2025-55182 (React Server Components RCE) in Next.js applications. Supports custom command…
 hunter24x24/cve-2025-55182-mass
Command-line scanner for detecting and exploiting CVE-2025-55182 (RCE) in Next.js React Server Components. Supports batch scanning from domain lists…
 testssl/testssl.sh
Testing TLS/SSL encryption anywhere on any port
 assetnote/react2shell-scanner
High Fidelity Detection Mechanism for RSC/Next.js RCE (CVE-2025-55182 & CVE-2025-66478)
 devploit/nomore403
🚫 Advanced tool for security researchers to bypass 403/40X restrictions through smart techniques and adaptive request manipulation. Fast. Precise.…
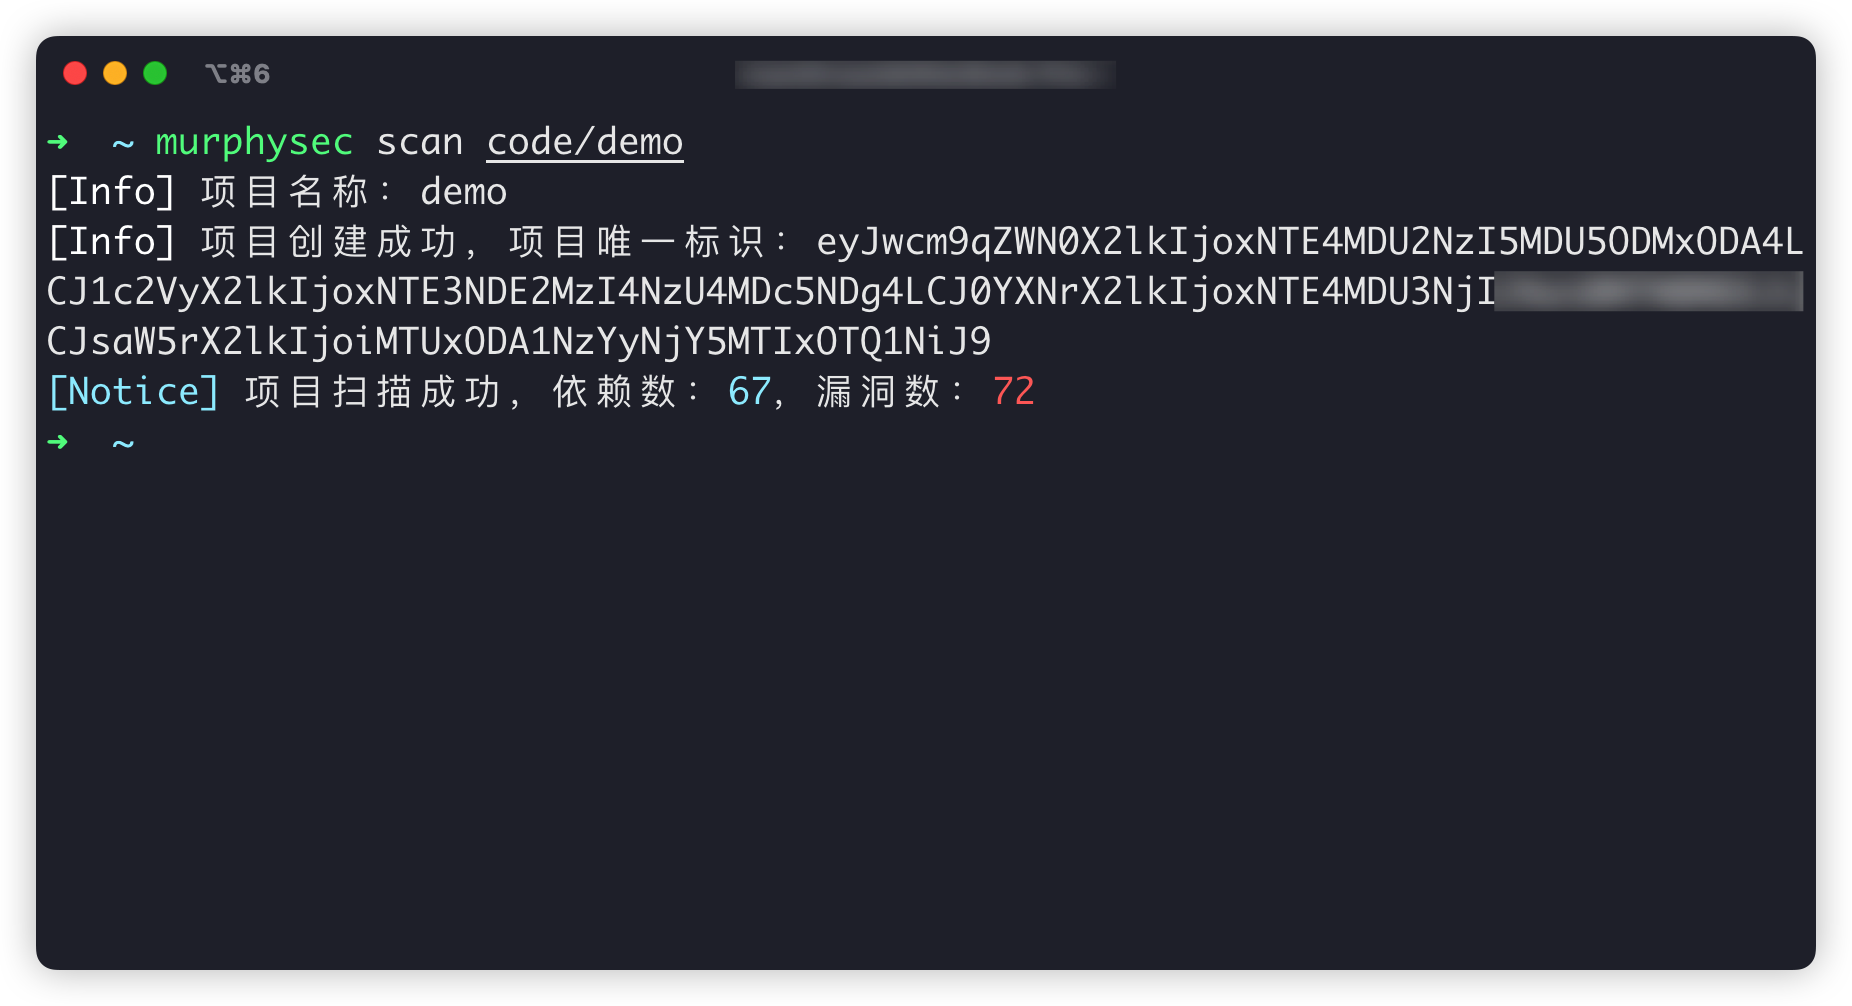 murphysecurity/murphysec
An open source tool focused on software supply chain security. 墨菲安全专注于软件供应链安全,具备专业的软件成分分析(SCA)、漏洞检测、专业漏洞库。
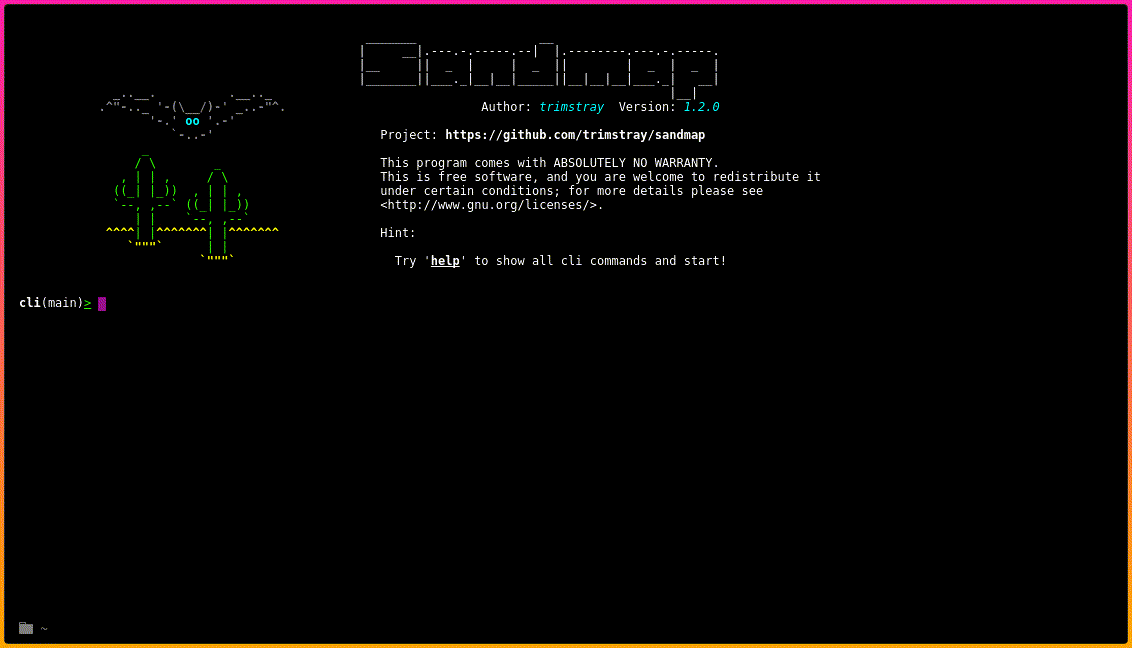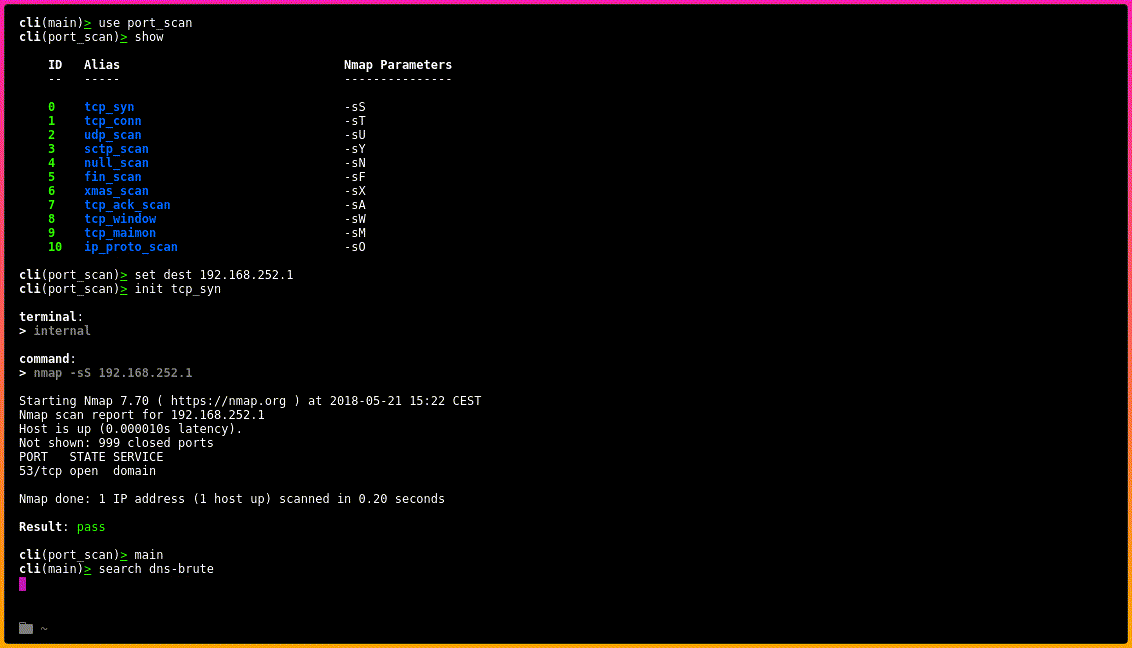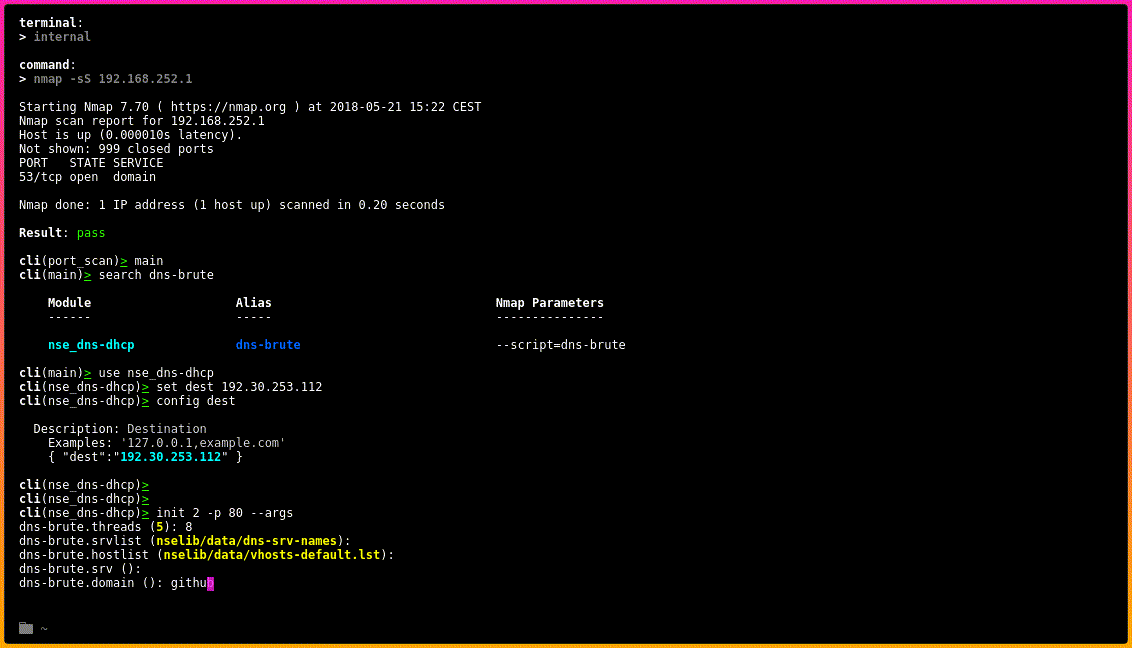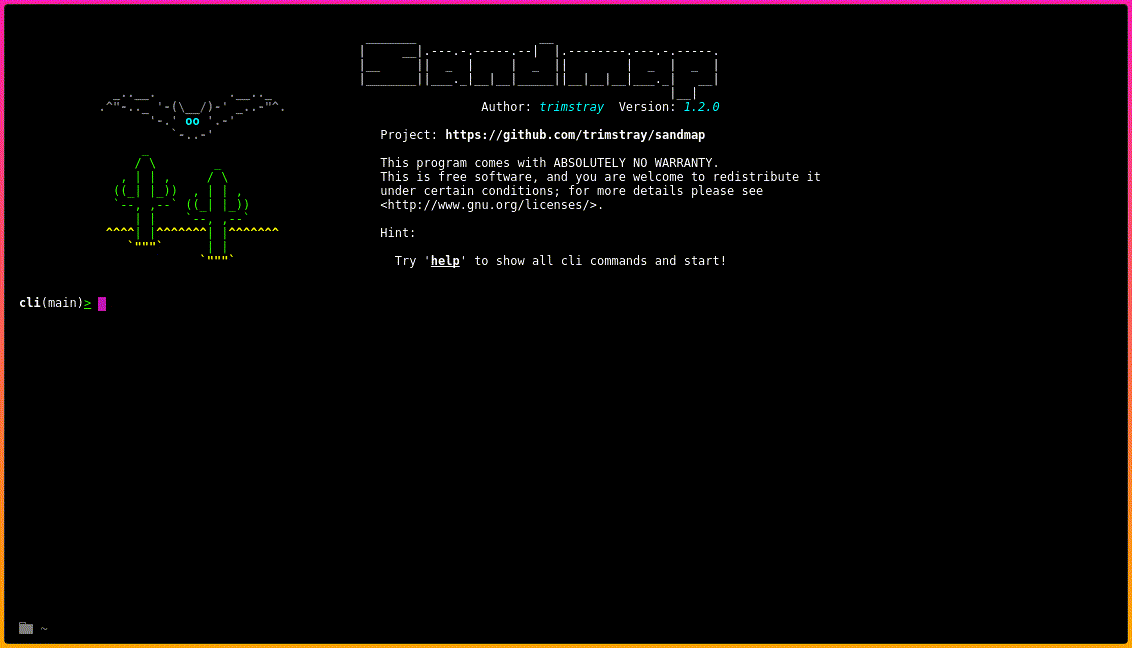 trimstray/sandmap
Nmap on steroids. Simple CLI with the ability to run pure Nmap engine, 31 modules with 459 scan profiles.
 bishopfox/sj
A tool for auditing endpoints defined in exposed (Swagger/OpenAPI) definition files.
 logpresso/cve-2021-44228-scanner
Vulnerability scanner and mitigation patch for Log4j2 CVE-2021-44228
 arpsyndicate/puncia
Panthera(P.)uncia - Official CLI utility for Subdomain Center & Exploit Observer.