
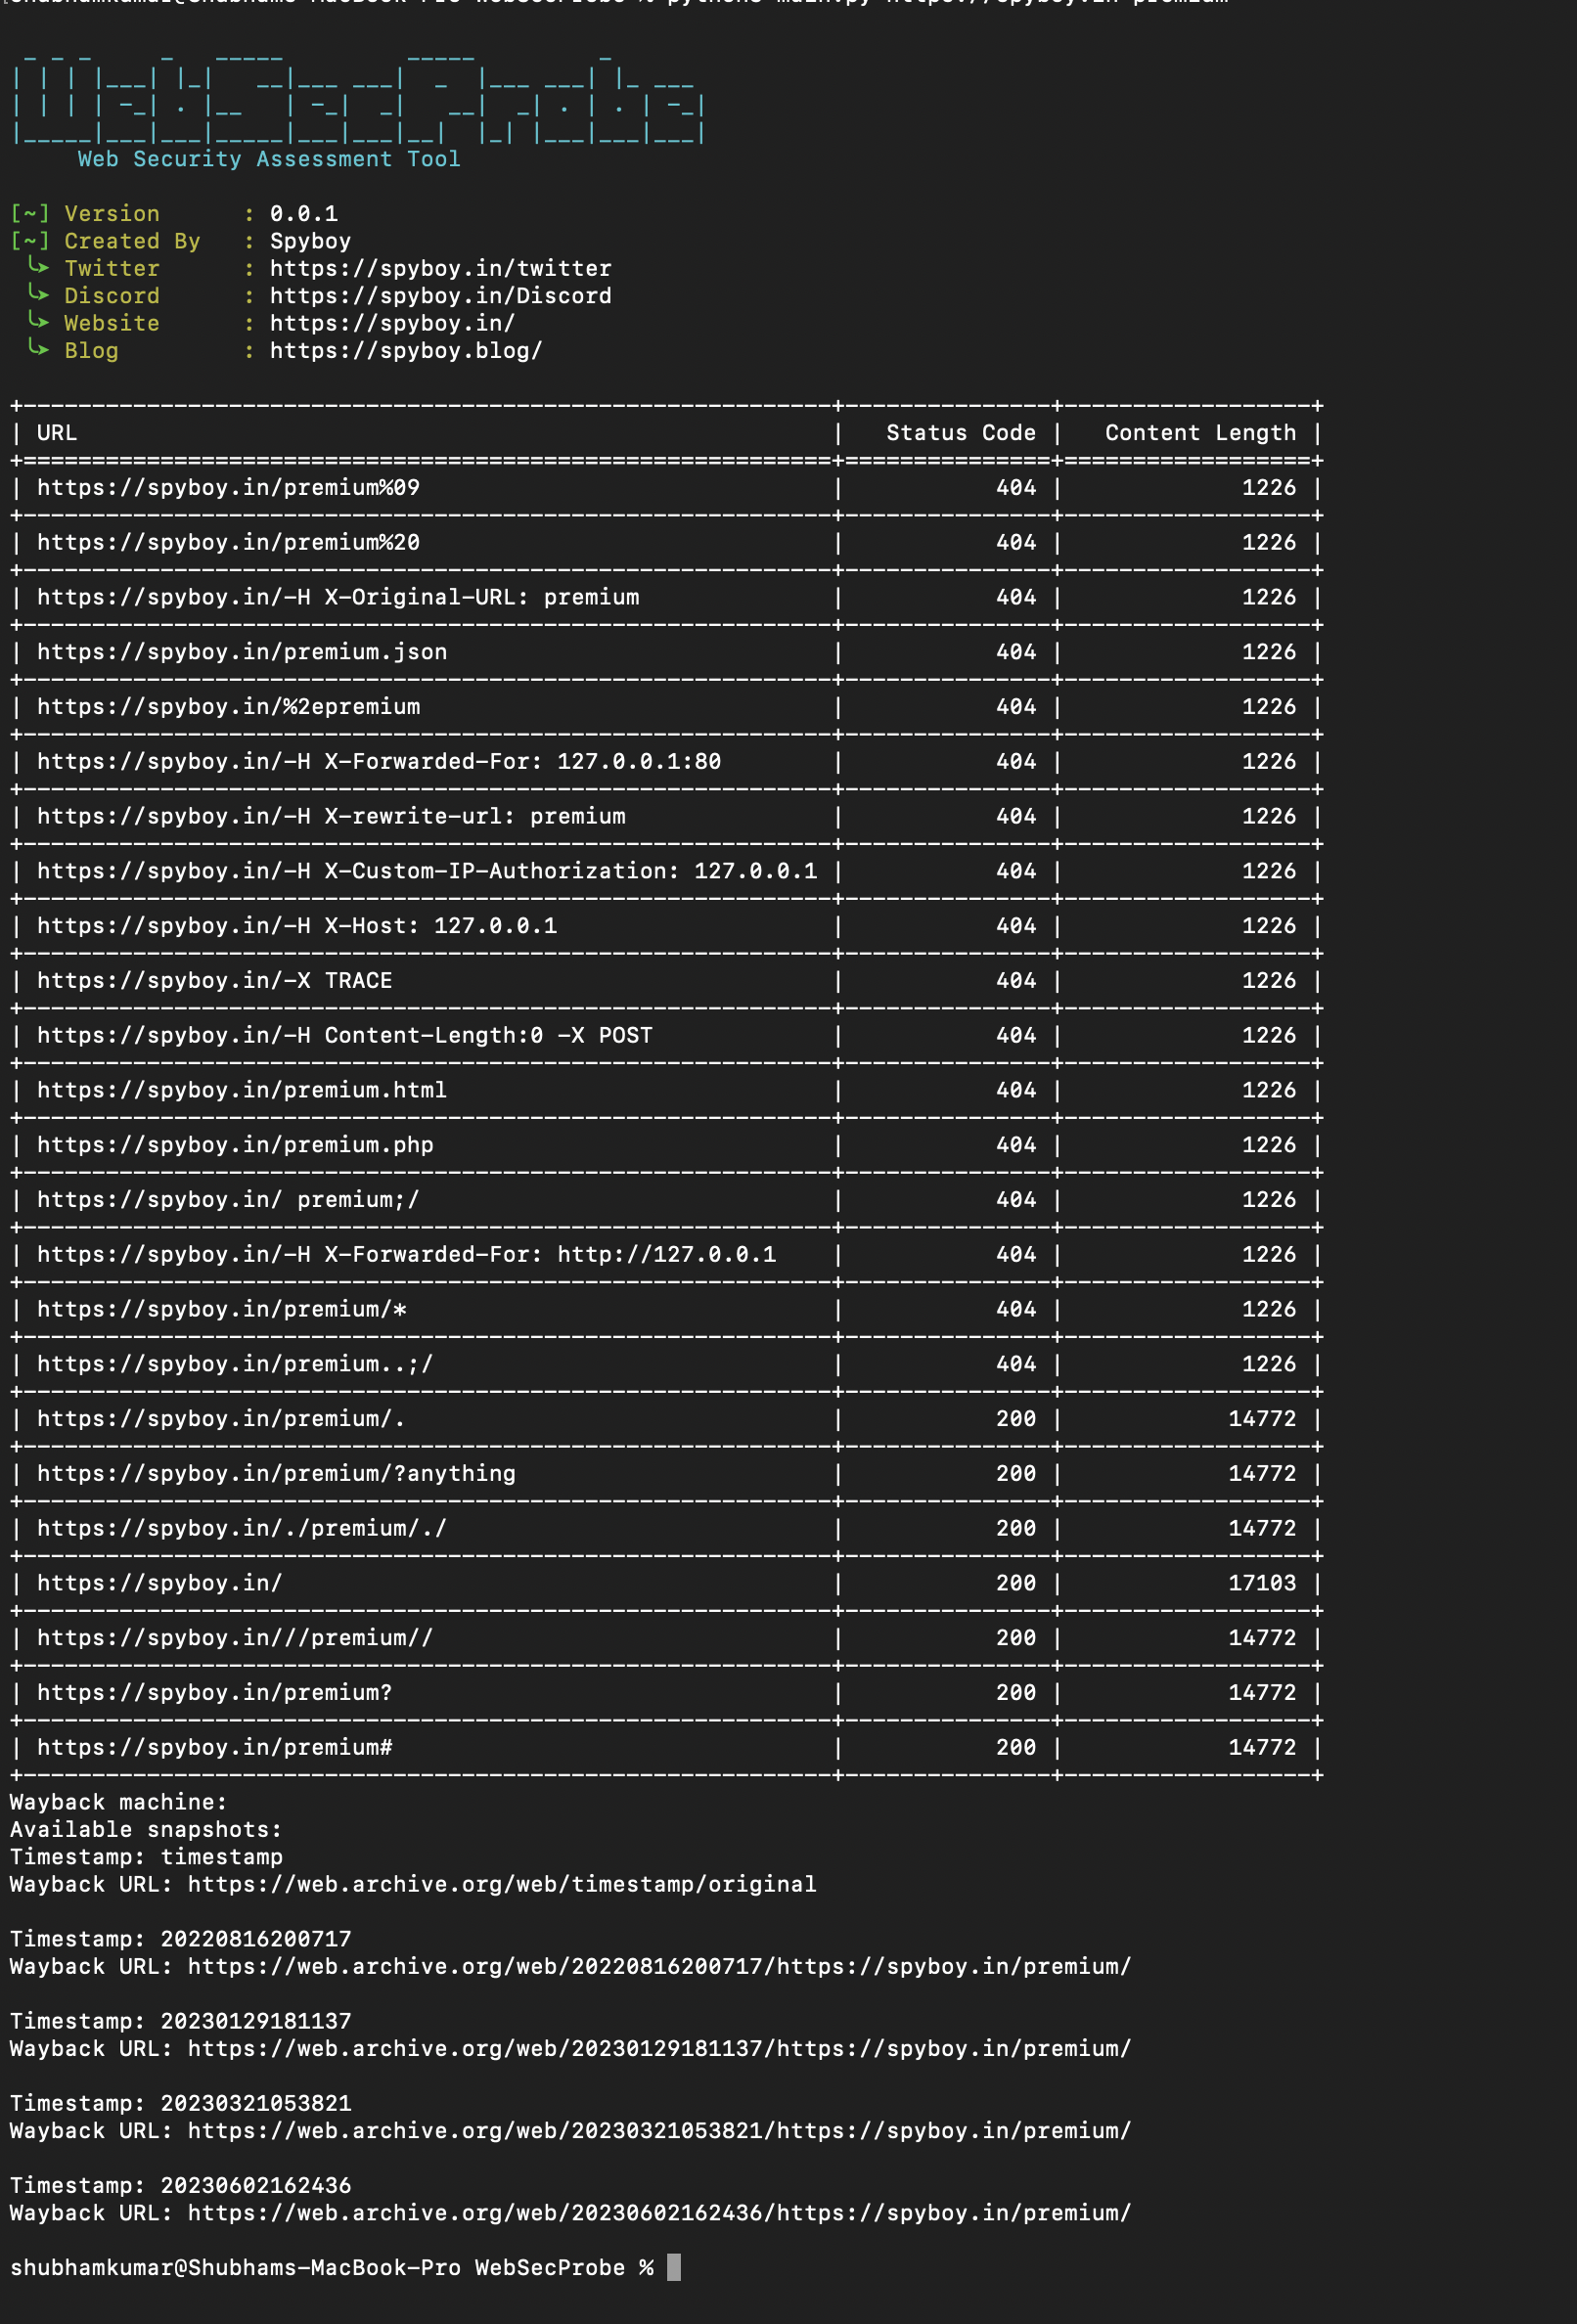
WebSecProbe
 spyboy-productions/websecprobe
Security testing tool for analyzing HTTP 403 responses and identifying access control misconfigurations in web applications.
misconfigurationpenetration-testingvulnerability-scanners+2
188
spyboy-productions/websecprobeSecurity testing tool for analyzing HTTP 403 responses and identifying access control misconfigurations in web applications.
 usdag/sncscan
Tool for analyzing SAP Secure Network Communications (SNC).
 sw33ber/nuclei-cve-analyzer
CVE intelligence pipeline that compares public CVEs against Nuclei templates to identify missing vulnerability coverage, classify types, and rank…
 tharindudh/tharindudh-log4j-vulnerability-in-ghidra-tool-cve-2021-44228
Ghidra-based tool for detecting and analyzing the Log4j vulnerability (CVE-2021-44228) in binary files, enabling reverse engineering of affected…
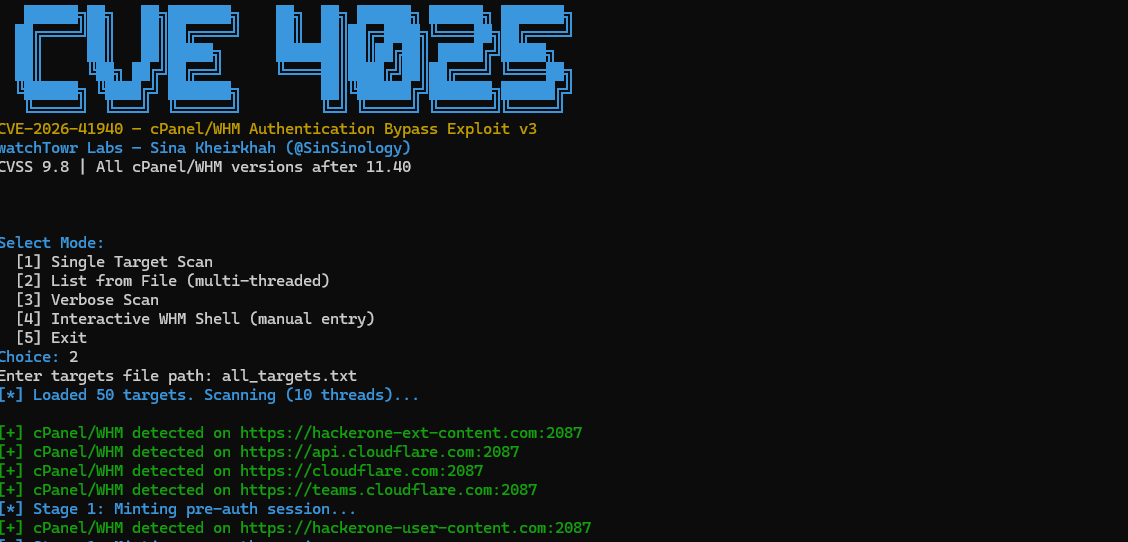 senyx122/cve-2026-41940
A security research tool for detecting and analyzing cPanel/WHM services and their authentication behavior. Designed for authorized testing and…
 e-m-b-a/embark
Centralized firmware scanning and reporting platform with a web UI, REST API, and automated analysis workflows for securing embedded/IoT devices.
 rav1010/cve-2026-27636
Passive reconnaissance and fingerprinting tool for detecting FreeScout deployments and analyzing exposure related to CVE-2026-28289, aiding…
 spyboy-productions/camxploit
Security reconnaissance and assessment tool for identifying potentially exposed IP cameras by analyzing open ports, service configurations, and…
 wi3memake/react2shell-scanner
Command-line security assessment framework for React and Next.js applications, analyzing React Server Components for misconfigurations, with…
 hav0cx0/cve-2023-48795
Python tool to identify SSH servers potentially vulnerable to CVE-2023-48795 (Terrapin) by analyzing OpenSSH version banners via netcat. Useful for…
 filosottile/heartbleed
A checker (site and tool) for CVE-2014-0160
 hackmanit/tinja
TInjA is a CLI tool for testing web pages for template injection vulnerabilities and supports 44 of the most relevant template engines for eight…
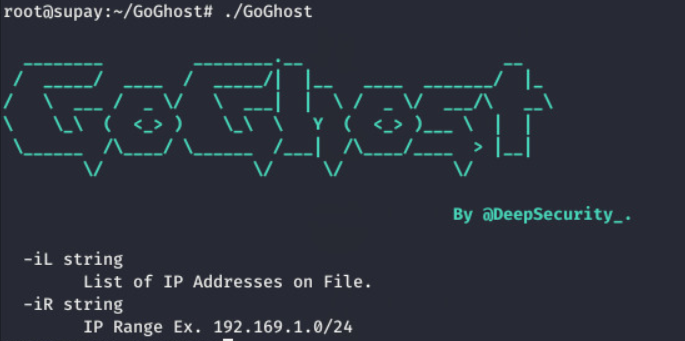 deepsecurity-pe/goghost
High Performance, lightweight, portable Open Source tool for mass SMBGhost Scan
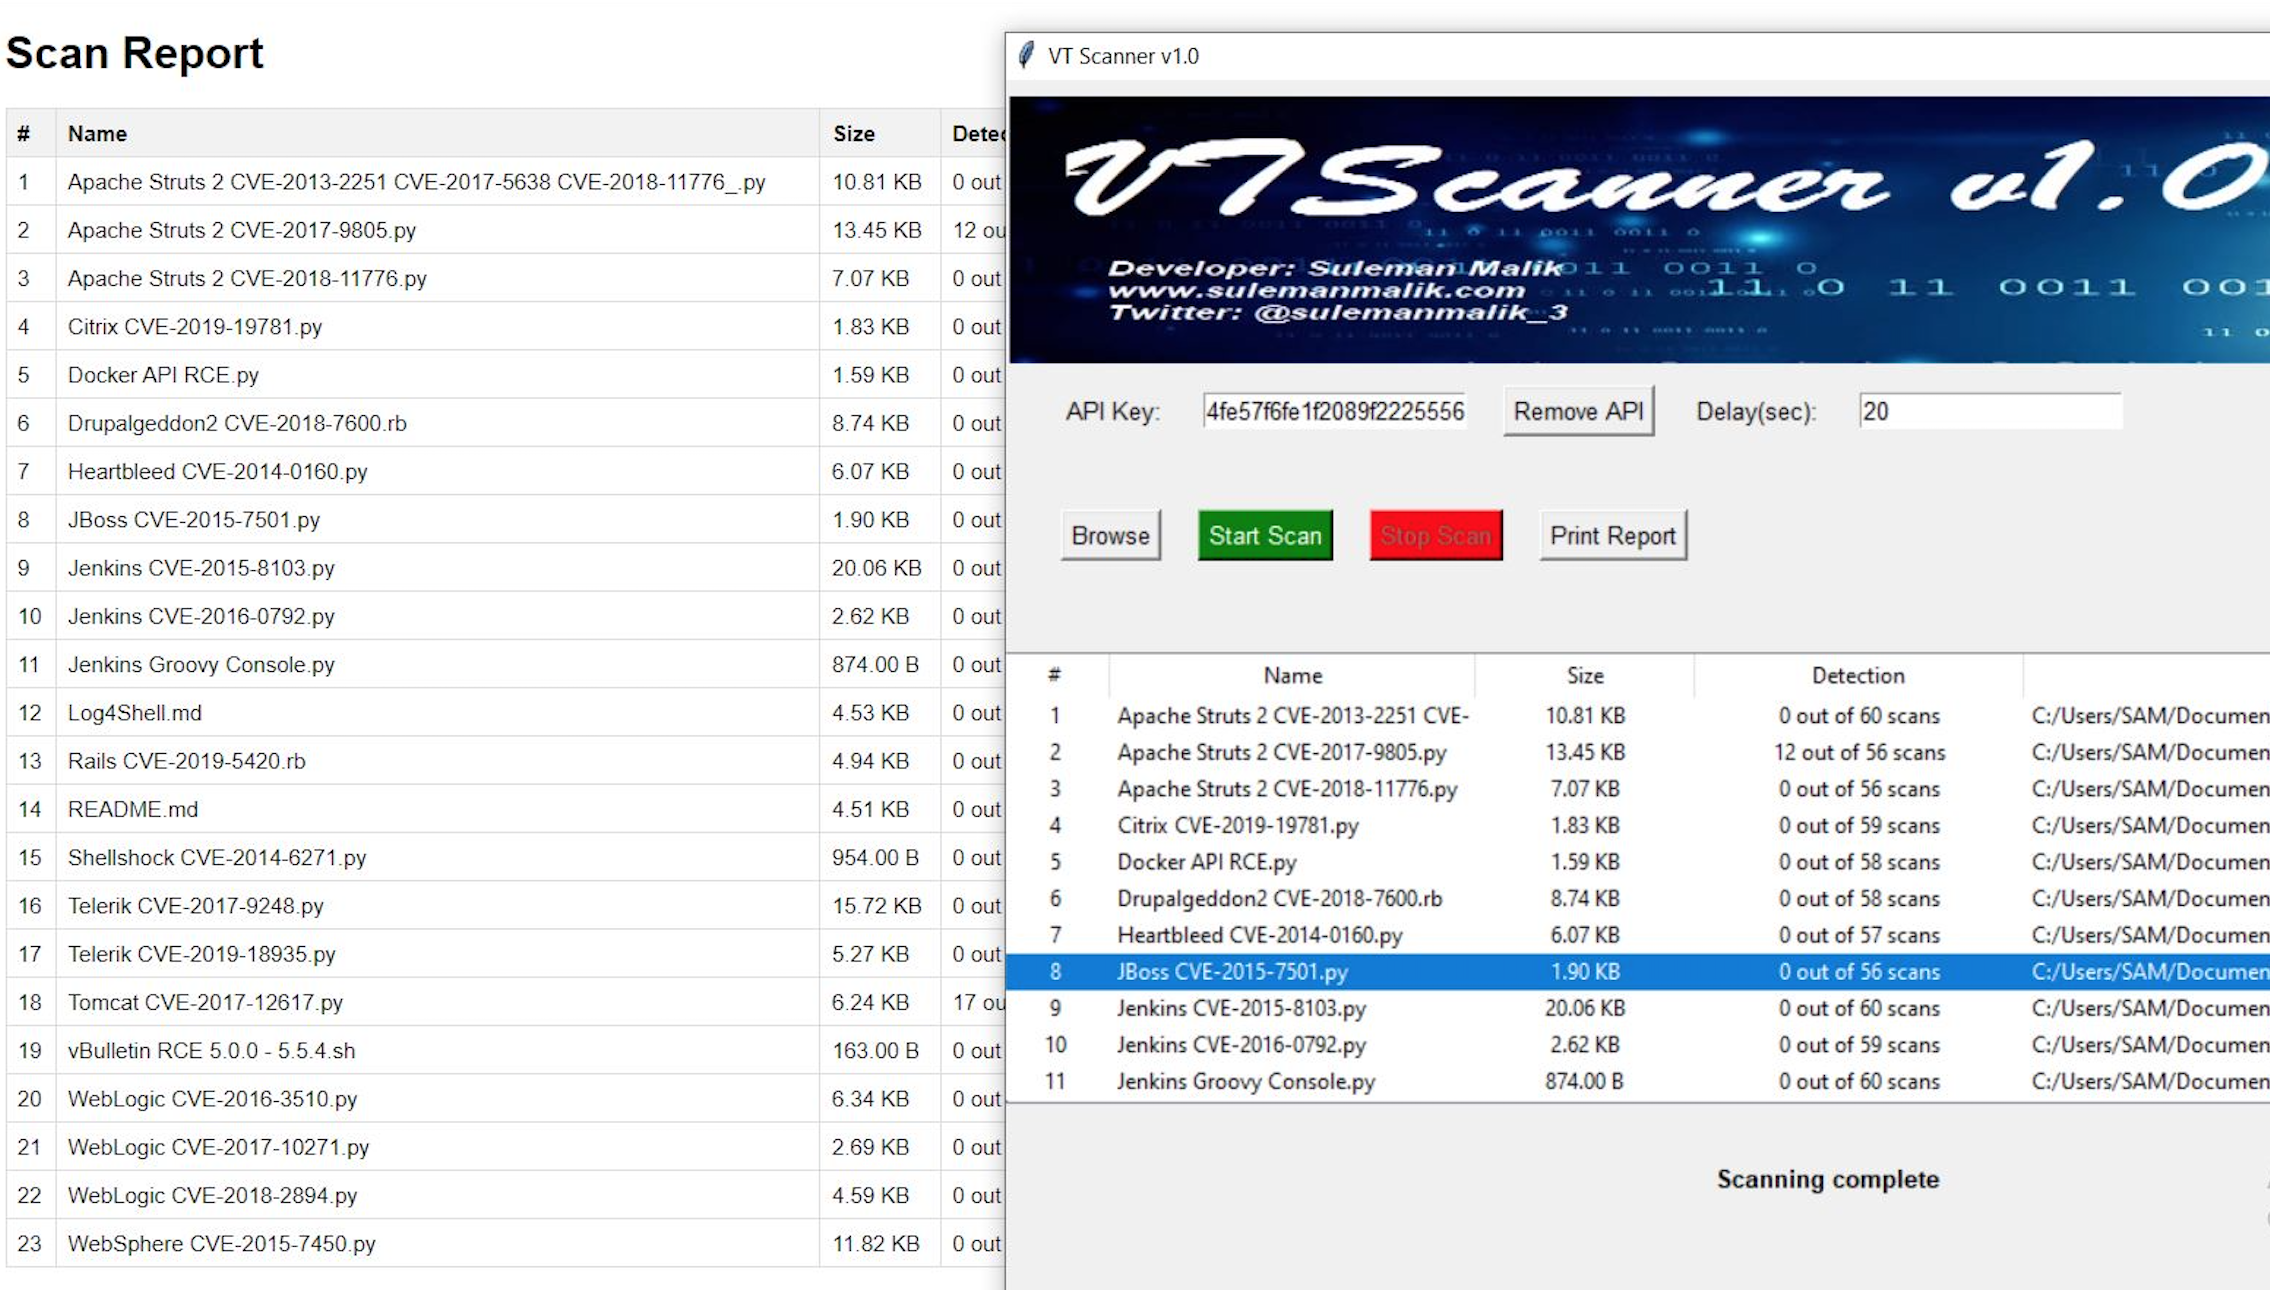 samhaxr/vtscanner
A comprehensive Python-based security tool for file scanning, malware detection, and analysis in an ever-evolving cyber landscape.
 ilmndwntr/cve-2026-41940-mass-exploit
Mass exploit tool for CVE-2026-41940 supporting single and mass scanning to automate exploitation of vulnerable targets.
 ssllabs/openssl-ccs-cve-2014-0224
Go-based tool for testing servers against the OpenSSL CCS injection vulnerability (CVE-2014-0224), using a patched TLS library to detect weak…
 talha1112/fyp
Desktop-based vulnerability assessment tool for security teams — scan web apps & networks, detect CVEs, map exploits, auto-score risk, and generate…
 4rt-net/mikrotrick_poc
Testing tool for the Mikrotrick exploit (CVE-2026-67276)