
Archived
local-log4j-vuln-scanner
 hillu/local-log4j-vuln-scanner
[Moved to Codeberg] Simple local scanner for vulnerable log4j instances
code-analysisdevsecopsstatic-analysis+3
hillu/local-log4j-vuln-scanner[Moved to Codeberg] Simple local scanner for vulnerable log4j instances
 01rabbit/pakuri
Semi-automated penetration testing framework with TUI, integrating Nmap, OpenVAS, Metasploit, and Faraday for streamlined information gathering,…
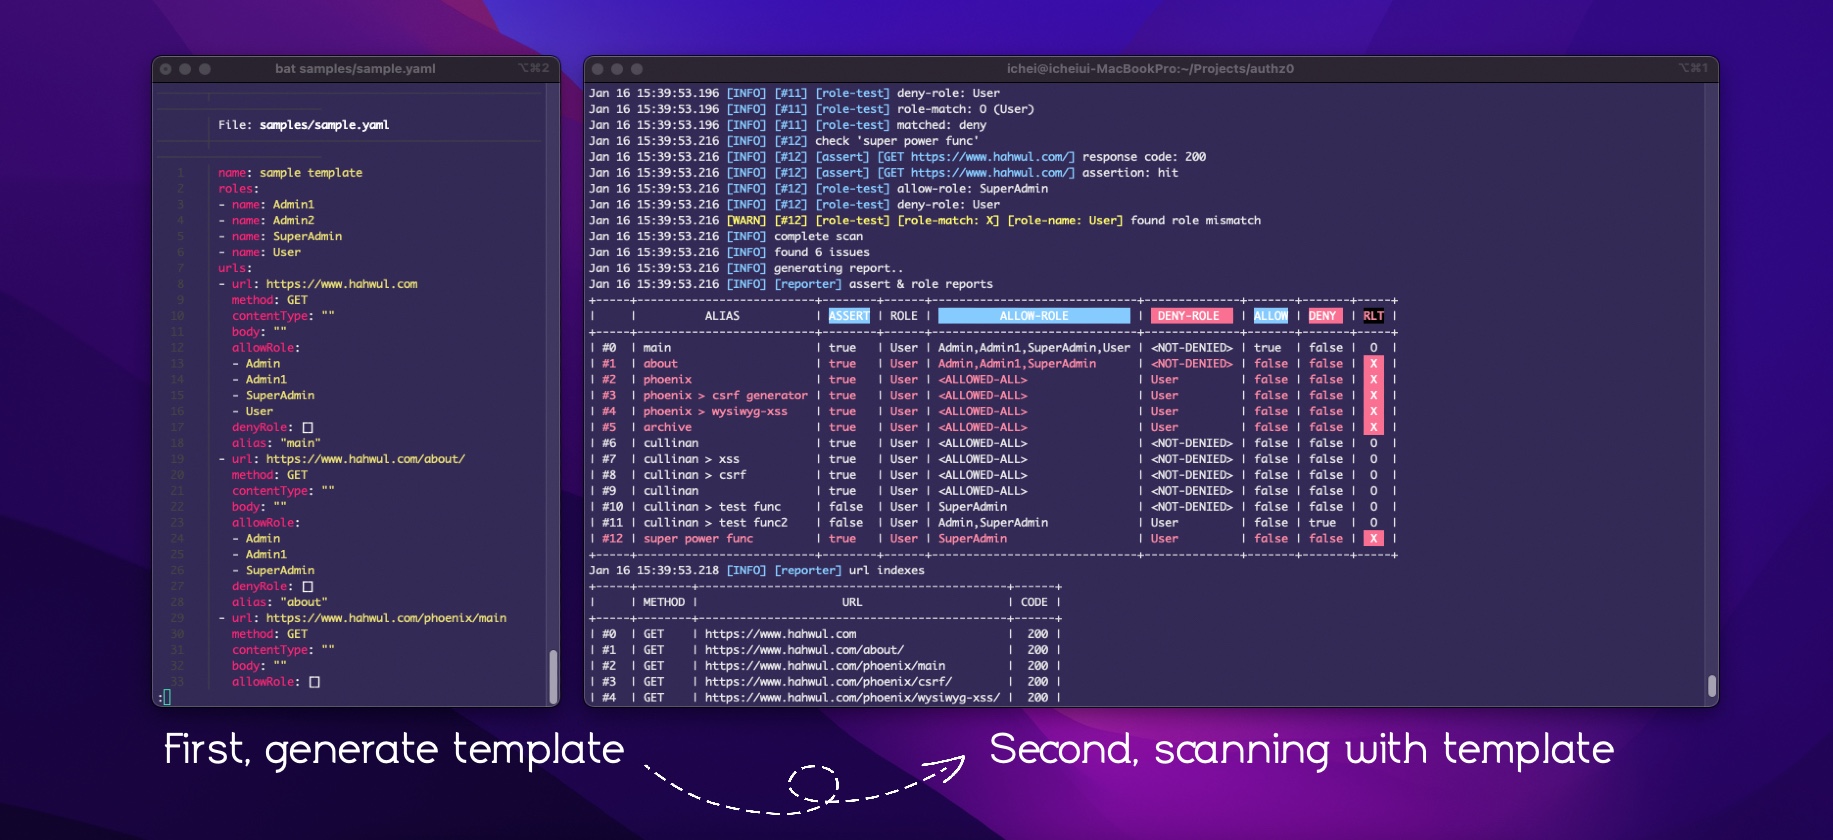 hahwul/authz0
Automated authorization testing tool that detects unauthorized access by scanning URLs with role-based credentials using YAML templates.
 codeskipper/python-patrol
Scan for python installations on macOS, and run CVE-2015-20107.py script to report if patching is needed