

MultiExploit
 vesu-nights/multiexploit
CVE-2023-21173 Exploit - Remote Code Execution in SQL Server 2022
authenticationdatabase-securityexploitation+3
vesu-nights/multiexploitCVE-2023-21173 Exploit - Remote Code Execution in SQL Server 2022
 randomrobbiebf/redis-checker
Checks for exposed Redis servers
 shanika04/dashbuilder
CVE-2016-4999
 paulsec/hqlmap
(Deprecated) HQLmap, Automatic tool to exploit HQL injections
 yym8538/cve-2026-30951
Proof-of-concept and vulnerable Node.js/Express/Sequelize app demonstrating CVE-2026-30951, a JSON cast-type SQL injection in Sequelize v6 where…
 yym8538/cve-2026-0603
Proof-of-concept and Docker lab reproducing CVE-2026-0603, a second-order SQL injection in Hibernate ORM bulk DELETE/UPDATE operations, with…
 wpscanteam/wpscan
WordPress security scanner that detects vulnerabilities, enumerates plugins/themes/users, and checks for weak passwords. Integrates with the WPScan…
 bi8d0/driversentinel
DriverSentinel is a security tool developed in Go that detects malicious and vulnerable drivers on Windows systems by comparing them against the…
 cycodelabs/raven
Scans GitHub Actions CI/CD workflows for security vulnerabilities, indexes findings into a Neo4j graph database, and provides a query library for…
 sonatype-nexus-community/devaudit
Open-source, cross-platform, multi-purpose security auditing tool
 farenhytee/database-sentinel
Open-source security audits for Supabase: a read-only MCP server, a CLI agent and a Claude Skill. Finds RLS misconfigurations, exposed keys and risky…
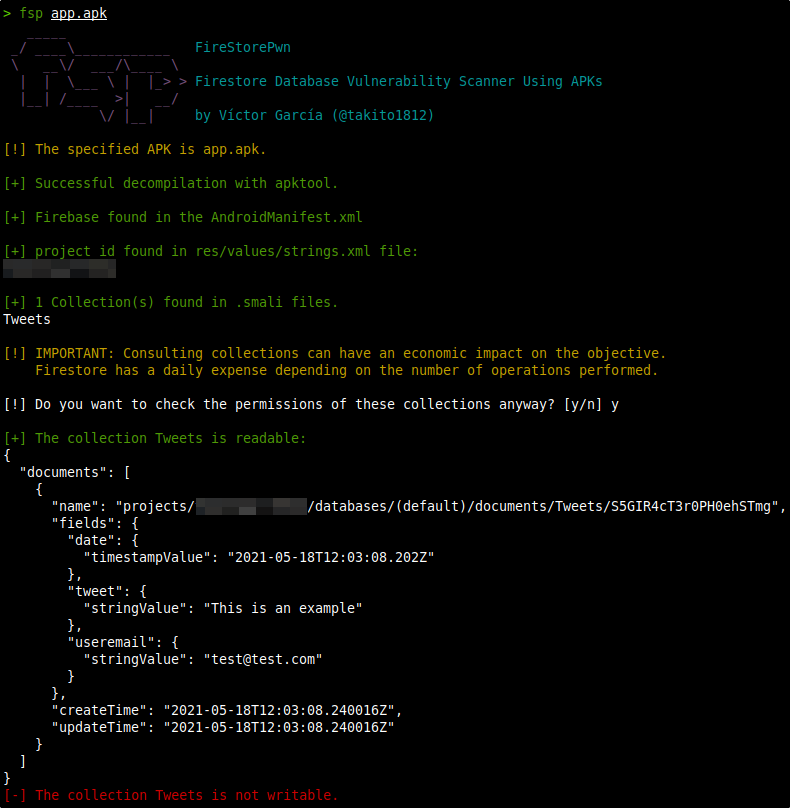 takito1812/firestorepwn
fsp - Firestore Database Vulnerability Scanner Using APKs
 securewithumer/exploit-index
The Ultimate CVE Proof of Concept (PoC) & Exploit Database. A zero-API, high-performance aggregator for 0days, vulnerabilities, and Threat…
 sqlmapproject/sqlmap
Automatic SQL injection and database takeover tool
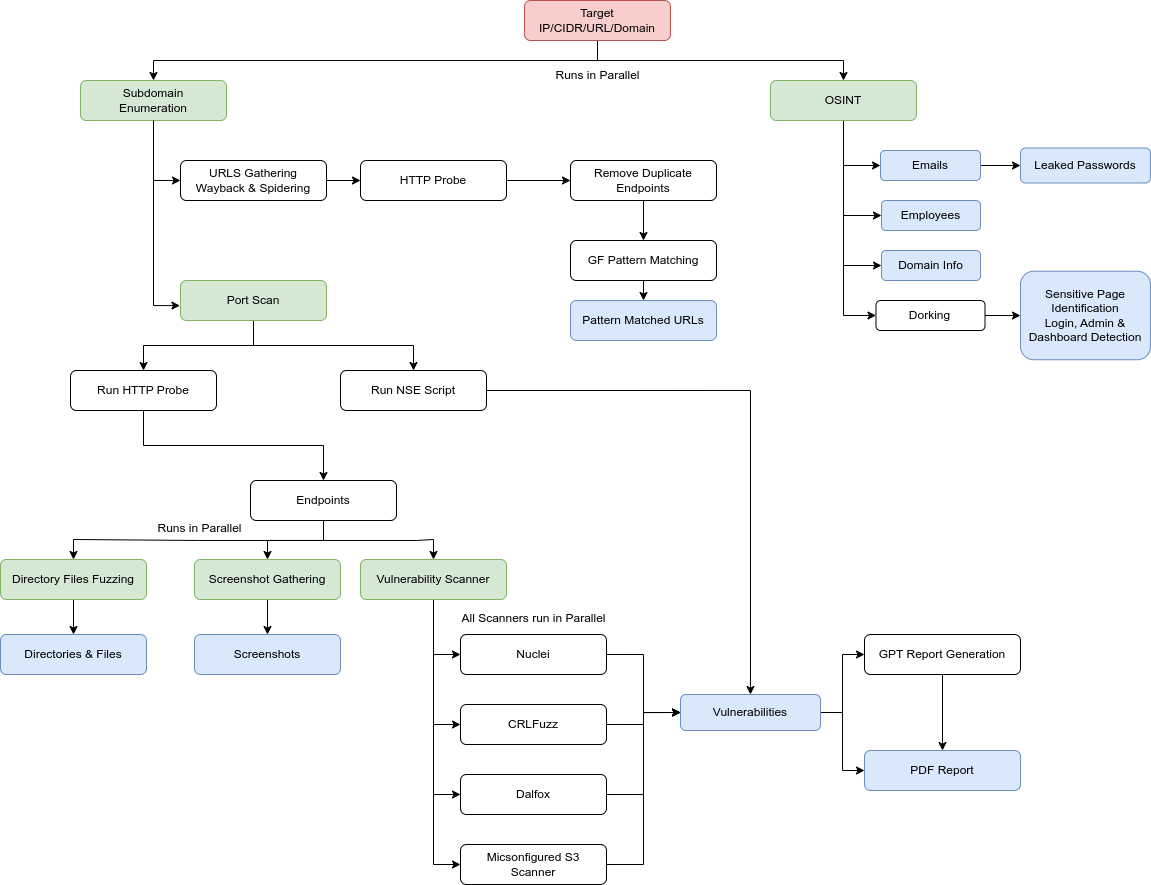 yogeshojha/rengine
reNgine is an automated reconnaissance framework for web applications with a focus on highly configurable streamlined recon process via Engines,…
 emposha/php-shell-detector
Web Shell Detector – is a php script that helps you find and identify php/cgi(perl)/asp/aspx shells. Web Shell Detector has a “web shells” signature…
 foospidy/dbdat
Db Database Assessment Tool