
yLog4j
 y-security/ylog4j
PortSwigger Burp Plugin for the Log4j (CVE-2021-44228)
api-security-testingexploitationpenetration-testing+2
y-security/ylog4jPortSwigger Burp Plugin for the Log4j (CVE-2021-44228)
 cropnet/ni8mare
Comprehensive vulnerability detection tool for n8n workflow automation instances. Detects the critical CVE-2026-21858 vulnerability (CVSS 10.0)…
 perufitlife/directus-security
Keyless active-probe security auditor for Directus CMS. Proves public-role data exposure, user enumeration, unauthenticated version/schema leaks,…
 amnnrth/cve-2025-34291_cors_security_scanner
A lightweight Python-based security assessment tool for detecting dangerous Cross-Origin Resource Sharing (CORS) misconfigurations - CVE-2025-34291.
 fevar54/forticlient_ems_cve_2026_35616_poc.py
PoC de CVE-2026-35616: control de acceso indebido en FortiClient EMS.
 functori/dev/gaia
Global API Integrity Assessor
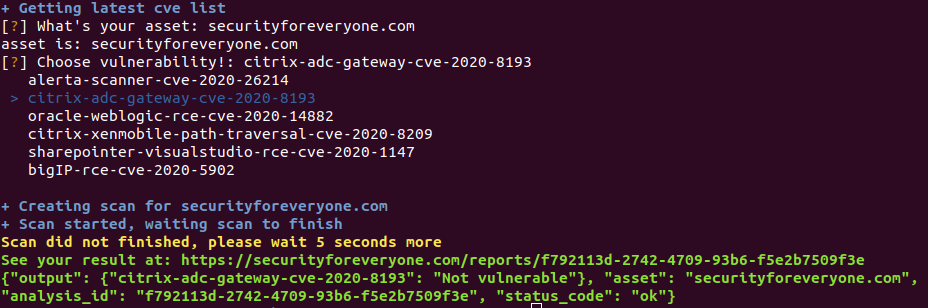 s4e-io-old-labs/s4e-cve-scanner
API-based scanner that retrieves and lists the latest Common Vulnerabilities and Exposures (CVEs) for automated security assessment and vulnerability…
 havoc10-sw/detect_polyfill_cve-2024-38537-
Here's a Python script that checks if the polyfill.io domain is present in the Content Security Policy (CSP) header of a given web application.
 corgizz/springcloud
Spring Cloud Config CVE-2019-3799|CVE_2020_5410 漏洞检测
 gsmith257-cyber/graphcrawler
GraphQL automated security testing toolkit
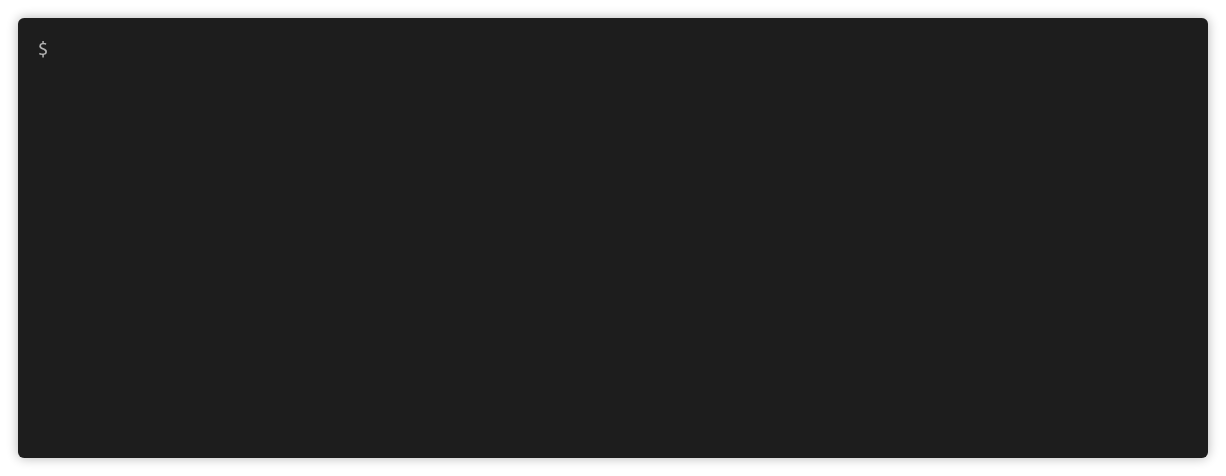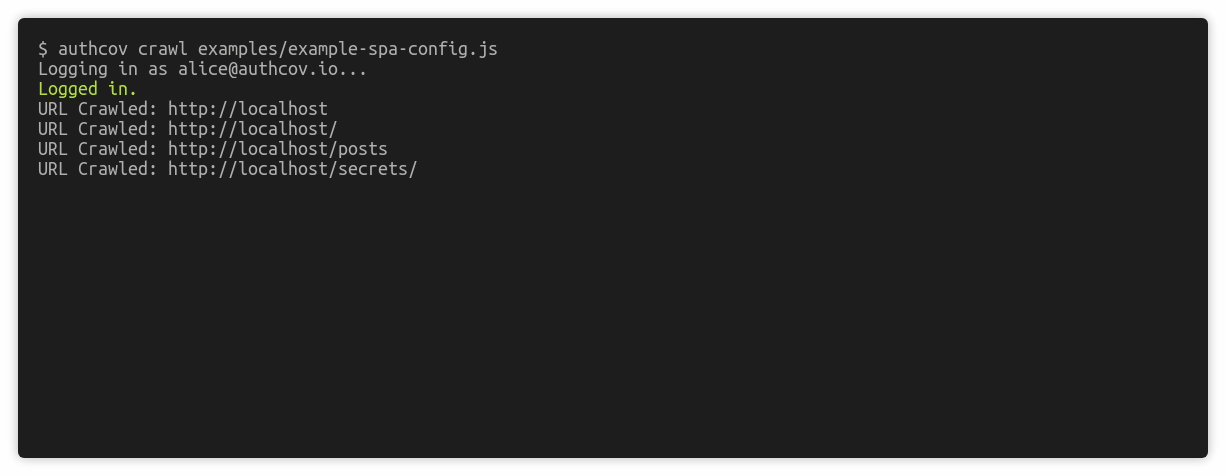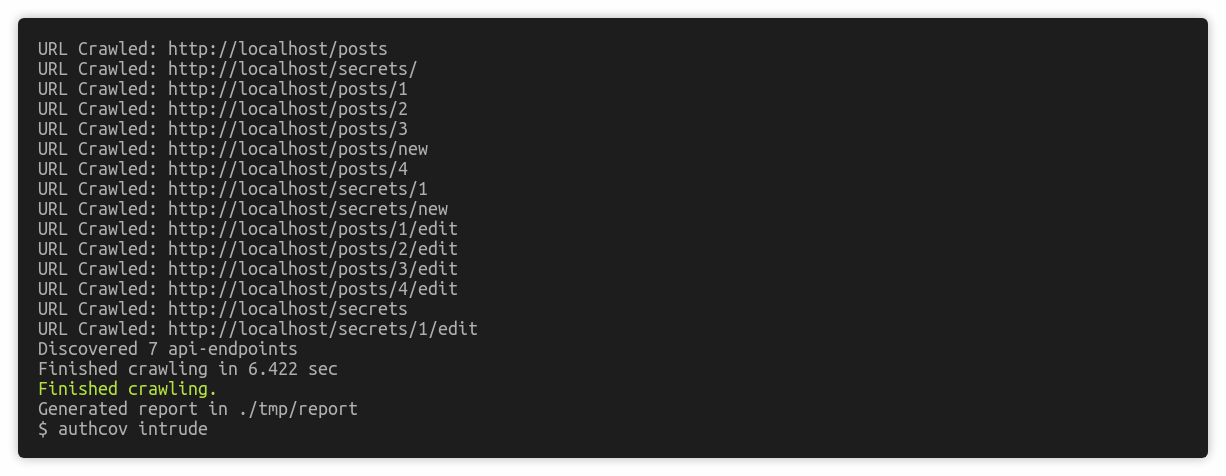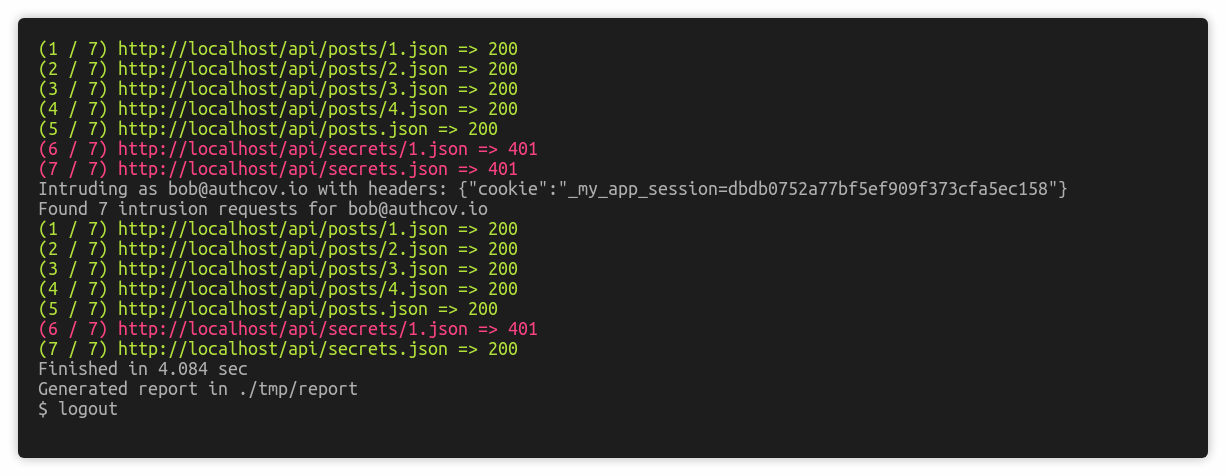 authcov/authcov
Web app authorisation coverage scanning
 openstack-archive/syntribos
Python API security testing tool from OpenStack Security Group
 vmware-archive/burp-rest-api
REST/JSON API to the Burp Suite security tool.
 google/nogotofail
An on-path blackbox network traffic security testing tool