
CVE-2026-41940
 dennisec/cve-2026-41940
Exploit script for CVE-2026-41940, an authentication bypass in cPanel/WHM using CRLF injection to gain admin access and change root password, with…
authentication-authorizationexploitationpenetration-testing+3
dennisec/cve-2026-41940Exploit script for CVE-2026-41940, an authentication bypass in cPanel/WHM using CRLF injection to gain admin access and change root password, with…
 sardine-web/automated-scanner-cve-2026-41940
Automated scanner & post-exploitation toolkit for CVE-2026-41940 — cPanel & WHM root authentication bypass via session-file CRLF injection
 hujiaozhuzhu/cve-2025-55182_liyon
Python-based exploit for CVE-2025-55182 (React Server Components RCE) with interactive shell, reverse shell, batch scanning, and Docker-based…
 oscar-mine/r2sae
Firefox extension for detecting and exploiting CVE-2025-55182 — Prototype Pollution RCE in Next.js React Server Actions
 ry-allan/tanstack-compromise-checker
Detects CVE-2026-45321 (TanStack supply chain compromise) and Mini Shai-Hulud worm artifacts. Scans node_modules, lockfiles, persistence hooks…
 epsilonpoint88-glitch/epsilonpoint-
Modular exploit framework targeting CVE-2026-23550 in WordPress, featuring mass exploitation, obfuscation, post-exploitation, and Docker-based C2…
 prowlsec/react2shell
An advanced command-line framework for discovery, validation, and exploitation of CVE-2025-55182 and CVE-2025-66478 affecting Next.js applications…
 gl1tch0x1/php_8.1.x_exploit
Automated detection & exploitation of critical PHP vulnerabilities (CVE-2024-4577 bypass, CVE-2025-14177, CVE-2025-14180, CVE-2025-14178)
 itsismarcos/sneeitscanner-cve-2025-6389
SneeitScanner - PoC & Scanner para RCE não autenticada no Sneeit Framework (CVE-2025-6389)
 atastycookie/cve-2025-55182
Python CLI exploit and scanner for CVE-2025-55182, a critical RCE in React Server Components, with command execution and nuclei-based detection.
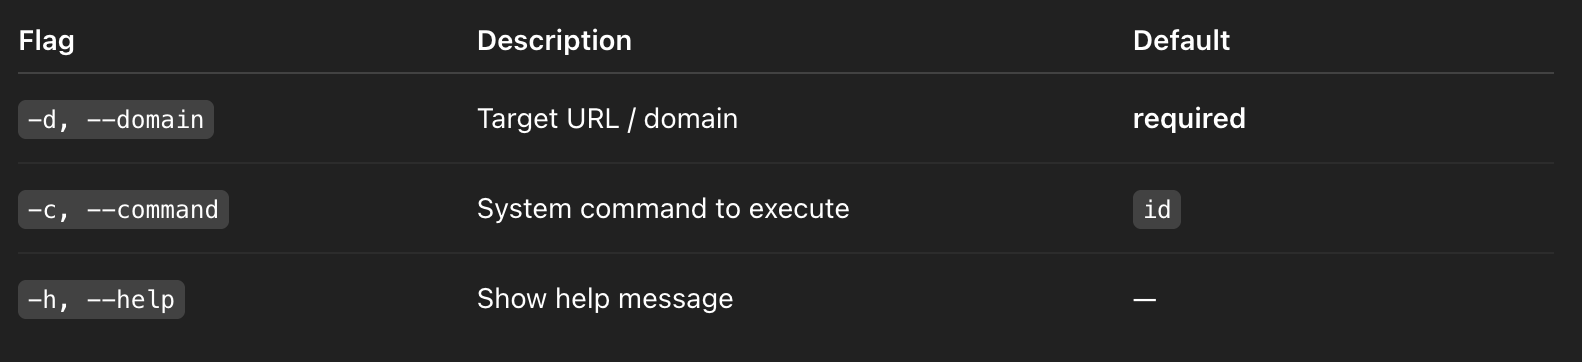 devvaibhav07/poc-cve-2025-55182
POC-CVE-2025-55182
 bambooqj/cve-2025-3248
Langflow 在对用户提交的“验证代码”做 AST 解析和编译时,在未做鉴权与沙箱限制的情况下调用了 Python 的 compile()/exec()(以及在编译阶段会评估函数默认参数与装饰器),攻击者可把恶意载荷放在参数默认值或装饰器里,借此在服务器上下文中执行任意语句(反弹…
 mantanhacker/mass-cve-2025-29306
Mass Exploit for CVE-2025-29306
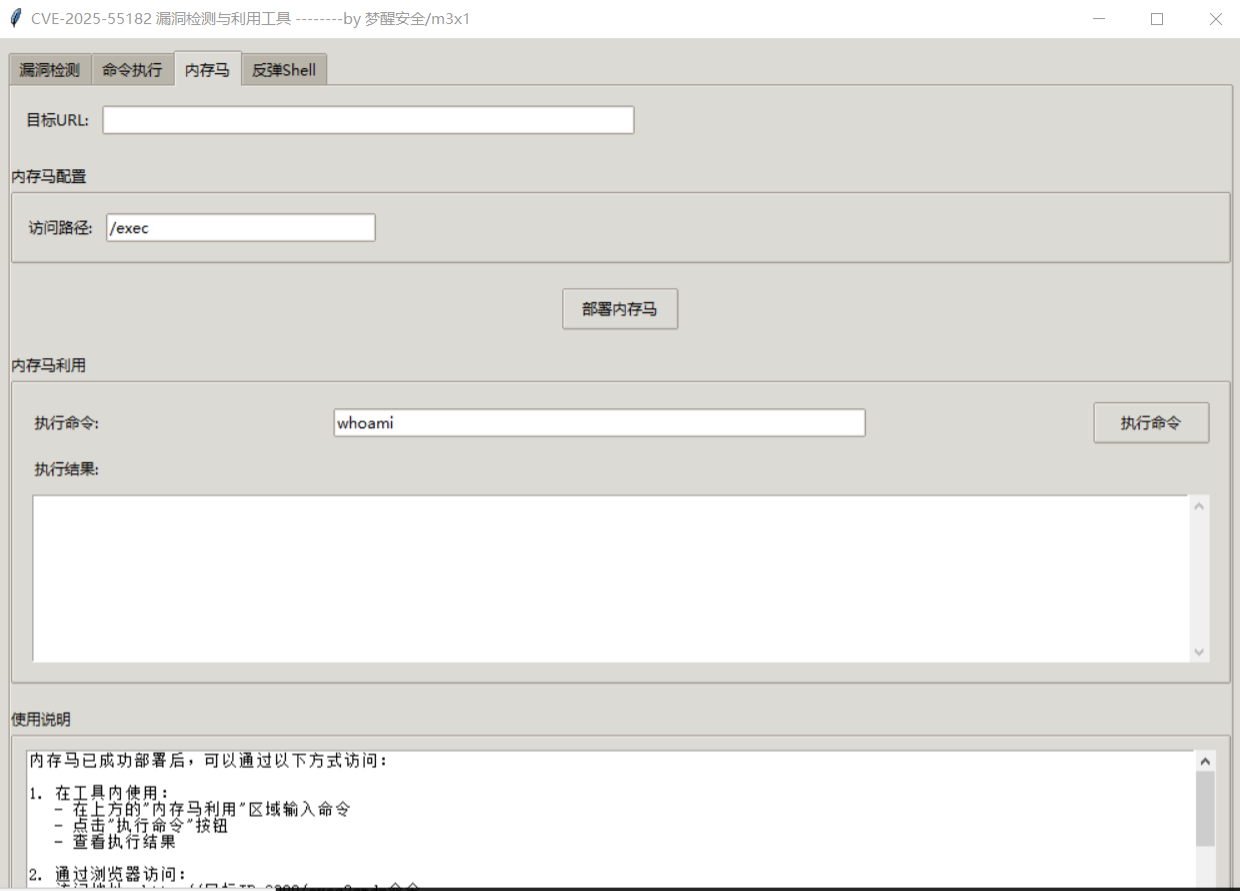 m3ngx1ng/cve-2025-55182-gui
CVE-2025-55182 漏洞检测与利用工具(GUI版)
 imbas007/auth-bypass-cve-2025-40554
Proof-of-concept exploit for CVE-2025-40554, an authentication bypass in SolarWinds Web Help Desk. Includes Nuclei template and Python exploit for…
 0xsj/cve-2025-55182
Proof-of-concept scanner for CVE-2025-55182, an unauthenticated RCE in React Server Components. Supports batch scanning, JSON/CSV export, and…
 aratane/cve-2024-9474
Palo Alto RCE Vuln
 amitlttwo/cve-2022-1388
Python-based exploit for CVE-2022-1388, an F5 BIG-IP iControl REST authentication bypass leading to remote code execution. Supports single URL,…