

Web-App-PenTesting
 sarthak4126/web-app-pentesting
Web application penetration testing lab — vulnerable Flask app, automated scanner, and professional pentest report. Covers OWASP Top 10, SQLi, XSS,…
educationlabs-practicepenetration-testing+4
sarthak4126/web-app-pentestingWeb application penetration testing lab — vulnerable Flask app, automated scanner, and professional pentest report. Covers OWASP Top 10, SQLi, XSS,…
 johenlastgen-jlg/cve-2025-6325_cve-2025-6327
Python PoC validating CVE-2025-6325 unauthenticated privilege escalation and CVE-2025-6327 arbitrary file upload RCE in King Addons for Elementor <=…
 murrez/cve-2026-84434
Python PoC scanner and exploit for CVE-2026-84434, an unauthenticated arbitrary file upload in Gravity Forms <=3.1.0.4 via hidden File Upload fields.…
 matakucing-ofc/cve-2026-49049
Python scanner and proof-of-concept for CVE-2026-49049, an arbitrary file write in Joomla Helix3 that enables PHP web shell upload and remote code…
 johenlastgen-jlg/cve-2026-18351
Mass exploit tool for CVE-2026-18351, an unauthenticated arbitrary file upload to RCE in Elementor Forms <= 1.6.0, with passive probing, shell…
 anggatechi/cve-2026-3844
CVE-2026-3844 — Unauthenticated Arbitrary File Upload to RCE in Breeze Cache (WordPress). CVSS 9.8 CRITICAL. Mass scanner + auto shell injector with…
 mohammad-008/rsfiles-cve-2026-57827
Unauthenticated File Upload → RCE PoC for CVE-2026-57827 (RSFiles! Joomla < 1.17.12). Authorized security research use only.
 hurrrraaaa/cve-2021-21972
Isolated lab research writeup for VMware vCenter Server CVE-2021-21972, covering unauthenticated arbitrary file upload to RCE, Nmap-based detection,…
 madexploits/ninja-form-exploit
CVE-2026-0740
 0xdenis77/cve-2026-56291
Mendeteksi versi (passive detection) & Exploitation CVE POC
 caterscam/cve-2026-5524-poc
Mass exploit toolkit for CVE-2026-5524, an unauthenticated file upload RCE in Divi Form Builder. Features multi-threaded scanning, WAF bypass…
 iicaicai/cve-2026-5524-poc
Python mass-exploit toolkit for CVE-2026-5524, an unauthenticated file upload RCE in the WordPress Divi Form Builder plugin, with webshell upload and…
 shinthink/pbck-exploit
📤 Mass exploitation framework for CVE-2026-56290 — Page Builder CK Joomla unauthenticated file upload to RCE
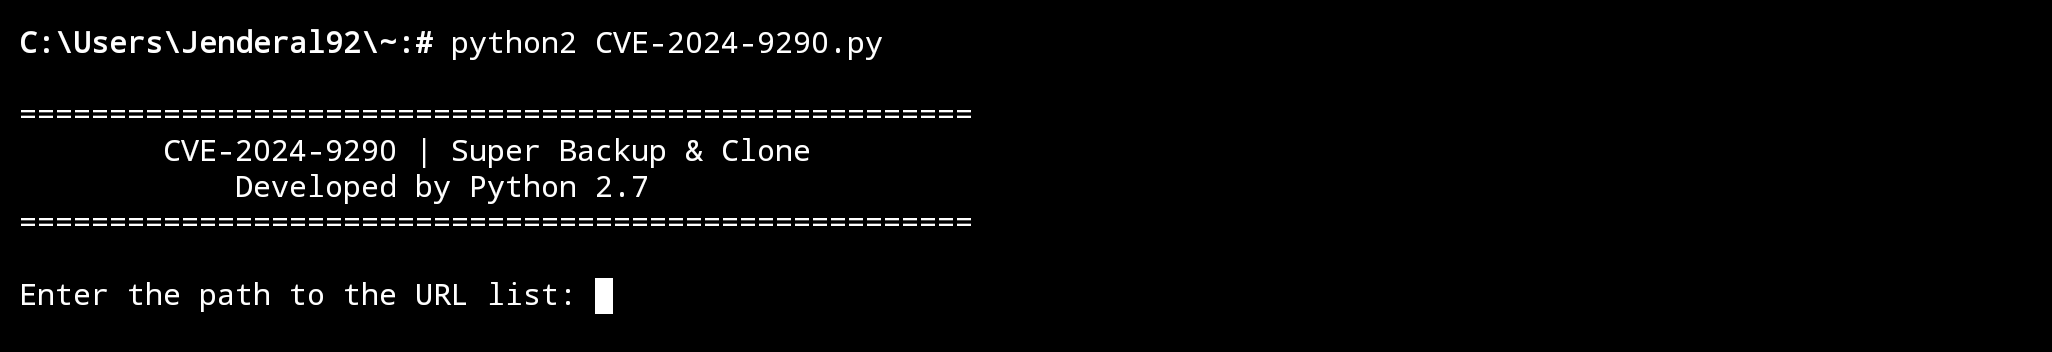 jenderal92/cve-2024-9290
The tool targets WordPress websites that use the Super Backup & Clone plugin and are vulnerable to arbitrary file upload.
 xxconi/cve-2026-6271
Automated scanner for CVE-2026-6271, a critical unauthenticated arbitrary file upload leading to RCE in the WordPress Career Section plugin. Supports…
 xxconi/cve-2026-2942
Automated scanner for unauthenticated arbitrary file upload and remote code execution in ProSolution WP Client (CVE-2026-2942). Supports…
 murrez/cve-2026-0740
Exploit script for CVE-2026-0740 targeting Ninja Forms file upload endpoints to upload a PHP shell, scanning a list of URLs and logging successful…
 0xgh057r3c0n/cve-2026-3844
WordPress - Breeze Cache <= 2.4.4 - Unauthenticated Arbitrary File Upload