
CVE-2026-66066
 hackspeak/cve-2026-66066
CVE-2026-66066 (KindaRails2Shell) PoC - Rails Active Storage/libvips arbitrary file read to RCE; for authorized security testing
exploitationinformation-gatheringpenetration-testing+5
3
hackspeak/cve-2026-66066CVE-2026-66066 (KindaRails2Shell) PoC - Rails Active Storage/libvips arbitrary file read to RCE; for authorized security testing
 0xsha/kindarails2shell
Single-file PoC for Rails CVE-2026-66066: arbitrary file read, secret recovery, threaded scanning, and conditional RCE via signed image variations.
 random-robbie/cve-2019-5418
Go-based scanner for CVE-2019-5418 (Ruby on Rails file disclosure) that reads a list of websites and tests for the vulnerability using a burl-derived…
 mikesplain/cve-2014-3566-poodle-cookbook
Chef cookbook that detects and fails runs on servers vulnerable to CVE-2014-3566 (POODLE) by scanning specified SSL ports, serving as both a security…
 heroku/heroku-cve-2013-0333
Scans Heroku applications for a critical Rails remote code execution vulnerability (CVE-2013-0333) and identifies unpatched instances requiring…
 heroku/heroku-cve-2013-0156
Inspect all of your heroku apps to see if they are running a vulnerable version of Rails
 m0nad/hellraiser
Vulnerability scanner using Nmap for scanning and correlating found CPEs with CVEs.
 presidentbeef/brakeman
A static analysis security vulnerability scanner for Ruby on Rails applications
 thesp0nge/dawnscanner
Dawn is a static analysis security scanner for ruby written web applications. It supports Sinatra, Padrino and Ruby on Rails frameworks.
 duriantaco/ravage
Evidence first autonomous web security testing for controlled, authorized targets. With reproducible labs, audit trails, reports, and XBEN…
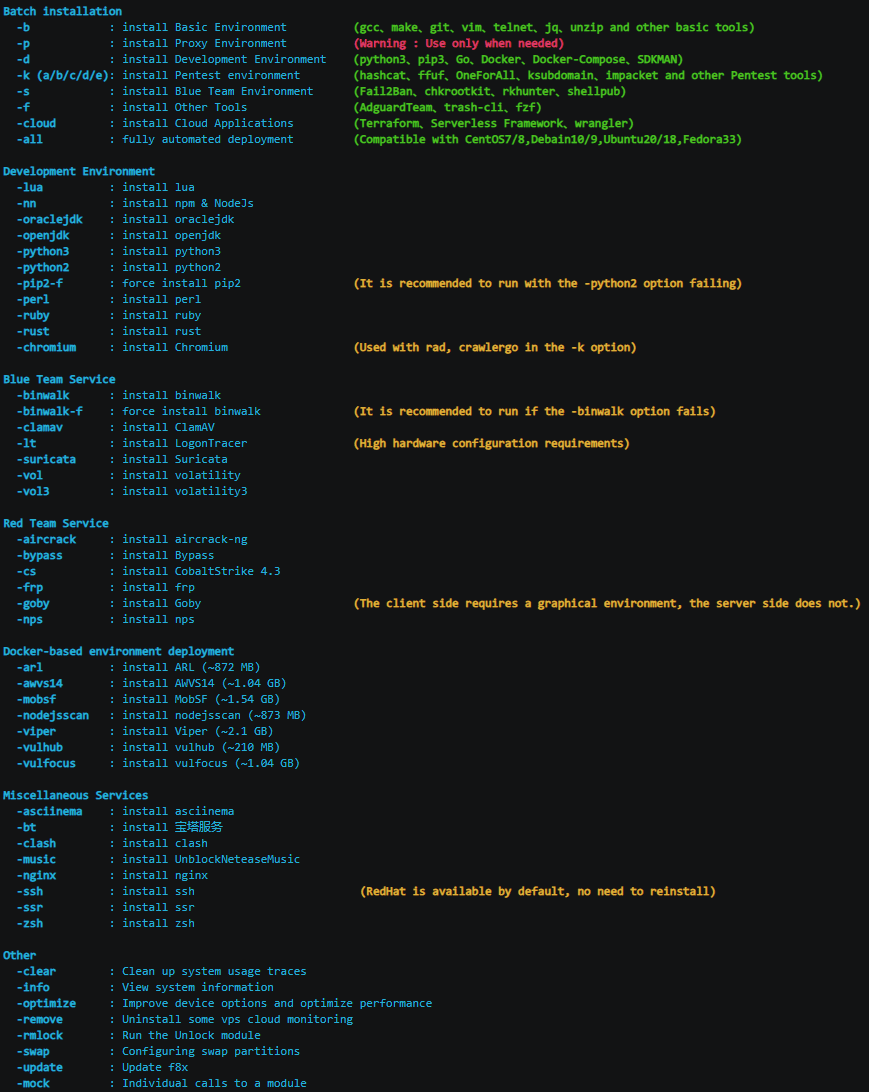 ffffffff0x/f8x
红/蓝队环境自动化部署工具 | Red/Blue team environment automation deployment tool