

reburp
 forefy/reburp
A Burp Suite extension that exposes the full Montoya API as a local REST API, with Swagger UI
ai-securityapi-security-testingfuzzing+7
forefy/reburpA Burp Suite extension that exposes the full Montoya API as a local REST API, with Swagger UI
 coactionbrittlemaidenhair51/cve-2026-42978-poc-research
Exploit and analyze CVE-2026-42978 with a Windows Push Notifications module for AI security, multi-protocol terminal, and autonomous agent suite.
 hashgraph-online/hol-guard
Open-source antivirus for AI agents: block risky tools, secret access, prompt injection, malicious packages, MCP servers, plugins, and skills at…
 xiaoqimikko/async-http-client-check
Self-hosted AI workspace with agents, skills, and tools (Gmail, Calendar) that runs entirely on your own provider API keys (BYOK). Bring your own…
 solivaquaant/cve-2026-85706
Proof-of-concept and reproduction lab for CVE-2026-85706, an unauthenticated path-traversal file read in GitLab CE/EE repository commits and files…
 xiaoqimikko/jetty-line-check
CVE-2026-2332 and 4 more 2026 Jetty CVEs: which does your Jetty (or Spring Boot) build hit, and does the fixed version Jetty names even exist on…
 hahwul/gori
A fast, keyboard-driven HTTP intercepting proxy and hacking & pentesting toolkit for the terminal.
 eugexo/security-baseline-ubuntu
Production-grade Security Baseline & Hardening Guide for Ubuntu 24.04/26.04 LTS. Kernel isolation, Emergency Panic Button, custom AppArmor/Firejail…
 dev-sec/puppet-os-hardening
This puppet module provides numerous security-related configurations, providing all-round base protection.
 xiaoqimikko/thymeleaf-check
Offline checker for Thymeleaf CVE-2026-40477 / CVE-2026-41901 — tells you which of the two CVSS 9.0 SSTI flaws you are exposed to, and whether your…
 xiaoqimikko/tomcat-line-check
CVE-2026-24880: does Apache's upgrade advice actually apply to your Tomcat? Detects the fix by class presence, not version comparison. Covers…
 hackervlogofficial/cve-2026-23918
This is a proactive tool for security auditing. For your GitHub repository, you’ll want a description that highlights its safety (non-intrusive) and…
 robrankin/cve-2021-44228-waf-tests
Testing WAF protection against CVE-2021-44228 Log4Shell
 mebibite/log4jhound
Created after the disclosure of CVE-2021-44228. Bash script that detects Log4j occurrences in your projects and systems, allowing you to get insight…
 hargabyte/cve-scanner
Local CVE scanner for OpenClaw that checks versions against 522+ known vulnerabilities, displays recent HIGH-severity CVEs, and recommends upgrades.…
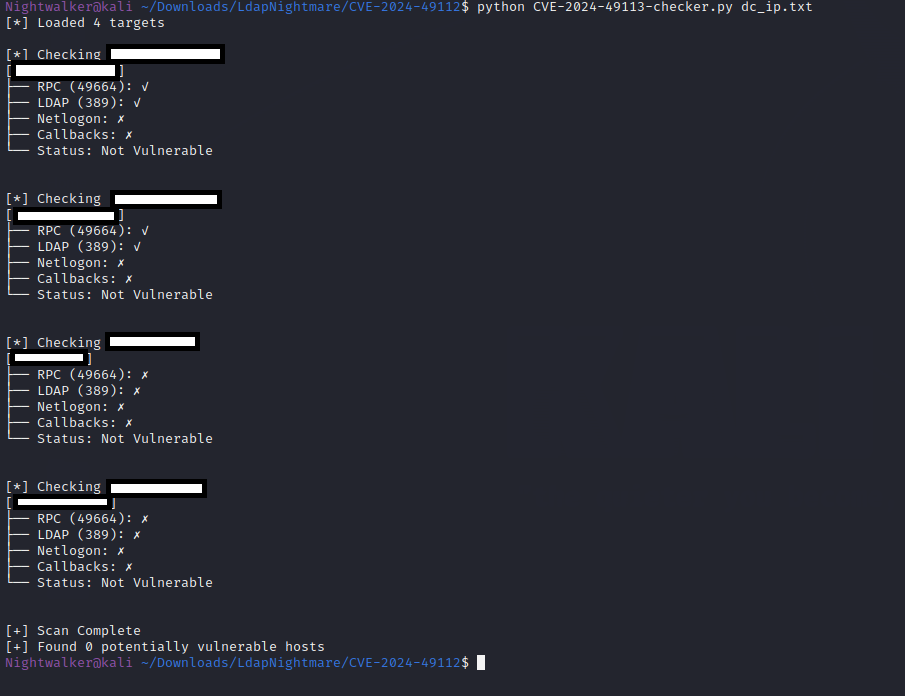 barcrange/cve-2024-49113-checker
Checks if a system is potentially vulnerable to CVE-2024-49113 (LDAP Nightmare) by testing RPC connectivity, LDAP ports, Netlogon service, and LDAP…
 atalovesyou/openclaw-security-checker
Check if your AI agent setup is vulnerable to CVE-2026-33579
 praiseimafidon/version_vulnerability_scanner
A vulnerability scanner for Firefox and Thunderbird that checks if your versions are out of date and susceptible to CVE-2024-9680.