hijagger
 firefart/hijagger
Checks all maintainers of all NPM and Pypi packages for hijackable packages through domain re-registration
dns-analysisosintreconnaissance+3
firefart/hijaggerChecks all maintainers of all NPM and Pypi packages for hijackable packages through domain re-registration
 synacktiv/depfuzzer
Scans project dependencies for dependency confusion vulnerabilities and checks package owner email takeover risks across multiple registries (npm,…
 rdoix/cve-2024-21762-checker
Shodan-based scanner that discovers FortiGate SSL VPN devices and tests them for CVE-2024-21762 vulnerability, displaying organization and country…
 ghostwirez/cve-2024-9326-poc
Automated PoC exploit for CVE-2024-9326, a SQL injection vulnerability in PHPGurukul Online Shopping Portal v2.0, enabling security professionals to…
 andripwn/pulse-exploit
Pulse Secure SSL VPN exploit (CVE-2019-11510) using hosts retrieved from Shodan API.
 soliux/cve-2021-41773
On the 11/11/21 the apache 2.4.49-2.4.50 remote command execution POC has been published online and this is a loader so that you can mass exploit…
 xaanziu/cve-2026-5513
CVE-2026-5513: Bookly <= 27.2 Stored XSS via Cookie (Unauthenticated)
 crussella0129/tricorne
a Fedora remix focused on pentesting and purple hat tooling
 flipkart-incubator/rta
Red team Arsenal - An intelligent scanner to detect security vulnerabilities in company's layer 7 assets.
 detexploit/detexploit
OSS Vulnerability Scanner for Windows Platform
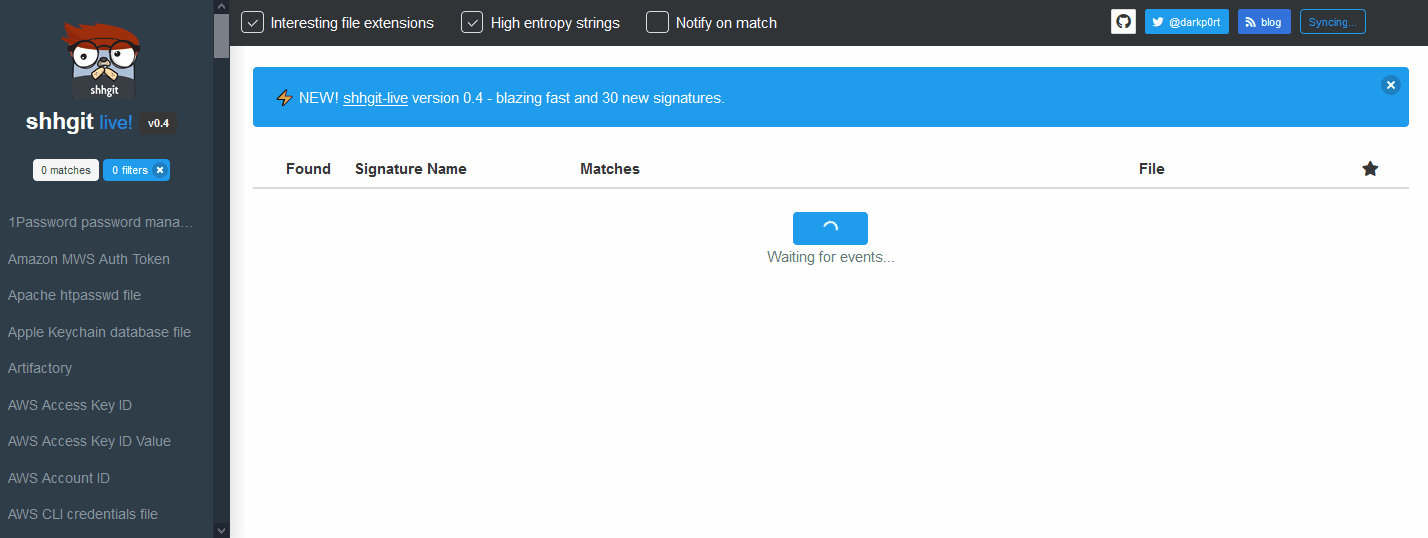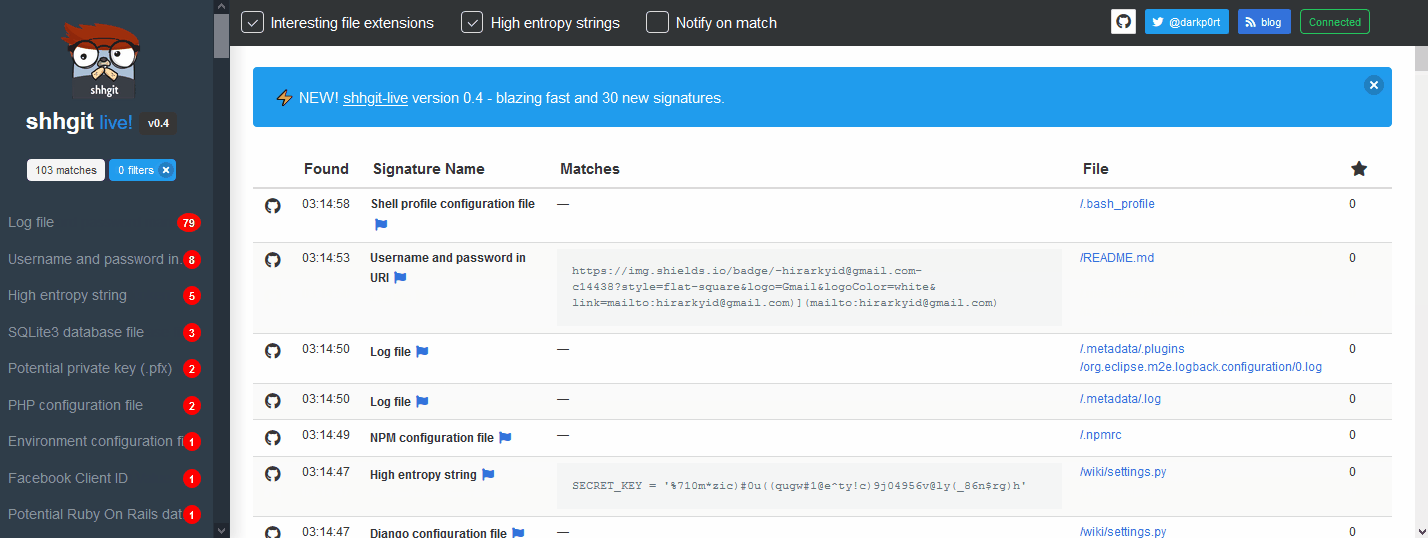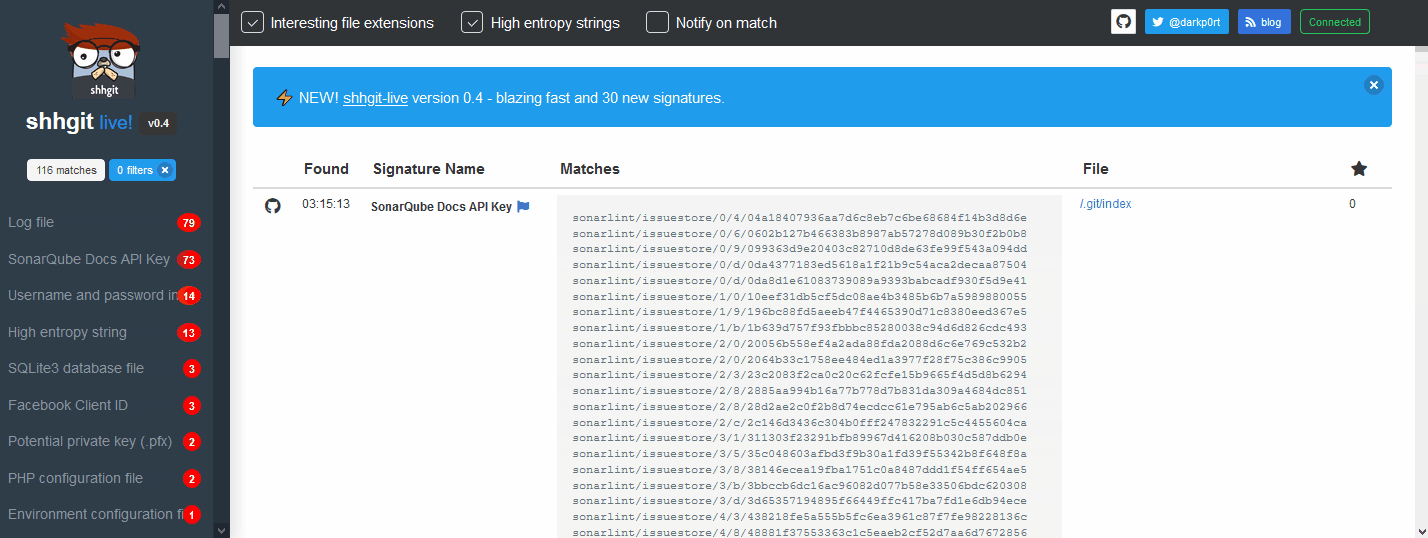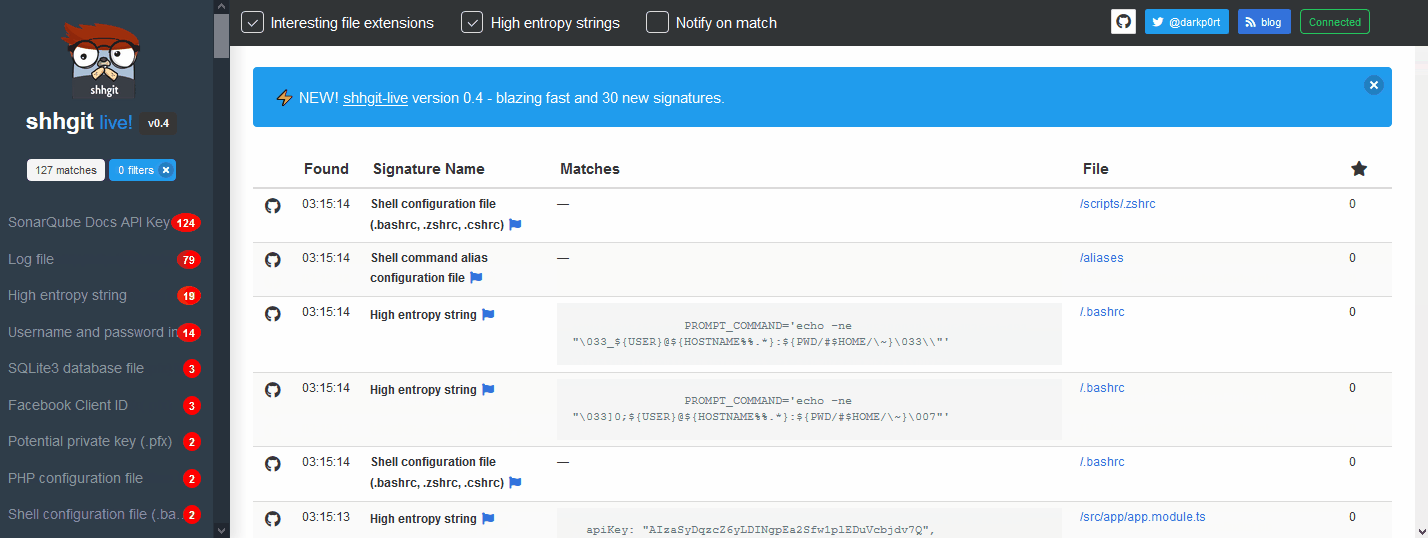 eth0izzle/shhgit
Ah shhgit! Find secrets in your code. Secrets detection for your GitHub, GitLab and Bitbucket repositories.
 storenth/lazyrecon
Wicked sick v2.0 script is intended to automate your reconnaissance process in an organized fashion.
 morpheuslord/nmap-api
RESTful API wrapping Nmap for automated network scanning, port detection, service enumeration, and vulnerability analysis with optional AI-powered…
 mfmokbel/crawlector
Crawlector is a threat hunting framework designed for scanning websites for malicious objects.
 xcapri/subdosec
Fast, accurate subdomain takeover scanner with zero false positives. Detects vulnerable subdomains, collects metadata (IP, CNAME, title, status…
 sobri3195/pegasus-neo
PEGASUS-NEO is a comprehensive penetration testing framework designed for security professionals and ethical hackers. It combines multiple security…