
Crawlector
 mfmokbel/crawlector
Crawlector is a threat hunting framework designed for scanning websites for malicious objects.
crawlerinformation-gatheringmalware-analysis+5
1239 months ago
mfmokbel/crawlectorCrawlector is a threat hunting framework designed for scanning websites for malicious objects.
 sobri3195/pegasus-neo
PEGASUS-NEO is a comprehensive penetration testing framework designed for security professionals and ethical hackers. It combines multiple security…
 firefart/hijagger
Checks all maintainers of all NPM and Pypi packages for hijackable packages through domain re-registration
 xcapri/subdosec
Fast, accurate subdomain takeover scanner with zero false positives. Detects vulnerable subdomains, collects metadata (IP, CNAME, title, status…
 morpheuslord/nmap-api
RESTful API wrapping Nmap for automated network scanning, port detection, service enumeration, and vulnerability analysis with optional AI-powered…
 flipkart-incubator/rta
Red team Arsenal - An intelligent scanner to detect security vulnerabilities in company's layer 7 assets.
 synacktiv/depfuzzer
Scans project dependencies for dependency confusion vulnerabilities and checks package owner email takeover risks across multiple registries (npm,…
 storenth/lazyrecon
Wicked sick v2.0 script is intended to automate your reconnaissance process in an organized fashion.
 rdoix/cve-2024-21762-checker
Shodan-based scanner that discovers FortiGate SSL VPN devices and tests them for CVE-2024-21762 vulnerability, displaying organization and country…
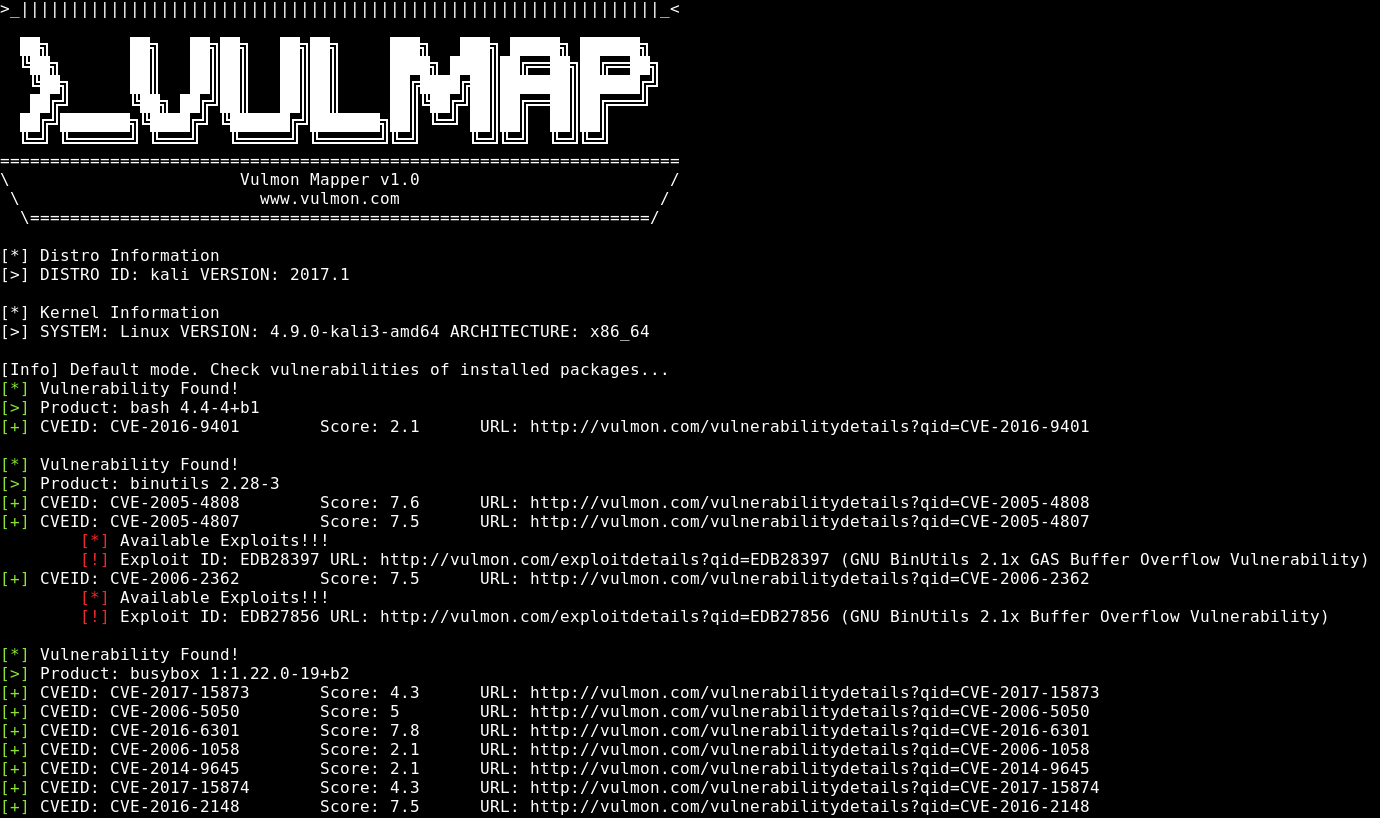 vulmon/vulmap
Vulmap Online Local Vulnerability Scanners Project
 andripwn/pulse-exploit
Pulse Secure SSL VPN exploit (CVE-2019-11510) using hosts retrieved from Shodan API.
 xaanziu/cve-2026-5513
CVE-2026-5513: Bookly <= 27.2 Stored XSS via Cookie (Unauthenticated)