
LibPNG_OSS-Fuzz
 enessar/libpng_oss-fuzz
Security research project on fuzzing libpng with OSS-Fuzz. Includes seed corpus analysis, custom read/write fuzzers, and a proof-of-concept exploit…
binary-analysiscode-analysiseducation+3
1
enessar/libpng_oss-fuzzSecurity research project on fuzzing libpng with OSS-Fuzz. Includes seed corpus analysis, custom read/write fuzzers, and a proof-of-concept exploit…
 google/oss-fuzz
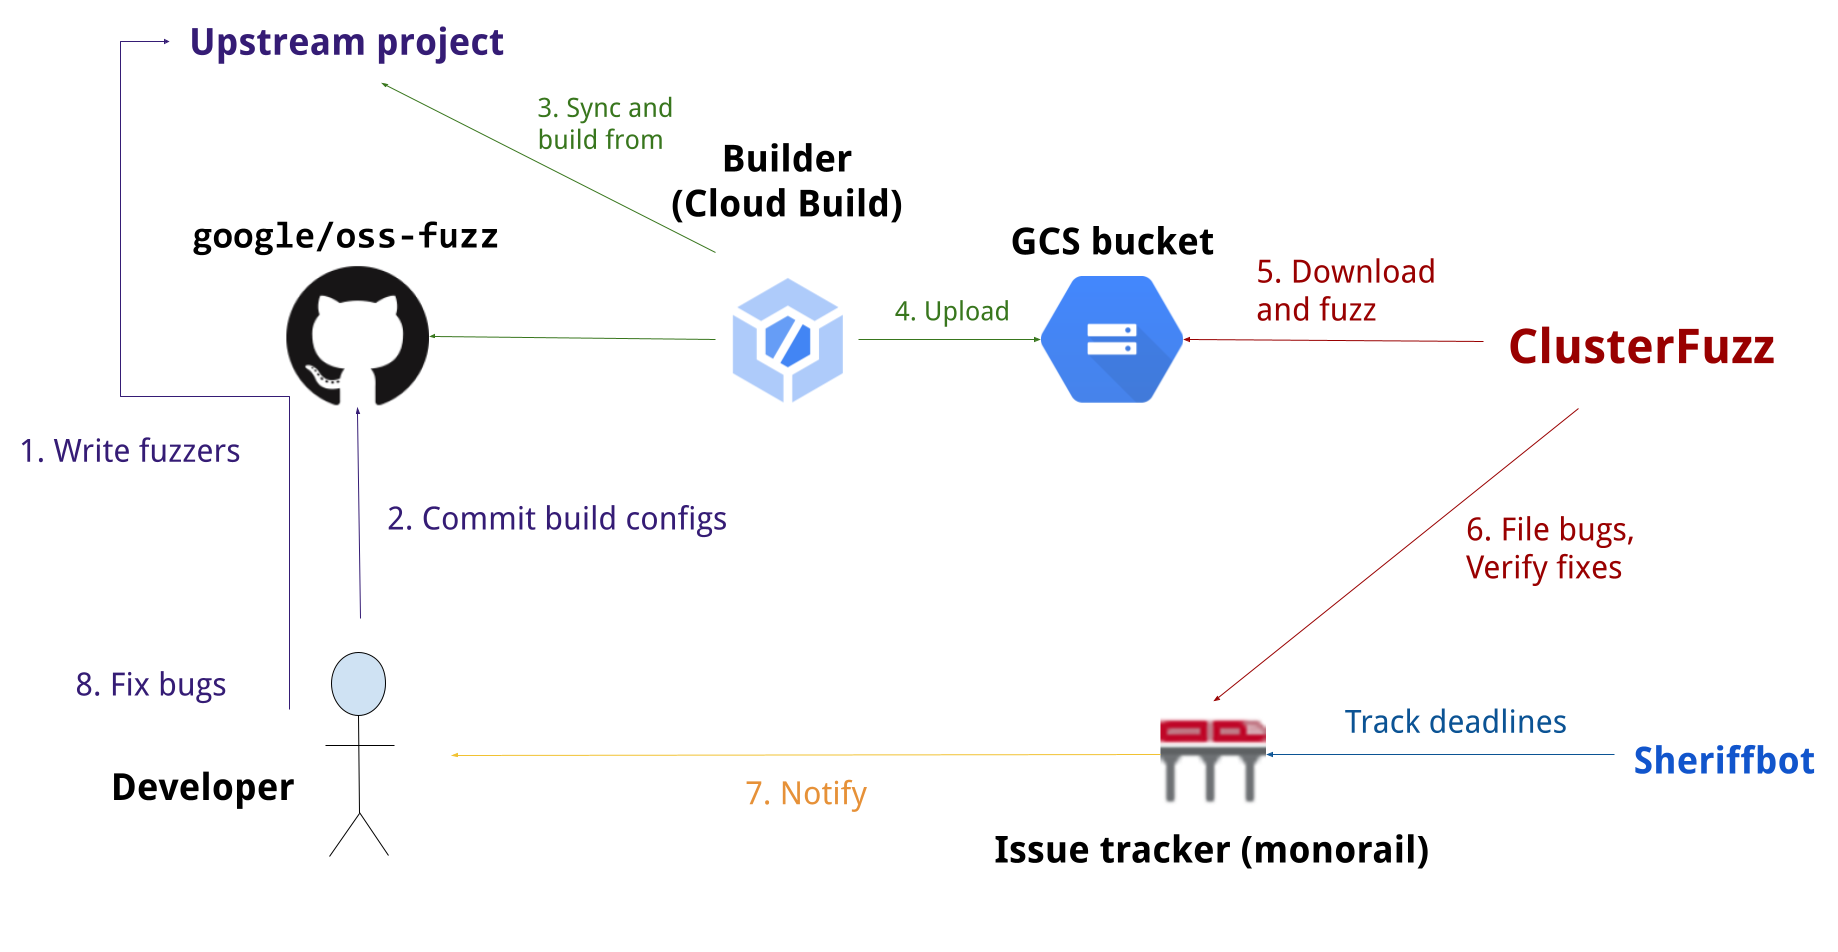
OSS-Fuzz - continuous fuzzing for open source software.
 mekoko/cve-2020-4276
Proof-of-concept exploit for CVE-2020-4276, targeting a specific vulnerability in affected software for security testing and validation.
 gkweb76/exploits
Collection of shellcode and proof-of-concept exploits for known vulnerabilities, intended for local testing and verifying software or network…
 ewilded/cve-2024-35315-poc
Proof-of-concept exploit for CVE-2024-35315, demonstrating local privilege escalation in Mitel Collab software. Intended for security testing and…
 lilang-wu/poc-cve-2018-4411
Proof-of-concept exploit for CVE-2018-4411, demonstrating a specific vulnerability in Apple software. Intended for security testing and educational…
 owasp/opencre
Interactive platform linking security standards and guidelines for designing, developing, testing, and procuring secure software. Provides a unified…
 smythtech/sdnpwn
An SDN penetration testing toolkit
 shoucheng3/apache__jspwiki_cve-2022-46907_2-11-3
Exploit module for Apache JSPWiki CVE-2022-46907, targeting a Java-based wiki platform with JAAS security integration. Provides vulnerability…
 owasp/tcasvs
OWASP Thick Client Application Security Verification Standard
 graysignal/cve-2024-23897-jenkins-arbitrary-read-file-vulnerability
Unauthenticated Jenkins CLI exploit scanner for CVE-2024-23897 that detects vulnerable versions and reads arbitrary files from the controller through…
 crypticq/cloudme_b0f
Proof-of-concept exploit for CVE-2018-6892 targeting a buffer overflow vulnerability in CloudMe software. Demonstrates exploitation technique for…
 owasp/nettacker
Automated Penetration Testing Framework - Open-Source Vulnerability Scanner - Vulnerability Management
 jonpichel/cve-2017-7358
Proof-of-concept exploit for CVE-2017-7358, demonstrating a specific vulnerability in a software application. Intended for security research and…
 btar1gan/exploit_cve-2022-35914
Exploit code for CVE-2022-35914, a vulnerability in a software component. Provides proof-of-concept implementation for security testing and research.
 shoucheng3/apache__jspwiki_cve-2019-10077_2-11-0-m3
Exploit module for Apache JSPWiki CVE-2019-10077, targeting a Java-based wiki platform with JAAS authentication and access control. Enables…
 shoucheng3/apache__jspwiki_cve-2019-10089_2-11-0-m4
Java-based wiki platform with detailed access control and JAAS security integration, provided as a vulnerable version for security testing and CVE…
 imjdl/cve-2012-4431
Apache Tomcat source code repository for CVE-2012-4431, a Java servlet container vulnerability. Provides the vulnerable codebase for analysis and…