
CVE-2018-10933
 soledad208/cve-2018-10933
CVE-2018-10933 very simple POC
authentication-authorizationexploitationpayload-generation+3
1268 years ago
soledad208/cve-2018-10933CVE-2018-10933 very simple POC
 acrono/cve-2024-6387-poc
32-bit PoC for CVE-2024-6387 — mirror of the original 7etsuo/cve-2024-6387-poc
 lflare/cve-2024-6387-poc
MIRROR of the original 32-bit PoC for CVE-2024-6387 "regreSSHion" by 7etsuo/cve-2024-6387-poc
 shoucheng3/apache__mina-sshd_cve-2023-35887_2-9-2
Pure Java SSH client/server library implementing SSH-2 protocol with support for multiple ciphers, key exchanges, authentication methods, SFTP, SCP,…
 anhvutuan/cve-2024-6387-poc-1
CVE-2024-6387, also known as RegreSSHion, is a high-severity vulnerability found in OpenSSH servers (sshd) running on glibc-based Linux systems. It…
 sxlmnwb/cve-2024-6387
Targeting a signal handler race condition in OpenSSH's server (sshd) on glibc-based Linux systems.
 7etsuo/cve-2024-6387-poc
a signal handler race condition in OpenSSH's server (sshd)
 t3rry327/cve-2024-6387-poc
Exploit for CVE-2024-6387 targeting a signal handler race condition in OpenSSH sshd on glibc-based Linux systems, enabling remote code execution as…
 jocker2410/cve-2024-6387_poc
Proof-of-concept exploit for CVE-2024-6387, a signal handler race condition in OpenSSH server (sshd) on glibc-based Linux systems, enabling remote…
 business1sg00d/cve-2023-25136
Looking into the memory when sshd 9.1p1 aborts due to a double free bug.
 s1d6point7bugcrowd/cve-2024-6387-race-condition-in-signal-handling-for-openssh
Technical analysis and proof-of-concept for CVE-2024-6387, a race condition in OpenSSH signal handling enabling unauthenticated remote code execution…
 michel-dv/xz-utils-backdoor-case-study
Technical case study of the XZ Utils backdoor (CVE-2024-3094), covering supply-chain trust abuse, malicious release artifacts, build-stage injection,…
 iheb2b/cve-2024-3094-checker
Bash script to detect CVE-2024-3094 vulnerability in XZ/LZMA utilities on Linux. Checks XZ version, SSHD LZMA linkage, and byte patterns, outputting…
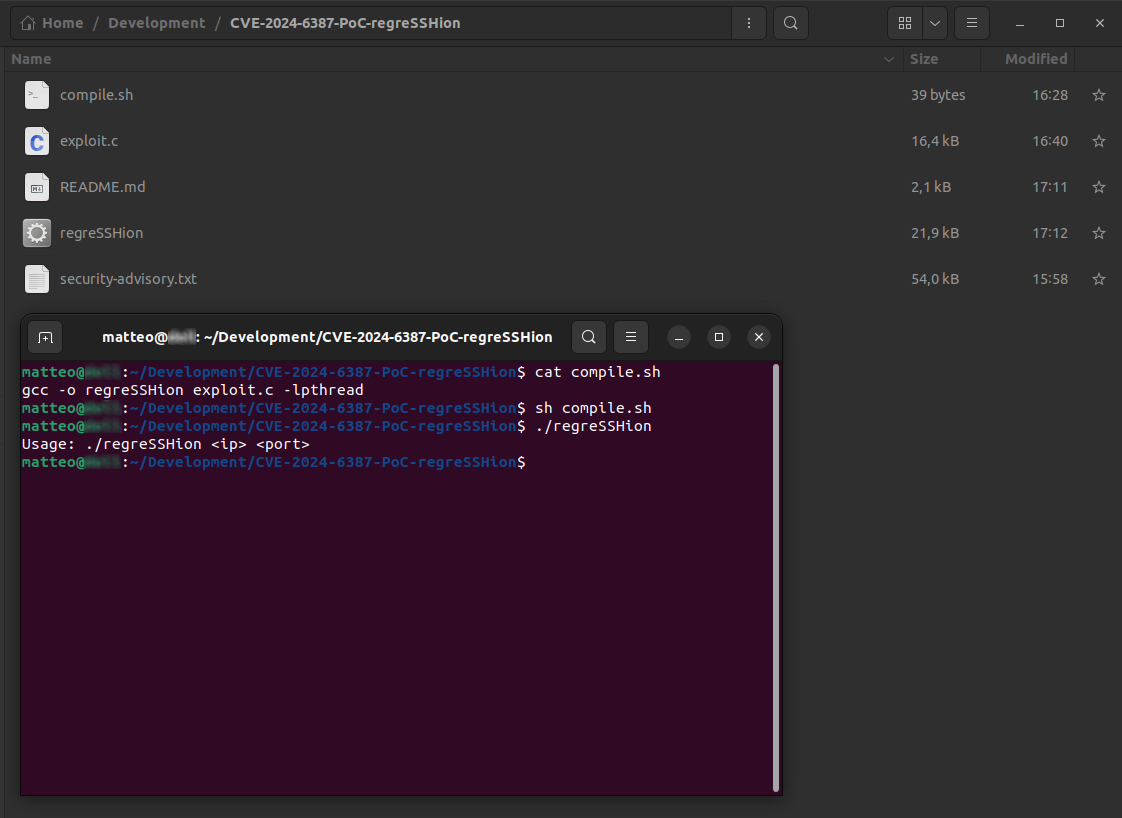 xonoxitron/regresshion
CVE-2024-6387 (regreSSHion) Exploit (PoC), a vulnerability in OpenSSH's server (sshd) on glibc-based Linux systems.
 4lxprime/regresshive
rewrited SSH Exploit for CVE-2024-6387 (regreSSHion)
 zgzhang/cve-2024-6387-poc
a signal handler race condition in OpenSSH's server (sshd)
 hasan8babiker/cve-2024-6387
PoC exploit for CVE-2024-6387 (OpenSSH regreSSHion), targeting sshd signal handler race condition for remote code execution on glibc Linux systems.
 passwa11/cve-2024-6387-poc
Proof-of-concept exploit for CVE-2024-6387, a signal handler race condition in OpenSSH's sshd, enabling remote code execution on vulnerable servers.