
Polkit-exploit
 almorabea/polkit-exploit
Privilege escalation with polkit - CVE-2021-3560
exploitationpenetration-testingpost-exploitation+3
1255 years ago
almorabea/polkit-exploitPrivilege escalation with polkit - CVE-2021-3560
 varchashva/vprioritizer
vPrioritizer enables us to understand the contextualized risk (vPRisk) on asset-vulnerability relationship level across the organization, for teams…
 carlos55ml/zerologon
Scripts to test and exploit the Zerologon vulnerability (CVE-2020-1472) in Active Directory, enabling password reset and hash dumping of domain…
 taielab/awesome-hacking-lists
A curated collection of top-tier penetration testing tools and productivity utilities across multiple domains. Join us to explore, contribute, and…
 microsoft/windowsprotocoltestsuites
⭐⭐ Join us at SNIA SDC for the SMB3 IO Lab (September 28 - October 1, 2026), see upcoming Interoperability Events
 osuni-99/cve-2019-6447
The above investigation of the ES file browser security weakness allows us to see the issue in its entirety
 jmaddington/serious-sam---cve-2021-36934-mitigation-for-datto-rmm
PowerShell script to apply Microsoft and US CERT mitigation measures for CVE-2021-36934 (Serious SAM) via Datto RMM, with UDF-based status tracking.
 th3xace/sudo_killer
A tool designed to exploit a privilege escalation vulnerability in the sudo program on Unix-like systems. It takes advantage of a specific…
 proviesec/google-dorks
Useful Google Dorks for WebSecurity and Bug Bounty
 bishopfox/iam-vulnerable
Use Terraform to create your own vulnerable by design AWS IAM privilege escalation playground.
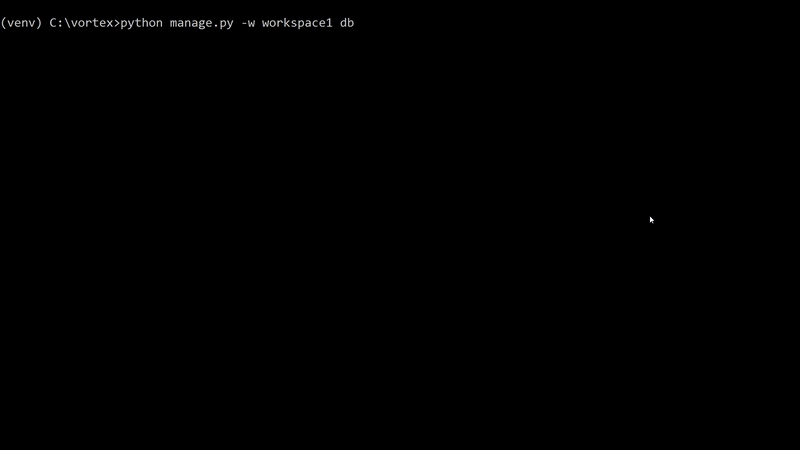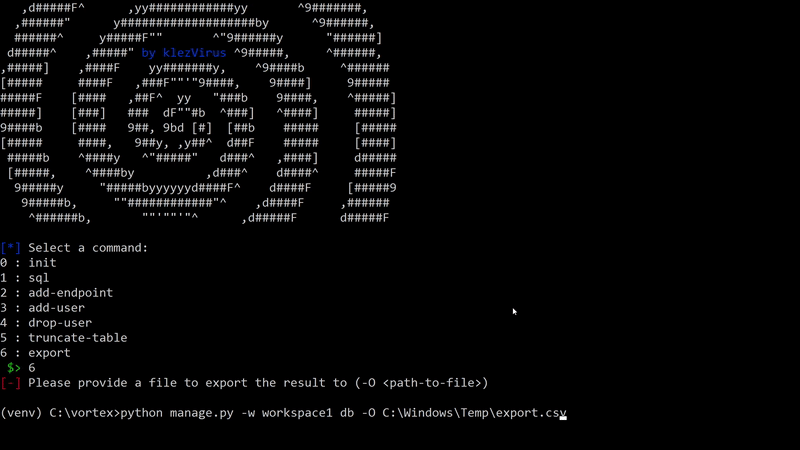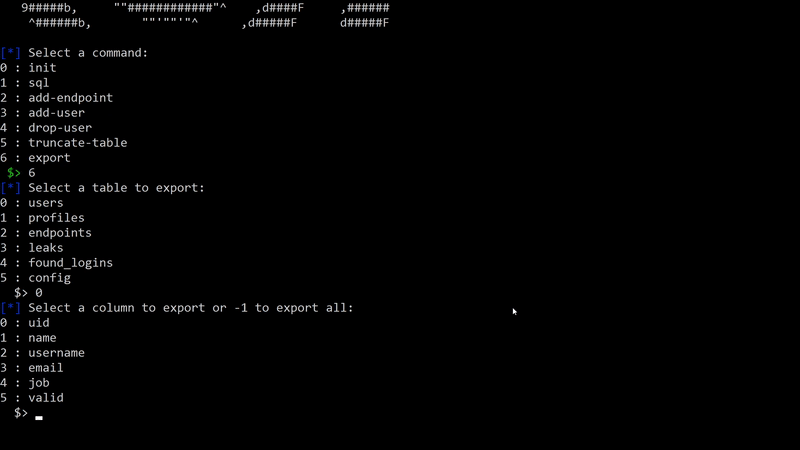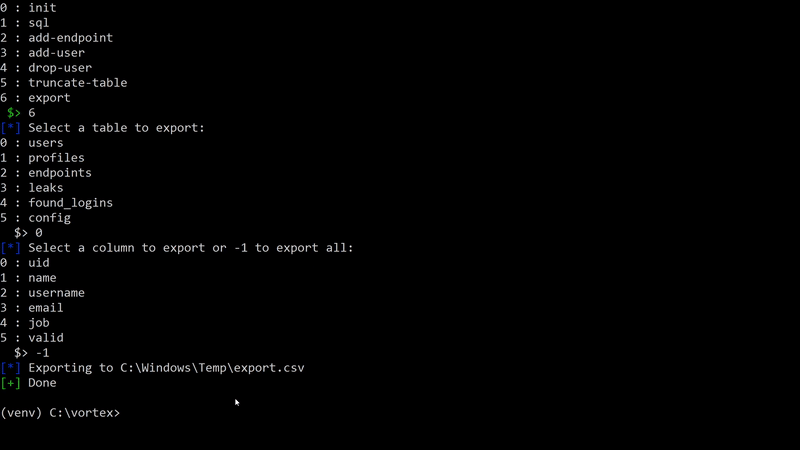 klezvirus/vortex
VPN Overall Reconnaissance, Testing, Enumeration and eXploitation Toolkit
 nu11secur1ty/kali-linux
Kali Linux advanced setup
 aeyesec/cve-2022-34265
PoC for CVE-2022-34265 (Django)
 daehee/nvd
Fast, simple library in Go to fetch CVEs from the National Vulnerability Database feeds
 claranet/ansible-role-log4shell
Ansible role to detect Log4Shell (CVE-2021-44228) by scanning filesystem and open files for vulnerable JAR/WAR files, reporting version and…
 argp/cve-2011-3026-firefox
Example of exploiting CVE-2011-3026 on Firefox (Linux/x86)
 alexfrancow/cve-2020-7200
CVE-2020-7200: HPE Systems Insight Manager (SIM) RCE PoC
 r4v3nbl4ck/apache-struts-2-cve-2017-5638-exploit-
Exploit created by: R4v3nBl4ck end Pacman