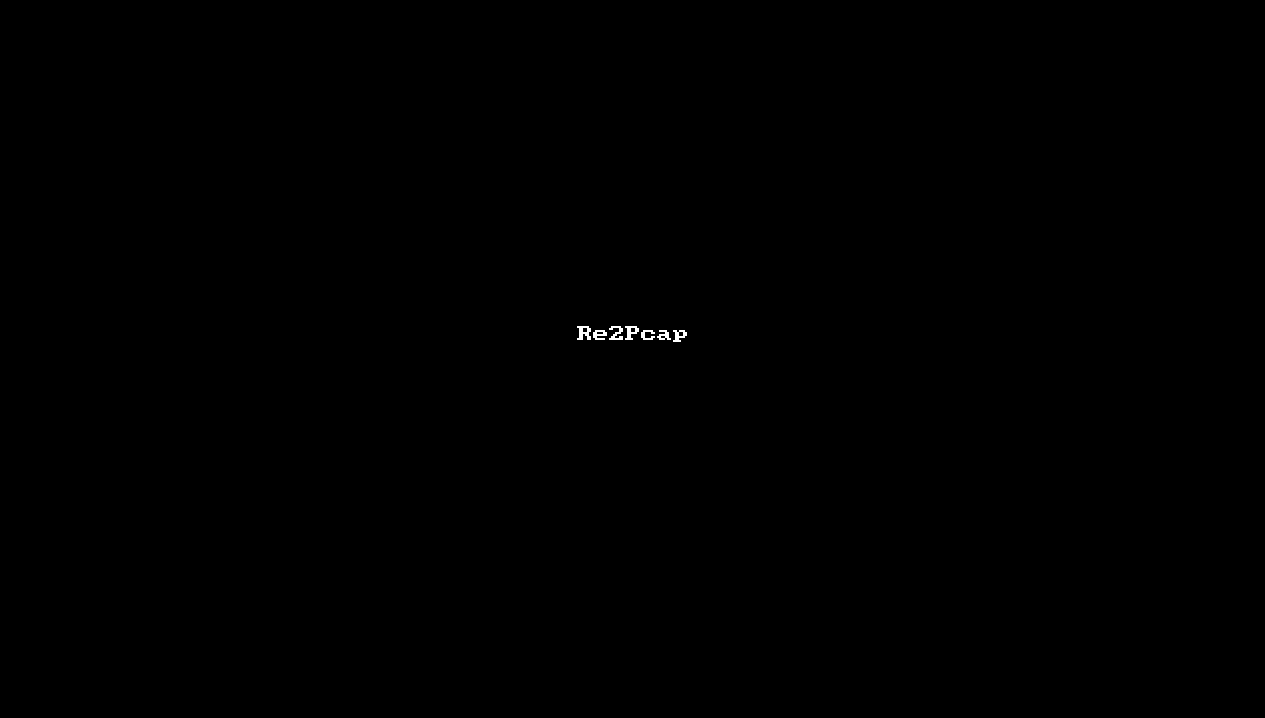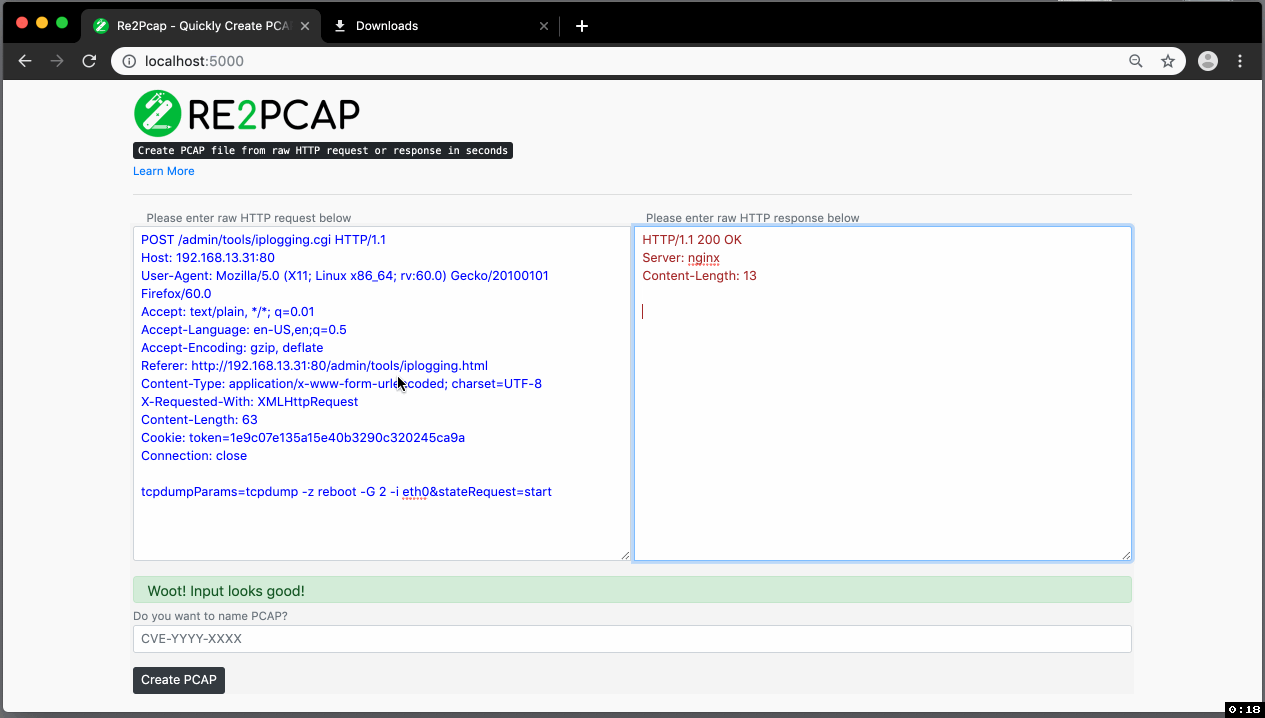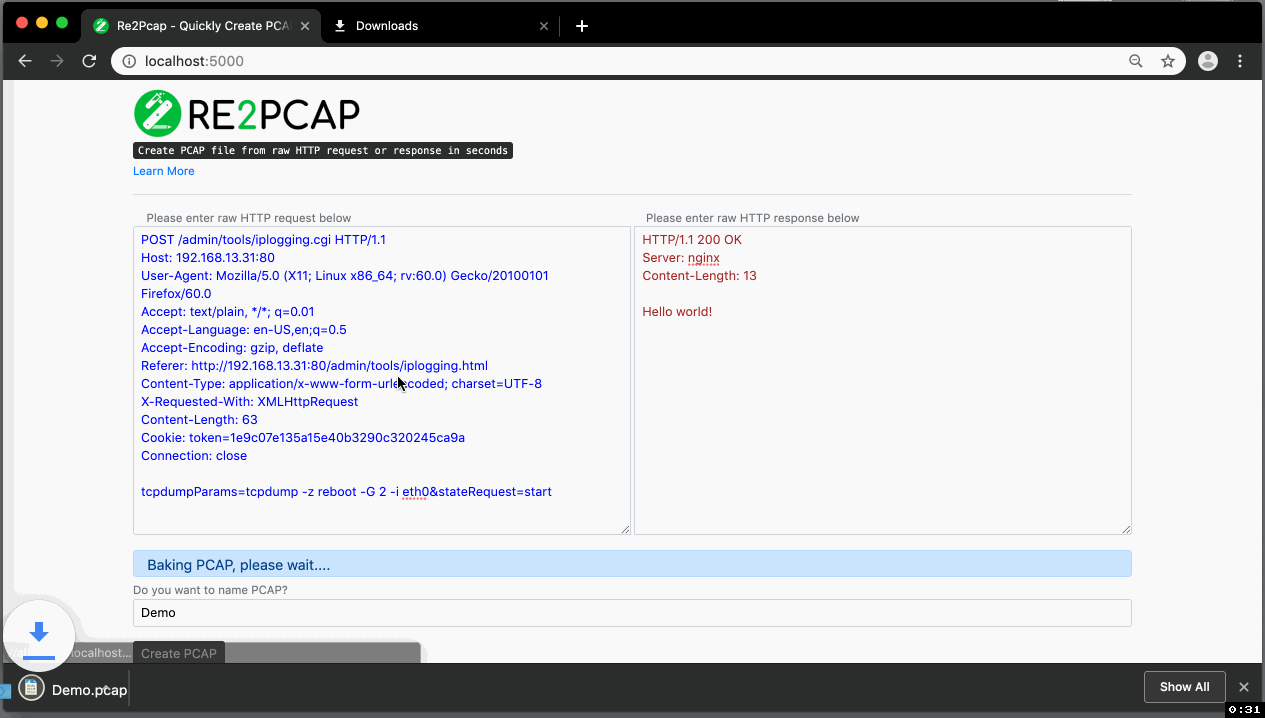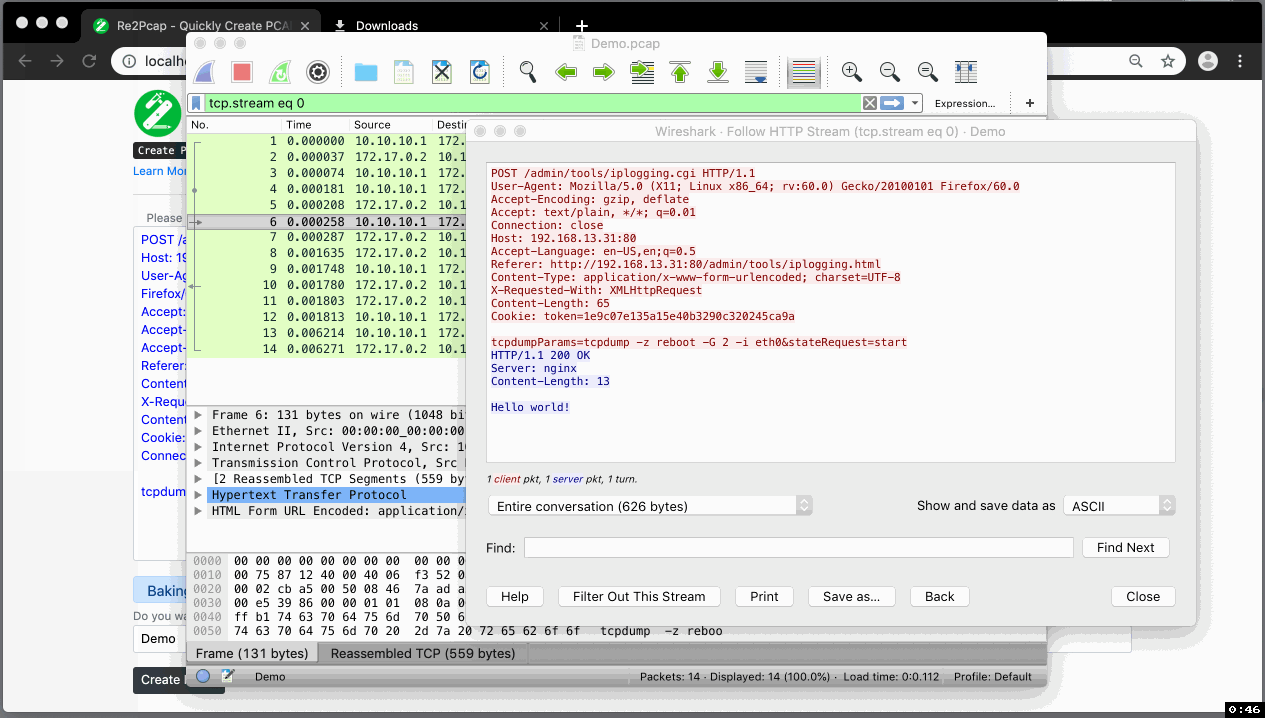
Network-Detection-Engine

Lightweight network intrusion detection engine capturing live traffic with libpcap. Detects SYN/ICMP floods, port scans, and signature-based web…

Lightweight network intrusion detection engine capturing live traffic with libpcap. Detects SYN/ICMP floods, port scans, and signature-based web…

Encrypted peer-to-peer mesh VPN for remote mobile forensics, enabling wireless ADB and libimobiledevice acquisition, network monitoring, and…

Edit and replay captured network traffic at arbitrary speeds — a suite of pcap tools for *NIX and Windows.

psad: Intrusion Detection and Log Analysis with iptables

Malformed ZIP archive that evades antivirus detection by declaring Method=0 (stored) while containing DEFLATE-compressed payload.

Exploit for Imperva Cloud WAF bypass using gzip Content-Encoding header to evade WAF rules on HTTP POST requests. Includes detection script and…

BYOVD: Use 360 WFP driver to block EDR/XDR network connection.

Convert raw HTTP requests/responses into PCAP files for testing Snort IDS rules and network security analysis. Supports Docker deployment and…

CVE-2020-16899 - Microsoft Windows TCP/IP Vulnerability Detection Logic and Rule

Zeek package detecting CVE-2022-26937 exploitation attempts against Windows NFS servers via Network Lock Manager protocol analysis.

Exploit for CVE-2023-23397 Outlook NTLM hash leak via malicious calendar invitations. Includes PowerShell weaponization, Responder integration, and…

CVE‑2025‑55182 Detection

Exploit for Apache Unomi pre-auth RCE (CVE-2020-13942) with a Suricata detection rule for identifying exploitation attempts.

Zeek-based network detector for CVE-2022-24497, identifying RPC portmap exploit attempts via real-time traffic analysis and alerting.

Zeek-based network detector for CVE-2022-24491, monitoring RPC portmap set and dump actions to identify exploit attempts in real-time traffic.

Suricata and Bro detection rules for CVE-2020-1938 (Ghostcat) Tomcat AJP file read vulnerability, enabling network-level monitoring and alerting.

CVE-2020-16898 — “Bad Neighbor” (ICMPv6 RDNSS length parsing) — Suricata Lua Detection

Detection rules for CVE-2020-1938 (Ghostcat) vulnerability in Apache Tomcat AJP connector, with Suricata and Bro signatures for network-based…