
dotnetpaddingoracle
 nccgroup/dotnetpaddingoracle
Python Implementation of a .NET Padding Oracle Assessment Tool
cryptographyencryption-decryption-toolsexploitation+3
31
nccgroup/dotnetpaddingoraclePython Implementation of a .NET Padding Oracle Assessment Tool
 rashedhasan090/aegisjava
I have created AegisJava, a tool to fix (detect and mitigate) CVE-2025-30749.
 cved-sources/cve-2017-10271
Docker container for CVE-2017-10271 (Oracle WebLogic RCE) used with Cved framework to manage and deploy vulnerable environments for security testing…
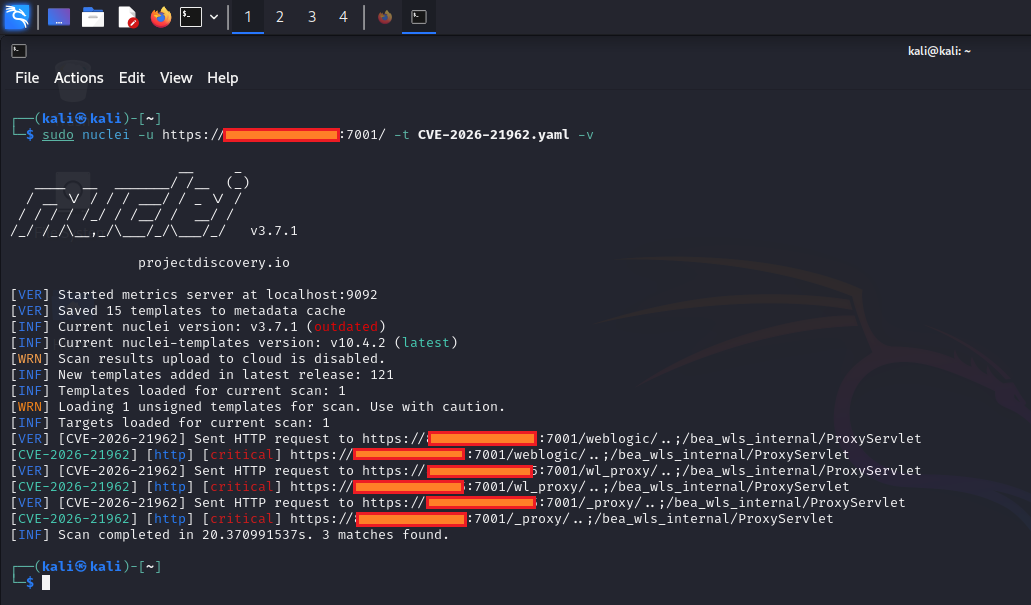 0xblackash/cve-2026-21962
CVE-2026-21962
 qianniaoge/cve-2020-14882_exploit_gui
GUI-based exploit tool for CVE-2020-14882 targeting Oracle WebLogic servers. Supports reverse shell payload generation, proxy configuration, and…
 aleksazatezalo/cve-2020-14882
Exploits Oracle WebLogic Server RCE (CVE-2020-14882) to execute commands on vulnerable targets, capturing output via HTTP listener.
 aymanelsherif/oracle-oam-authentication-bypas-exploit
Exploit for Oracle Access Manager padding oracle vulnerability (CVE-2018-2879)
 9uest/cve-2018-2628
Python exploit for CVE-2018-2628 targeting Oracle WebLogic Server T3 deserialization vulnerability to achieve remote code execution.
 muhammedhussein17/keycloak
Security research disclosing CVE-2026-9794, an unauthenticated client ID enumeration flaw in Keycloak SAML ECP via faultstring oracle, fixed in…
 root-shells/cve-2020-14882
CVE-2020-14882 rewritten in PowerShell
 naozibuhao/cve-2026-21962_java_gui_exploit_tool
Java GUI tool for exploiting CVE-2026-21962, an unauthenticated RCE in Oracle WebLogic Proxy Plug-In, enabling multi-target command execution via…
 wise-security/cve-2025-69600
Demonstrates command injection vulnerabilities in RayVentory Scan Engine's rvia tool, allowing arbitrary command execution via getconfig, upload,…
 lasensio/cve-2019-2725
Python exploit for Oracle WebLogic CVE-2019-2725, enabling unauthenticated remote code execution via crafted HTTP requests to vulnerable servers.
 mindflarex/cve-2025-61882-poc
Exploit for CVE-2025-61882, a critical pre-auth RCE in Oracle E-Business Suite. Combines SSRF, CRLF injection, HTTP smuggling, and XSLT injection for…
 grrrdog/acedcup
Payload generator for Java Binary Deserialization attack with Commons FileUpload (CVE-2013-2186)
 vulnmachines/oracle-weblogic-cve-2021-2109
Oracle Weblogic RCE - CVE-2022-2109
 danny-lli/cve-2020-14882
This script allows for remote code execution (RCE) on Oracle WebLogic Server
 ludy-dev/oracle-wls-weblogic-rce
(CVE-2019-2725) Oracle WLS(Weblogic) RCE test sciript