web-penetration-drupal

Penetration test of a Drupal web app — CVE-2018-7600 (Drupalgeddon 2) exploited using Nmap, Burp Suite & Metasploit | Internship @ BB CyberSec

Penetration test of a Drupal web app — CVE-2018-7600 (Drupalgeddon 2) exploited using Nmap, Burp Suite & Metasploit | Internship @ BB CyberSec

Burp Suite extension for API security testing with 15 attack types, 108+ payloads, intelligent fuzzing, BOLA/IDOR detection, AI integration, and…

Proof-of-concept exploit for an actively exploited Zimbra Collaboration Suite vulnerability, designed for authorized penetration testing and…

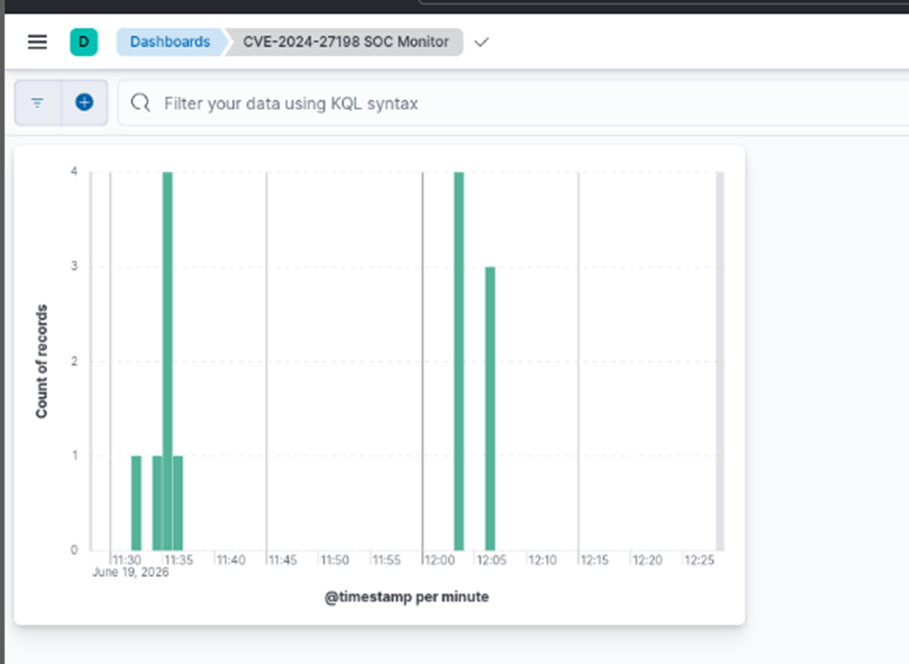
SOC detection and incident response lab simulating CVE-2024-27198 authentication bypass in JetBrains TeamCity. Includes ELK SIEM, Suricata IDS, Sigma…

Log4Shell (CVE-2021-44228) exploit demo for SEAS 8405. Includes a vulnerable Spring Boot app, fake LDAP server, Docker setup, MITRE mapping, incident…

Linux operating system for embedded devices with writable filesystem, package management, and build framework. Enables custom firmware creation for…

Setup and exploit recreation for CVE-2022-42889 Text4Shell.

Researched and executed real-world CVE exploits in a controlled sandbox: CVE-2000-0168 DoS on Windows 95, ARP Spoofing with NTLMv2 credential…

A Rust CLI tool that recursively discovers Git repositories, captures state changes, generates diffs, extracts code elements with full snippets, and…

An automated, high-precision zero-shot evaluation pipeline for OpenAI's CLIP model on CIFAR-10. Features 88.80% accuracy, Safetensors security…

Executable security regression testing for agentic applications and MCP-integrated systems.

A Fullstack Academy Cybersecurity project examining the full cycle of the Follina (CVE-2022-30190) vulnerability, from exploit to detection and…

Hands-on project demonstrating Log4Shell exploitation, detection engineering with Splunk and auditd, and validated remediation in a containerized…

Full-lifecycle penetration test of a legacy Linux environment (Metasploitable 2) emulated on Apple Silicon. Demonstrating network reconnaissance, RCE…

Burp suite extension that lets you easily copy issues

Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.

Local proof-of-concept and sanitized report for CVE-2026-103437, a canonical URL XSS in MediaWiki ReadingLists triggered via crafted import links.

full javascript reproduction of CVE-2026-63030 (author_exclude, author__not_in and misalignment between validations and matches)