
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
241 results
moneta preview

moneta

GitHubforrest-orr/moneta

Moneta is a live usermode memory analysis tool for Windows with the capability to detect malware IOCs

digital-forensicsforensicsioc-management+3
8492 years ago
systeminformer preview

systeminformer

GitHubwinsiderss/systeminformer

Real-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…
debuggersdigital-forensicsforensics+6
16.2k14h 32m ago
BigBountyRecon preview

BigBountyRecon

GitHubviralmaniar/bigbountyrecon

BigBountyRecon tool utilises 58 different techniques using various Google dorks and open source tools to expedite the process of initial…
dns-subdomain-enumerationeducationinformation-gathering+6
1.6k5 years ago
Windows_LPE_AFD_CVE-2023-21768 preview

Windows_LPE_AFD_CVE-2023-21768

GitHubchompie1337/windows_lpe_afd_cve-2023-21768

Local privilege escalation exploit for CVE-2023-21768 targeting Windows AFD driver. Elevates arbitrary process to SYSTEM using I/O Ring read/write…
binary-exploitationexploitationpayload-development+3
5063 years ago
evil-mhyprot-cli preview

evil-mhyprot-cli

GitHubkkent030315/evil-mhyprot-cli

A PoC for Mhyprot2.sys vulnerable driver that allowing read/write memory in kernel/user via unprivileged user process.
binary-exploitationexploitationprivilege-escalation+2
3585 years ago
Mhyprot2DrvControl preview

Mhyprot2DrvControl

GitHubkagurazakasanae/mhyprot2drvcontrol

A lib that allows using mhyprot2 driver for enum process modules, r/w process memory and kill process.
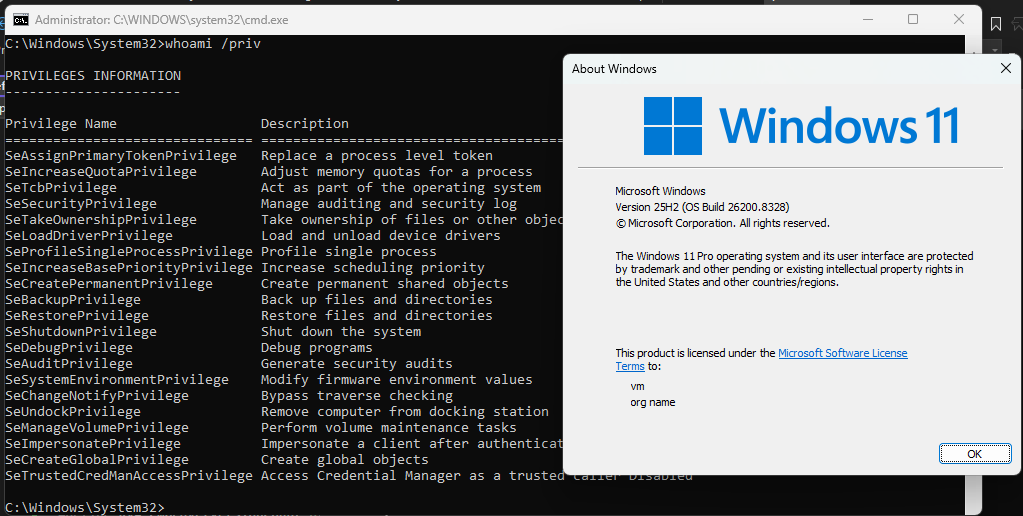
privilege-escalationvulnerability-analysis
3625 years ago
CVE-2026-40369-EXPLOIT preview

CVE-2026-40369-EXPLOIT

GitHuborinimron123/cve-2026-40369-exploit

Full exploit code for CVE-2026-40369 - A Windows kernel arbitrary write vulnerability that allows browser sandbox escape from all browsers render…
binary-exploitationexploitationprivilege-escalation+1
2614 months ago
slicer preview

slicer

GitHubmzfr/slicer

A tool to automate the boring process of APK recon
android-securityinformation-gatheringmobile-app-pentesting+2
3434 years ago
TProxer preview

TProxer

GitHubethicalhackingplayground/tproxer

A Burp Suite extension made to automate the process of finding reverse proxy path based SSRF.
api-security-testingpenetration-testingvulnerability-analysis+2
1844 years ago
POC-for-CVE-2023-41993 preview

POC-for-CVE-2023-41993

GitHubpo6ix/poc-for-cve-2023-41993

Proof-of-concept exploit for CVE-2023-41993, a WebKit JIT type confusion in Safari. Provides addrof/fakeobj primitives via heap manipulation and…
binary-exploitationexploitationpayload-development+2
2022 years ago
Windows_MSKSSRV_LPE_CVE-2023-36802 preview

Windows_MSKSSRV_LPE_CVE-2023-36802

GitHubchompie1337/windows_mskssrv_lpe_cve-2023-36802

Local privilege escalation exploit for CVE-2023-36802 targeting Windows kernel streaming service (MSKSSRV) on Windows 11 22H2, using I/O Ring…

binary-exploitationexploitationexploit-frameworks+3
1632 years ago
Inspector preview

Inspector

GitHubgraniet/inspector

The Inspector tool is a privilege escalation helper (PoC), easy to deployed on web server, this tool can list process running with root, check kernel…

information-gatheringpenetration-testingprivilege-escalation+1
1208 years ago
ResourcePoison preview

ResourcePoison

GitHubmichalbednarski/resourcepoison

Writeup and exploit for CVE-2025-22441: Privilege escalation from installed app to SystemUI process on Android due to pass of untrusted…
android-securityexploitationmobile-security+3
1080 years ago
0xKern3lCrush preview

0xKern3lCrush

GitHubdeathshotxd/0xkern3lcrush

Advanced PoC & Research for CVE-2026-0828 (Safetica) and CVE-2025-7771 (ThrottleStop). Analysis of BYOVD (Bring Your Own Vulnerable Driver) TTPs for…
educationexploitationmalware-analysis+4
573 days ago
Enumprotections_BOF preview

Enumprotections_BOF

GitHuboctoberfest7/enumprotections_bof

A BOF to enumerate system process, their protection levels, and more.

information-gatheringpenetration-testingpost-exploitation+4
1241 year ago
aether preview

aether

GitHub0xsp-srd/aether

Windows memory-forensics and threat hunting tool that scans live process memory for malicious patterns, injection techniques, and reflectively loaded…

binary-analysiscommand-and-controldigital-forensics+7
673 months ago
Win10Pcap-Exploit preview

Win10Pcap-Exploit

GitHubrootkitsmm-zz/win10pcap-exploit

Exploit Win10Pcap Driver to enable some Privilege in our process token ( local Privilege escalation )
binary-exploitationexploitationpost-exploitation+2
6110 years ago
gentlemen-decryptor preview

gentlemen-decryptor

GitHubbedrock-safeguard/gentlemen-decryptor

First-ever decryptor for The Gentlemen ransomware — recovers encryption keys from process memory dumps using X25519 ephemeral key extraction. 35/35…

cryptographydigital-forensicseducation+7
314 months ago
Previous12…14Next