
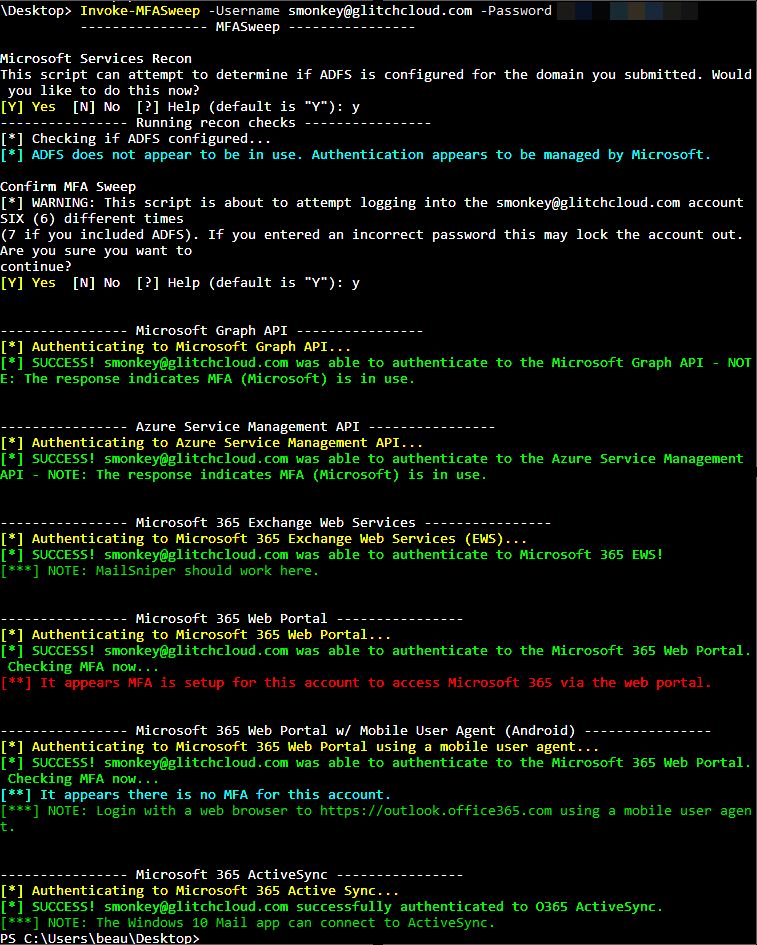
MFASweep
 dafthack/mfasweep
A tool for checking if MFA is enabled on multiple Microsoft Services
authenticationcloud-securitypenetration-testing+2
dafthack/mfasweepA tool for checking if MFA is enabled on multiple Microsoft Services
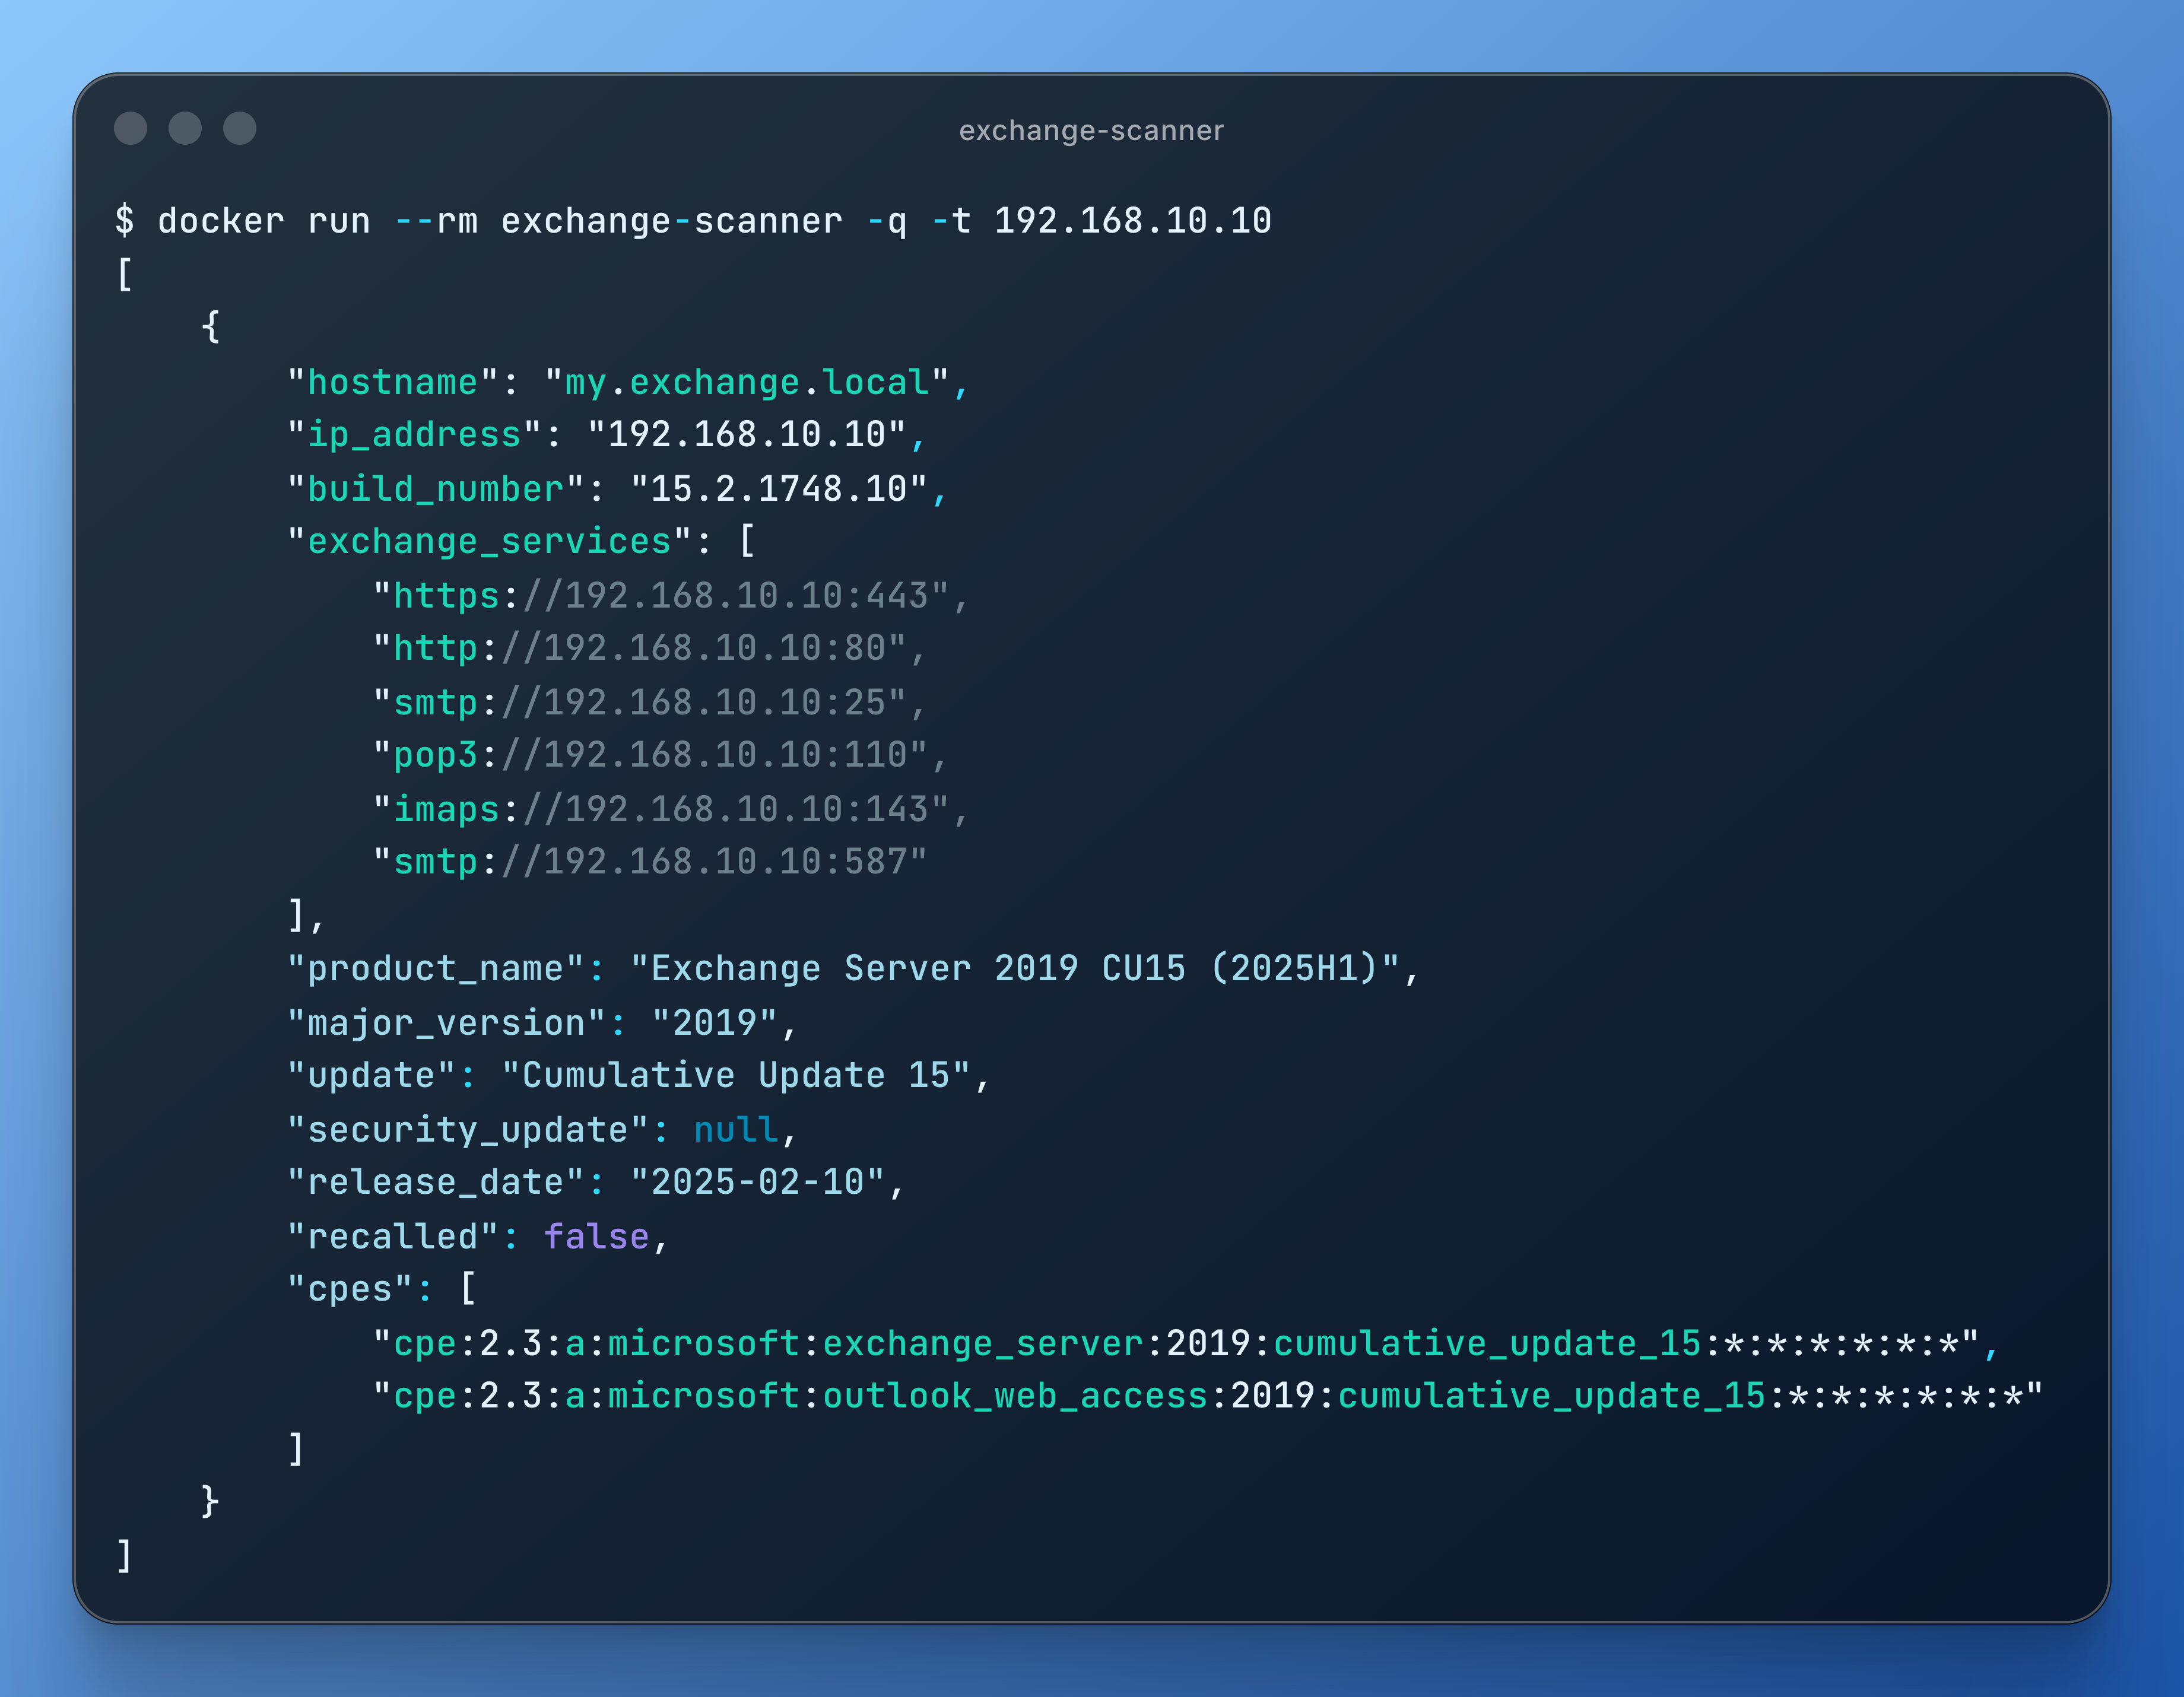 bishopfox/exchange-scanner
Identify public-facing Microsoft Exchange servers and determine their software versions
 virologi-info/mssharepoint-scanner
A scanner for CVE-2026-55040 and CVE-2026-63520, designed to determine whether the server is affected by these two CVEs.
 bsec404/cve-2020-00796
Python scanner to identify systems vulnerable to CVE-2020-0796 (SMBv3 RCE) by sending crafted negotiate requests and checking for the flaw.
 strozfriedberg/windows-exploit-suggester
This tool compares a targets patch levels against the Microsoft vulnerability database in order to detect potential missing patches on the target. It…
 microsoft/routeros-scanner
Tool to scan for RouterOS (Mikrotik) forensic artifacts and vulnerabilities.
 haotiku/cve-2021-26855-exploit-exchange
Automated scanner and exploit tool for CVE-2021-26855 targeting Microsoft Exchange servers, enabling remote code execution on vulnerable instances…
 soltanali0/cve-2022-41082
CVE-2022-41082-poc
 exfil0/cve-2025-53770
A sophisticated, wizard-driven Python exploit tool targeting CVE-2025-53770, a critical (CVSS 9.8) unauthenticated remote code execution (RCE)…
 bitsadmin/wesng
Windows Exploit Suggester - Next Generation
 dhananjayasj/cve-2024-21413-microsoft-outlook-remote-code-execution-vulnerability
Proof-of-concept exploit for CVE-2024-21413, a critical Outlook RCE vulnerability that leaks NetNTLMv2 hashes via crafted file:// links, enabling…
 secorizon/msfinger
Microsoft Network Service Fingerprinting Tool
 synacktiv/cve-2024-43468
Exploit for CVE-2024-43468: unauthenticated SQL injection in Microsoft Configuration Manager Management Points, enabling arbitrary SQL execution and…
 synacktiv/cve-2025-59213
Unauthenticated SQL injection exploit for Microsoft Configuration Manager (SCCM) 2503, enabling arbitrary SQL execution on the site database via the…
 ahmedumarehman/cve-2025-21293
CVE-2025-21293 is an elevation of privilege vulnerability in Active Directory Domain Services. It allows "Network Configuration Operators" to execute…
 chpratik/cve-2026-50522
Deserialization of untrusted data in Microsoft Office SharePoint allows an unauthorized attacker to execute code over a network.
 chpratik/cve-2026-54121
Improper authorization in Active Directory Certificate Services (AD CS) allows an authorized attacker to elevate privileges over a network.