CVE-2016-010033-010045

Python3 port of a PHP mail() remote code execution exploit targeting CVE-2016-010033/45 for penetration testing and vulnerability verification.

Python3 port of a PHP mail() remote code execution exploit targeting CVE-2016-010033/45 for penetration testing and vulnerability verification.

Reproducer for CVE-2026-33454: Apache Camel camel-mail header injection to RCE via camel-exec

Proof-of-concept exploit for CVE-2021-33766 (ProxyToken) authentication bypass in Microsoft Exchange Server. Supports single and batch target…

Unauthenticated remote code execution exploit for Zimbra Collaboration Suite (CVE-2022-27925). Delivers a reverse shell payload to compromise…

This vulnerability exists in OpenBSD’s mail server OpenSMTPD’s “smtp_mailaddr()” function, and affects OpenBSD version 6.6. This allows an attacker…

analytics ProxyLogo Mail exchange RCE

Proof-of-concept exploit and lab for CVE-2026-84753, an unauthenticated PHP Object Injection in Mail Mint <= 1.31.0 via the mint-form-submit REST…

POC of CVE-2018-8718 + tool

nginx 1.15.10 patch against cve-2021-23017 (ingress version)


Insecure attachment handling when using Canary Mail or Blue mail

POC to test CVE-2024-39929 against EXIM mail servers

Exploit script for WordPress Plugin Mail Masta 1.0 - CVE-2016-10956

This repository contains research notes and a high-level proof-of-concept (PoC) for CVE-2024-21413, a vulnerability observed in certain mail clients…

Local Docker lab demonstrating CVE-2026-8206 unauthenticated account takeover in Kirki WordPress plugin. Compares vulnerable 6.0.6 vs patched 6.0.7…

Docker-based environment to reproduce CVE-2020-7247 (OpenSMTPD) with a Python exploit script for arbitrary command execution and reverse shell via…

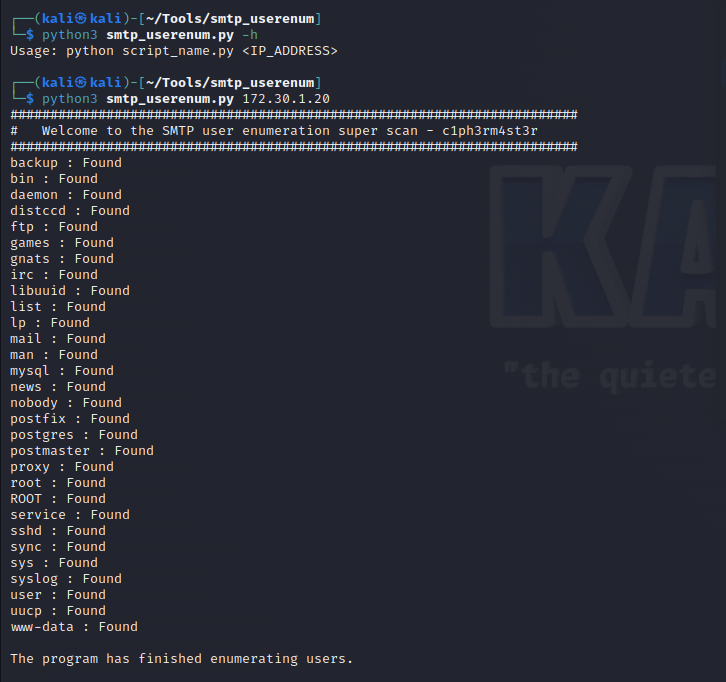
Python script for enumerating SMTP users by leveraging VRFY and EXPN commands to identify valid email accounts on a target mail server.

A better whois and domain intelligence toolkit