Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
357 results
gpgsm-cve-2026-57062-cms-gcm-short-tag preview

gpgsm-cve-2026-57062-cms-gcm-short-tag

GitHubgoldendivider/gpgsm-cve-2026-57062-cms-gcm-short-tag

Proof-of-concept demonstrating a CMS AES-GCM short-tag authentication bypass in GnuPG's gpgsm (CVE-2026-57062). Forges a message that decrypts on…

cryptographyexploitationpenetration-testing+1
1 month ago
CVE-2026-26980-Ghost-CMS-Api preview

CVE-2026-26980-Ghost-CMS-Api

GitHubgagaltotal/cve-2026-26980-ghost-cms-api

Go-based PoC for Ghost CMS Content API SQL injection (CVE-2026-26980). Verifies vulnerability, extracts admin credentials and API secrets, and…

exploitationinformation-gatheringpenetration-testing+2
114 months ago
cve-2019-9053-py3 preview

cve-2019-9053-py3

GitHubvedantrana73/cve-2019-9053-py3

Unauthenticated time-based blind SQL injection exploit for CMS Made Simple ≤ 2.2.9 (CVE-2019-9053), ported to Python 3.

educationexploitationpassword-cracking+3
4 months ago
CVE-2024-46987 preview

CVE-2024-46987

GitHubik0nw/cve-2024-46987

Exploit for CVE-2024-46987 path traversal in Camaleon CMS enabling arbitrary file download and automated SSH key extraction via brute-force.

exploitationinformation-gatheringpassword-attacks+3
8 months ago
CVE-2025-2304 preview

CVE-2025-2304

GitHub0xk4rth1/cve-2025-2304

A critical mass assignment vulnerability in Camaleon CMS (< 2.9.1) allows authenticated low-privileged users to elevate their privileges to…

educationexploitationpenetration-testing+3
14 months ago
CVE-2019-19609 preview

CVE-2019-19609

GitHubglowbase/cve-2019-19609

Python exploit script targeting unauthenticated remote code execution in Strapi CMS 3.0.0-beta.17.4 via CVE-2019-18818 and CVE-2019-19609, delivering…

exploitationpenetration-testingremote-access-tool+2
24 years ago
CVE-2018-16763 preview

CVE-2018-16763

GitHubsome-1hing/cve-2018-16763

Python tool for analyzing CVE-2018-16763 in FUEL CMS with cleaner response parsing and interactive vulnerability checking.

code-analysisexploitationpenetration-testing+3
4 months ago
CVE-2022-26159-Ametys-Autocompletion-XML preview

CVE-2022-26159-Ametys-Autocompletion-XML

GitHubp0dalirius/cve-2022-26159-ametys-autocompletion-xml

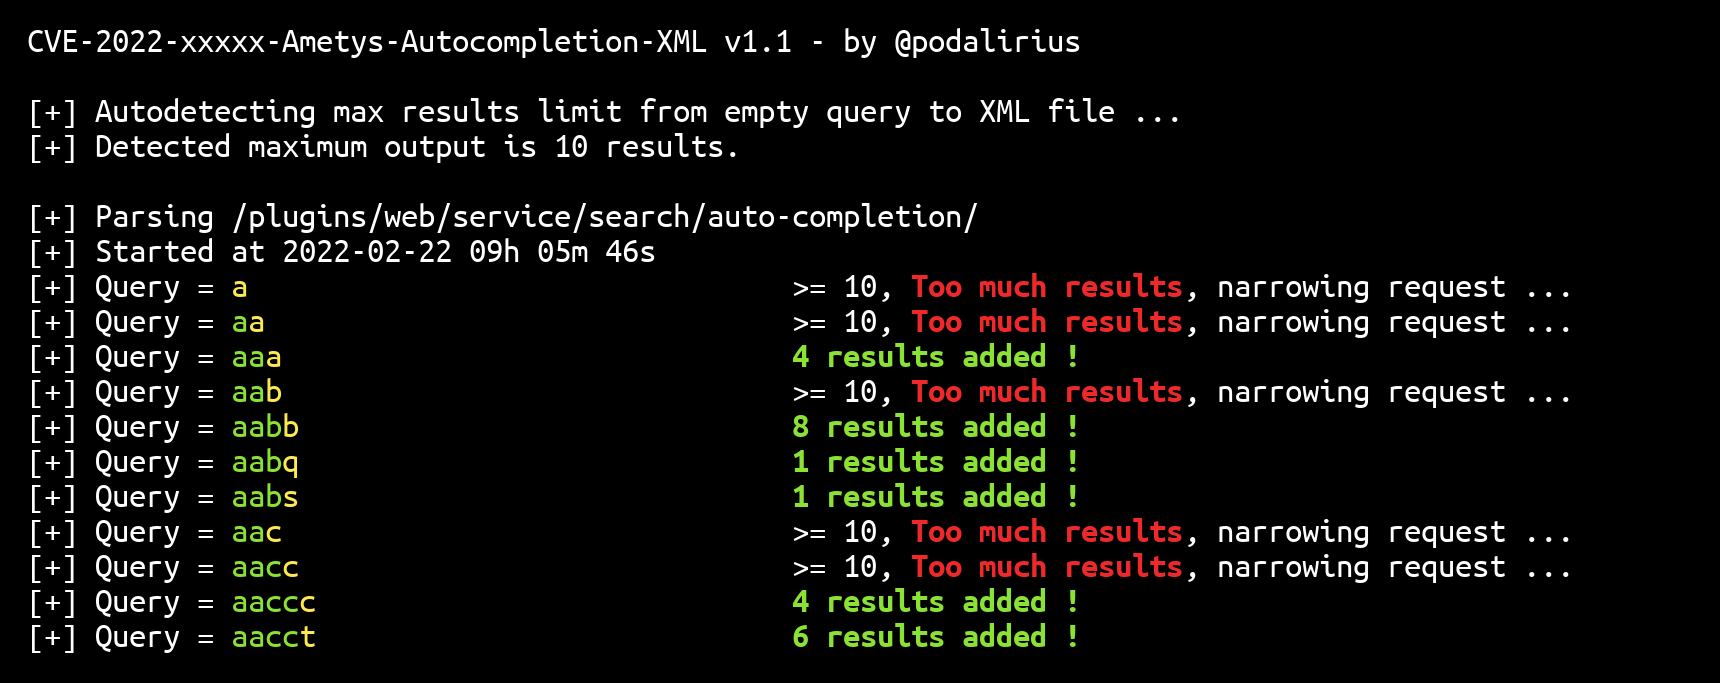
A python exploit to automatically dump all the data stored by the auto-completion plugin of Ametys CMS to a local sqlite database file.

crawlerdata-exfiltrationexploitation+3
144 years ago
CVE-2016-16113-POC preview

CVE-2016-16113-POC

GitHubd3vn0mi/cve-2016-16113-poc

cve-2016-16113

exploitationpassword-attackspayload-generation+4
19 months ago
CVE-2026-8237 preview

CVE-2026-8237

GitHubaj2108/cve-2026-8237

In-depth IDOR write-up for Concrete CMS, covering the message_detail endpoint, missing authorization root cause, attack scenarios, impact, and fix.

authentication-authorizationeducationvulnerability-analysis+2
2 months ago
CVE-2026-8239 preview

CVE-2026-8239

GitHubaj2108/cve-2026-8239

Security write-up for an IDOR in Concrete CMS exposing conversation ratings through missing authorization on the get_rating endpoint, with root…

authentication-authorizationeducationinformation-gathering+3
2 months ago
Craft-CMS-Exploit preview

Craft-CMS-Exploit

GitHubdiegaccio/craft-cms-exploit

Python exploit for Craft CMS CVE-2023-41892 Remote Code Execution vulnerability, delivering a PHP reverse shell for authorized penetration testing.

exploitationpenetration-testingred-teaming+3
52 years ago
CVE-2026-8347 preview

CVE-2026-8347

GitHubaj2108/cve-2026-8347

CVE-2026-8347 is an Insecure Direct Object Reference (IDOR) combined with a wrong authorization level vulnerability in Concrete CMS versions 9.5.0…

authentication-authorizationvulnerability-analysisweb-application-exploitation+1
3 months ago
CVE-2018-16763 preview

CVE-2018-16763

GitHubh3x0v3rl0rd/cve-2018-16763

Python-based remote code execution exploit targeting fuel CMS 1.4.1, enabling authenticated attackers to execute arbitrary commands on vulnerable web…

exploitationpenetration-testingremote-access-tool+2
21 year ago
CVE-2022-42092 preview

CVE-2022-42092

GitHubajdumanhug/cve-2022-42092

CVE-2023-46818 Python3 Exploit for Backdrop CMS <= 1.22.0 Authenticated Remote Command Execution (RCE)

exploitationpenetration-testingremote-access-tool+2
11 year ago
CVE-2023-43154-PoC preview

CVE-2023-43154-PoC

GitHubally-petitt/cve-2023-43154-poc

PoC for the type confusion vulnerability in Mac's CMS that results in authentication bypass and administrator account takeover.

authentication-authorizationexploitationpassword-attacks+3
3 years ago
CVE-2019-16113 preview

CVE-2019-16113

GitHubm4rm0k/cve-2019-16113

Bludit 3.9.2 - Remote command execution - CVE-2019-16113

exploitationpassword-attacksremote-access-tool+2
6 years ago
CVE-2026-44011-poc preview

CVE-2026-44011-poc

GitHubkhush-613/cve-2026-44011-poc

Python proof-of-concept exploit for CVE-2026-44011, an authenticated RCE in Craft CMS via Yii behavior injection, with two-stage command output…

exploitationpayload-developmentpenetration-testing+4
11 month ago
Previous12…20Next