

CosmicRakp
 fin3ss3g0d/cosmicrakp
Go-based tool to exploit CVE-2013-4786 for dumping IPMI password hashes via RAKP authentication, supporting concurrent scanning of IP ranges or…
exploitationinformation-gatheringpassword-cracking+3
42
fin3ss3g0d/cosmicrakpGo-based tool to exploit CVE-2013-4786 for dumping IPMI password hashes via RAKP authentication, supporting concurrent scanning of IP ranges or…
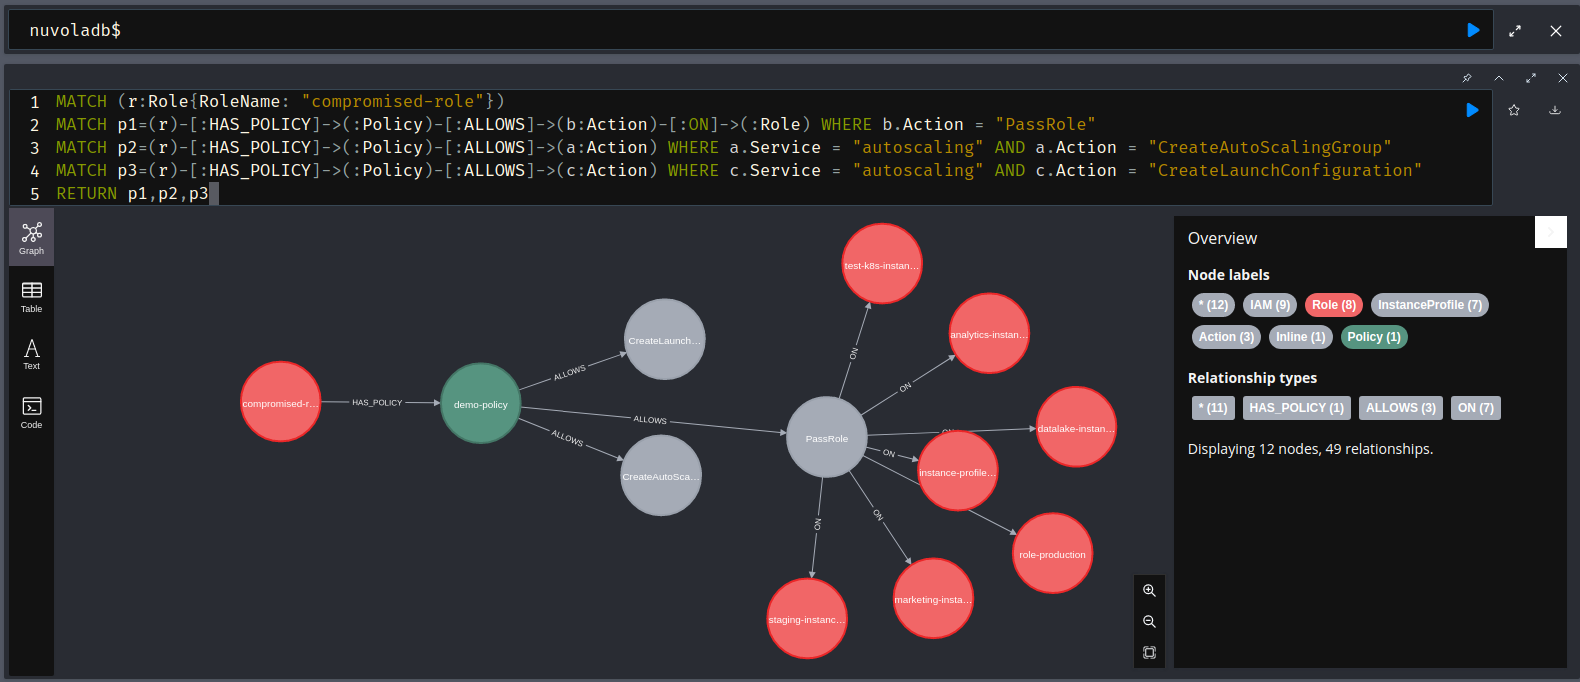 primait/nuvola
Graph-based AWS security analysis tool that dumps cloud configurations, detects misconfigurations, and maps attack paths using a Neo4j digital twin…
 protectai/vulnhuntr
Zero shot vulnerability discovery using LLMs
 mmarting/unwaf
Go tool that passively discovers the real origin IP behind a WAF/CDN using multiple OSINT sources, then verifies candidates via HTML similarity, SSL…
 knqyf263/go-mal-pkgs
A security tool to detect malicious Go packages by verifying checksums in go.sum against the original source code
 kento-sec/cve-2024-34102
Go-based exploit for CVE-2024-34102, an XXE vulnerability in Adobe Commerce leading to remote code execution. Supports single and batch URL scanning…
 bughuntar/cve-2024-34102
Exploitation CVE-2024-34102
 neex/http2smugl
Detects and exploits HTTP request smuggling vulnerabilities via HTTP/2 to HTTP/1.1 conversion, using automated header smuggling techniques to…
 sadicann/andor
Blind SQL Injection Tool with Golang
 dwisiswant0/cve-2023-50164-poc
Proof of Concept for Path Traversal in Apache Struts ("CVE-2023-50164")
 google/capslock
CLI tool for analyzing Go package capabilities by tracing transitive calls to privileged standard library operations, enabling supply chain risk…
 ndrscodes/http2-rst-stream-attacker
Highly configurable tool to check a server's vulnerability against CVE-2023-44487 by rapidly sending HEADERS and RST_STREAM frames and documenting…
 rek2/goenumerator
A personal tool in GO for my usual first enumeration steps on a target
 nccgroup/glasgo
Go static analysis tool that checks for security issues using an AST.
 cythonic1/cve-2024-9264
A go implementation for CVE-2024-9264 which effect grafana versions 11.0.x, 11.1.x, and 11.2.x.
 retocode/golang-cve-2023-44487
Testing resources and attacker tool for CVE-2023-44487 (HTTP/2 Rapid Reset) to evaluate server resilience across Go, gRPC, reverse proxy, and nginx…
 hackersonlineclub/hocig1_2
HOCig- Automatic HOC Information Gathering Tool V 1.2
 hillu/local-log4j-vuln-scanner
[Moved to Codeberg] Simple local scanner for vulnerable log4j instances