

CVE-2026-48939
 shinthink/cve-2026-48939
Pre-auth arbitrary file upload RCE exploit for iCagenda Joomla extension < 4.0.8 (CVSS 10.0)
exploitationpayload-generationpenetration-testing+3
2
shinthink/cve-2026-48939Pre-auth arbitrary file upload RCE exploit for iCagenda Joomla extension < 4.0.8 (CVSS 10.0)
 chiefyoru/cve-2026-56291_poc
The Joomla extension Balbooa Forms is vulnerable to an unauthenticated arbitrary file upload that allows uploading executable files and leads to full…
 chiefyoru/cve-2026-56290_poc
The Joomla extension Page Builder CK is vulnerable to an unauthenticated arbitrary file upload that allows uploading executable files and leads to…
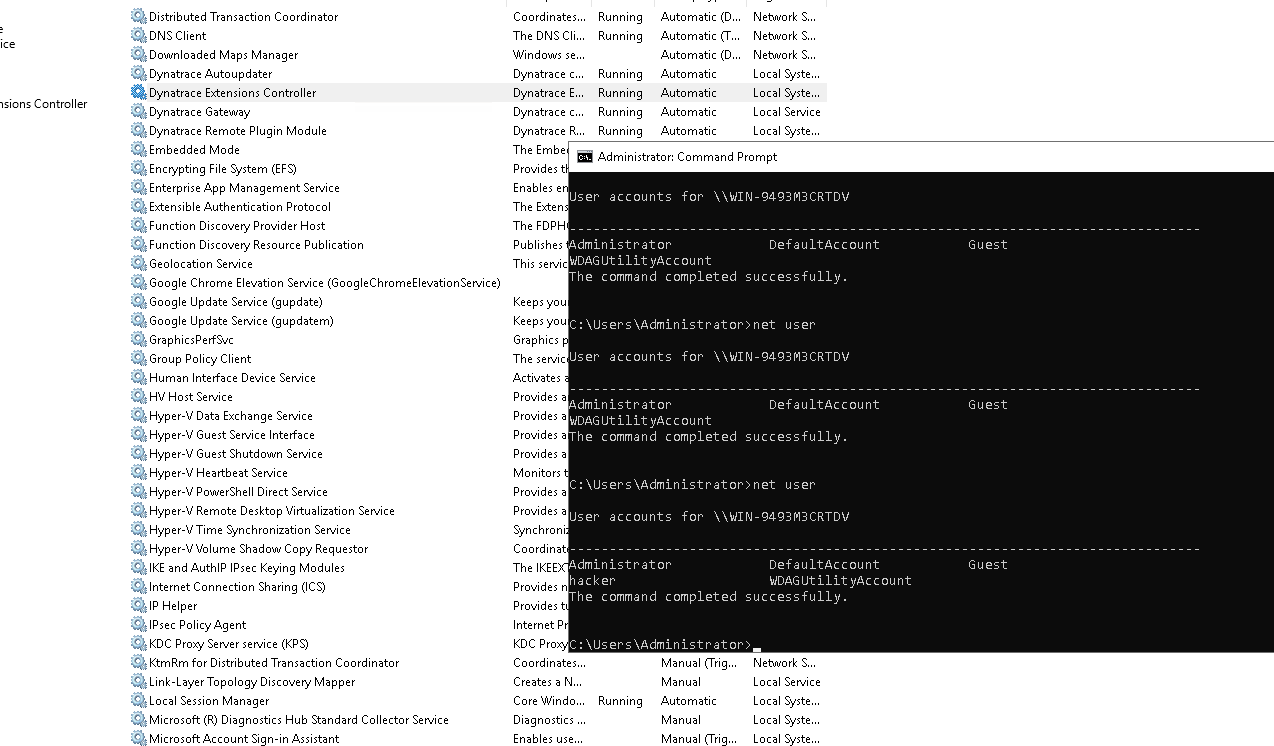 pentastic-be/cve-2025-61304
OS command injection vulnerability in Dynatrace ActiveGate ping extension up to 1.016 via crafted ip address
 wearehackers160/cve-2026-48907
CVE-2026-48907 is a critical improper access control vulnerability in the JCE editor extension for Joomla. It allows unauthenticated attackers to…
 bly-coder/python-exploit-cve-2020-25213
Python exploit for RCE in Wordpress
 galoget/responsivefilemanager-cve-2022-46604
Responsive FileManager v.9.9.5 vulnerable to CVE-2022-46604.
 nxploited/cve-2024-31114
Shortcode Addons <= 3.2.5 - Authenticated (Admin+) Arbitrary File Upload