

terrier
 heroku/terrier
Terrier is a Image and Container analysis tool that can be used to scan Images and Containers to identify and verify the presence of specific files…
container-securityhash-analysissupply-chain-security+1
228
heroku/terrierTerrier is a Image and Container analysis tool that can be used to scan Images and Containers to identify and verify the presence of specific files…
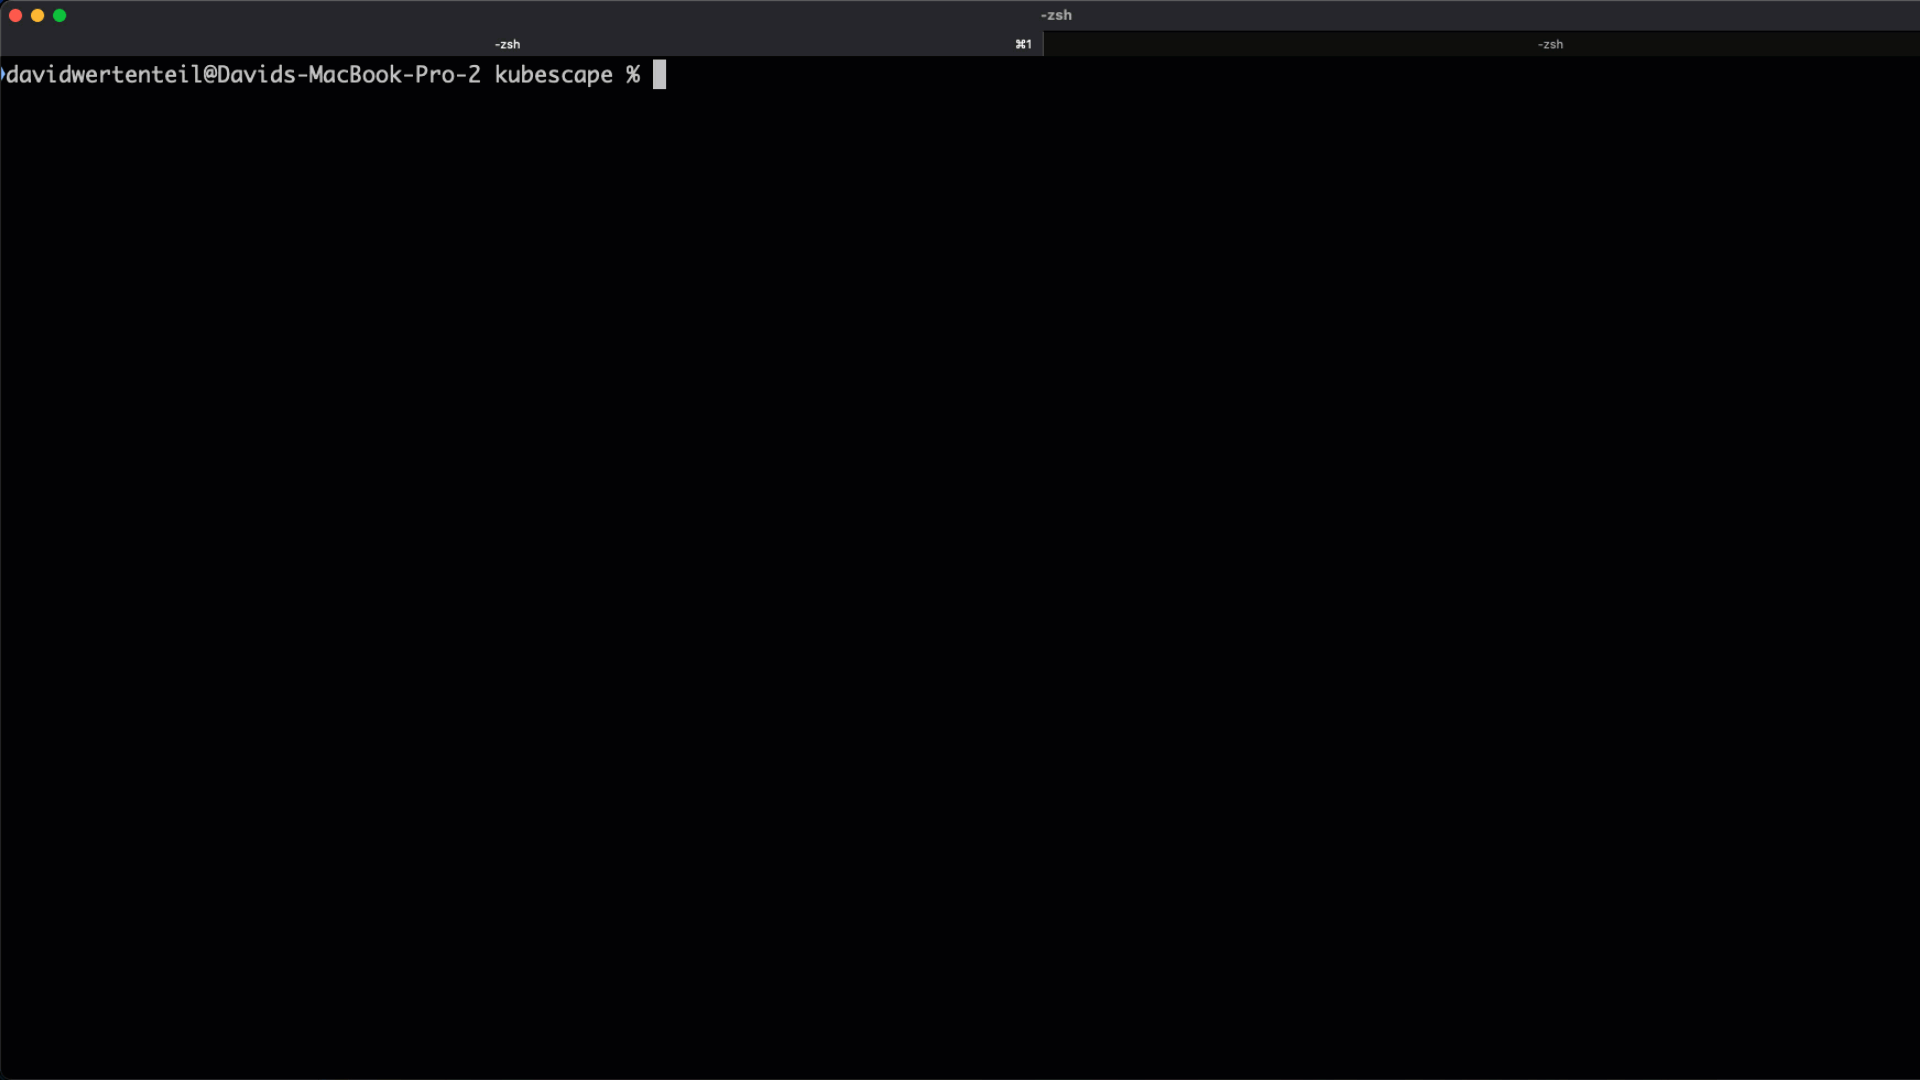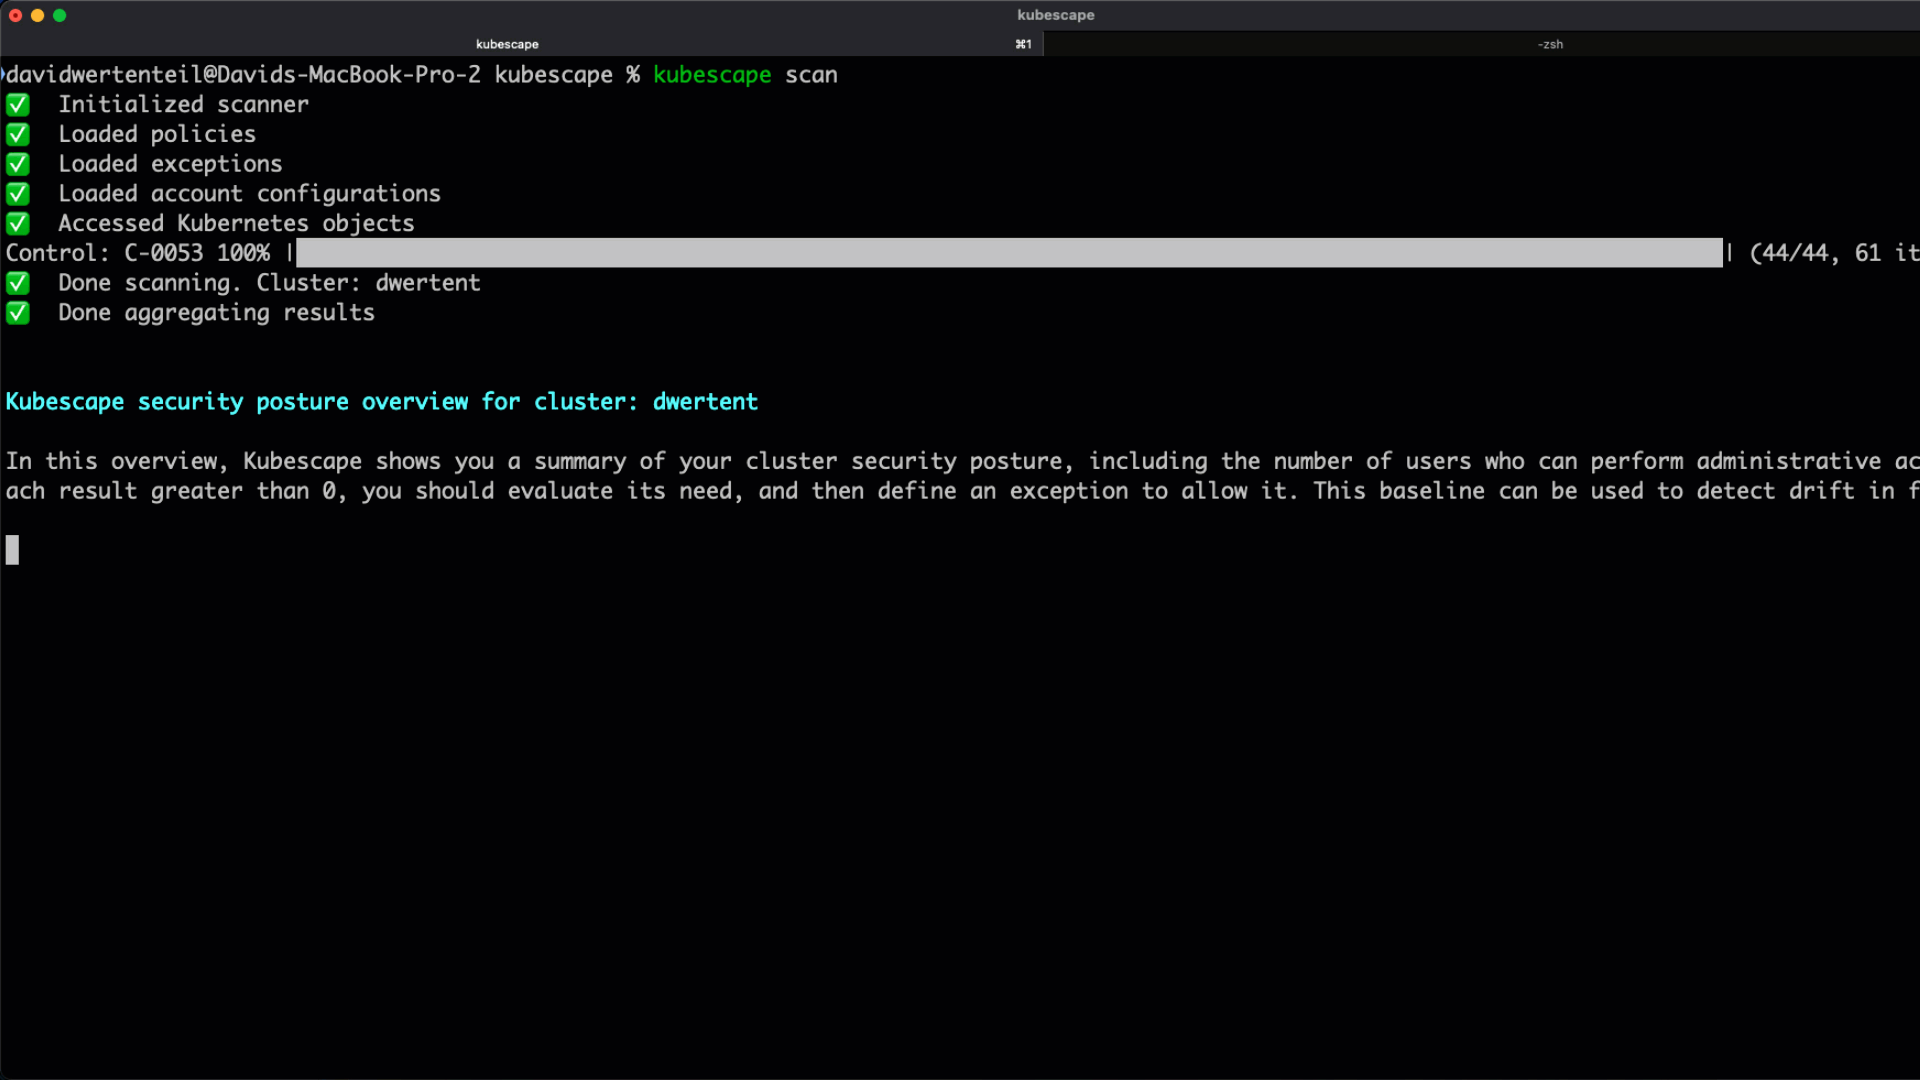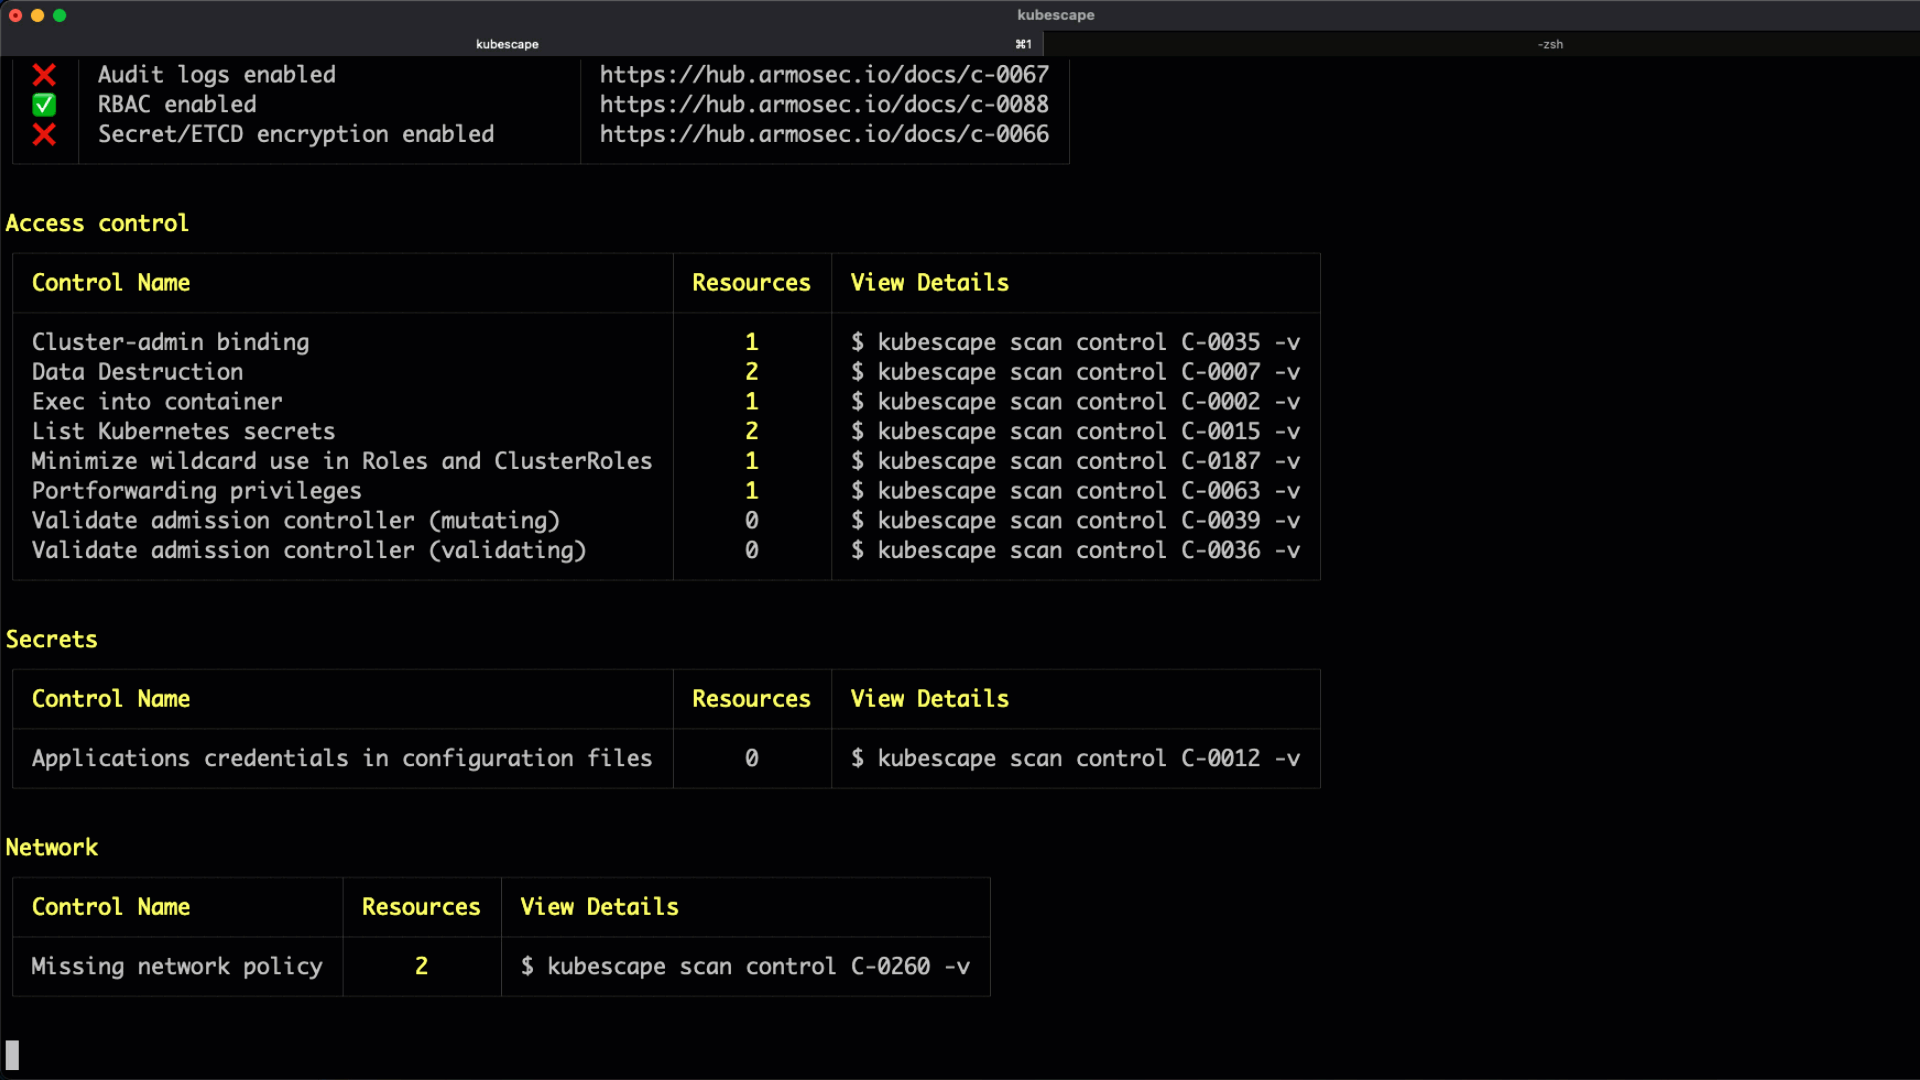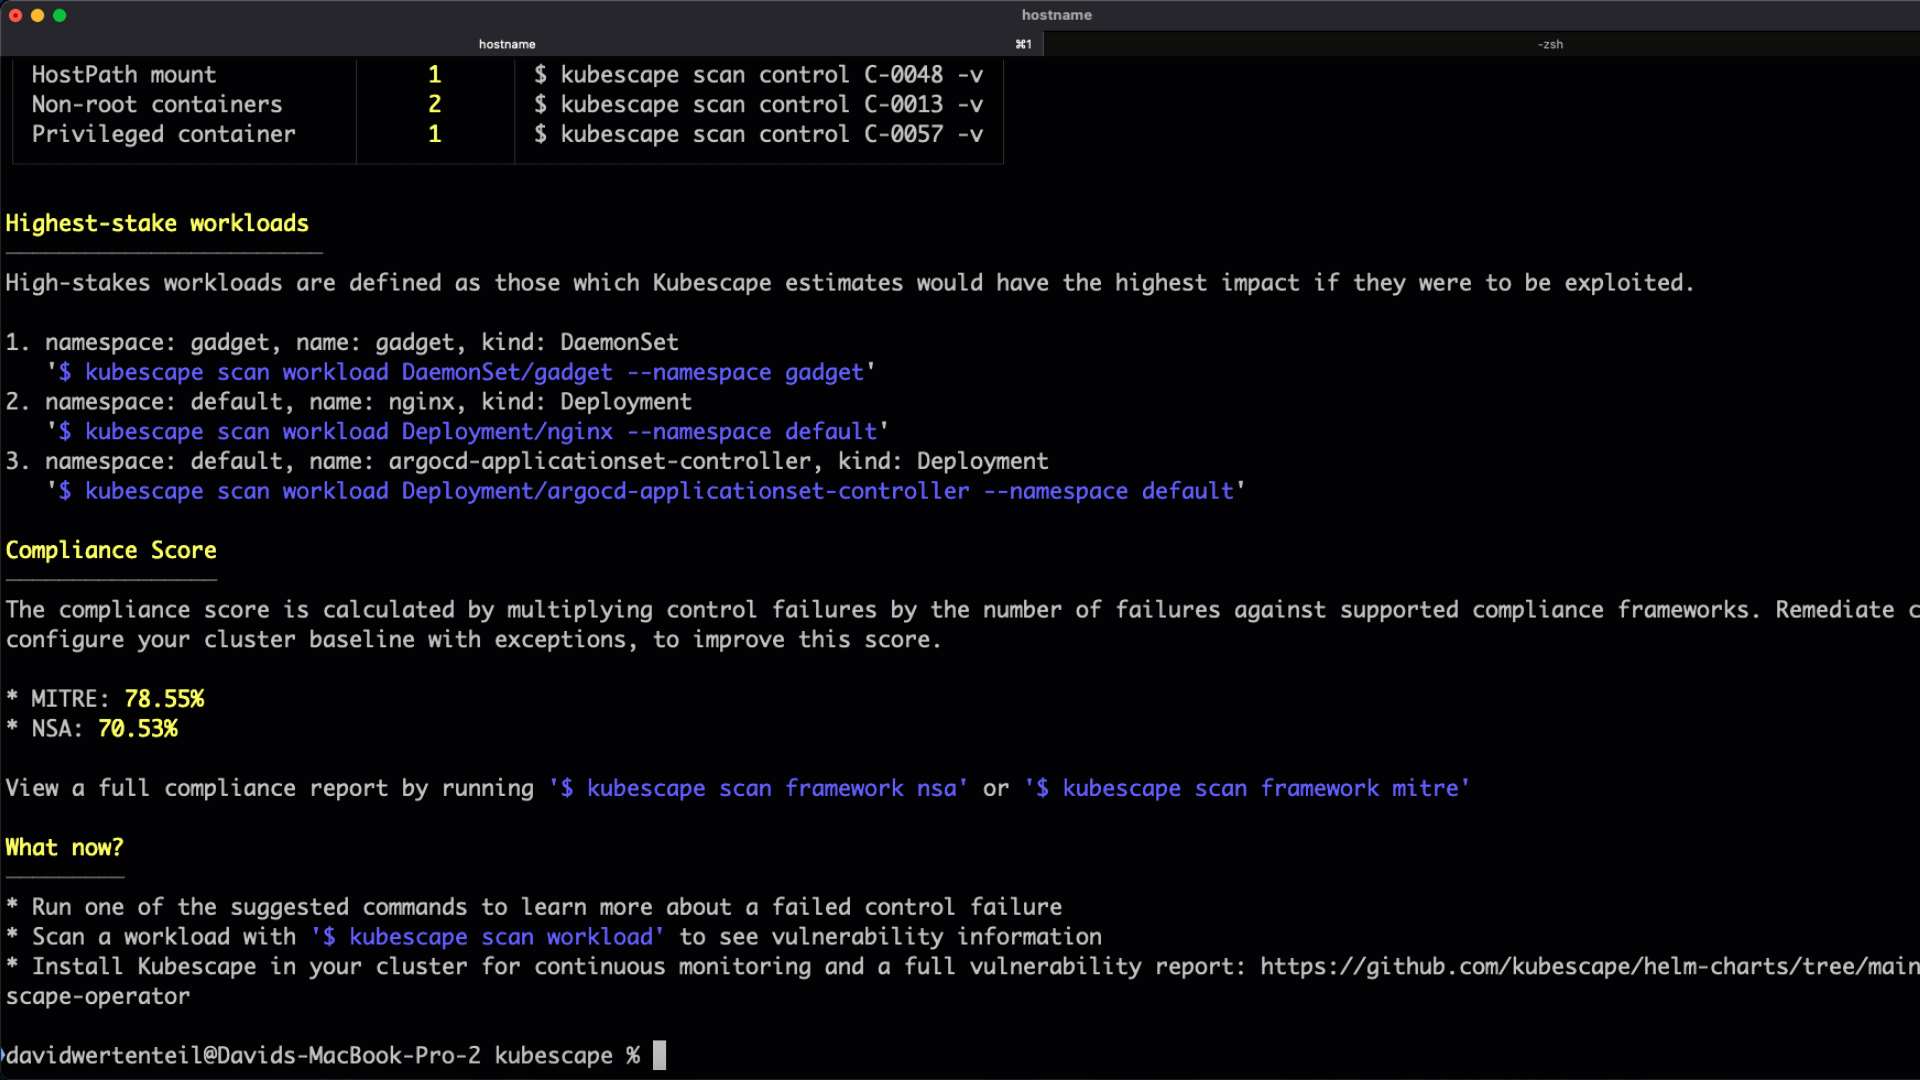 kubescape/kubescape
Open-source Kubernetes security platform scanning clusters, manifests, and images for misconfigurations, vulnerabilities, and compliance against NSA,…
 bridgecrewio/checkov
Static analysis tool for infrastructure as code that detects cloud misconfigurations, vulnerabilities, and secrets across Terraform, Kubernetes,…
 anchore/syft
CLI tool and library for generating a Software Bill of Materials from container images and filesystems
 notselwyn/cve-2024-1086
Universal local privilege escalation Proof-of-Concept exploit for CVE-2024-1086, working on most Linux kernels between v5.14 and v6.6, including…
 bishopfox/forticrack
Decrypt encrypted Fortienet FortiOS firmware images
 dtact/divd-2021-00038--log4j-scanner
Recursive vulnerability scanner for Log4j CVEs in archives and Docker images. Detects JndiLookup.class and vulnerable versions via SHA256 hashes,…
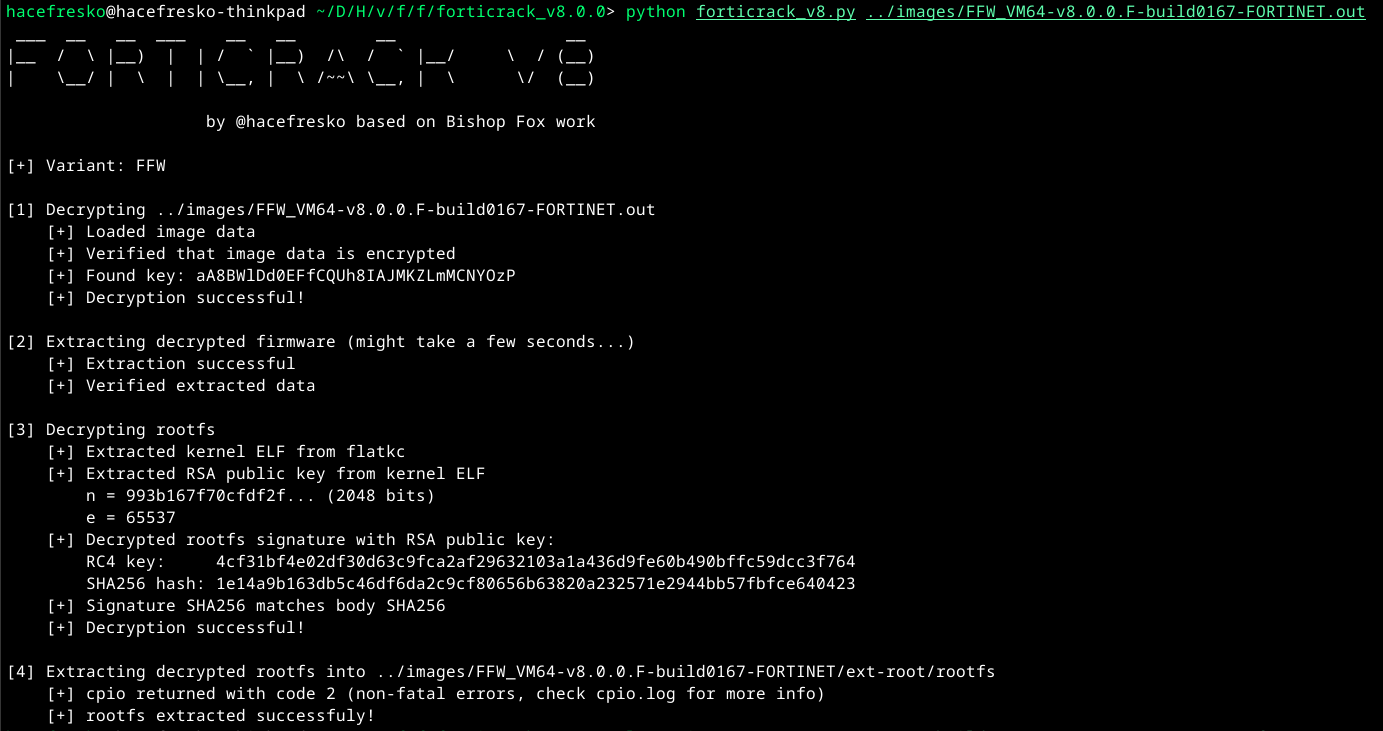 hacefresko/forticrack_v8
Decrypt and extract FortiOS 8.0.0 firmware images.
 ctf-o-matic/capture-the-flag
Helper scripts to remaster Linux Live CD images for the purpose of creating ready to use security wargames with pre-installed vulnerabilities to…
 kljunowsky/cve-2022-44268
Proof-of-concept exploit for CVE-2022-44268 enabling arbitrary file read via poisoned PNG images uploaded to vulnerable ImageMagick instances.…
 ebux/cable-modems
Black-box security evaluation of five ISP cable modem/router gateways, analyzing firmware images and documenting 35+ vulnerabilities including…
 aradhyacp/secflow
AI-driven automated threat analysis pipeline that routes files, URLs, IPs, domains, or images through specialized security analyzers and generates…
 blueteamsteve/cve-2021-41773
Vulnerable docker images for CVE-2021-41773
 portbuster1337/cve-2026-27771
CVE-2026-27771 - Gitea/Forgejo Container Registry Auth Bypass Exploit PoC - Pull private container images without authentication
 kaill-jlq/mmskillrisk
Benchmark and evaluation harness testing whether LLM agents resist malicious instructions hidden in multimodal skill images, with 108 cases across…
 nccgroup/test_avb_key
Python utility to check if Android verified boot images (vbmeta) are signed with publicly known test keys, identifying misconfigurations in release…
 fakeshell/cve-2021-1931-bbry-key2
proof of concept CVE-2021-1931 exploit for the blackberry key2 (le) that allows to flash unsigned images temporarily
 ankur-katiyar/log4j-docker
Docker images and k8s YAMLs for Log4j Vulnerability POC (Log4j (CVE-2021-44228 RCE Vulnerability)