
FollinaXploit
 abbarhissarh/follinaxploit
A Command Line based python tool for exploit Zero-Day vulnerability in MSDT (Microsoft Support Diagnostic Tool) also know as 'Follina' CVE-2022-30190.
command-and-controlexploitationpayload-generation+3
8
abbarhissarh/follinaxploitA Command Line based python tool for exploit Zero-Day vulnerability in MSDT (Microsoft Support Diagnostic Tool) also know as 'Follina' CVE-2022-30190.
 tylabs/qs_old
Command line tool for scanning streams within office documents plus xor db attack
 owasp/cwe-tool
A command line CWE discovery tool based on OWASP / CAPSEC database of Common Weakness Enumeration.
 zcgonvh/cve-2017-0213
CVE-2017-0213 for command line
 pentest-a2p2v/pentest-a2p2v-core
Core A2P2V functionality (command line based)
 valtersit/wordpress-cve-scanner
Scan your WordPress core, themes and plugins for known CVEs from the command line. Open source, auditable, privacy-first — powered by the ValtersIT…
 unicorn-hyh/cve-2026-31156
There is a path injection vulnerability in OpenPLC-v3, which arises from the program not performing any validity checks on the file path parameters…
 peckre/pncve-win10-20h2-exploit
A one-click script to gain a System privileges command line in Windows 10 20H2 that exploits CVE-2021-1675
 alt3kx/cve-2002-0740
SLRNPull Spool Directory Command Line Parameter Buffer Overflow Vulnerability
 ayrx/tlsenum
A command line tool to enumerate TLS cipher-suites supported by a server
 hrishikesh7665/follina_exploiter_cli
Exploit Microsoft Zero-Day Vulnerability Follina (CVE-2022-30190)
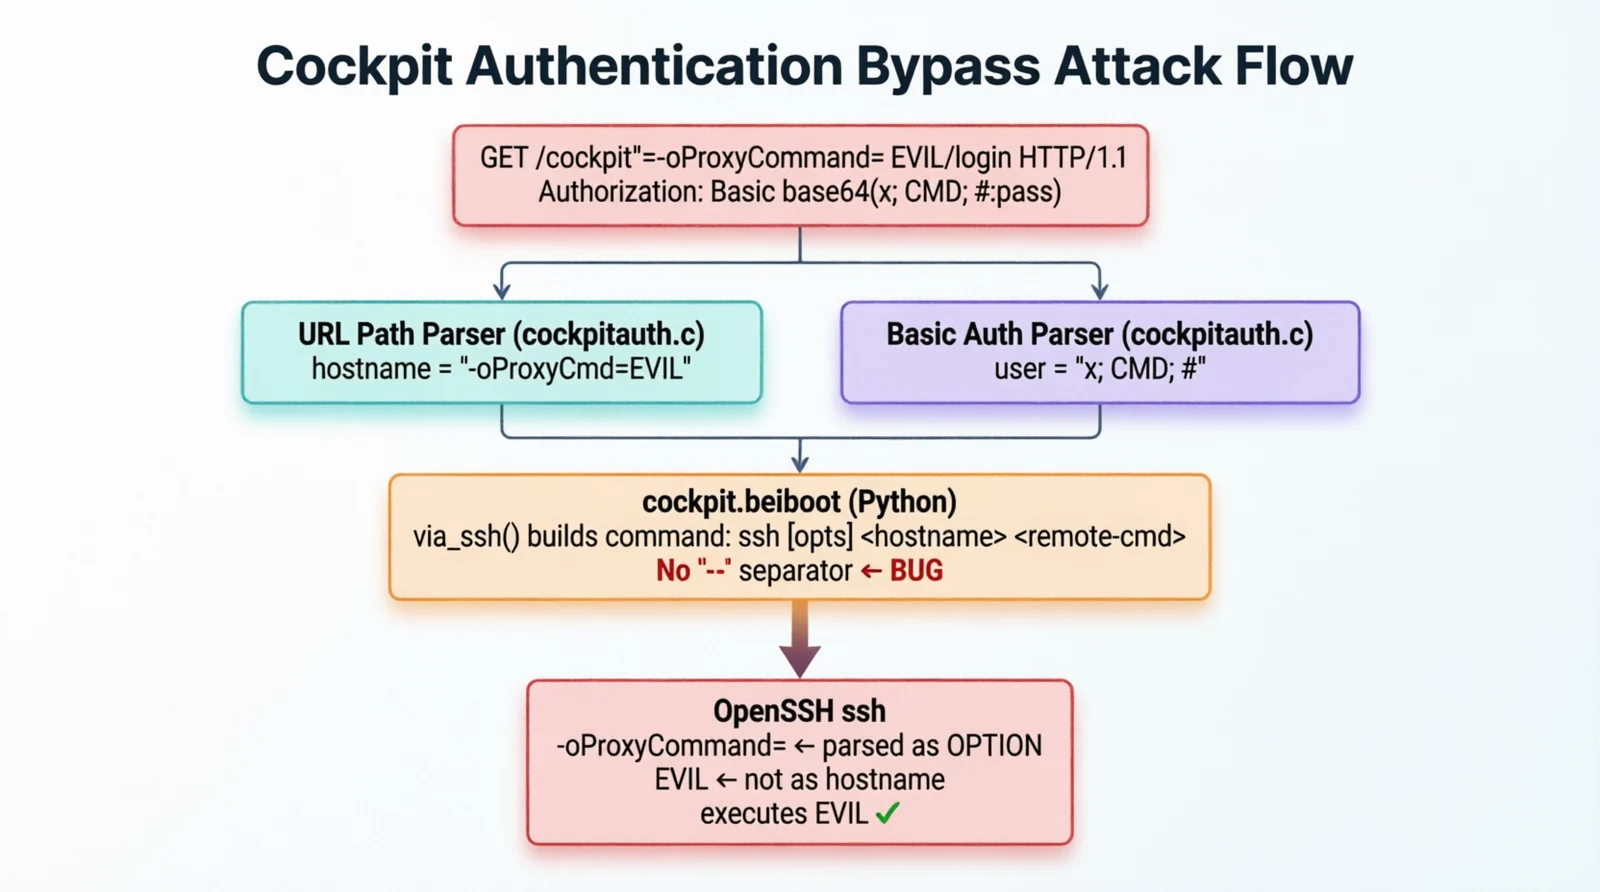 cyberheartmi9/cve-2026-4631-cockpit-rce
Cockpit: Unauthenticated Remote Code Execution via SSH Command-Line Argument Injection
 falcon-lnhg/strutsshell
Interactive command-line shell for exploiting Apache Struts CVE-2017-5638. Automates HTTP/HTTPS exploitation with real-time shell interaction on…
 noname-elv/cve-2026-48907
Python CLI that exploits CVE-2026-48907 in Joomla JCE via profile-import upload, verifies shell paths, and opens an interactive command channel on…
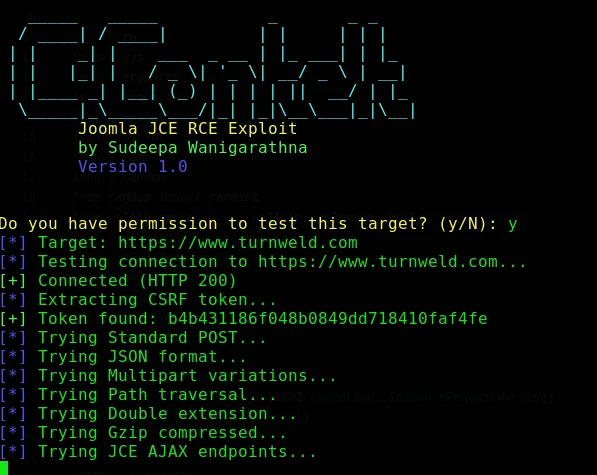 cerberusmrxi/jcezploit-cve-2026-48907
Automated RCE exploit for Joomla JCE (CVE-2026-48907) with interactive shell, batch command execution, file download, and proxy support for…
 e4zyy/project-cve-2026-33017
CVE-2026-33017 - Langflow Unauthenticated RCE Exploit
 baboopan/log4shell-cve-2021-44228-demo
Log4Shell Demo with AWS
 r1cksec/cheatsheets
Collection of knowledge about information security