
htb-ctf-walkthroughs
 rootsecnz/htb-ctf-walkthroughs
Walkthroughs for Capture the Flag challenges on the HTB Cybersecurity Platform.
ctfeducationexploitation+6
rootsecnz/htb-ctf-walkthroughsWalkthroughs for Capture the Flag challenges on the HTB Cybersecurity Platform.

 swisskyrepo/payloadsallthethings
A list of useful payloads and bypass for Web Application Security and Pentest/CTF
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
 timothyjxhn/deliberatelyvulnerablewebapp
A Deliberately Vulnerable Web Application built on Struts 2 (CVE-2017-5638) and Log4J (CVE-2021-44228) for testing and demonstration of OWASP Top 10…
 webgoat/webgoat
Deliberately vulnerable web application with interactive lessons and challenges for learning web application security and penetration testing…
 owasp/owaspwebgoatphp
A deliberately vulnerable web application for learning web application security.
 bwasp/bwasp
BoB Web Application Security Project
 p0pr0ck5/lua-ffi-libinjection
LuaJIT FFI bindings for libinjection, providing SQL injection and XSS detection with context-specific APIs for web application security.
 nu11secur1ty/payload-lists
Curated collection of injection payloads for web application security testing, covering SSTI, XXE, XSS, SSRF, SQLi, NoSQLi, LDAP, command injection,…
 alchemist3dot14/cve-2024-30270-poc
The script exploits Mailcow vulnerabilities via XSS and RCE, emphasizing the need for robust security measures and responsible usage to enhance web…
 fairyming/cve-2019-11043
Proof-of-concept exploit for CVE-2019-11043, a PHP-FPM underflow vulnerability, built on the pocsuite framework for automated web application…
 vutiendat323/int14107_cve-2021-35042
Django-based CTF blog platform with integrated CVE-2021-35042 exploit tool for learning web application security and vulnerability exploitation.
 owasp/mimosa
Open-source web application security challenge platform with auto-approved registration, SQL dump generation, and Docker deployment for hands-on…
 shoucheng3/vert-x3__vertx-web_cve-2019-17640_3-9-3
Analysis and exploitation code for CVE-2019-17640, a vulnerability in Vert.x-Web. Provides a targeted test case for security researchers validating…
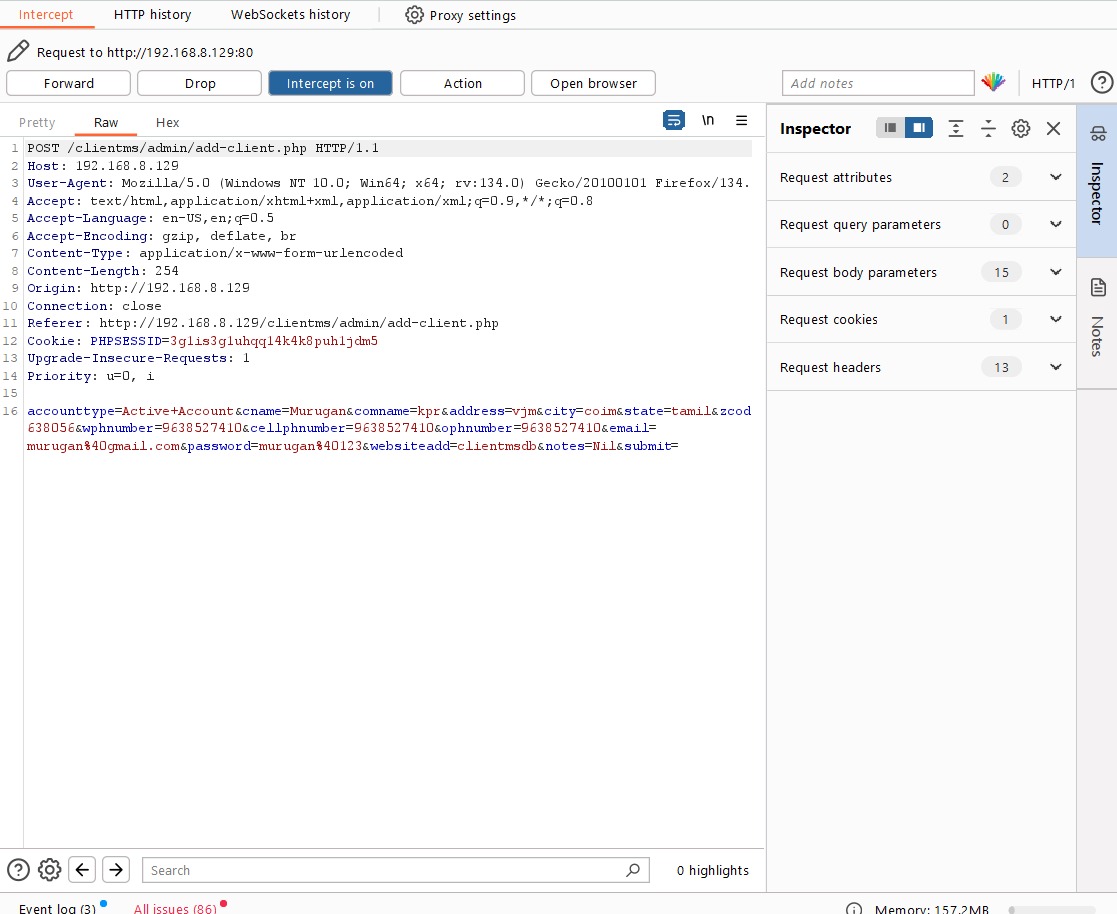 moulish2004/cve-2025-44603-csrf-leads_to_create_fakeusers
Proof-of-concept demonstrating a CSRF vulnerability in a PHP-based Client Management System, with HTML exploit code and mitigation strategies for web…
 imjdl/cve-2012-4431
Apache Tomcat source code repository for CVE-2012-4431, a Java servlet container vulnerability. Provides the vulnerable codebase for analysis and…
 costacoco/adiscon
SQL injection exploit for Adiscon LogAnalyzer v4.1.13 and earlier (CVE-2023-34600). Provides proof-of-concept code for testing web application…
 shoucheng3/apache__jspwiki_cve-2022-46907_2-11-3
Exploit module for Apache JSPWiki CVE-2022-46907, targeting a Java-based wiki platform with JAAS security integration. Provides vulnerability…