
POC_CVE-2025-32433
Proof-of-concept exploit for CVE-2025-32433 with simulated and real attack modes, including a Flask-based C2 server for reverse shell callbacks and…

Proof-of-concept exploit for CVE-2025-32433 with simulated and real attack modes, including a Flask-based C2 server for reverse shell callbacks and…

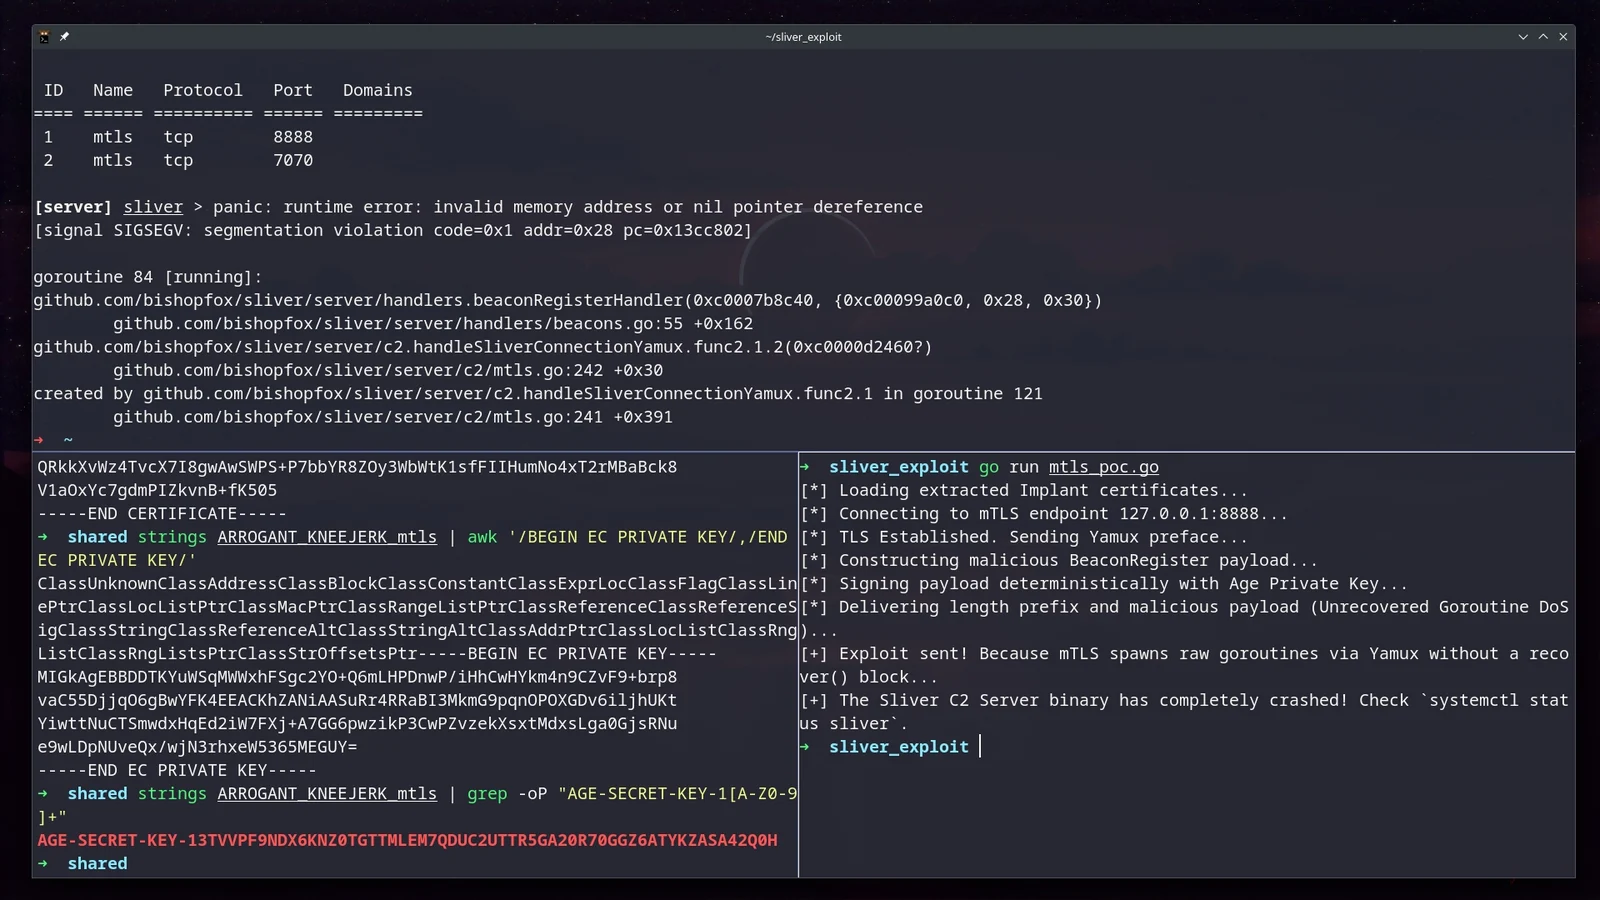
Proof-of-concept exploit for CVE-2026-29781, weaponizing captured Sliver implant credentials to trigger a nil-pointer panic and crash the C2 server…

Research PoC demonstrating a prototype pollution and JavaScript injection chain in Adobe Acrobat Reader, enabling privileged JavaScript execution and…

Step-by-step reproduction guide for CVE-2022-30190 (Follina) MSDT remote code execution vulnerability, including malicious document creation and C2…

Source code minh họa máy chủ c2 demo kịch bản thực thi của CVE-2024-23700

Proof-of-concept demonstrating CORS to CSRF chain on Sliver's unauthenticated MCP interface, enabling silent interaction with C2 from any webpage.

Step-by-step walkthrough of exploiting CVE-2022-22965 (Spring4Shell) with Metasploit, deploying a C2 listener, and mitigating the vulnerability by…

MCP Server for Metasploit

a signal handler race condition in OpenSSH's server (sshd)

LdapNightmare is a PoC tool that tests a vulnerable Windows Server against CVE-2024-49113

command injection vulnerability in the web server of some Hikvision product. Due to the insufficient input validation, attacker can exploit the…

his repository contains an automated Proof of Concept (PoC) script for exploiting **CVE-2025-24813**, a Remote Code Execution (RCE) vulnerability in…

Proof-of-concept exploit for Microsoft Exchange Server RCE vulnerability CVE-2023-36745, enabling remote code execution via authenticated PowerShell…

Exploit for CVE-2018-3191 targeting Oracle WebLogic Server via T3 protocol, enabling unauthenticated remote code execution with JNDI payload…

Time Based SQL Injection in Zabbix Server Audit Log --> RCE

Proof-of-concept exploit for CVE-2020-2551, demonstrating remote code execution in Oracle WebLogic Server via the IIOP protocol. Includes default…

DHCP Server Remote Code Execution impact: 2008 R2 SP1 до Server 2019

Exploit for CVE-2021-26084 targeting Confluence Server OGNL injection vulnerability for unauthenticated remote code execution.