

faraday_burp
 infobyte/faraday_burp
Burp Extension for collaboration in Faraday
api-security-testingdevsecopspenetration-testing+3
13
infobyte/faraday_burpBurp Extension for collaboration in Faraday
 shoucheng3/perwendel__spark_cve-2018-9159_2_7_2_fixed
Lightweight Java 8 web framework for building REST APIs and web applications, with built-in routing, static file serving, and template engine support.
 projectdiscovery/nuclei
Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…
 semgrep/semgrep
Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.
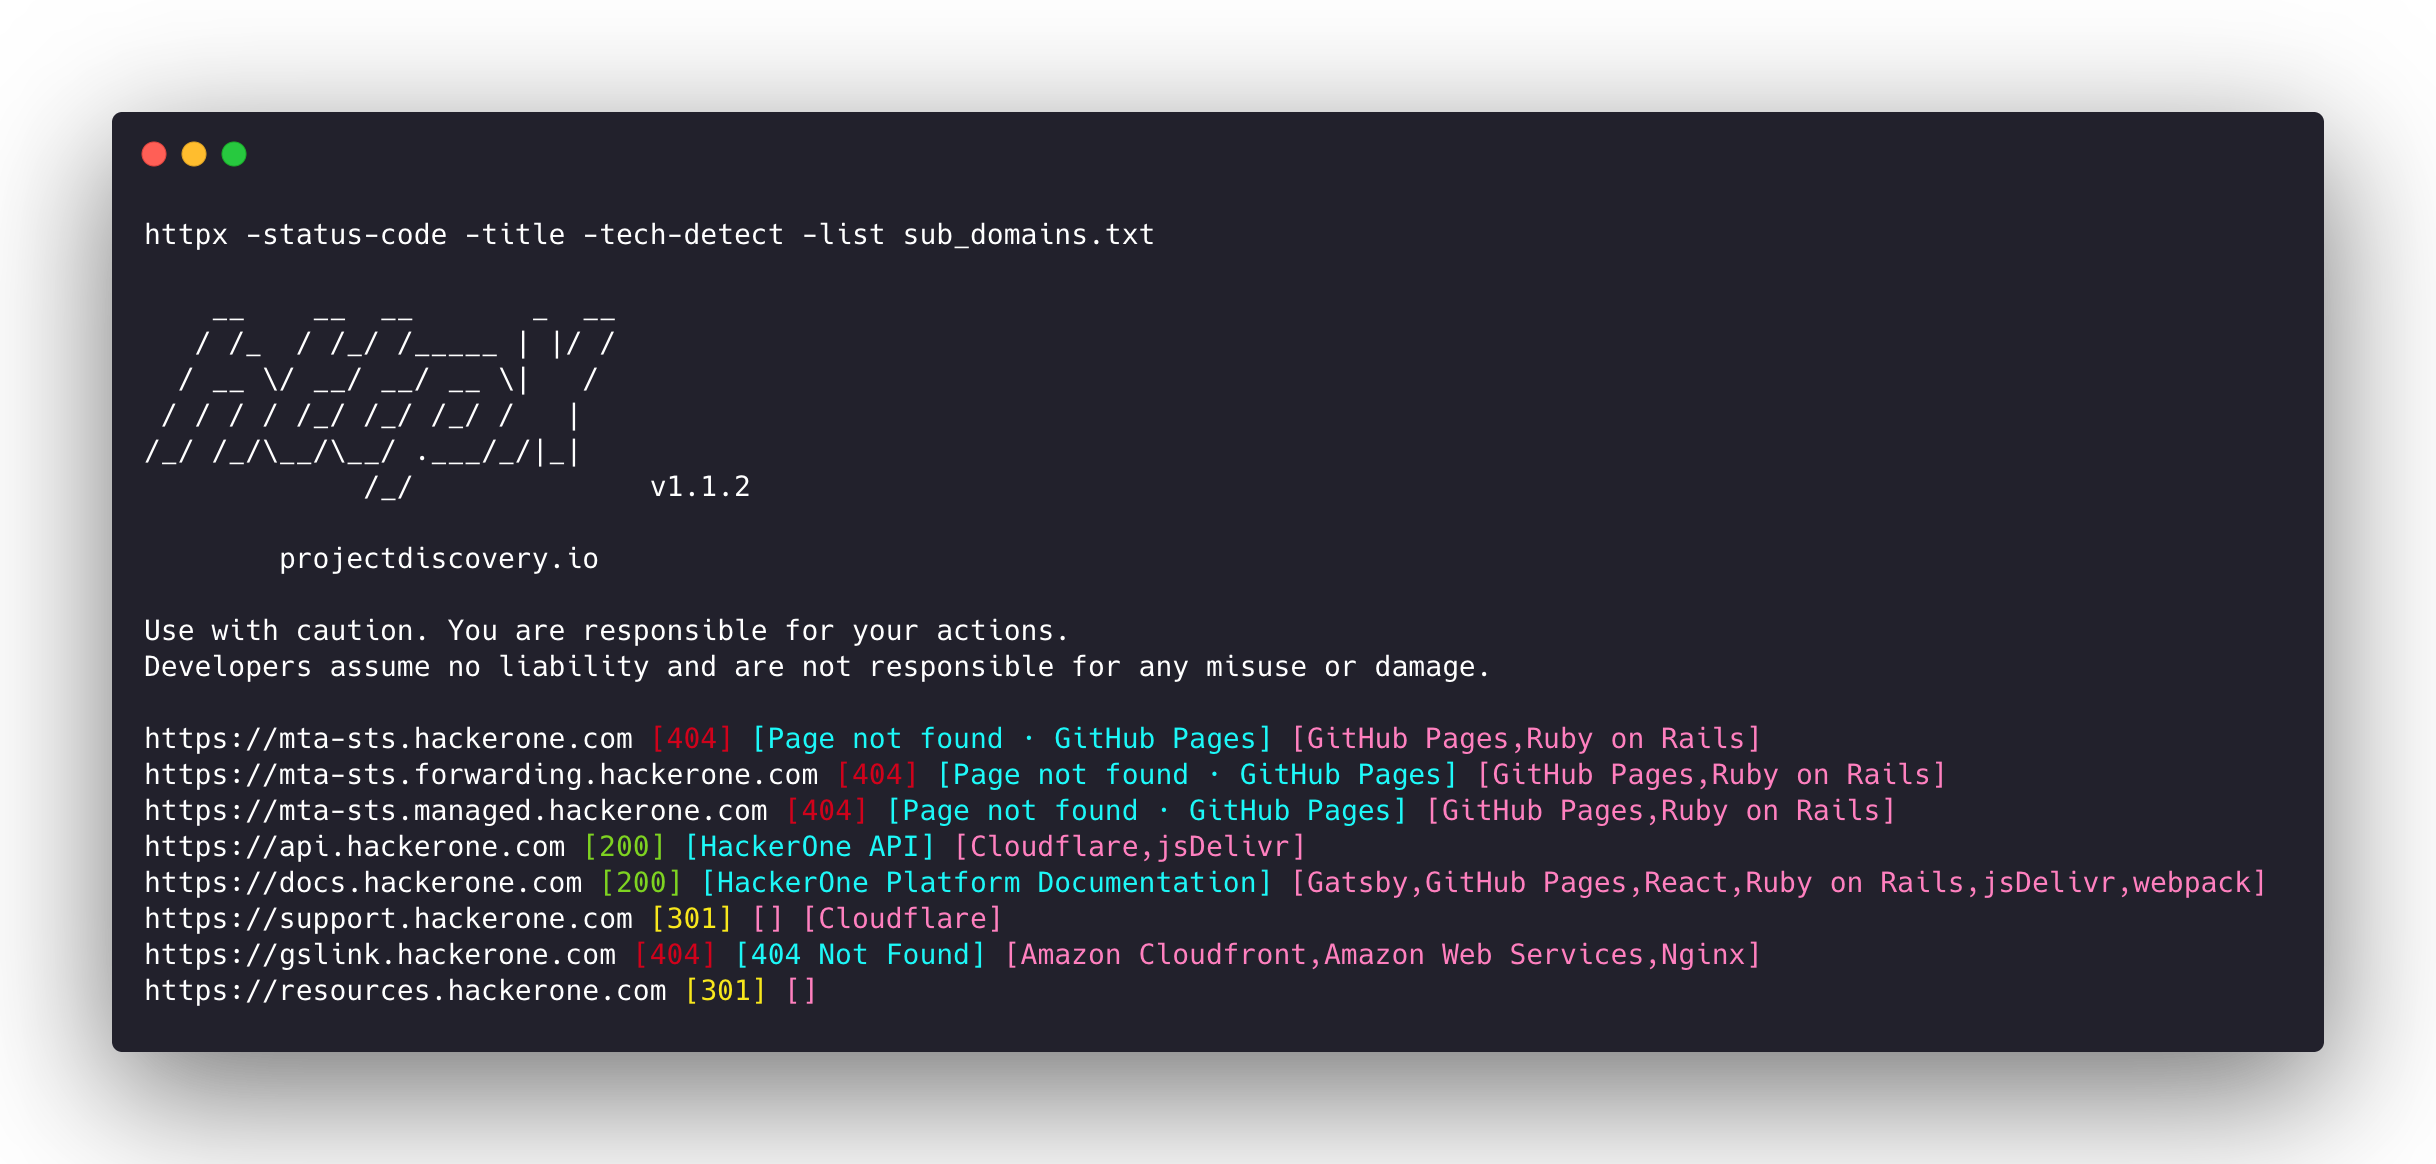 projectdiscovery/httpx
Fast, multi-probe HTTP toolkit for reconnaissance and information gathering. Probes TLS, CSP, headers, tech stack, and CDN. Supports matchers,…
 owasp/crapi
Deliberately vulnerable microservices API designed for hands-on training in the OWASP API Security Top 10 risks, with built-in challenges and a…
 erev0s/vampi
Vulnerable REST API with OWASP top 10 vulnerabilities for security testing
 dolevf/damn-vulnerable-graphql-application
Damn Vulnerable GraphQL Application is an intentionally vulnerable GraphQL service implementation designed for learning about and practising GraphQL…
 aws/http-desync-guardian
Analyze HTTP requests to minimize risks of HTTP Desync attacks (precursor for HTTP request smuggling/splitting).
 teycir/burpapisecuritysuite
Burp Suite extension for API security testing with 15 attack types, 108+ payloads, intelligent fuzzing, BOLA/IDOR detection, AI integration, and…
 tno-s3/wuppiefuzz
A coverage-guided REST API fuzzer developed on top of LibAFL
 owasp/raider
OWASP Raider: a novel framework for manipulating the HTTP processes of persistent sessions
 horizon3ai/cve-2023-27532
Proof-of-concept exploit for CVE-2023-27532 in Veeam Backup and Replication that abuses an unsecured API endpoint to extract credentials from the…
 owasp/agent-security-regression-harness
Executable security regression testing for agentic applications and MCP-integrated systems.
 portswigger/pentest-mapper
A Burp Suite Extension for Application Penetration Testing to map flows and vulnerabilities
 trailofbits/slither-mcp
MCP server for Slither static analysis of Solidity smart contracts
 hackinglz/maps_scanner
MAPS cloud scanner and response parser for Microsoft Defender research.
 emo-crab/slinger
An HTTP client specifically developed for security researchers