

CVE-2026-42613
 ivanesk315/cve-2026-42613
PHP proof-of-concept for CVE-2026-42613, demonstrating exploitation of the referenced vulnerability.
exploitationpenetration-testingvulnerability-analysis+2
ivanesk315/cve-2026-42613PHP proof-of-concept for CVE-2026-42613, demonstrating exploitation of the referenced vulnerability.
 4ybrick/cve-2026-79303
Proof-of-concept for CVE-2026-79303, a critical boolean-blind SQL injection in Kaiten affecting order_by and order_direction parameters, with…
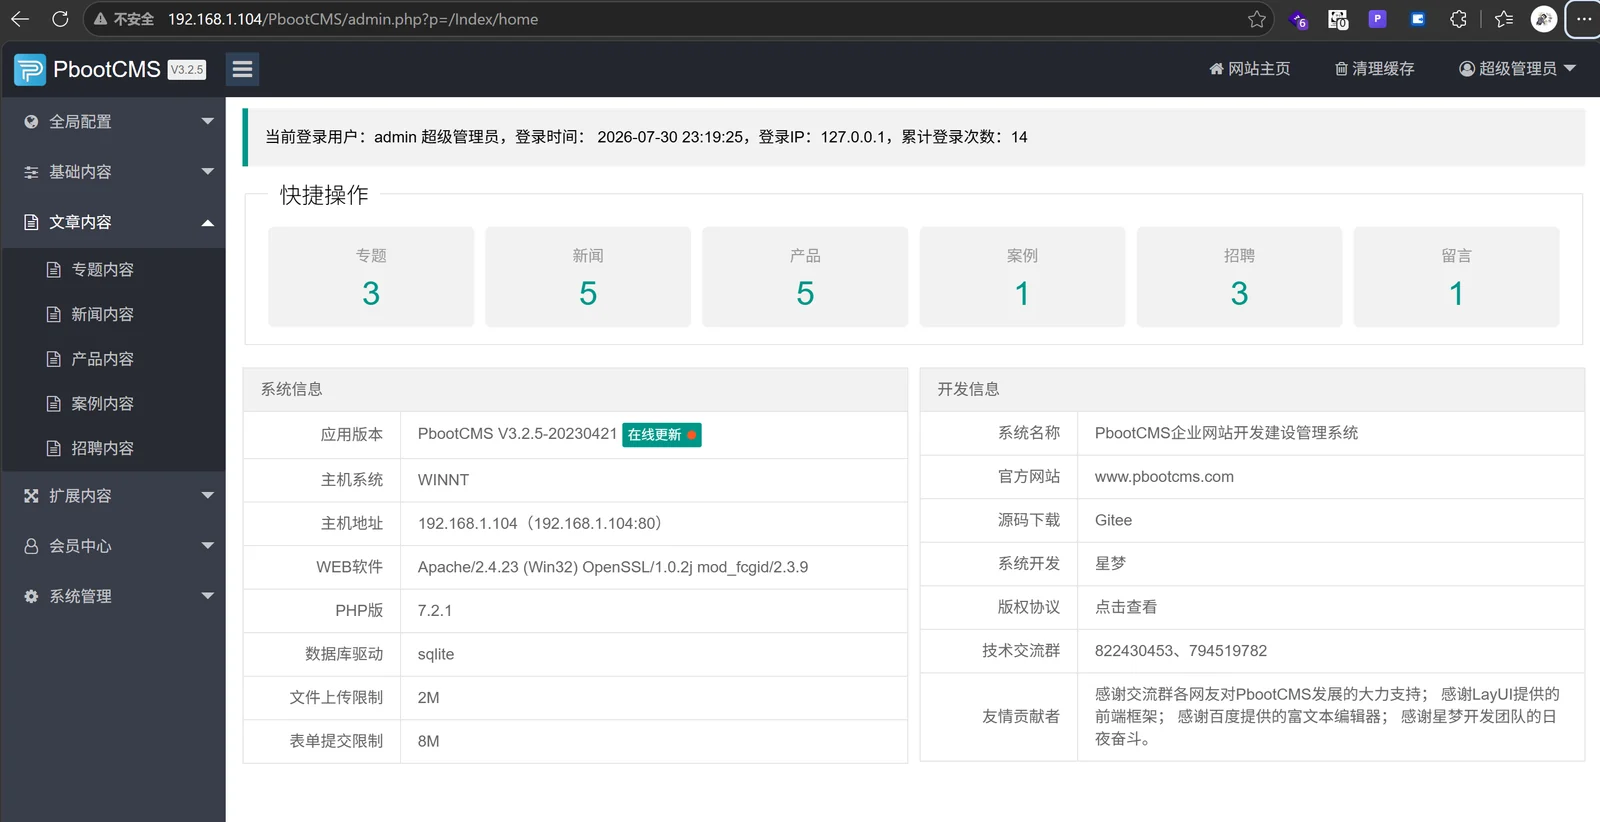 jhli07/cve-2026-79387-pbootcms-sql-injection
Proof-of-concept for CVE-2026-79387, an authenticated SQL injection in PbootCMS user management allowing arbitrary field updates and account takeover.
 bombobombone/cve-2026-73311
Proof-of-concept exploit demonstrating OAuth2 authorization code reuse in XenForo before 2.3.13, allowing token replay and multiple token families.
 bombobombone/cve-2026-73314
Proof-of-concept exploit for CVE-2026-73314, a PayPal REST webhook signature verification bypass in XenForo before 2.3.13, allowing unauthorized…
 sneakynachos/cve-2026-85046-who-put-the-silverback-guerilla-in-the-wasm
Proof-of-concept exploit for CVE-2026-85046 in Chrome 152.0.7977.75, demonstrating type confusion in sort() to achieve arbitrary code execution via a…
 0xterror/cve-2026-81780-hash-form
Exploit for CVE-2026-81780: unauthenticated file upload in WordPress Hash Form plugin leading to remote code execution via crafted PHP payloads.
 mufasa-noir/xmlrpc-pingback-vulnerability-poc
This is my own written POC on the xmlrpc-pingback vulnerabiity found on wordpress. CVE-2025-54352.
 bombobombone/cve-2026-73310
Proof of concept and technical write-up for CVE-2026-73310, an OAuth2 authorization code redirect URI binding flaw in XenForo before 2.3.13,…
 testardou/cve-2026-65540
Popup for CF7 with Sweet Alert <= 1.6.5 - Cross-Site Request Forgery
 starscow/cve-2024-38077-poc
Proof-of-concept exploit code for CVE-2024-38077, a remote code execution vulnerability in Windows Remote Desktop Licensing Service. Backup copy, not…
 bombobombone/cve-2026-74239
Proof of concept and technical write-up for CVE-2026-74239, a path traversal vulnerability in XenForo style archive imports on Windows, allowing file…
 linan-oo/cve-2026-52307
Proof-of-concept for CVE-2026-52307, an authenticated stored XSS in 1CMS v5.6 Column Management, with reproduction steps and impact analysis.
 moksh-nfsu/cve-2026-36392
Proof-of-concept for stored XSS in RISE CRM item title field (CVE-2026-36392), demonstrating session hijacking and account takeover with remediation…
 valencenavy/isolatedanarchy-public
Proof-of-concept exploit for CVE-2026-87492, a Chromium site isolation bypass using a patched renderer and MojoJS to demonstrate cross-origin data…
 anirbala98/cve-2022-4140
WordPress plugin Welcart e-Commerce < 2.8.5 - Arbitrary File Read
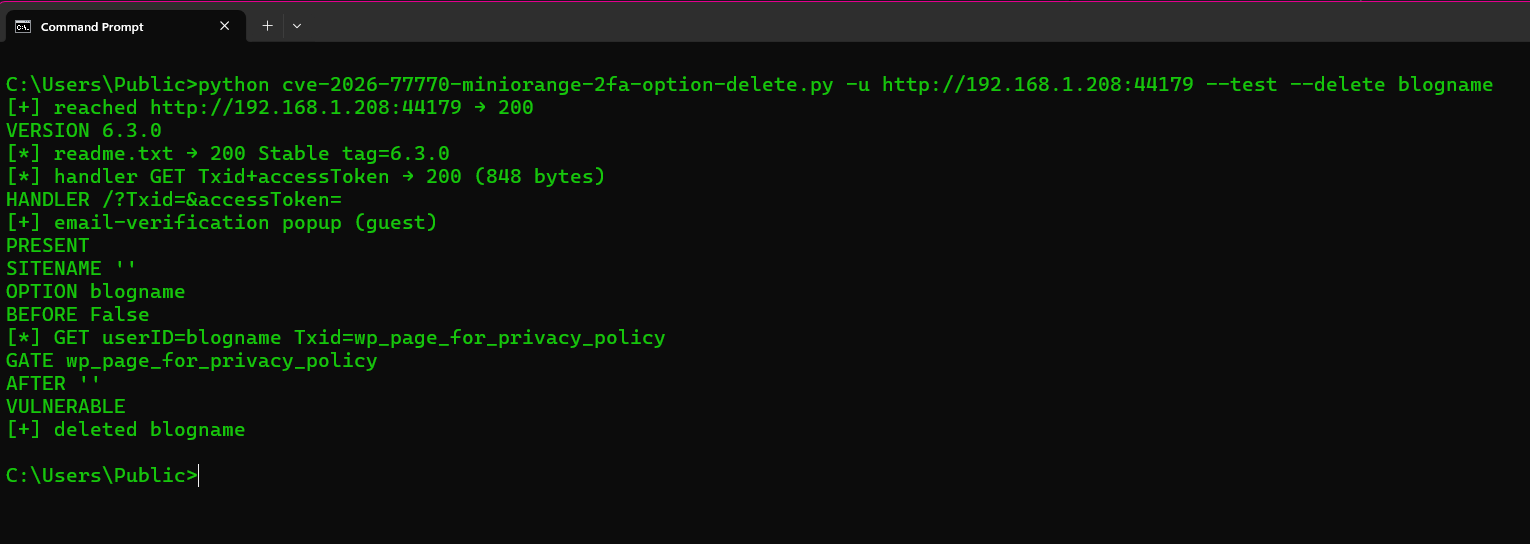 cflowsec/cve-2026-77770
Python PoC for CVE-2026-77770, an unauthenticated arbitrary WordPress option deletion flaw in the miniOrange 2FA plugin (<= 6.3.0) via the…
 hateshape/frevvomapexec
PoC Exploit for CVE-2018-8820