

silica
 nathan-luevano/silica
Exhaustive differential validation of all 4.3B AArch64 instruction encodings.
binary-analysisdynamic-analysis-sandboxingfuzzing+5
41 month ago
nathan-luevano/silicaExhaustive differential validation of all 4.3B AArch64 instruction encodings.
 madcdan/jndilookup
Some tools to help mitigating Apache Log4j 2 CVE-2021-44228
 bcoles/rootkit-signal-hunter
Detect Linux rootkits which use signals to elevate process privileges.
 tang-yikai/copy-fail-mitigation-with-bpftrace
CVE-2026-31431, AKA Copy Fail, can be mitigated in one-line with bpftrace
 crackercat/cve-2023-4863-
Triggering the famous libweb 0day vuln with libfuzzer
 johanneslks/cve-2026-32945
PJSIP DNS Compression Pointer Heap OOB Read (Remote DoS)
 vladjrfhfg/react-site-cve-2025-55182
Intentionally vulnerable Next.js corporate landing page demonstrating CVE-2025-55182, a JSON injection leading to RCE/SSRF via unsafe deserialization…
 andrii-kovalenko-celonis/log4j-vulnerability-demo
Endpoint to test CVE-2021-44228 – Log4j 2
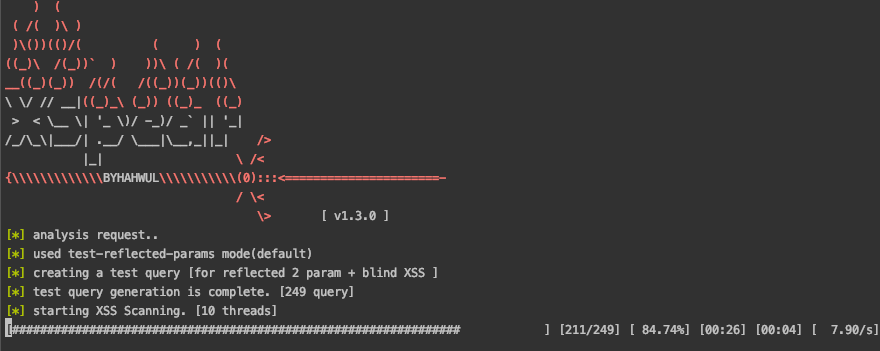 hahwul/xspear
🔱 Powerfull XSS Scanning and Parameter analysis tool&gem
 microsoft/onefuzz
A self-hosted Fuzzing-As-A-Service platform
 alchemist3dot14/cve-2025-2783
Simulated PoC for CVE-2025-2783 — a sandbox escape vulnerability in Chrome's Mojo IPC. Includes phishing delivery, memory fuzzing, IPC simulation,…
 sentebale/cve-2026-46300
Proof-of-concept exploit for CVE-2026-46300, demonstrating sandbox escape on Kylin Linux. Intended for authorized security research and educational…
 sneakynachos/cve-2026-2796-escape-wasm-by-using-wasm
PoC exploit chain for CVE-2026-2796: SpiderMonkey WebAssembly sandbox escape (signature type confusion -> arbitrary R/W -> RCE)
 abraxas/n8n-function-vm2
Proof-of-concept and lab for an n8n 2.42.0 sandbox escape: hidden Function/FunctionItem nodes execute JS in the main process, giving authenticated…
 jaf0rk/cve-2026-14431
Exploit for CVE-2026-14431 providing V8 sandbox read/write primitives via a crafted JavaScript file, targeting Chromium's V8 engine on Linux x64.
 trustsig-eu/wasm2c-tableflip
wasm2c sandbox escape. An untrusted WebAssembly module breaks out of the generated C sandbox and executes an arbitrary shell command on the host.
 wgnet/wg.copyfail.patch
eBPF-based workaround for CVE-2026-31431 (Copy.Fail) that filters or kills AF_ALG socket creation to prevent local privilege escalation and container…
 canhieu/cve-2026-100671-poc
Local-only proof-of-concept verifier for CVE-2026-100671, reproducing Grav Twig page-cache session-cookie disclosure and replay against loopback…