
ModSecurity
 owasp-modsecurity/modsecurity
ModSecurity is an open source, cross platform web application firewall (WAF) engine for Apache, IIS and Nginx. It has a robust event-based…
anti-botapi-securitydefensive-tools+7
9.8k
owasp-modsecurity/modsecurityModSecurity is an open source, cross platform web application firewall (WAF) engine for Apache, IIS and Nginx. It has a robust event-based…
 owasp/asvs
Application Security Verification Standard
 xalgord/massive-web-application-penetration-testing-bug-bounty-notes
A comprehensive guide for web application penetration testing and bug bounty hunting, covering methodologies, tools, and resources for identifying…
 christophetd/log4shell-vulnerable-app
Spring Boot web application vulnerable to Log4Shell (CVE-2021-44228).
 numencyber/vulnerability_poc
Collection of proof-of-concept exploits and technical analyses for high-impact CVEs, covering browser memory corruption, TCP/IP RCE, and web…
 dzonerzy/gowapt
Go Web Application Penetration Test
 4auvar/vulnnodeapp
Deliberately vulnerable Node.js web application for practicing exploitation of SQL injection, XSS, IDOR, command injection, XXE, and deserialization…
 owasp/tcasvs
OWASP Thick Client Application Security Verification Standard
 owasp/fiasse
A Framework for Integrating Application Security into Software Engineering (FIASSE) using the Securable Software Engineering Model (SSEM)
 infosecak/defenselessv1
Just another vulnerable web application.
 ulyssessaicha/cve-2023-6875
Proof-of-concept exploit for CVE-2023-6875, demonstrating a web application vulnerability. Includes code and instructions for reproducing the issue.
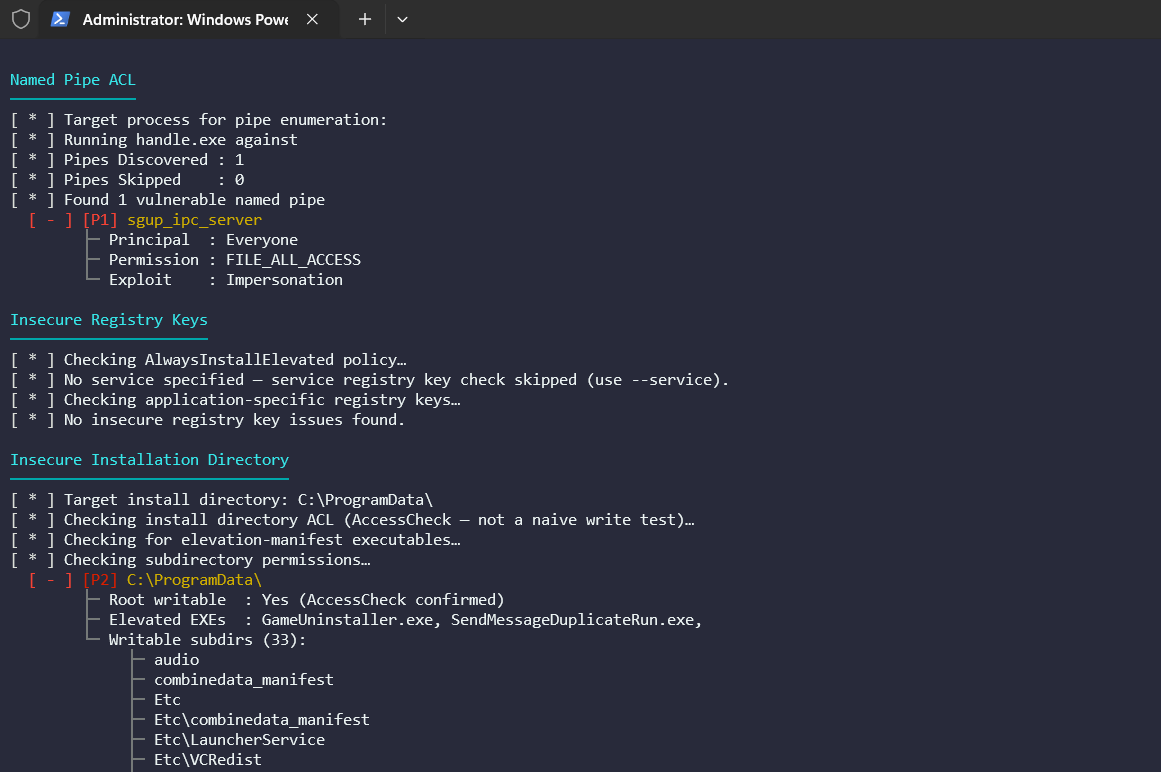 shellkraft/anvil
Anvil is a runtime-first attack surface assessment tool for Windows thick client applications, built for penetration testers and security researchers…
 nishantiyer/cve-2020-15215-discord-poc
Proof-of-concept validation harness for Electron boundary hardening, modeling renderer/main-process isolation, IPC policy enforcement, and navigation…
 halkichi0308/cve-2015-9251
Proof-of-concept exploit for CVE-2015-9251, demonstrating a specific web application vulnerability with minimal code for testing and verification.
 venablee/cve-2026-30252
The ZenShare Suite application is vulnerable by a Reflected Cross-Site Scripting (XSS) vulnerability, affecting web application login and recovery…
 snapattack/damn-vulnerable-log4j-app
Vulnerable web application to test CVE-2021-44228 / log4shell and forensic artifacts from an example attack
 nu11secur1ty/cve-2021-44228-vuln-app
Dockerized vulnerable web application demonstrating the Log4j CVE-2021-44228 remote code execution vulnerability for educational exploitation and…
 lite-os15/lab-001-gitea-cve-2026-20896-
Educational lab for exploiting Gitea CVE-2026-20896, focusing on web application vulnerability analysis and penetration testing.