CVE-2025-55182_Vulnerable-Application

Intentionally vulnerable React Server Components lab for studying CVE-2025-55182. Provides a safe environment for security researchers, developers,…

Intentionally vulnerable React Server Components lab for studying CVE-2025-55182. Provides a safe environment for security researchers, developers,…

Python-based XSS vulnerability scanner with support for POST/GET requests, parameter injection in cookies/referer/user-agent, and multiple encoding…

Modular web vulnerability scanner with template-driven detection engine for automated testing of XSS, SQLi, LFI, RFI, and sensitive file/directory…

Proof-of-concept exploit for CVE-2021-23369, demonstrating a specific vulnerability in a JavaScript-based application.

Java application vulnerable to the CVE-2021-44228 (a.k.a log4shell) vulnerability

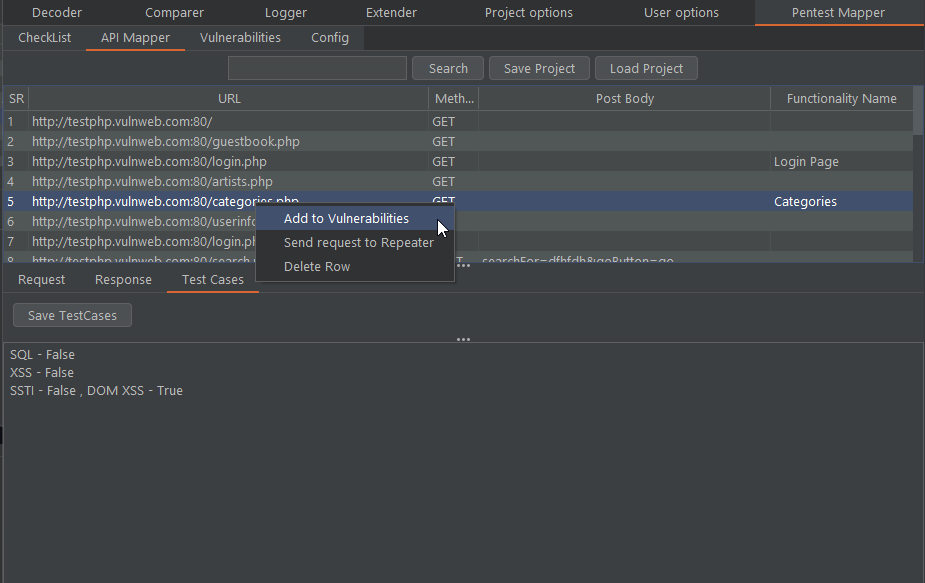
A Burp Suite Extension for pentester and bug bounty hunters an to maintain checklist, map flows, write test cases and track vulnerabilities

listmonk’s Session Persistence After Password Reset and Password Change

Proof-of-concept for CVE-2021-3130: demonstrates credential exposure via HTML obfuscation bypass in Open-AudIT up to 4.0.2, revealing SSH, SNMP, and…

XSS spider - 66/66 wavsep XSS detected

PwnXSS: Vulnerability (XSS) scanner exploit

An automatic XSS discovery tool

traxss | Automated XSS Vulnerability Scanner Currently In Development 🐍 HACKTOBERFEST PROJECT 2019

This extension will help you to detect GET/POST based XSS vulnerability in any website easily

Web application with vulnerabilities found in real cases, both in pentests and in Bug Bounty programs.

Formal inter-procedural taint analysis engine for application security. Tracks untrusted data across function boundaries, persistence layers, and…

Collaborative application security testing between humans and agents via CLI and MCP

"Sucosh" is an automated Source Code vulnerability scanner and assessment framework for Python(Flask-Django) & NodeJs capable of performing code…

A TypeScript package that provides AI-powered agents for Application Security (AppSec) tasks, built on top of the frontier models.