CVE-2019-9053-CMS-Made-Simple-2.2.10---SQL-Injection-Exploit

Python exploit for CVE-2019-9053 SQL injection in CMS Made Simple 2.2.10 with password hash cracking and user enumeration capabilities.

Python exploit for CVE-2019-9053 SQL injection in CMS Made Simple 2.2.10 with password hash cracking and user enumeration capabilities.


Recursively scan folders with VirusTotal API to detect malware. Features hash lookup, CSV export, real-time progress, and rate-limit handling for…

This script is a modified version of the original exploit by Daniele Scanu which exploits an unauthenticated SQL injection vulnerability in CMS Made…

Proof-of-concept decrypting Araxis Merge's DPAPI-protected server credentials (CVE-2026-92680), demonstrating insufficiently protected credential…

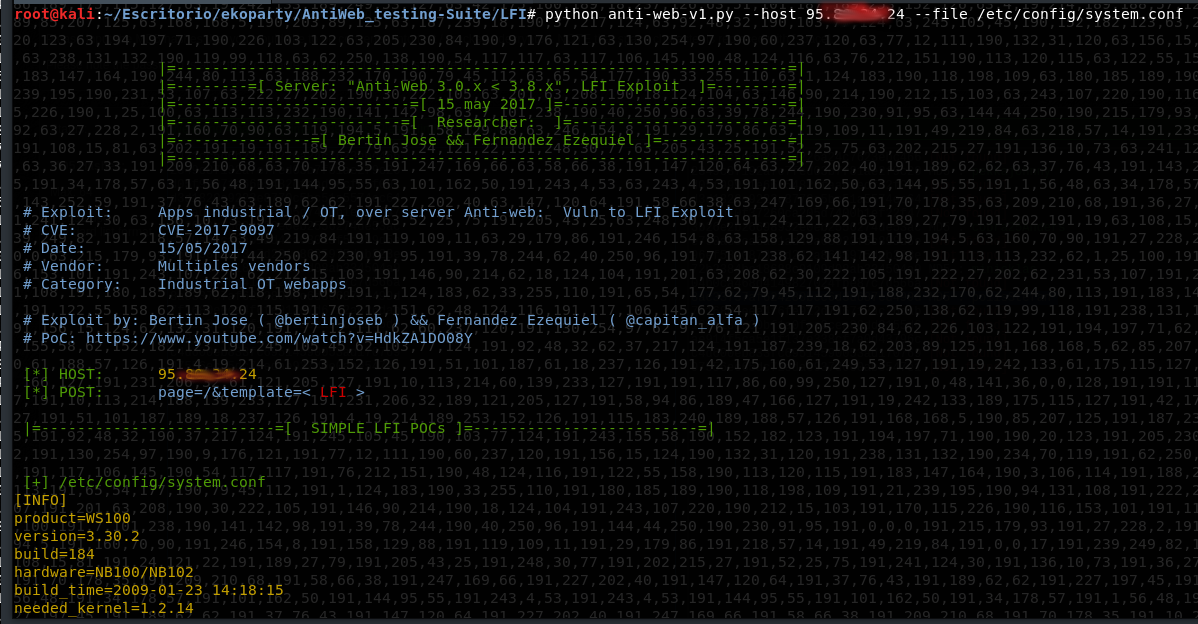
Suite de herramientas que sacan partido del CVE-2017-9097 (+RCE)

Python proof-of-concept demonstrating IPFS CID spoofing via multihash length extension, highlighting content-addressing verification flaws that can…

Bash and PowerShell scripts to scan a local filesystem for Log4j .jar files which could be vulnerable to CVE-2021-44228 aka Log4Shell.

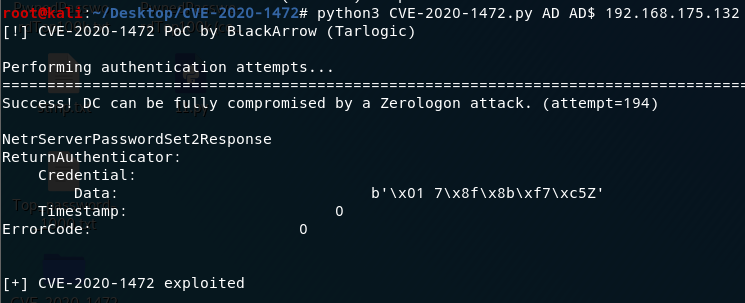
cve-2020-1472_Tool collection

Exploit for CVE-2019-9053, an unauthenticated SQL injection in CMS Made Simple 2.2.9, that extracts admin credentials and optionally cracks the…

Windows File Explorer Zero Click NTLMv2-SSP Hash Disclosure

Simple hash cracker for Apache Shiro hashes written in Golang. Useful for exploiting CVE-2024-4956.

cve-2024-21413

A simple implementation/code smash of a bunch of other repos

This repo shows an exploit to CVE-2021-24762. This is an Blind SQLi exploit that, on default config, greps the admin password.

Exploit for CVE-2025-2011

CMS Made Simple < 2.2.10 - SQL Injection . Actual working version

CVE-2023-23397 C# PoC