
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
884 results
cve-2019-10678 preview

cve-2019-10678

GitHubcved-sources/cve-2019-10678

Docker container providing a vulnerable environment for CVE-2019-10678, designed for security training and exploitation practice within the Cved…
container-securityeducationexploitation+2
1
5 years ago
chakra-exploit-framework preview

chakra-exploit-framework

GitHubntdelta/chakra-exploit-framework

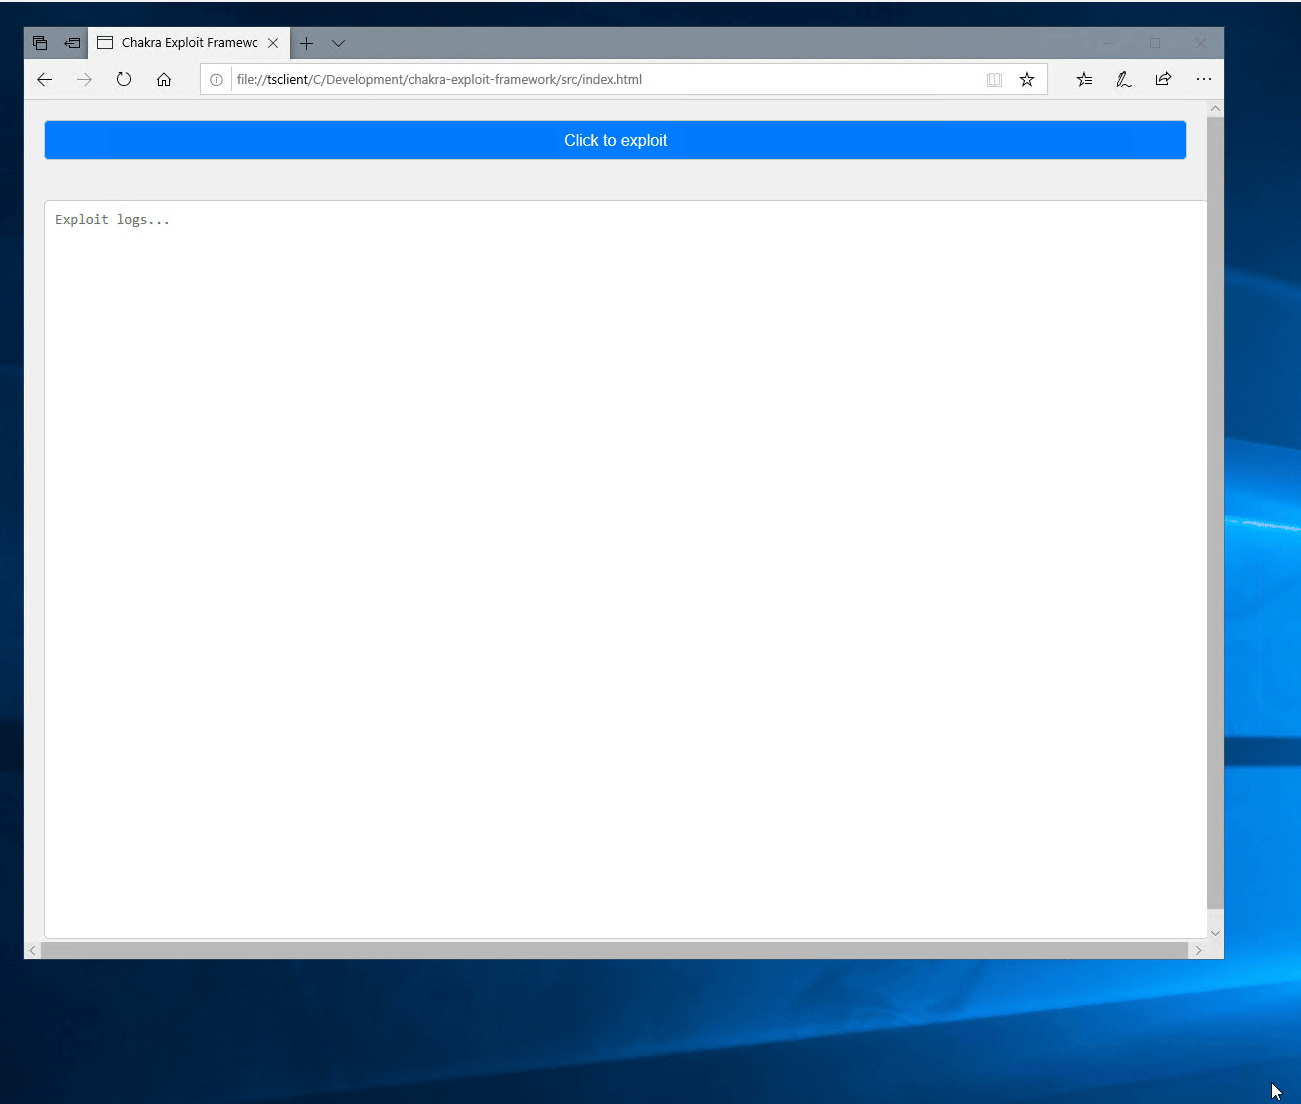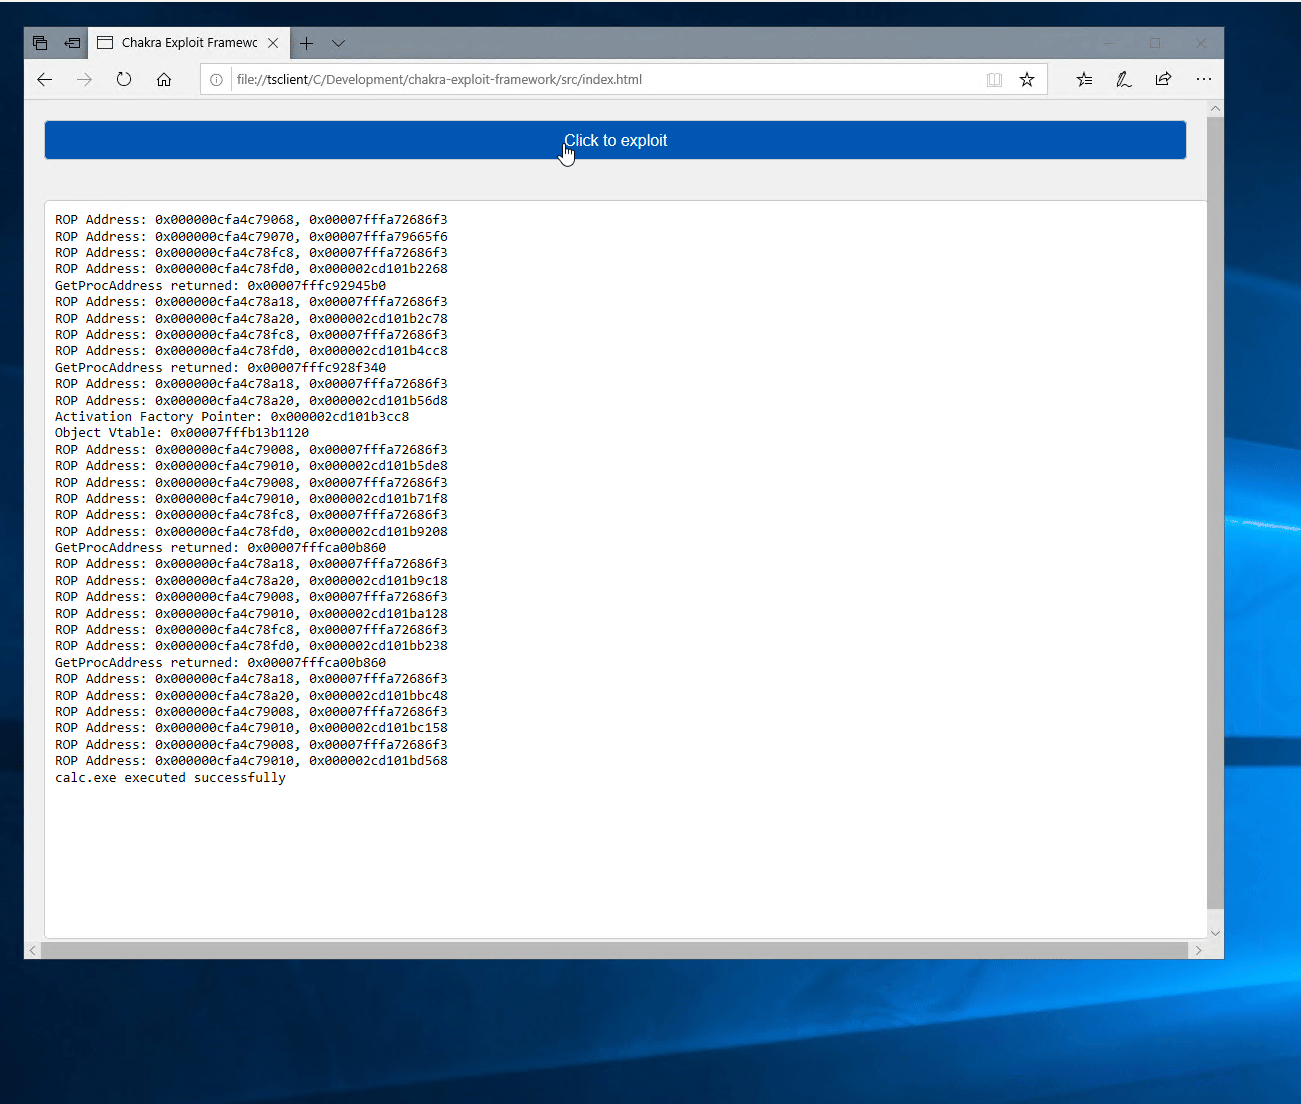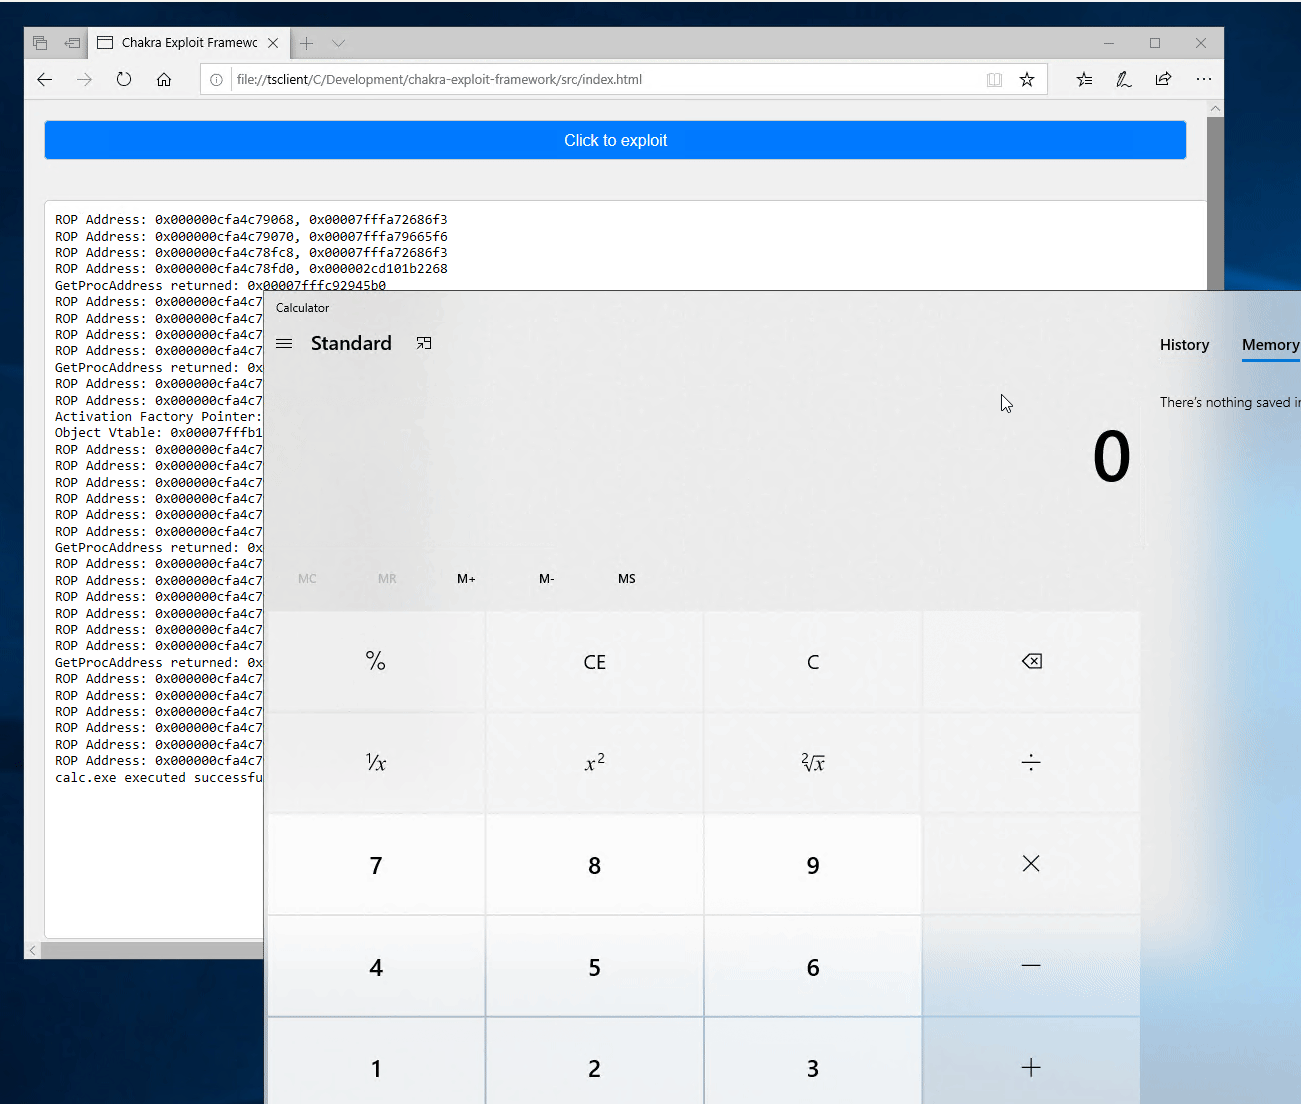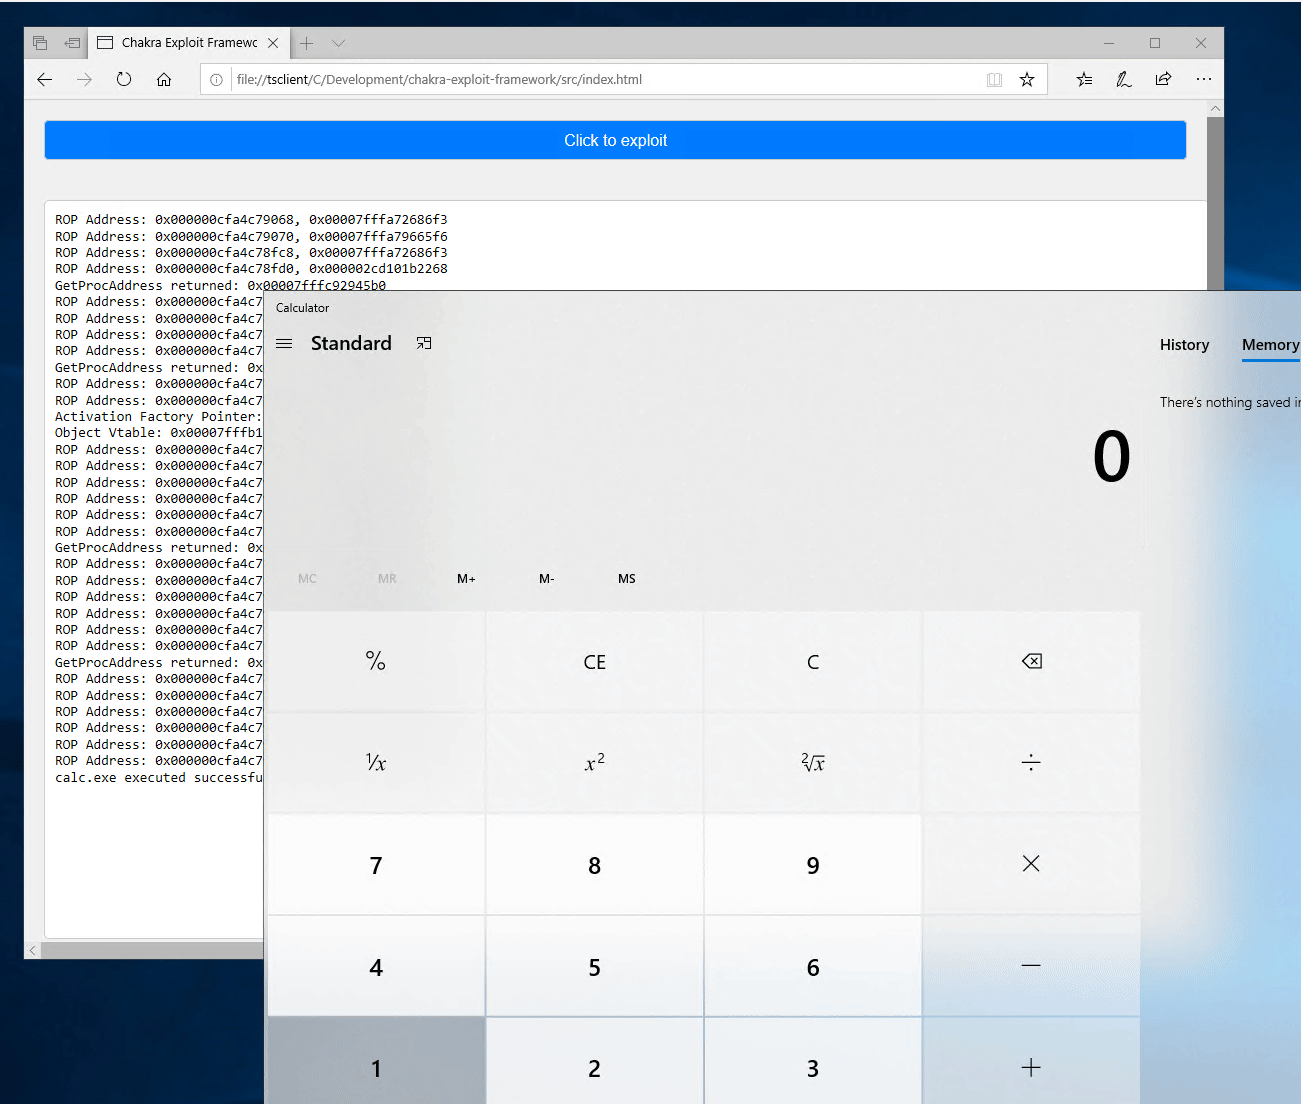
Browser exploitation framework for Chakra (Edge). Written as part of OSEE preparation. Demo bug: CVE-2019-0567

binary-exploitationeducationexploit-frameworks+6
11 year ago
GhostStrike preview

GhostStrike

GitHubmylo-2001/ghoststrike

Fully automated Spring4Shell (CVE-2022-22965) + GitLab RCE framework
exploitationpayload-generationpenetration-testing+3
110 months ago
LlamaStack-RCE-Deterministic-Supply-Chain-Exploitation-Hardening-Framework-CVE-2024-50050- preview

LlamaStack-RCE-Deterministic-Supply-Chain-Exploitation-Hardening-Framework-CVE-2024-50050-

GitHubsastraadiwiguna-purpleeliteteaming/llamastack-rce-deterministic-supply-chain-exploitation-hardening-framework-cve-2024-50050-

LlamaStack-RCE: Deterministic Supply Chain Exploitation & Hardening Framework [CVE-2024-50050] Focus on AI Security Research…
ai-securitybinary-exploitationcommand-and-control+9
8 months ago
CTT-Serverless-RCE-v1.0---Convergent-Time-Theory-Enhanced-MCP-Exploit preview

CTT-Serverless-RCE-v1.0---Convergent-Time-Theory-Enhanced-MCP-Exploit

GitHubsimoesctt/ctt-serverless-rce-v1.0---convergent-time-theory-enhanced-mcp-exploit

Serverless Framework MCP Server (CVE-2025-69256) Base Score: 9.4/10 → CTT Enhanced Score: 9.9/10 A critical command injection vulnerability in…
ai-securitycloud-securitycommand-and-control+8
7 months ago
CVE-2025-6389 preview

CVE-2025-6389

GitHubnxploited/cve-2025-6389

Sneeit Framework <= 8.3 - Unauthenticated Remote Code Execution in sneeit_articles_pagination_callback

educationexploitationpenetration-testing+3
5 months ago
CVE-2025-59057-PoC preview

CVE-2025-59057-PoC

GitHubboroeurnprach/cve-2025-59057-poc

A XSS vulnerability exists in in React Router's meta()/<Meta> APIs in Framework Mode when generating script:ld+json tags which could allow arbitrary…
exploitationpenetration-testingvulnerability-analysis+2
8 months ago
cve-2018-15473 preview

cve-2018-15473

GitHubcved-sources/cve-2018-15473

Docker-based vulnerable environment for CVE-2018-15473 exploitation, part of the Cved framework for managing and testing against known…
container-securityeducationexploitation+2
15 years ago
CVE-2025-64328_FreePBX-framework-Command-Injection preview

CVE-2025-64328_FreePBX-framework-Command-Injection

GitHubmcorybillington/cve-2025-64328_freepbx-framework-command-injection

CVE-2025-64328 FreePBX Authenticated Command Injection in the framework module.

command-and-controlexploitationpenetration-testing+2
10 months ago
CSV-Injection-in-Instant-Developer-Foundation-25.0-PoC preview

CSV-Injection-in-Instant-Developer-Foundation-25.0-PoC

GitHubvaleriocassoni/csv-injection-in-instant-developer-foundation-25.0-poc

This repository contains a Proof of Concept (PoC) for a CSV Injection (Formula Injection) vulnerability (CVE-2025-60852) affecting applications built…
data-exfiltrationeducationexploitation+3
10 months ago
cve-2021-3007-vulnerable preview

cve-2021-3007-vulnerable

GitHubkre80r/cve-2021-3007-vulnerable

CVE-2021-3007 Vulnerable Test Environment - Laminas/Zend Framework Deserialization RCE

educationexploitationlabs-practice+3
9 months ago
context-aware-offensive-intelligence preview

context-aware-offensive-intelligence

GitHubindoushka/context-aware-offensive-intelligence

Research framework redefining post-exploitation through decision intelligence.
configuration-auditinginformation-gatheringmisconfiguration+4
7 months ago
CVE-2025-55182 preview

CVE-2025-55182

GitHubnerium-security/cve-2025-55182

Host-based detection rules for the RCE vulnerability in the React JavaScript framework.

incident-responseintrusion-detectionthreat-intelligence+3
9 months ago
cve-2018-15961 preview

cve-2018-15961

GitHubcved-sources/cve-2018-15961

Docker container for CVE-2018-15961, part of the Cved framework for managing and testing vulnerable Docker environments in security labs.

container-securityeducationexploitation+3
15 years ago
vulnerability-assessment preview

vulnerability-assessment

GitHubabdirisaq-ali-aynab/vulnerability-assessment

Professional cybersecurity assessment demonstrating vulnerability identification, CVSS severity scoring, MITRE ATT&CK framework application, and…

educationpenetration-testingthreat-intelligence+2
10 months ago
frameworks_base_CVE-2022-20493 preview

frameworks_base_CVE-2022-20493

GitHubtrinadh465/frameworks_base_cve-2022-20493

Android framework base repository containing patches or analysis for CVE-2022-20493, addressing a security vulnerability in the Android platform.

android-securitybinary-exploitationexploitation+2
3 years ago
cve-2018-7600 preview

cve-2018-7600

GitHubcved-sources/cve-2018-7600

Docker container for CVE-2018-7600 (Drupalgeddon2) vulnerability exploitation, part of the Cved framework for managing vulnerable Docker environments…
container-securityeducationexploitation+3
5 years ago
frameworks_base_AOSP10_r33_CVE-2021-0334 preview

frameworks_base_AOSP10_r33_CVE-2021-0334

GitHubshaikusaf/frameworks_base_aosp10_r33_cve-2021-0334

Android framework base repository for AOSP 10 R33, modified to address CVE-2021-0334, focusing on vulnerability analysis and exploitation.

android-securityexploitationvulnerability-analysis
4 years ago
Previous1…404142…50Next